
Strategic Circle Briefing
Join to unlock strategic briefings after signing in.
Join Strategic CircleGovernance / IETF
The IETF writes the protocols every network runs on. We follow the drafts, the working-group fights and the standards that ship, and explain what each one changes for operators before it reaches production.

Latest Coverage
1,656 articles
IETF
A post-quantum signature can look affordable when a device is starting up and much dearer when it is still doing its job. An IETF draft headed for a 5 November review forces buyers to specify which moment their update system uses.
IETF
A registrar asks to take over a domain and receives an HTTP `201 Created` response. What was created? Under a new IETF RPP draft, it can be the *transfer process*, not the completed change of sponsor. The process has its own URL, decisions and messages. A customer-facing…
IETF
A 2 November IETF revision puts a sharper edge on Mobile User Plane routing: a controller can turn one mobile session into a route that beats a broader VPN path. The DMM draft now states which behaviour is normative, while a separate BESS draft holds the BGP bytes. The handoff…
IETF
A CoAP server can replace many individual notifications with one multicast message. The network bill falls; the attendance sheet disappears. A current IETF draft asks a random fraction of listeners to reply, then turns those replies into an estimate of who remains interested. In…
IETF
An IETF draft offers eleven new cipher suites for secure group messaging. Eight use post-quantum key encapsulation but keep traditional signatures; three add ML-DSA signatures. The November revision now spells out what a forged classical signature could do to a later group epoch…
IETF
In a cross-provider chat, an encrypted attachment travels separately from its message. Somebody must fetch it. A new MIMI draft offers three routes, and each gives a different operator a view of the request. The receiving provider can lose sight of the asset host under Oblivious…
IETF
A website owner changes its DNS alias to a new provider. New visitors follow the new route. A proposed HTTP/2 and HTTP/3 feature complicates the goodbye: the former provider can still offer that site's certificate on a connection opened for another site it serves. The server's…
IETF
The IETF's new PCE state-sync draft has changed its label from Standards Track to Experimental. Its reason is concrete: when three path controllers lose a session, each may see a different set of reachable peers. No implementation is listed to settle the question in running…
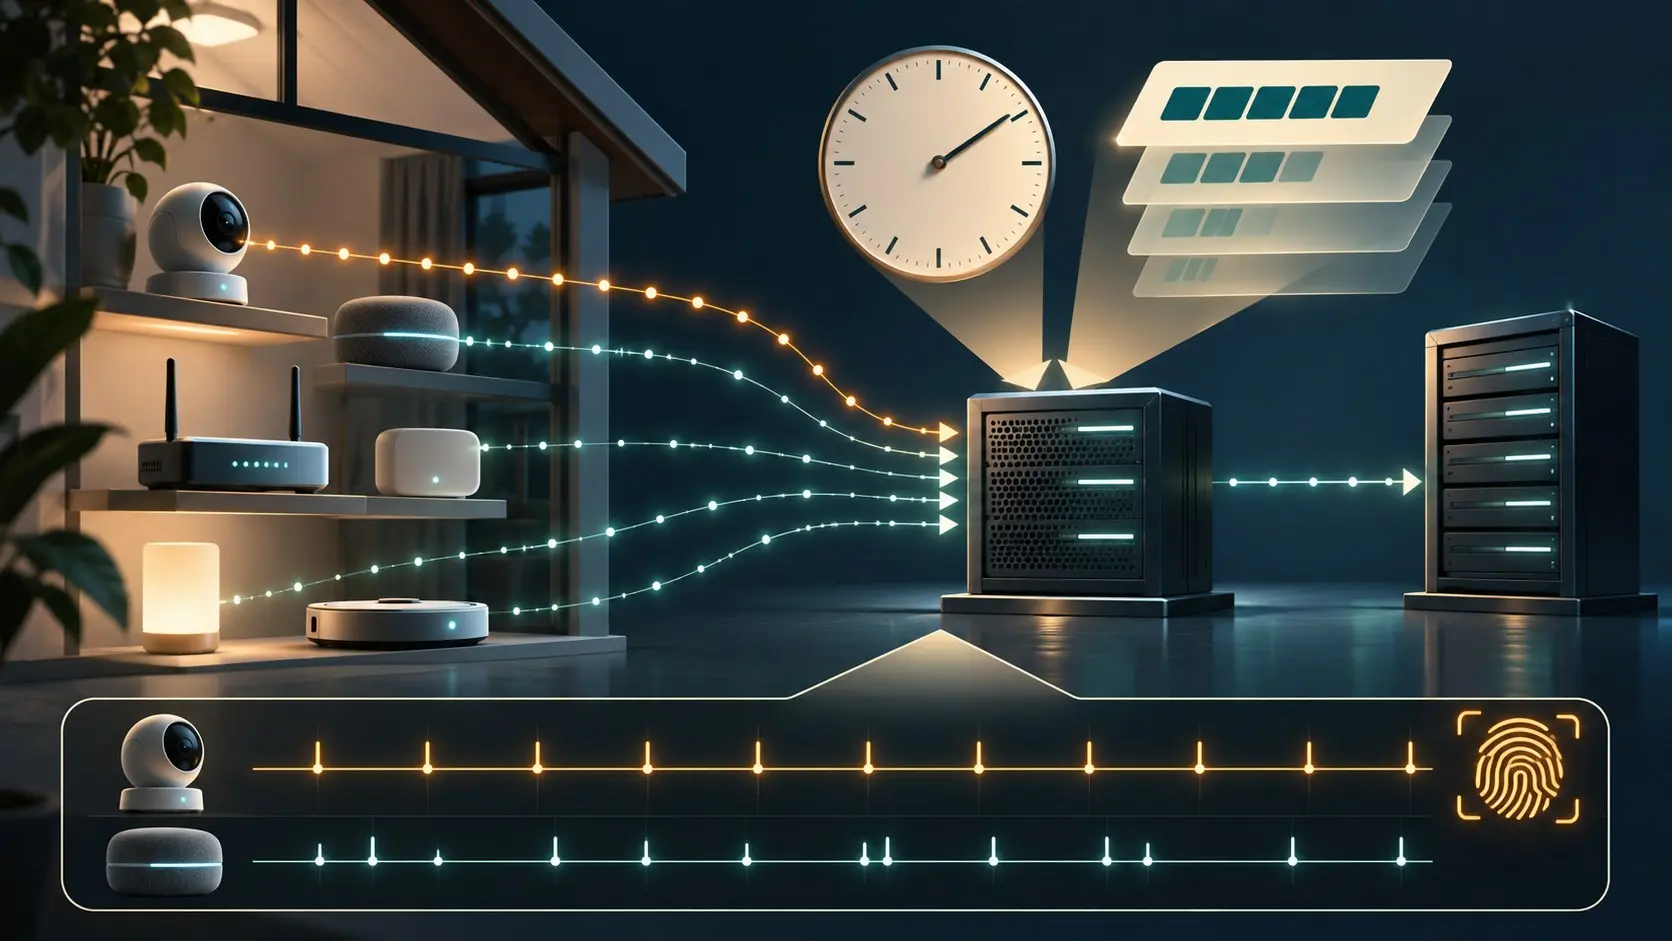
IETF
A camera checking its management domain on a fixed schedule can reveal its own rhythm to anyone watching DNS traffic. That pattern may survive a change of address, network or owner. An IETF IoT draft asks manufacturers to respect the DNS record's lifetime, vary necessary rechecks…
IETF
Two independent systems can serve one domain and still fight over the single DNS alias used to prove control of it. An IETF draft gives each ACME account its own validation name. The bargain moves a piece of certificate continuity onto the exact spelling of the account URL.
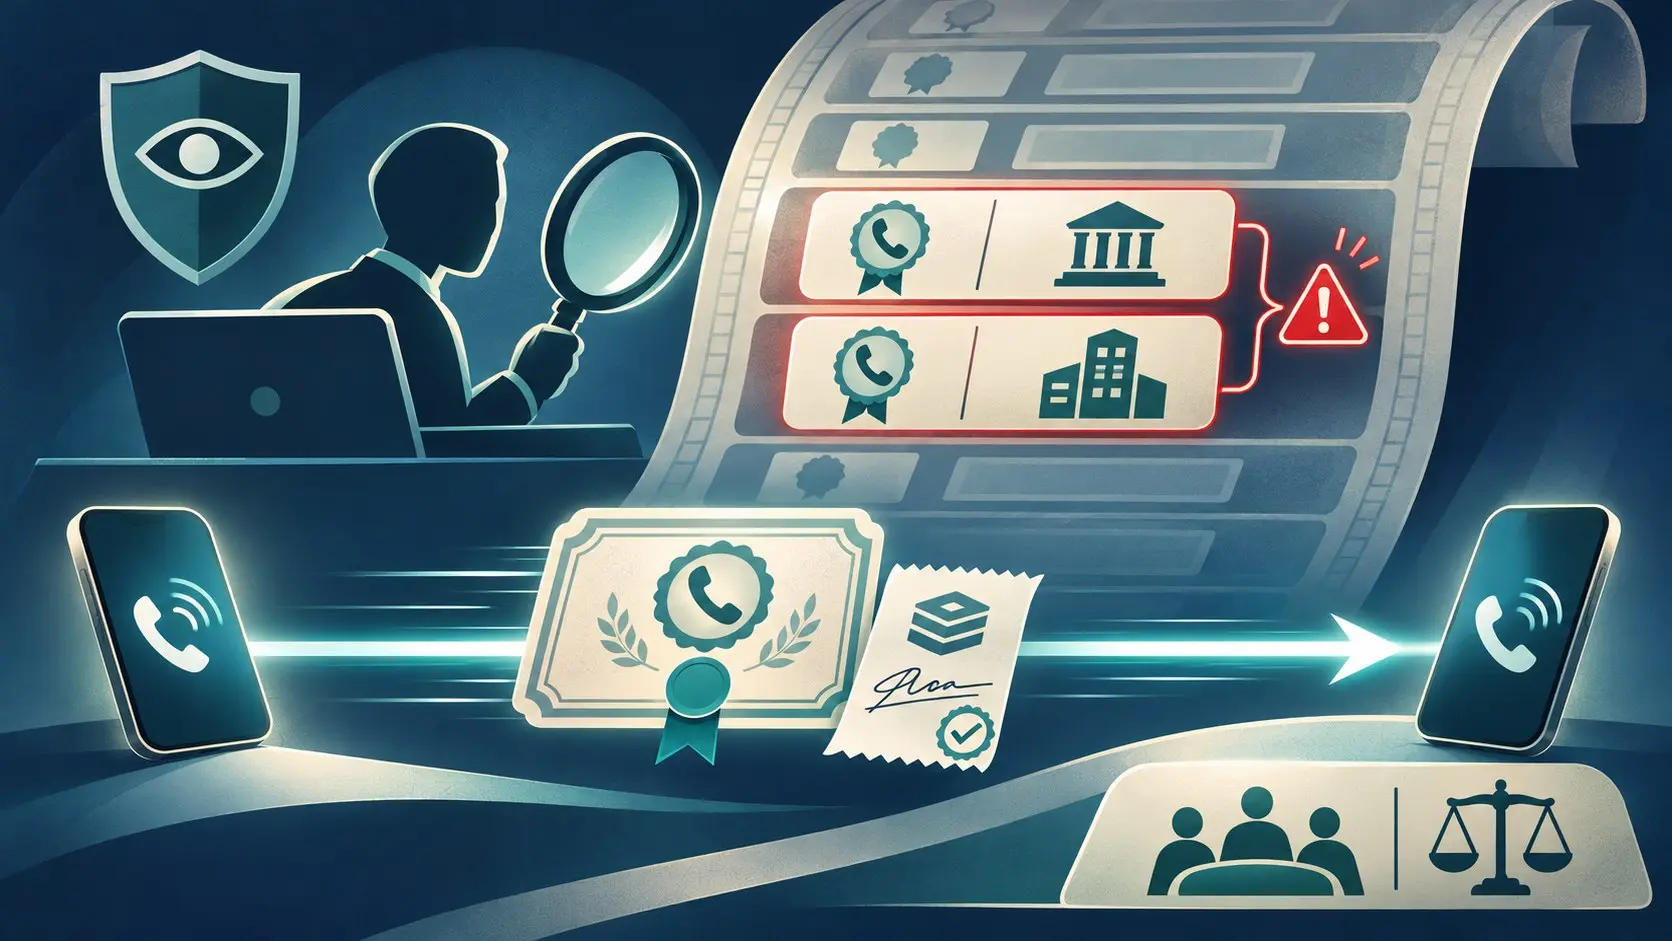
IETF
A proposed telephone-identity certificate log gives a call verifier a signed receipt it can check without waiting for the log. The same speed leaves the conflict hunt to a monitor working on another clock. If two certificates claim the same number for different parties, the first…
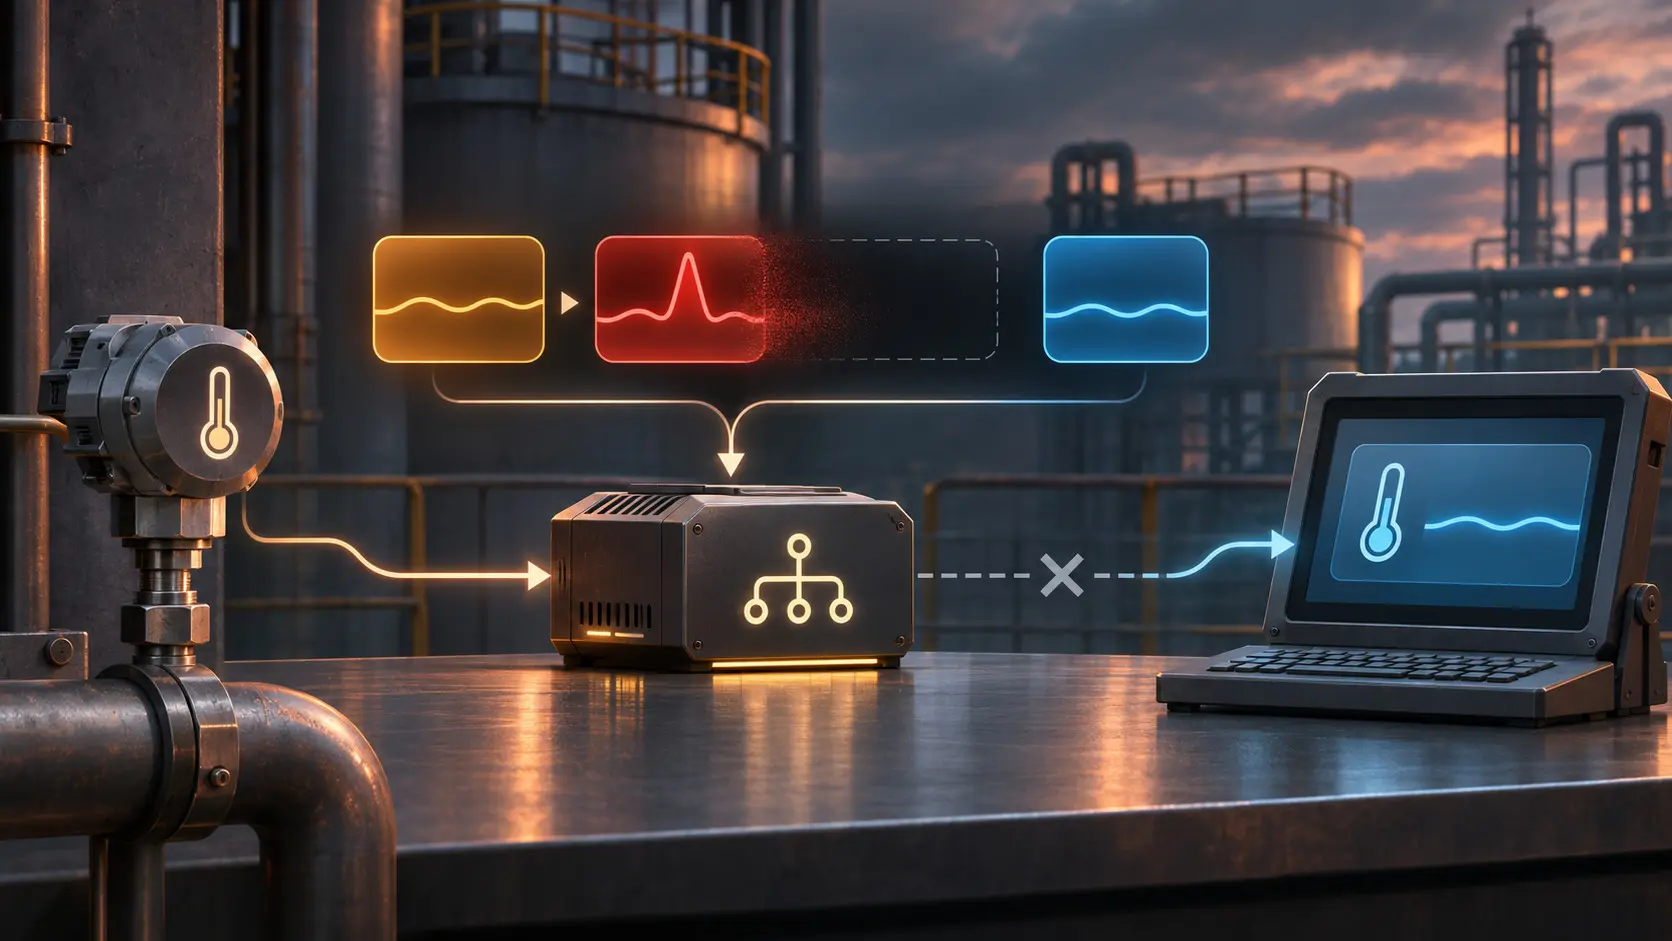
IETF
A proposed CoAP broker can hold a sensor's latest published reading for a subscriber that disappears and returns. That is useful until the reading goes bad and recovers during the outage. The returned normal value is the broker's latest record; the alarm that mattered to the…
IETF
A buyer can take the factory, the brand and the web domain. The old devices still carry an address for the file that tells a firewall what they may do. An IETF draft turns that awkward inheritance into a signed succession problem: move the MUD file without giving a compromised…
IETF
An IETF draft would let a DNS zone advertise several signing algorithms while serving one widely supported path. That frees providers to move separately. The sharp edge sits at the resolver: disable a supposedly universal algorithm locally and the draft makes that zone insecure…
IETF
An IETF draft would let the familiar `64:ff9b::/96` translation prefix reach private IPv4 addresses. That may rescue applications on IPv6-only networks. It also ends a convenient arrangement in which a standards prohibition quietly did part of the firewall's job.

IETF
A new research draft gives the automated network operator a less glamorous assignment than writing policy: identify itself, leave a trail, wait for a human at the dangerous junction and know how to reverse a mistake.

IETF
The IETF is weighing a reversal of a simple 2010 rule: drop private IPv4 destinations carried under NAT64’s well-known prefix. The latest draft adds the question an operator needs answered before touching the switch: what does this translator do today?
IETF
The Internet’s standards gatekeepers approved a wider HPKE design on 2 November. The same document draws a bright line around how far its existing security analysis reaches.
IETF
A new remote-attestation proposal lets an enrollment server move credential requests, evidence and sealed replies. The issuer or vault keeps the power to decide. That line matters most when a convenient middlebox starts to look like a trusted authority.
IETF
The 2 November AACP proposal puts a separate confirmation service between an agent’s proposed side-effecting action and the system that executes it. The service must show the user the consequential fields and sign the decision; a chat transcript no longer gets to play the part of…
Member Unlock
Login is required to unlock full profile briefings and deep-dive sections.
Join to unlock strategic briefings after signing in.
Join Strategic CircleFor IP-asset owners and leadership teams: alliance briefings, private reports and direct analyst support.
Join Leadership Alliance