
Open standards body with worldwide implementation impact.
Governance / IETF
IETF
IETF governance intelligence tracks institutions, policy processes, standards activity, registry operations, accountability disputes, and implementation signals that affect internet infrastructure. BTW.
GlobalProtocol GovernanceInteroperability Risk

Protocol process and standards legitimacy.
Spec-to-implementation gap across vendors and operators.
Major standards shifts usually affect systems over 120d+ cycles.
Latest Coverage
Latest from IETF
1,159 articles
IETF
The String Looked Like an Address. Part of It Was an Instruction.
A field labelled “phone” can contain far more than a destination. RFC 3601 allowed the same text string to carry digits, pauses, waits for tone, access codes and post-connection menu choices. For leaders migrating contact, voice or gateway systems, the decisive question is…
IETF
The Label Said Confirmed. Nobody Had Approved It as Training Truth.
A network engineer can confirm an anomaly for one incident, service and evidence window without authorising that label to retrain every future detector. The state transition records a judgment. It does not, by itself, define the judgment’s scope, authority, evidence custody or…

IETF
The Ticket Was Cleared. The Authentication Wave Had Not Yet Begun.
A two-byte DHCP instruction can make a security dashboard look decisive: selected reusable tickets are no longer in a device's persistent store. RFC 3594 defines that local transition precisely. It does not say that a live association was revoked, a replacement ticket was…
IETF
The Scheduler Was Fair to Flows. One Customer Had Opened Eight.
FQ-PIE can give competing packet flows separate queue state and scheduled service while still answering the wrong fairness question for an operator. The mechanism sees five-tuples and finite buckets; leadership may care about customers, applications, tunnels, networks or service…
IETF
The Reply Found Its Port; the Next Request Could Still Vanish
RFC 3581 repaired a precise SIP failure: a response could know the right translated IP address and still be sent to the wrong port. Its `rport` parameter lets the server answer through the opening made by the request. That success belongs to one transaction. It does not turn the…
IETF
The Audio Played. The Extension Had Never Taken Effect.
An Opus packet can survive an optional extension being unknown, malformed or deliberately ignored. That continuity is the point of the design—and precisely why audible base output cannot certify the enhancement around it.
IETF
The Line Went Quiet; the Session Had Not Ended
RFC 3573 solved a narrow dial-up problem with a durable systems lesson: a temporary condition, the policy chosen in response, and the eventual service result are three different records. Its modem-on-hold message tells a remote session server what the access edge observed. It…
IETF
The Token Authenticated Twice. Only One Server Had Marked It Used.
Two front ends accepted the same reconnect proof. Both HMACs were correct. The first node had already consumed the token; the second had not yet received that state. Cryptography answered who possessed the secret. Replication decided whether the possession could be exercised…

IETF
The Best Surrogate Was Chosen for the Resolver, Not the Client
A request-routing system can make a perfectly reproducible decision about the wrong subject. RFC 3568 exposes the substitution: DNS commonly reveals the address of a client-site resolver, and recursion can replace even that address with another name server. The system may then…

IETF
The Server Said Nothing Had Changed. Another Authority Was Already Serving Something Else.
The resolver received a tiny “nothing new” signal and kept the large signed RRset already in its cache. That saved a retrieval. It did not establish that every authoritative server held the same generation—or that the cached entity still represented the operator's current intent.
IETF
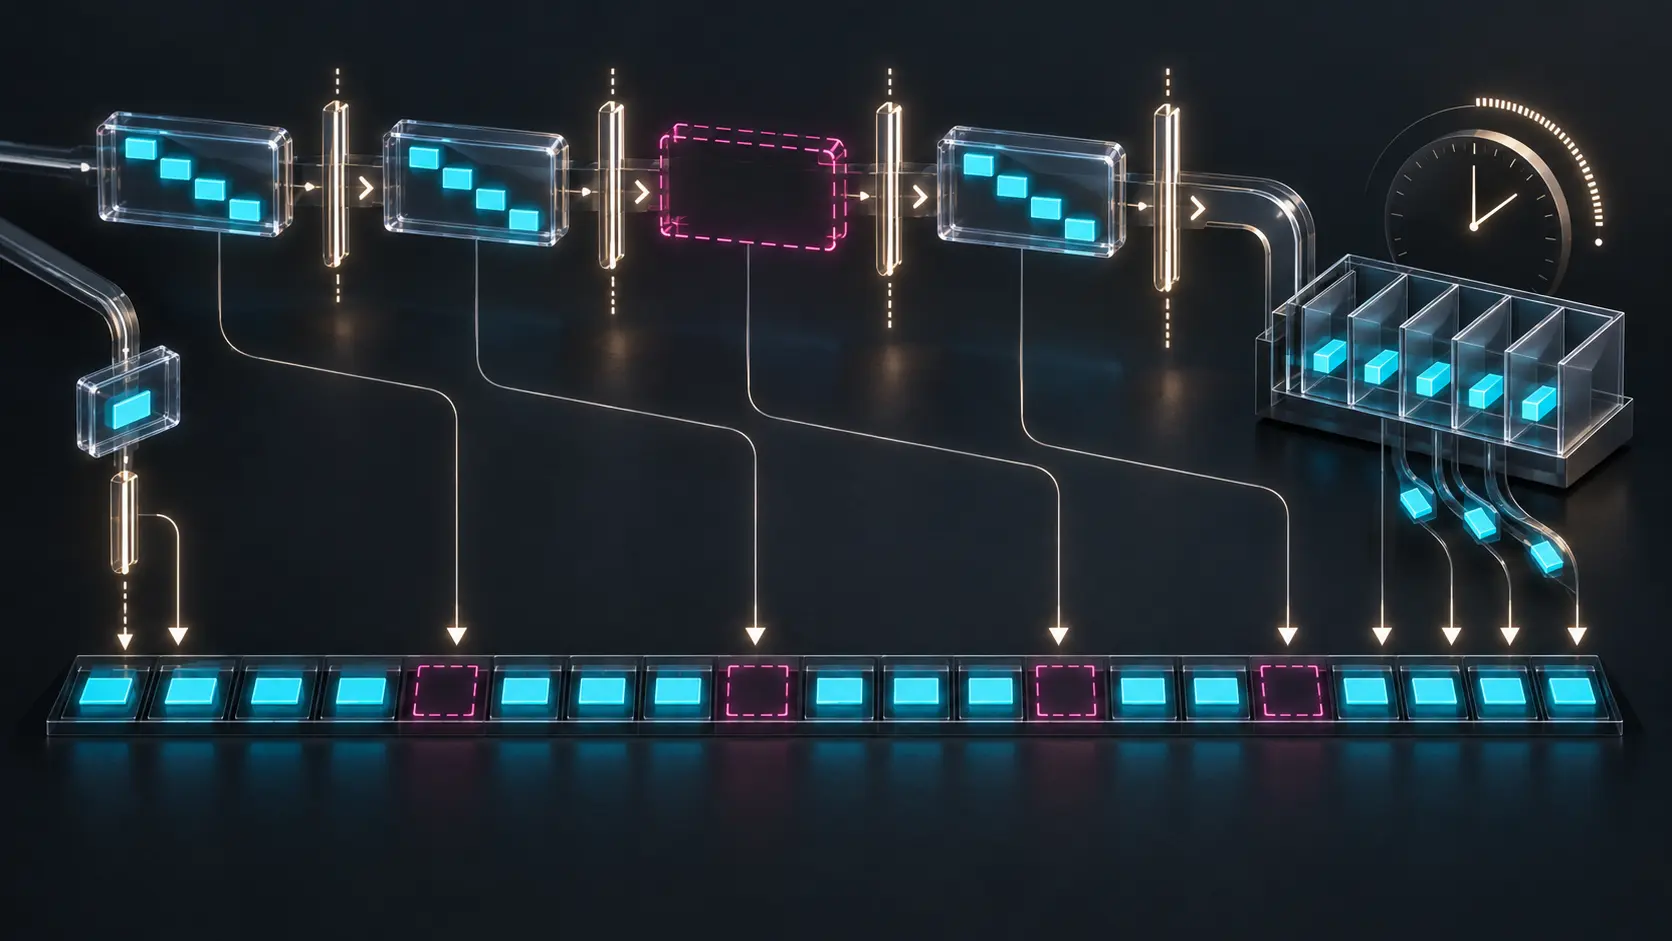
One Packet Vanished. The Damage Arrived in Instalments.
An interleaver can turn one lost datagram into several separated 20-millisecond holes instead of one continuous wound in speech. That sounds like recovery. It is not. RFC 3558 buys a different loss shape by making the receiver hold more state and wait longer before it knows what…

IETF
The Update Was Accepted. The Parent Had Not Published It Yet.
The child received `NOERROR` from the delegation update receiver and closed its change ticket. Minutes later, an authoritative parent server still returned the previous delegation. Nothing in that constructed sequence contradicts the draft: acceptance means the change should…
IETF
The Packet Saved Three Headers. It Lost Eighty Milliseconds at Once.
Four 20-millisecond feature pairs shared one RTP packet. The packetizer paid for one header instead of four. When that datagram disappeared, the speech engine did not lose a header-efficiency statistic; it lost one continuous 80-millisecond stretch of evidence. RFC 3557 makes…

IETF
The Peer Was Valid. One Claimed Address Could Still Redirect the Traffic.
The certificate checked out, the IKE exchange completed, and the SCTP association had several paths to choose from. One address at the end of the selector list belonged to somebody else. RFC 3554 makes the uncomfortable point explicit: authenticating the peer is not the same as…
IETF
The Timer Reached Zero. One Signer Was Still Serving Yesterday.
In a constructed operator transition, the controller completed its last configured wait and marked the departing DNS provider safe to remove. The parent showed the new nameserver set. The shared DNSKEY view looked correct. One remaining secondary, however, was still serving an…
IETF
The Agents Agreed the Binding Was Gone. The Mobile Node Was Still on the Old Path.
The revocation crossed the tunnel, its authenticator checked out, and an acknowledgment came back. Between the home agent and foreign agent, the record looked closed. Below that exchange, the mobile node could still be waiting for a sequence-zero advertisement, trying the route…
IETF
The Token Matched. The Privilege Scope Was Still Blank.
In a constructed operating case, a DNS administrator placed an opaque TXT value at the requested challenge name. The provider found the exact token and granted control over several service features. The record proved that a challenge had reached DNS. Nothing in it showed that the…

IETF
Failover Copied the Login. One Server Said Accept, the Other Reject.
The watchdog expired, so the client sent every pending request to an alternate AAA server. The alternate answered first. The original request had not vanished; it was still alive on the old path. One logical login had become two opportunities to decide, and a faster recovery…
IETF
The Origin Changed the File. DNS Kept the Old World.
In a constructed operating case, an origin replaced its `origin-svcb` JSON and the fetch returned valid HTTPS. The dashboard marked the ECH rotation complete. The zone serial had not changed, one zone factory had rejected an endpoint, and recursive caches still carried the…

IETF
The Ceiling Was Large. The Memory Was Never Promised.
A capacity model saw a peer advertise a very large TLS receive limit and booked the same number of bytes as dependable headroom. In the constructed test, many connections exercised that permission together. The protocol ceiling held; the memory assumption did not. A maximum…
Member Unlock
Restricted Profile Intelligence
Login is required to unlock full profile briefings and deep-dive sections.
Strategic Circle Briefing
Join to unlock strategic briefings after signing in.
Join Strategic CircleLeadership Alliance Briefing
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance