
Impact
HIGH
Within the Impact facet, HIGH impact intelligence highlights articles where the expected effect level, operational exposure, or decision relevance is comparable. Readers can use the page to separate routine market updates from higher-consequence governance, infrastructure, security, and investment signals that may affect planning, procurement, policy, or customer exposure. The page connects the consequence band to public evidence, related organisations, regional context, operating dependencies, service continuity, competition, investment timing, compliance, and customer risk. It helps readers decide which developments deserve deeper monitoring, which actors are most exposed, and how a signal may affect operations or market planning.
CASE FILE
The Algorithm Name Matched. The Hash Receipt Did Not: RFC 9861
KangarooTwelve and TurboSHAKE give operators fast, extendable cryptographic output, but the label on a library call is only the beginning of the evidence. Reproduction depends on the exact function, byte stream, domain or customization input, output length and execution path that…

IETF
James Gould and the Redaction Signal That Is Not Policy Proof
An empty place in an RDAP response can mean that no value exists, that a value was withheld, or that the question exposed a shape the server chose not to acknowledge. RFC 9537 gives one of those absences a machine-readable explanation. James Gould’s work on the specification…

IETF
Hugo Krawczyk and the Public Salt That Is Not Password Hardening
A value may be public, repeated and still do important cryptographic work. That is the apparent paradox at the centre of HKDF. Hugo Krawczyk’s extract-then-expand design makes the answer operational: salt, source entropy and application context are separate inputs with separate…

IETF
Suzanne Woolf and the Server Label That Is Not a Machine Identity
A DNS reply can carry a label for the server that produced it. That sounds like identity until anycast, operator-defined bytes and hop-by-hop scope are allowed back into the picture. Suzanne Woolf’s work on the requirements behind NSID offers a more useful interpretation: the…

IETF
Sara Dickinson and the Resolver Promise Encryption Cannot Prove
The padlock beside a DNS resolver name is reassuring because it proves something useful: the client has protected its conversation on the way to a particular service. It is also dangerously easy to ask that icon to prove the rest. Sara Dickinson’s co-authored RFC 8932 follows the…
IETF
Ole Trøan and the Three Decisions NAT Used to Hide
A laptop has two globally usable IPv6 addresses, two routers and two DNS resolvers. Nothing is missing, yet the first packet can still fail: the chosen source may belong to one provider, the chosen door to another, and the chosen name answer to a third context. Ole Trøan’s…

IETF
Tim Chown and the Host List Hidden Inside an IPv6 Address Plan
IPv6 made blind enumeration uneconomic, but it did not abolish reconnaissance. Tim Chown’s work shows how addressing conventions and operational exhaust can turn an immense namespace into a succession of small, testable target lists—and why defenders face the same discovery…

IETF
Brian Haberman and the 40-Bit Global ID That Was Not an Allocation Receipt
A locally generated IPv6 prefix can be extraordinarily unlikely to collide with another one and still carry no guarantee. Brian Haberman’s work on RFC 4193 makes that distinction operational: probability reduces coordination cost, but only an inventory, a route decision and a…

ICANN
Allison Mankin and the Name-Collision Sample That Could Not Prove Its Cause
A root server can record a query for a private-looking name with great precision. The record still cannot say which application produced it, who owns the broken dependency, how many users rely on it or what a future delegation would harm. Allison Mankin’s work on RFC 8023 helps…
CASE FILE
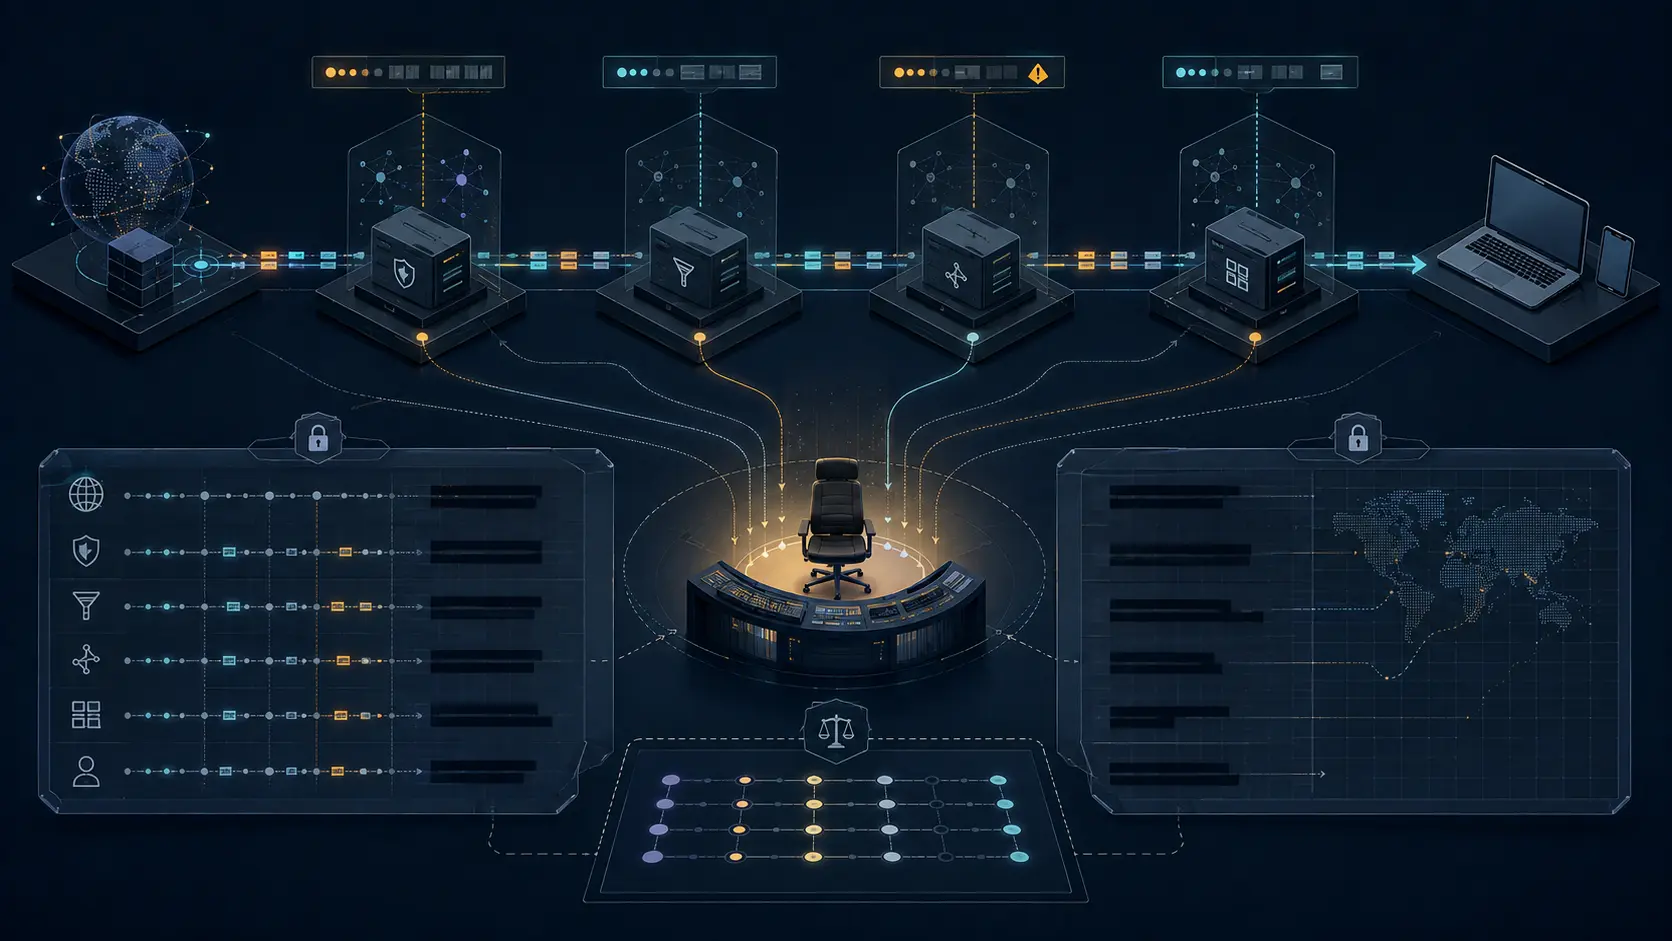
A Proxy-Status Chain Does Not Name the Incident Owner
RFC 9209 can make a failure path legible without making anyone accountable for repairing it. The missing entity is an intermediary fault-handoff matrix: a private governance record that connects each visible or redacted hop to an operator, an escalation clock, retained evidence…

History
The Test Measured the Reserve by Spending It: RFC 1628
A UPS exists to preserve power when ordinary supply disappears. RFC 1628 defined a diagnostic that learned more about that reserve by deliberately drawing it down. The result could improve confidence in battery replacement and run time, but the test left the protected load with…
History
The Address That Had to Be Empty: How SMTP Stopped Errors from Mailing Errors
The most important address in SMTP is sometimes no address at all. A delivery failure has to travel back to the system responsible for the original message, yet a failure to deliver that failure must not produce another failure notice, and another after that. `MAIL FROM:<>`…

History
The Address That Recruited a Subnet: Why Routers Stopped Forwarding Directed Broadcasts
One IPv4 datagram could cross the Internet as an ordinary routed packet, reach the router responsible for a remote network and become a local broadcast there. With a victim's address forged as the source, that last-hop conversion could turn willing hosts on someone else's subnet…

History
The Link That Borrowed Its Address: How Relative URLs Made Documents Movable
A short hyperlink is not a small absolute address. It is an instruction to borrow missing components from a base. That dependency let authors omit repeated schemes, hosts and path prefixes, and it let a collection of pages move while preserving its internal edges. The economy…
Global Cloud Services Trends
A CDN-Cache-Control Field Is Not a Chain-Wide Cache Policy
`CDN-Cache-Control` lets an origin address CDN caches separately from other HTTP caches. That is a useful control surface, but the field is not a declaration that every cache on the path will apply the same policy. Recognition, parsing, target-list order and forwarding still…

Global Cloud Services Trends
A Cache-Status Header Is Not a Complete Cache Trace
`Cache-Status` can make an HTTP cache’s decision visible in a structured form. Its presence is useful evidence about the cache that reports it. It is not automatic proof that every cache, hop or earlier acquisition decision in the delivery chain has been observed.
Global Cloud Services Trends
A Cache-Only 504 Is Not Proof the Origin Failed
An HTTP 504 often points investigators toward an upstream timeout. When the request explicitly forbids forwarding, however, the same status can report a cache-only miss. Incident attribution must preserve that distinction.
Global Cloud Services Trends
A Collapsed Cache Miss Is Not Permission to Share the Response
Combining several cache misses into one origin request can protect capacity. The optimization remains safe only when every waiting request is separately entitled to use the response that comes back.

History
The Link Was Open. Configuration Still Belonged to a Second Negotiator: RFC 1552
In one 1993 PPP design, reaching `Opened` could mean the network protocol was ready. In another, the very same state was only permission for a second negotiator to begin. RFC 1552 made that difference explicit—and showed why a state name is never a complete receipt.
Global Cloud Services Trends
Where HTTP Cache Invalidation Actually Stops
A successful write can prove that an origin accepted a change. It cannot, by itself, prove that every cache which might answer a later read has forgotten the old state.