
Topic
WHOIS/RDAP Accountability
Within the Topic facet, WHOIS/RDAP Accountability topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.

Story
APNIC’s WHOIS Archive Reports Two Totals for the Same Hour
The latest completed hour says APNIC received 3,192,583 WHOIS queries. Add the seven query types printed beside that total and the answer is 3,183,463. The missing bridge is not a rounding error; it is the meaning of the measurement.
Story
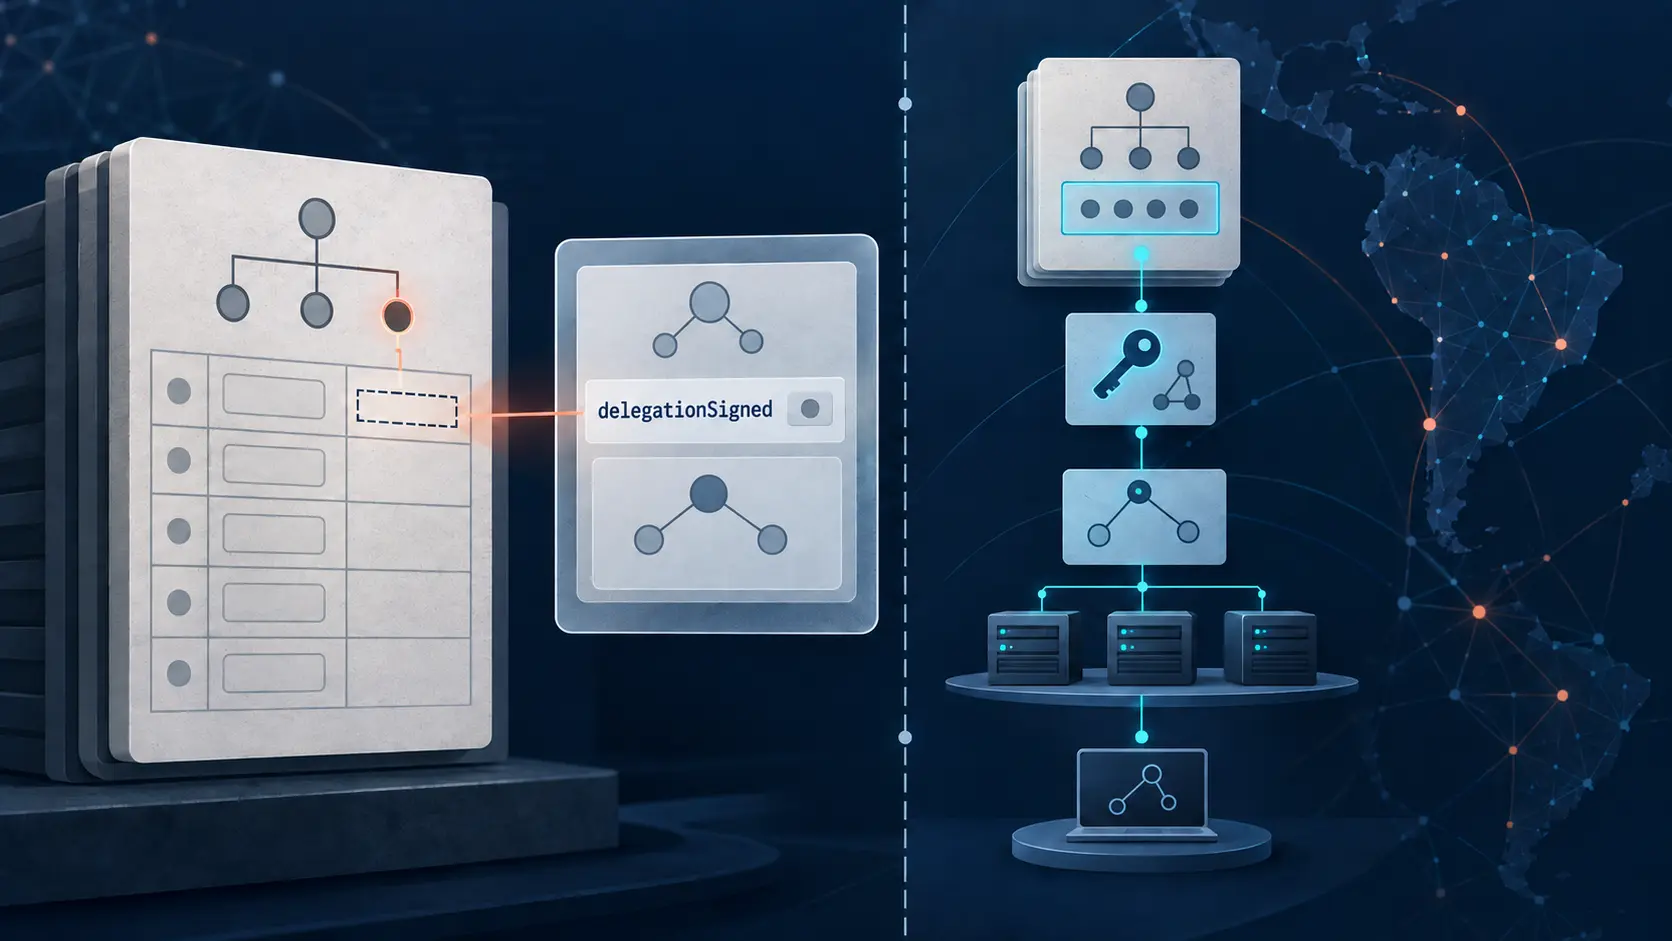
LACNIC's RDAP delegationSigned Records Parent DS Presence, Not DNSSEC Validation
A boolean in a registry response can look like a verdict on the security of a DNS chain. LACNIC's RDAP `delegationSigned` field answers a narrower question: whether the registration view reports DS records in the parent. It does not run a resolver, test the child keys or prove…

IETF
A Deprecation Date Retires an RDAP Label, Not Its Clients
An IANA registry can mark an RDAP extension obsolete. An operator can publish an end date. Yet somewhere beyond both records, a client may still ask for yesterday’s interface. That is not a contradiction. It is a map of divided authority—and a warning against treating one date as…

CASE FILE
A Holder-Designated RDAP Referral Extends Discovery, Not Registry Authority
A Holder-Designated RDAP Referral Extends Discovery, Not Registry Authority intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may…

Story
LACNIC Says to Email the Bulk WHOIS Form. The Same Page Says Email Is Not Accepted
LACNIC’s public instructions give a Bulk WHOIS applicant two doors and no label for the threshold between them. The signed form is to be emailed first, the original is to be posted after approval, yet the same page ends by saying emailed forms are not accepted. The problem is not…

Story
RIPE Database Is Switching to OIDC. Maintainer Authority Does Not Move With the Session
RIPE NCC plans to replace a site-wide cookie with an OIDC session for interactive RIPE Database use. That can improve authentication, but the harder acceptance question begins after login: which `mntner` authorises this identity to change this entity, under which session regime…

IETF
James Gould and the Redaction Signal That Is Not Policy Proof
An empty place in an RDAP response can mean that no value exists, that a value was withheld, or that the question exposed a shape the server chose not to acknowledge. RFC 9537 gives one of those absences a machine-readable explanation. James Gould’s work on the specification…

Story
AFRINIC's upd-to Receives Failed Update Notices, Not Database Authority
An unexpected Whois update can place a complete rejected entity in somebody's inbox. AFRINIC's `upd-to` field explains why that person received the warning; it does not identify the sender, confer a credential or prove that the attempted change ever reached the registry.
Story
ARIN's Retired Origin AS Field Recorded a Possibility, Not a Live Route
Old registration exports can preserve an `Origin AS` value long after ARIN removed the field. The label looks authoritative, but ARIN defined it as an optional holder-supplied list of ASNs from which a block might originate. It was neither a cryptographic authorization nor a…
Story
LACNIC Whois created Dates the Registry Record, Not the Network's Launch
A timestamp precise to the second can look like a birth certificate. In LACNIC registration data, however, `created` dates the record for an address block. It does not reveal when the holder was founded, when engineers switched on a network, when the addresses were first used, or…

Europe and Middle East Regional ISP Trends
REGISTRANT LLC: one registration number, two operational control planes
REGISTRANT LLC: one registration number, two operational control planes intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow.…

Story
AFRINIC Whois org-type Classifies a Registry Relationship, Not Legal Corporate Form
AFRINIC’s `org-type` field looks deceptively familiar: a short label attached to an organisation record. Its proper use is narrower. It helps describe how that record sits inside the registry’s resource and membership system; it does not answer the legal, ownership or operational…
Story
RIPE Database mnt-ref Authorises an Organisation Reference, Not Corporate Control
An accepted `org:` link in the RIPE Database has passed a meaningful authorisation test. That makes it evidence of an approved database reference—not a shortcut to proving ownership, group membership or control of the network behind the record.

Story
APNIC’s NIR RDAP Redirect Finds a More-Specific Record, Not a Network Operator
A redirect from APNIC to an NIR-specific RDAP host is an evidence trail about where registration data is served. It can lead to a narrower record without proving who currently routes, owns or operates the network.

Story
ARIN’s Whois Retirement Proposal Is a Protocol Transition, Not the End of Directory Data
Three dates in ARIN’s latest consultation can look like shutdown deadlines. They are not. The registry is asking how to retire three older access protocols in favour of RDAP, with separate dependencies and earliest dates for each path. The proposal changes how registration data…

Story
LACNIC Whois routing-c Can Register Routing Policy, Not Prove Who Operates BGP
LACNIC Whois routing-c Can Register Routing Policy, Not Prove Who Operates BGP intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may…

Story
AFRINIC Whois mnt-domains Authorizes Reverse-Domain Records, Not DNS Service Operation
A database key can authorize the creation of a reverse-domain record while every DNS query to the supposed service still times out. In the AFRINIC Database, `mnt-domains` identifies a maintainer with authority over child domain-entity creation. It is evidence about registry…
Story
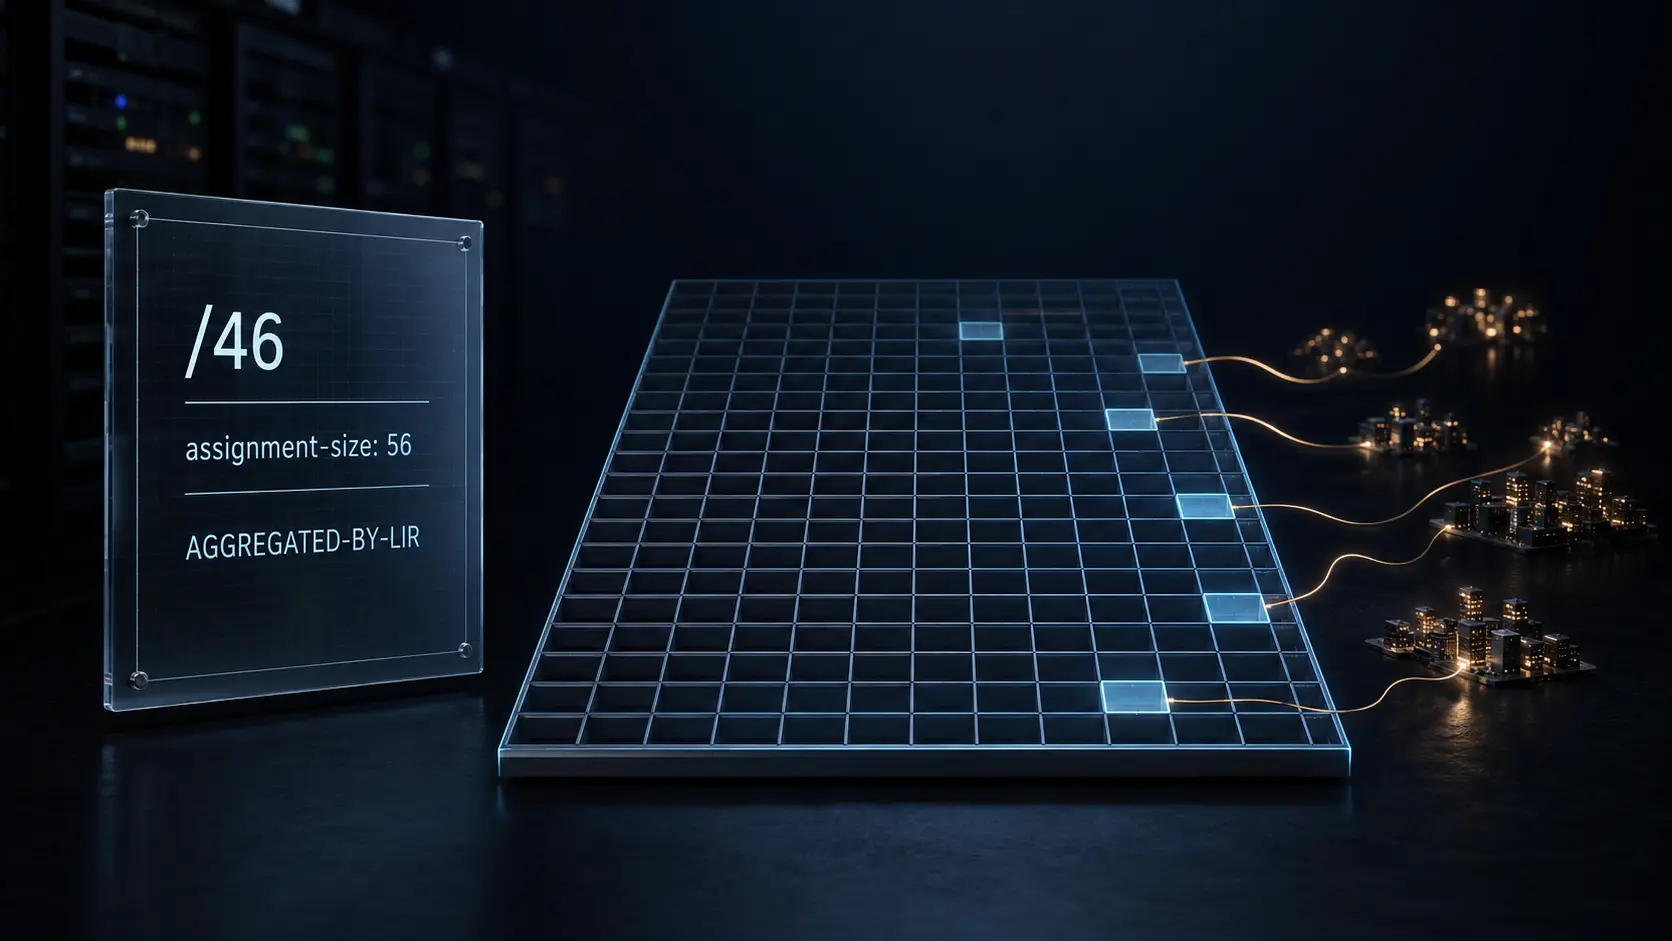
RIPE assignment-size Describes Aggregated IPv6 Assignments, Not Active Subscribers
A `/46` contains 1,024 possible `/56` prefixes. When a RIPE Database entity pairs that aggregate with `assignment-size: 56`, the arithmetic is exact—but the tempting subscriber count is not. The field records the size used for End User assignments inside an aggregate…
CASE FILE
RDAP Can Name the Assessor. It Cannot Authenticate the Result
Revision 02 turns a lone score into a time-bounded, contestable set of claims from multiple issuers. Yet its most important field, `scoreIssuer`, supplies attribution rather than in-band proof that the named assessor actually made the assertion.
Story
APNIC Whois mnt-irt Points to Incident Response, Not Network Control
A mandatory contact pointer can look like a declaration of who runs a network. In APNIC Whois, `mnt-irt` has a narrower and more useful meaning: it connects a number-resource record to an Incident Response Team entity for security and abuse handling. That link strengthens…