
Topic
Abuse-contact Economics
Within the Topic facet, Abuse-contact Economics topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.
IETF
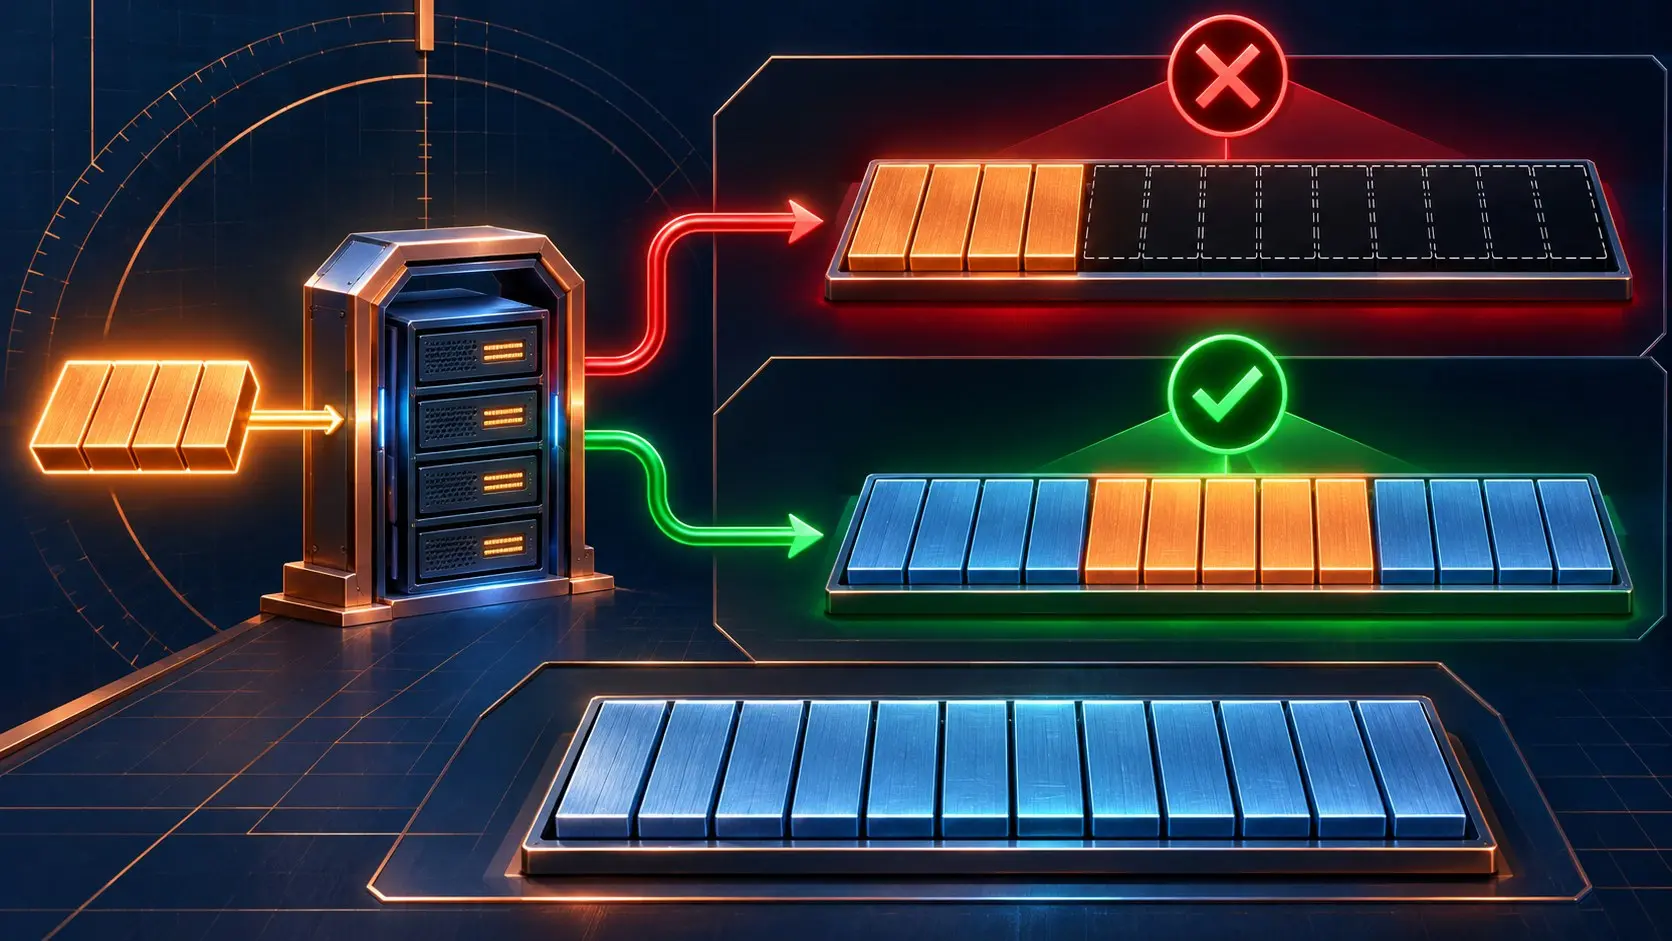
Four Bytes Came In. The Server Replaced the File.
A client wants to change four bytes in a twelve-byte file. It sends the fragment with a range saying where those bytes belong. A server that treats the range as a mere hint can replace the whole file with the fragment. The [IETF Byte Range PATCH…
Europe and Middle East National Telecom Trends
Ofcom Gives Scam Calls a Two-Day Paper Trail
The regulator will work backward through the providers that carried a suspect call. Each handoff now has a short evidence clock, a formal information demand and an awkward possible ending: the next provider does not answer.
History
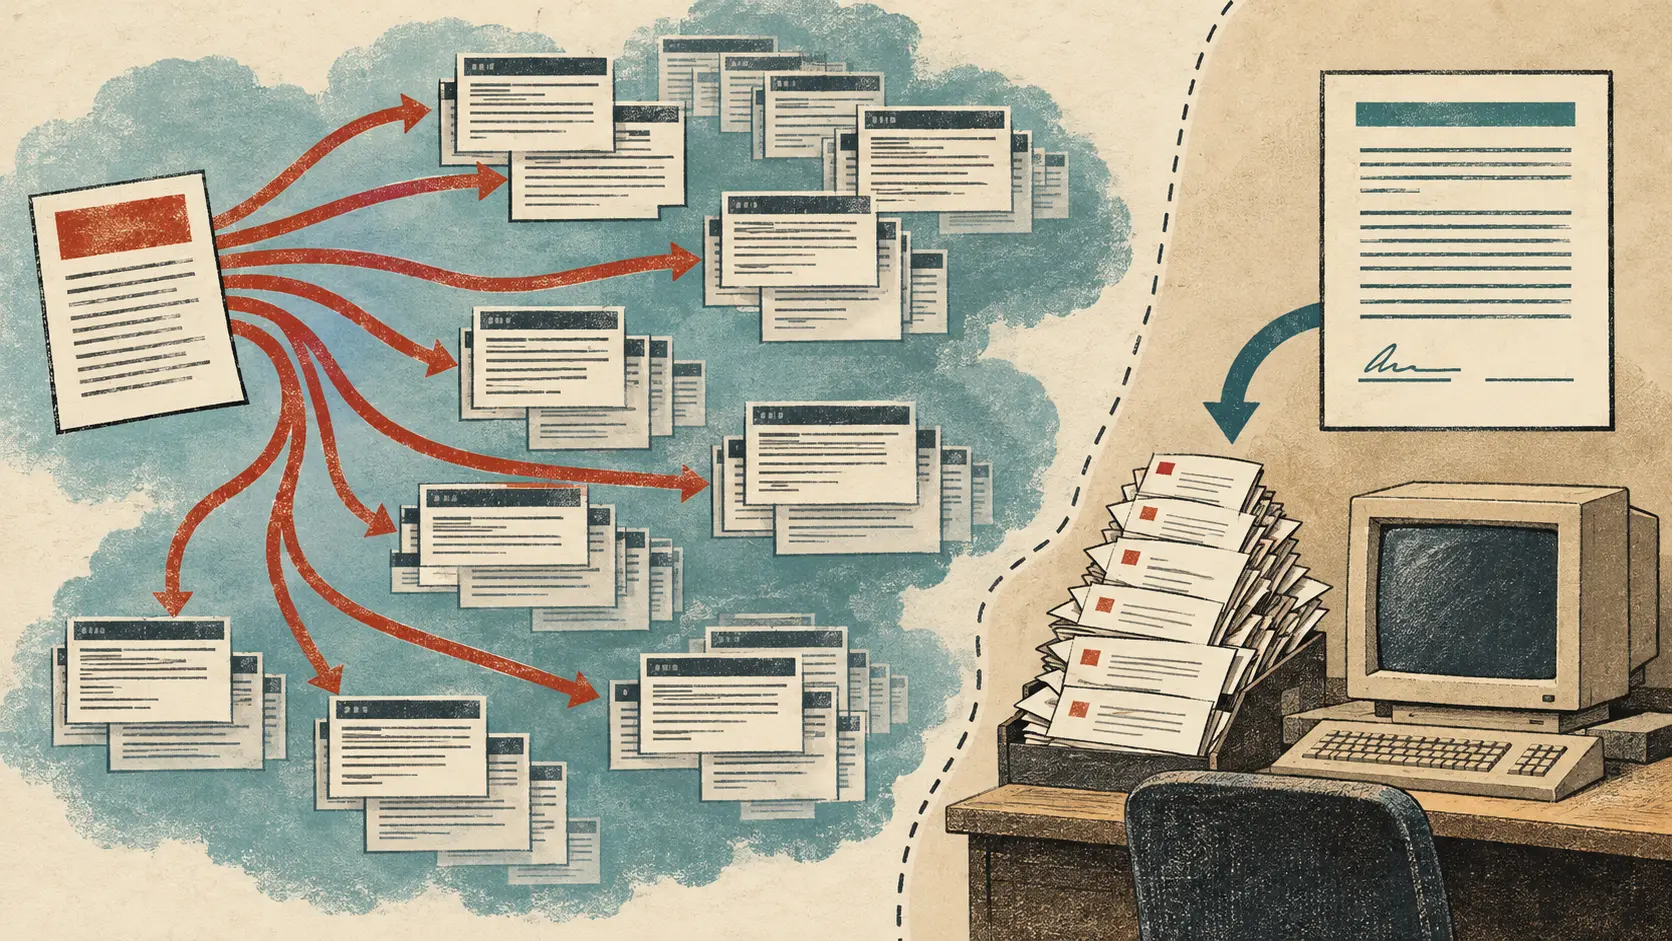
Almost 5,000 Usenet Groups—and a $250,000 Threat to the Provider
On 12 April 1994, Internet Direct’s system administrator said a Green Card Lottery advertisement had reached almost 5,000 Usenet groups, the provider had disabled the users, and the law firm threatened a $250,000 suit. The telling question was who controlled the account that sent…
North America National Telecom Trends
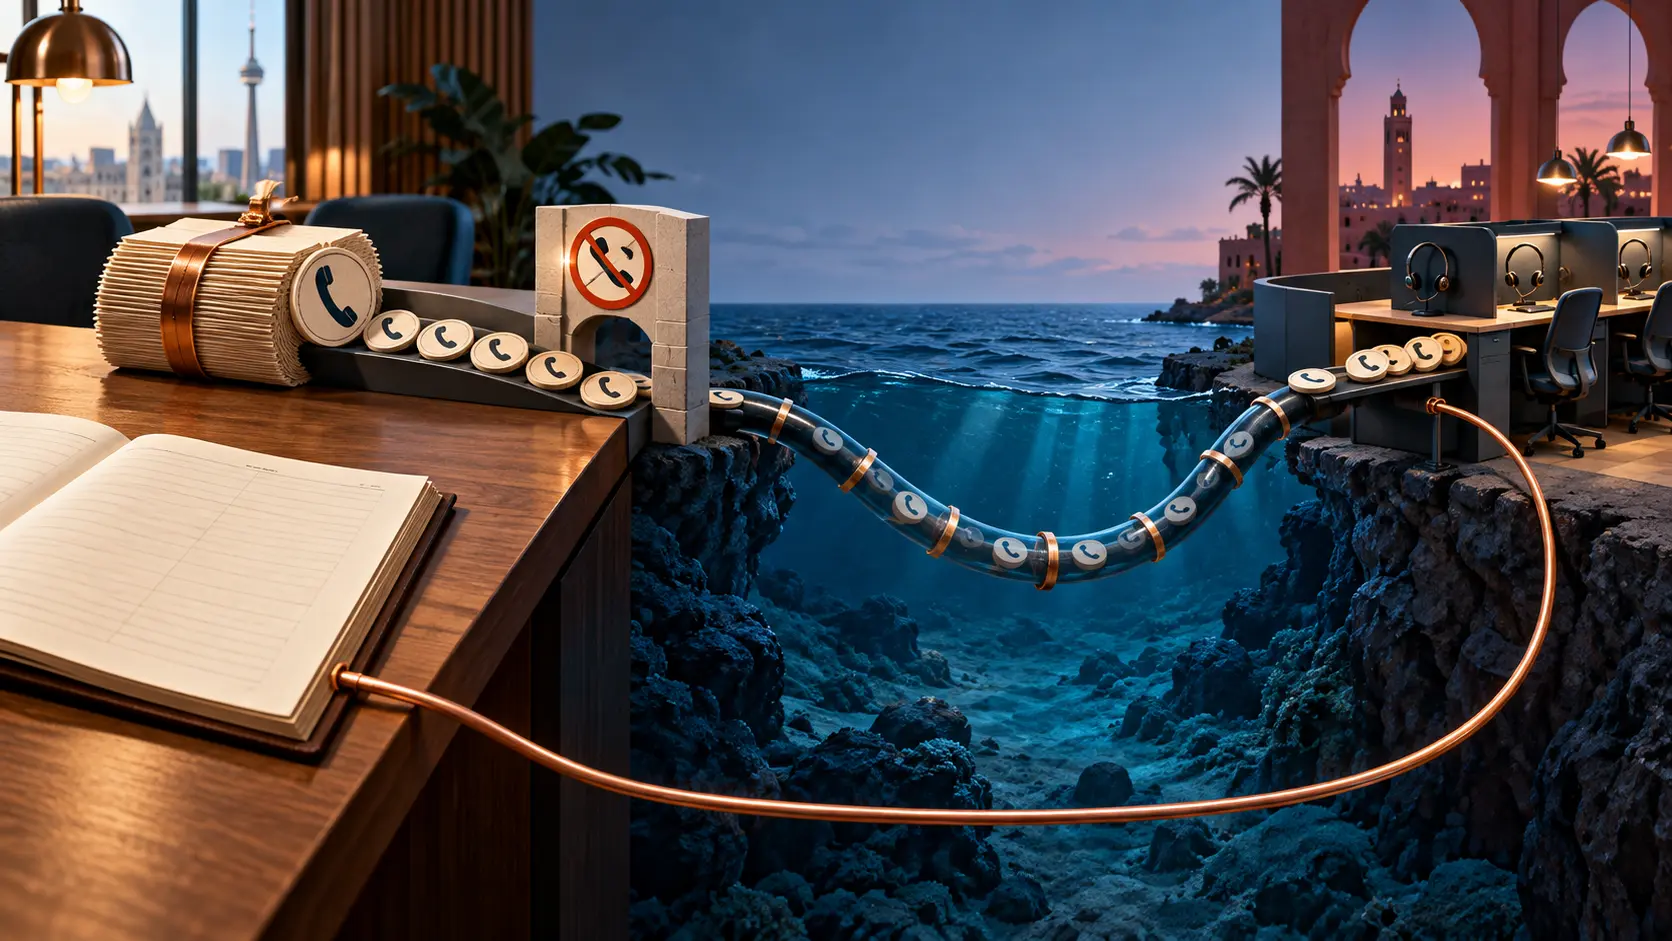
The Call Centre Was in Morocco. The $106,000 Bill Landed in Quebec.
Esprit Habitat hired a call centre across the Atlantic to invite Canadians to furniture sales. Canada's telecom regulator traced the calls back to the company that wanted the customers, then cut its own proposed penalty to a defensible number.
CASE FILE
The Honeypot Lives Elsewhere. The Accusation Starts on Your Server.
LightScope finds scanners from live hosts and offers automatic ISP reports. Its own data warns that an IP address is not an identity. Who signs the accusation?
CASE FILE
The Hotel Listing, the Phishing Message and the Ad Walk Into Brussels
Booking.com’s search page, reservation messages and paid rankings now sit in one European Commission case file. The regulator has opened a formal Digital Services Act investigation into three different doors through which a booking can go wrong. The fourth door is institutional…
Story
RIPE’s Abuse Clock Has Three Timers. The Exit Test Changes Halfway Through.
Fourteen days can start the process, seven business days can end the grace period, and RIPE NCC has one working day to lift restrictions. The schedule is crisp. The proposal’s definition of a successful repair changes between the notice and the exit.

Story
RIPE’s Proposed Abuse Ladder Needs an Auditable Exit
RIPE policy proposal 2026-02 puts a concrete sequence around infrastructure-level network abuse: a qualifying report, a measured threshold, formal notice, a cure period and administrative restrictions. The least settled part may be the point at which that sequence runs in…
CASE FILE
FTC asks whether platform ad optimisation furthers impersonation scams
The Federal Trade Commission is asking whether ad optimisation that helps impersonation scams reach consumers belongs inside its existing rule. The notice opens an evidence-gathering process; platforms have no new duty under it.
Asia-Pacific National Telecom Trends
TRAI's spam rules: an identity check is not a clean slate
India's September framework gives a sender a way to challenge a spam label. It also says that passing an identity check need not erase an instance from the enforcement history. The distinction matters well beyond the warning on a phone.
Asia-Pacific National Telecom Trends
A phone number moves. The duty to protect its owner does not.
Amaysim paid A$138,600 over unauthorised number transfers. A separate Ezee Mobile case shows why a fraud safeguard also needs to work after the transfer.

Story
A Deleted ROA Is Not an Abuse-Clearing Record
RIPE proposal 2026-02 starts from a cumulative record on an approved infrastructure blocklist, then allows removal of an “appropriate ROA” to count as compliance when restrictions are lifted. A route authorization can change without proving that the network operation named in the…

CASE FILE
Completed According to Whose Plan? Svea Bank's Self-Reported AML Remediation Meets the Regulator's Record
When Sweden's financial supervisor Finansinspektionen (FI) announced a sanction against Svea Bank AB on 17 December 2025, the operational part of the decision contained exactly two points: a formal remark (anmärkning) and an administrative fine of SEK 170 million. There was no…

CASE FILE
Three Names on One Netblock: How Custody of Svea's Legacy Abuse Contact Split Across a Merger
When a Swedish bank merges, its internet number resources do not disappear — they inherit. The RIPE Database record for 193.105.138.0/24 is a rare case where you can read the aftermath directly in a public registry entity: three distinct legal parties, one dissolved predecessor…

CASE FILE
Three Months After the Fine: No Follow-Up, No Appeal, No Documented Remedy for Svea Bank
On 17 December 2025, Sweden's financial supervisor Finansinspektionen (FI) gave Svea Bank AB (org. no. 556158-7634) a formal remark (anmärkning) and a sanction fee of SEK 170 million for breaches of core anti-money-laundering rules…

CASE FILE
Sanctioned but Not Ordered: Svea's Two Accountability Channels
When a Swedish financial regulator fined Svea Bank AB 170 million kronor in December 2025, the fine made headlines. What the decision itself ordered — and, more precisely, what it did not — tells a sharper story about where accountability for the bank and for its internet-facing…

CASE FILE
The Mailbox Was Never the Remedy: Where Accountability Actually Fired in the Svea Abuse-Contact Chain
Every abuse report has to land somewhere. For Svea's legacy routed network block 193.105.138.0/24, the landing place shown by independent mirrors of the RIPE Database is a shared mailbox on the Verizon Business domain — a carrier-era contact inherited from a lineage Svea never…

Story
The Svea Abuse-Role Record: Validated Contactability, No Documented Processing
The abuse contact recorded and mirrored for Svea's legacy netblock 193.105.138.0/24 is a carrier-era inherited mailbox on the Verizon Business/UUNET lineage — registry-validated for technical deliverability but never documented to have received, answered, escalated or remediated…

CASE FILE
The Mailbox That Exists Only in the Registry: Svea's Abuse Contact and the Limits of "Valid"
When Svea Ekonomi AB merged into Svea Bank AB on 3 January 2022, the group's abuse-contact surface in the RIPE registry did not follow the merger. Nearly four years later, the routed legacy netblock 193.105.138.0/24 still presents a mailbox on a third party's domain…

Story
Control Split: Who Held Prevention and Detection on the Svea Abuse-Contact Surface
Svea Ekonomi AB merged into Svea Bank AB on 3 January 2022, but the RIPE registry entities that describe the group's abuse-contact surface have barely moved since 2021 and 2022. A timestamp-by-timestamp reading shows that recent maintenance in this chain fell almost entirely on…