
Summary
- Singapore’s 2026 strategy and enhanced NC3 aim to connect national threat intelligence with earlier detection and coordinated response, while the published plan leaves capabilities at different stages of development.
- A shared cyber picture improves coordination only if the path from signal to recommendation, authority, operator action and correction remains reconstructable without exposing sensitive infrastructure details.
A common picture is a new control surface
Singapore launched its Cybersecurity Strategy 2026 on 13 October. The strategy sets a whole-of-nation direction: protect critical infrastructure, secure the wider digital ecosystem, prepare for AI and quantum risks, deepen international partnerships, and build capabilities and a future-ready workforce. The launch is a policy commitment, not a report card on delivery.
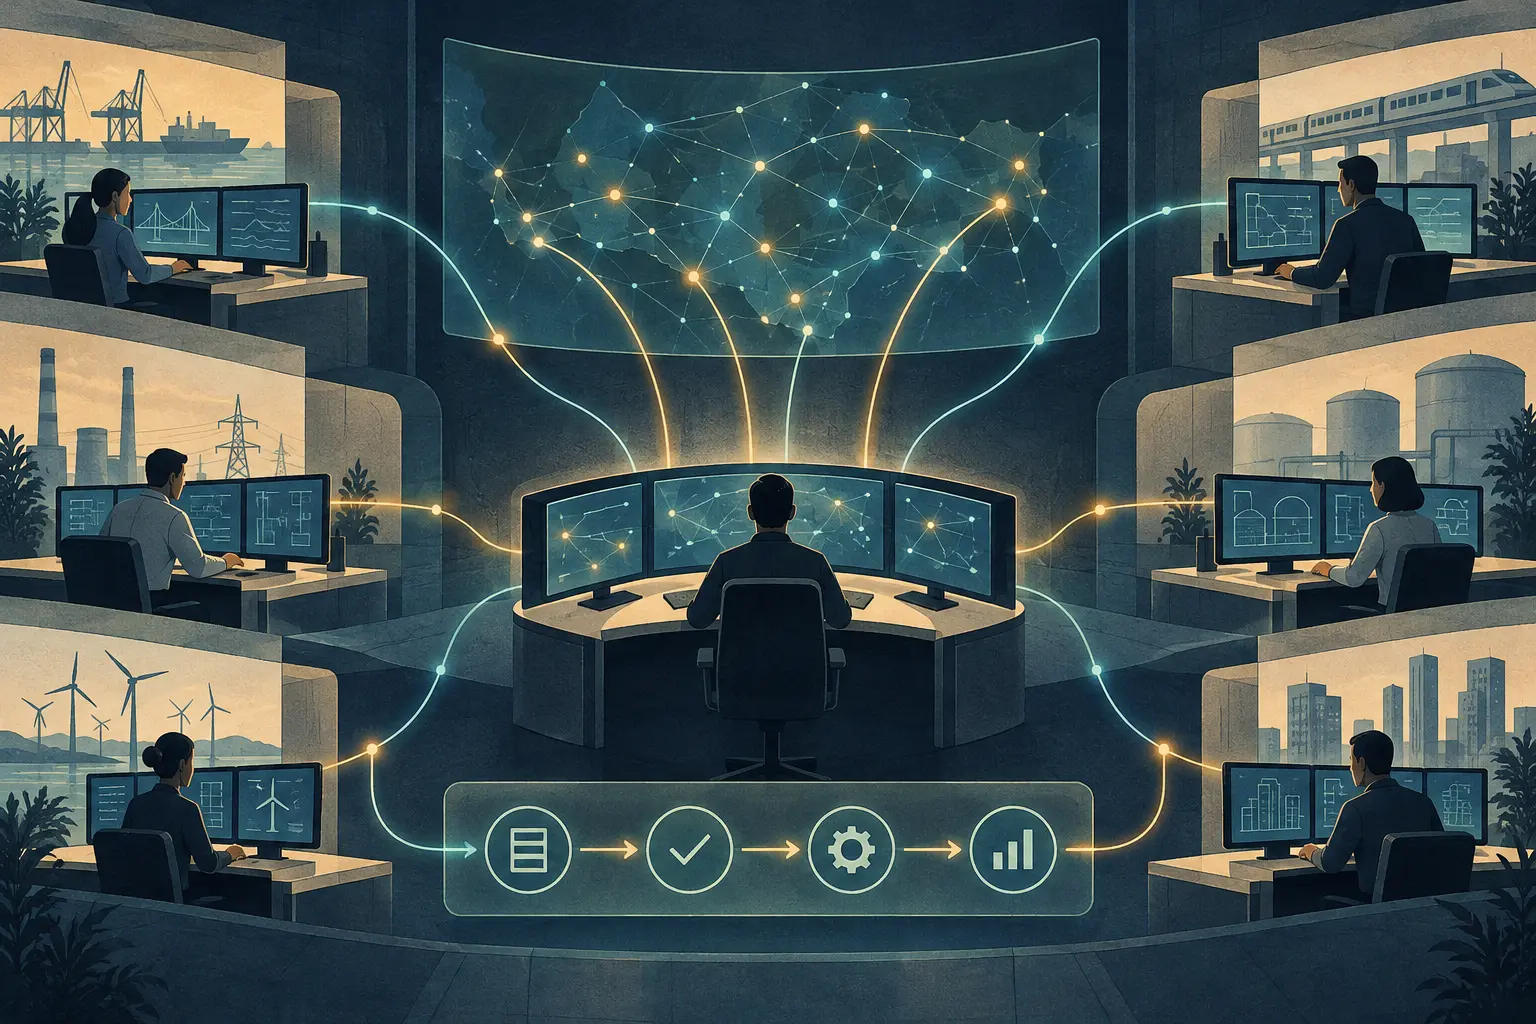
The same day, the Cyber Security Agency (CSA) described enhancements to the National Cybersecurity Command Centre. NC3 is CSA’s national operations hub. It is intended to fuse threat intelligence from multiple sources, help defenders anticipate risk, and coordinate action across government agencies and critical-information-infrastructure (CII) owners.
The announcement also describes a national Protective Domain Name Service (PDNS) that blocks known malicious domains under the Online Criminal Harms Act, with safeguards; more visibility of CII owners’ internet-facing assets; and detection systems being progressively installed at selected owners. AI-enabled systems are to help track incidents, form operational assessments and plan next actions. CSA says these capabilities will continue to develop.
That detail matters because “national picture” can sound like a transfer of command. The public announcement instead describes a coordination and support layer that complements individual CII owners. The Cybersecurity Act overview says owners remain responsible for the cybersecurity and resilience of their CII even as they adopt cloud and other operating models. Better shared visibility therefore makes the allocation of decisions more important, not less.
Information fusion does not decide what an operator should do
A threat signal is not yet an operational instruction. It may be incomplete, stale, relevant to one system but not another, or strong enough to justify immediate containment. A national team may see patterns an individual owner cannot see; that owner may understand dependencies, service consequences and safe recovery paths that are invisible from the centre. The decision chain has to preserve both kinds of knowledge.
Singapore’s 2026 Code of Practice for Critical Information Infrastructure gives that division a concrete institutional setting. The Code assigns boards oversight of cybersecurity strategy, adequate resources and risk appetite, and requires material decisions to be effective and timely. It also calls for a documented resilience framework, annual review, board minutes, and threat briefings every six months. Specified new board and senior-management requirements have a 29 July 2027 compliance date for existing CII owners. The timetable leaves room for preparation; it does not make the responsibilities optional.
The Code also establishes a separate timetable for specified detection, exercise, asset-management and interconnected-system provisions. Other provisions not listed in its compliance table are described as existing requirements that should be followed from the Code’s effective date. The useful governance question is not whether the central dashboard is comprehensive. It is whether the owners’ own decision records can show what the signal meant locally, who accepted the risk, who acted and what happened next.
Build a protected action record, then publish only safe measures
An operational record could connect each recommended intervention to its source and timestamp, an evidence-confidence assessment, the affected owner and system scope, the person or office making the recommendation, the authority approving or directing action, the owner’s acknowledgement, the action taken and the observed outcome. If the operator departs from a recommendation, the reason and decision owner should remain visible to authorized reviewers. A correction, false positive or changed assessment should append to the history rather than silently overwrite it.
This is a design proposal, not a claim that Singapore has no such records. The public material reviewed here does not describe a common, end-to-end decision log or publish comparable rates for detection, containment, reversals and correction. Nor should a public log expose threat intelligence, exposed asset inventories, CII topology or details that help an attacker. The operational trail can remain restricted; an external report can aggregate process measures such as time to acknowledge, time to decide, time to contain, correction frequency, and completion of post-incident review, with appropriate suppression and context.
PDNS makes the need for correction especially legible. Blocking a known malicious domain can reduce exposure, and CSA says the measure is grounded in OCHA and subject to safeguards. That does not establish that a particular block was mistaken or that safeguards failed. It does identify a decision with real effects for people and services. A durable process should let an authorized party contest a classification, assess the evidence, restore access when warranted and preserve why the original action was taken.
The same pattern applies to asset remediation priorities and AI-assisted assessments: advice should retain its provenance, and a human decision-maker should be identifiable where an action has material service consequences.
The incident-reporting instructions provide another observable clock, though their scope must not be blurred. For provider-owned CII, listed steps include an initial verbal notice within two hours of awareness, supplementary details within 72 hours and a final report within 30 days after those details. Separate instructions address third-party-owned CII and designated providers. These deadlines can help test whether information moves through the reporting system; they do not by themselves measure whether decisions were sound or services recovered safely.
Singapore’s strategy is moving coordination earlier in the threat lifecycle. That can improve resilience when central visibility and local authority meet in a record that is secure, attributable and correctable. The national picture should make coordinated action possible. The decision trail should show who acted, on what evidence, under which authority and with what review after the urgency passed.
Sources
- CSA — Singapore launches Cybersecurity Strategy 2026
- CSA — NC3 enhancements
- Cybersecurity Code of Practice for Critical Information Infrastructure 2026
- CSA — Cybersecurity Act overview
- CSA — Cybersecurity incident reporting forms and instructions
- CSA — Singapore International Cyber Week opening address
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance