
Topic
Security Automation
Within the Topic facet, Security Automation topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.

Global Cloud Services
Ivanti's own scanner said clean. Ivanti's own words say that proves little.
No leak was needed to establish the limit of the Integrity Checker Tool. The vendor wrote it down itself, in the knowledge-base article it maintains for CVE-2023-46805 and CVE-2024-21887 on Ivanti Connect Secure and Ivanti Policy Secure. The sentence customers should read twice…

CASE FILE
DigiCert Gave Itself 24 Hours, Then Granted Itself 120 More
A missing underscore in DigiCert's own domain validation started a revocation clock with a 24-hour fuse. The party under the obligation then recalculated the fuse, granted itself five more days, and published the only timeline anyone has.
IETF
GOAWAY Can Send a Relay's Audience to Your Server
A Media over QUIC relay can tell connected clients where to resume. The November threat analysis points to the ugly version: one relay names an unrelated host, and its audience obediently makes that host's day worse.
Creators
Barry O’Donovan’s CRA test: one software team, two roles—one product at a time
At RIPE 93, the INEX developer argued that the Cyber Resilience Act can assign different roles to the same organization across different products. For network operators, the label changes who handles security work upstream.
Leaders
Darren Kara Is Adding DNS Sites. The User Cannot Become the Debug Log.
A small engineering team can add resolver locations faster than it can hire a new army of operators. Kara's harder job is seeing enough to run that network while leaving a visitor's address out of its durable records.
IETF
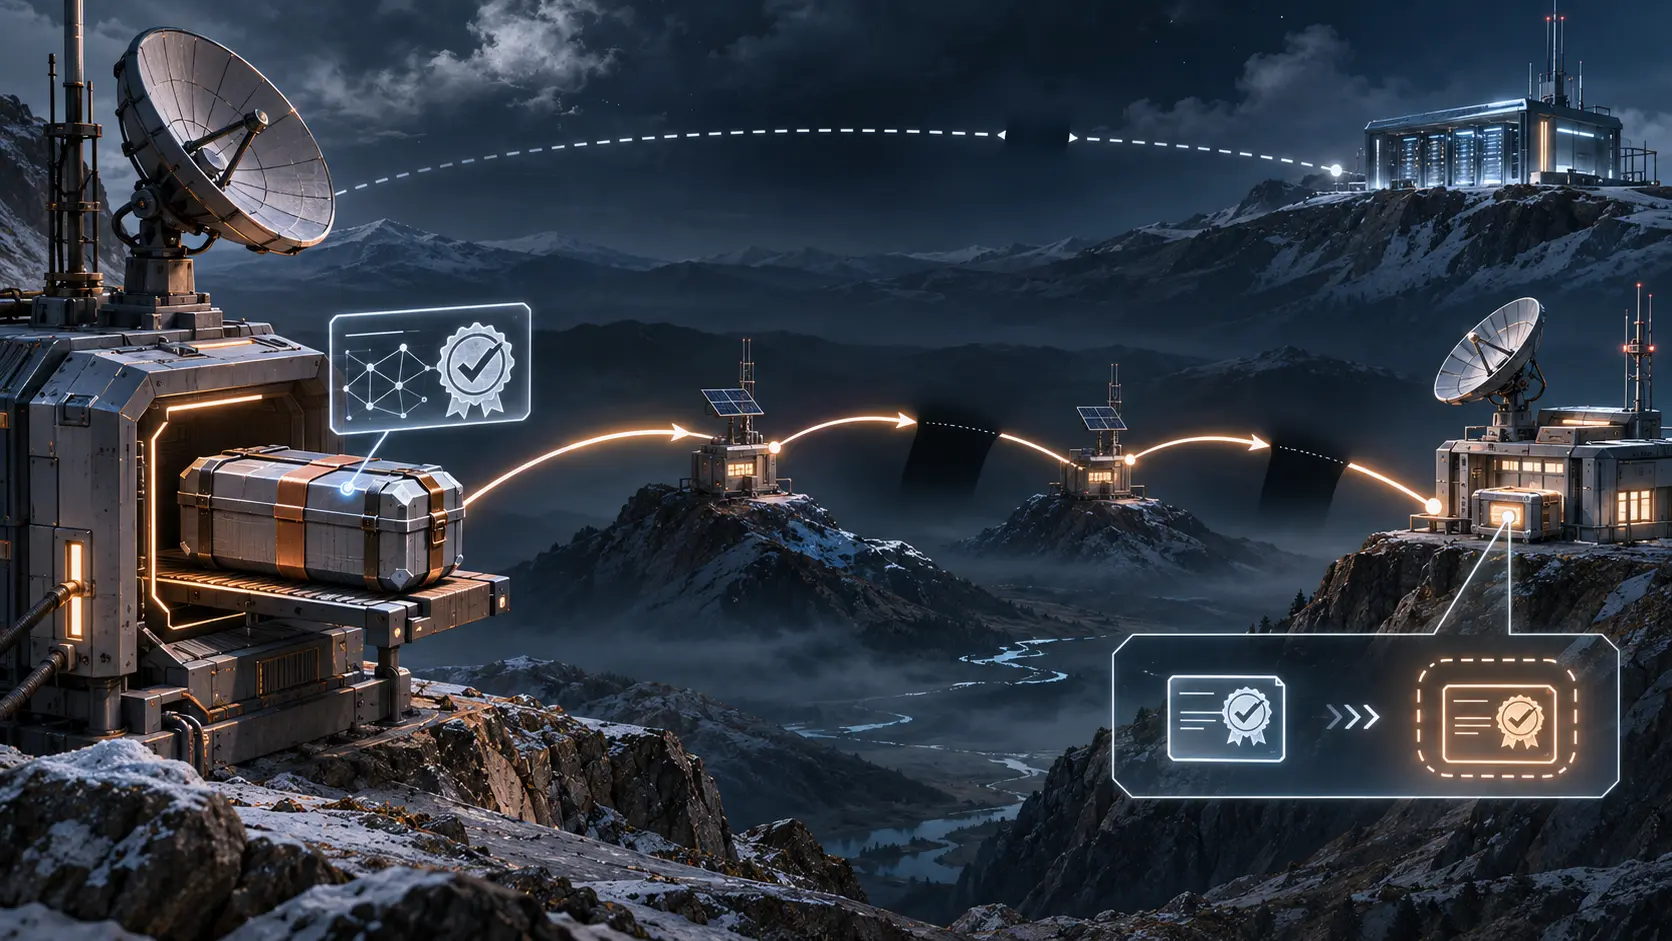
The Bundle Arrived. Its Revocation Server Did Not.
A signed message can cross a broken network while a certificate-status query cannot. A 2 November IETF revision puts that contradiction in the operator’s hands: choose a reachable OCSP responder, or move the online work toward short-lived certificate issuance.
IETF
The Bootloader Has the Room. The Firmware Update Does Not.
A post-quantum signature can look affordable when a device is starting up and much dearer when it is still doing its job. An IETF draft headed for a 5 November review forces buyers to specify which moment their update system uses.
IETF
One Mobile Session Gets Its Own Route. Two Drafts Hold the Instructions.
A 2 November IETF revision puts a sharper edge on Mobile User Plane routing: a controller can turn one mobile session into a route that beats a broader VPN path. The DMM draft now states which behaviour is normative, while a separate BESS draft holds the BGP bytes. The handoff…
IETF
The Quantum Door Has a Classical Lock in Eight MLS Suites
An IETF draft offers eleven new cipher suites for secure group messaging. Eight use post-quantum key encapsulation but keep traditional signatures; three add ML-DSA signatures. The November revision now spells out what a forged classical signature could do to a later group epoch…
IETF
Two Certificate Teams, One DNS Name: IETF Splits the Gate
Two independent systems can serve one domain and still fight over the single DNS alias used to prove control of it. An IETF draft gives each ACME account its own validation name. The bargain moves a piece of certificate continuity onto the exact spelling of the account URL.
IETF
The Call Can Pass Before the Duplicate Certificate Is Caught
A proposed telephone-identity certificate log gives a call verifier a signed receipt it can check without waiting for the log. The same speed leaves the conflict hunt to a monitor working on another clock. If two certificates claim the same number for different parties, the first…
History
CVE Named 321 Security Problems. The Fixes Were Somewhere Else.
When CVE launched in September 1999, its first public list held 321 entries. It did not ship 321 patches. It gave scanners, advisories and software vendors a way to stop arguing over whether their different labels referred to the same flaw. That narrow ambition was the…
CASE FILE
Thirteen Countries Joined Europe’s Cyber Alarm. Its First Two Hubs Couldn’t Sound.
Europe recruited countries for a shared cyber alarm before it finished the equipment order or agreed how a warning would travel. An audit of the European Cybersecurity Alert System found its first two cross-border hubs, ATHENA and ENSOC, unable to operate. The delay was built…
Europe and Middle East Institutional Trends
Finland Calls the Sender “Spam.” Your Restaurant May Still Have the Table.
Finland has tightened the identity check on business messages. A failed check can now erase a sender's name and replace it with “Roskaposti”, even when the message confirms a real booking.
History
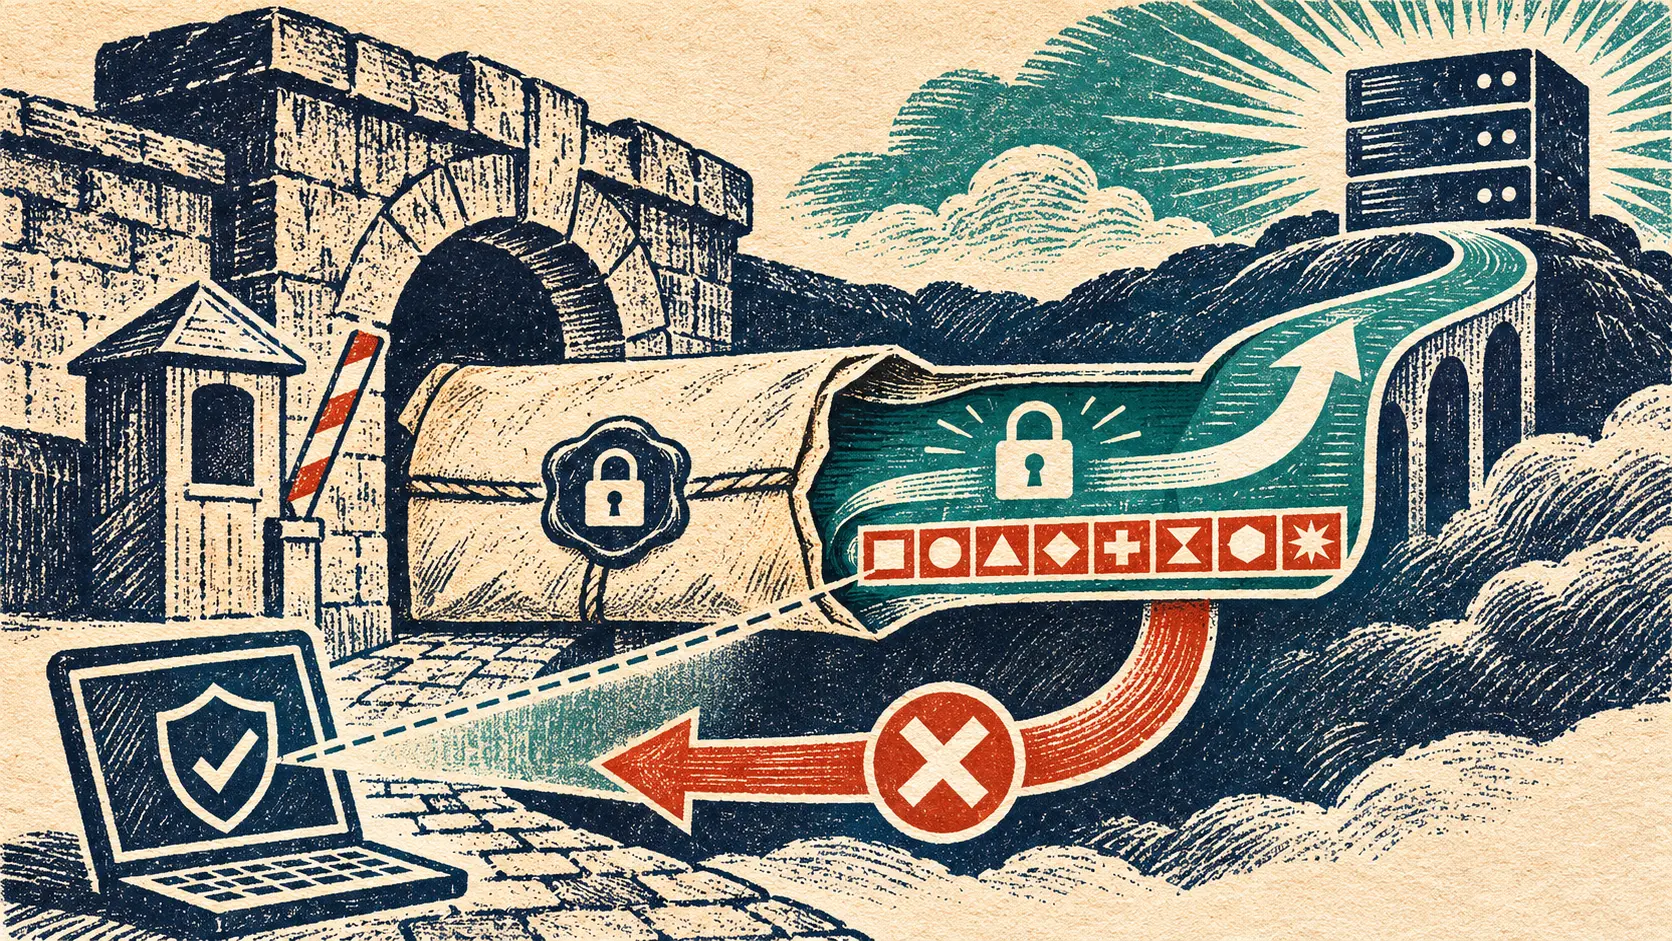
TLS 1.3 Wore a TLS 1.2 Name Tag. It Hid a Downgrade Alarm in Eight Bytes.
The newest version of a security protocol introduced itself with an old version number. A TLS 1.3 handshake left `0x0303`, the number for TLS 1.2, in a field that earlier software expected to read. The actual version traveled in an extension. That apparent costume was part of the…
History
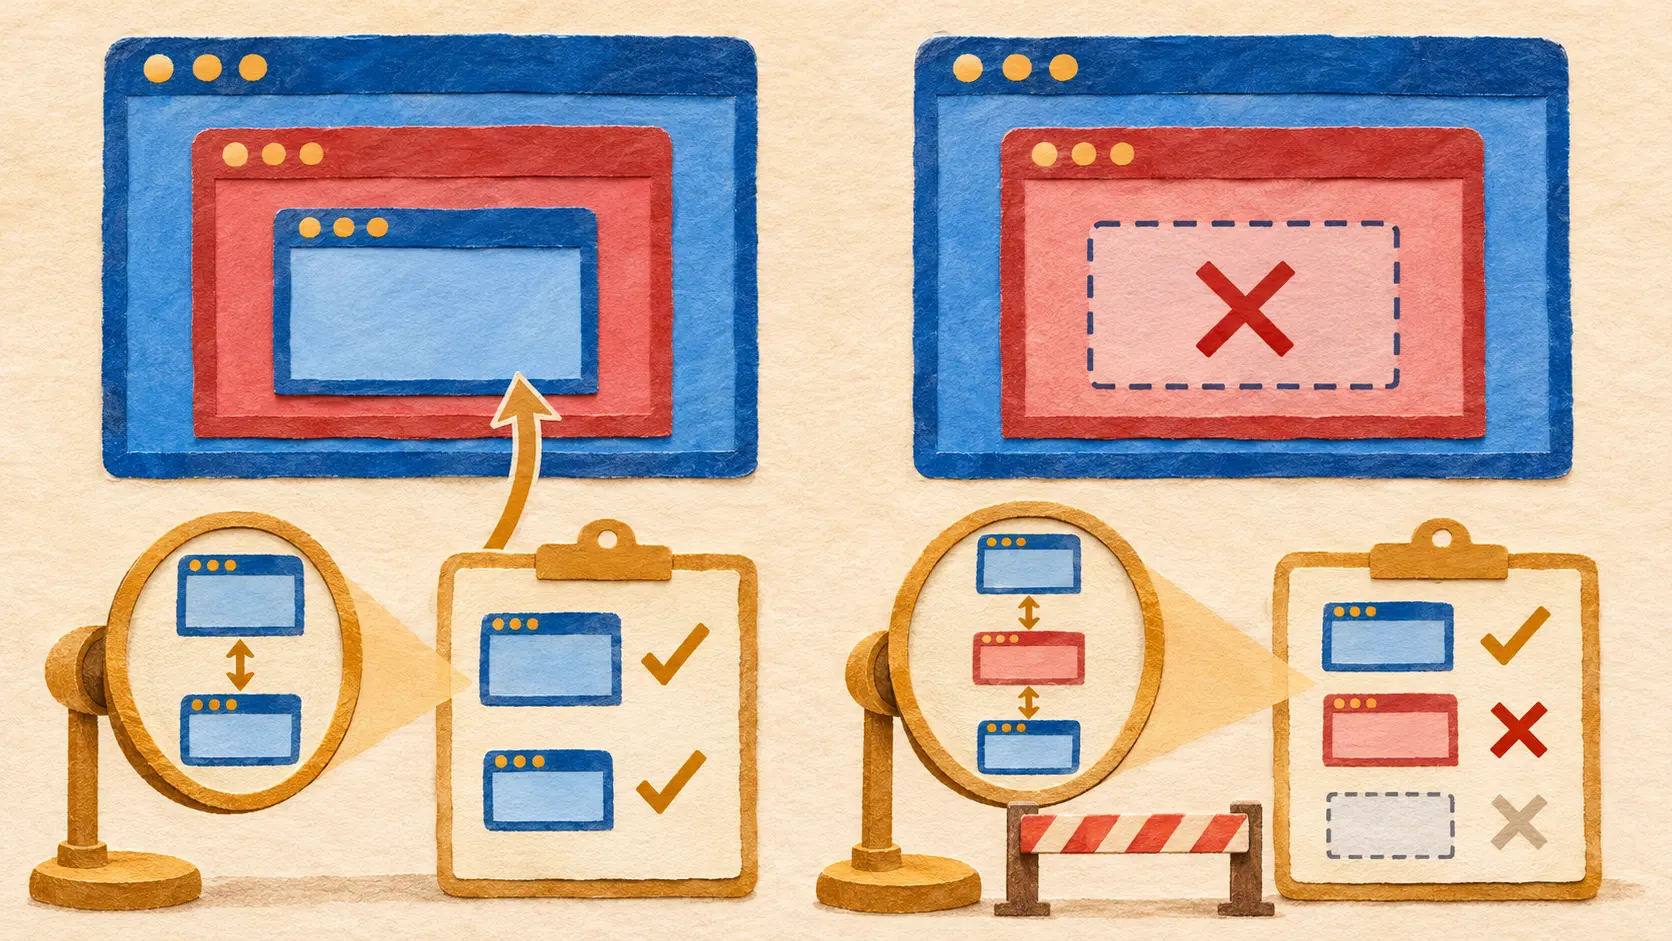
The Page Said SAMEORIGIN. The Browser Missed the Frame in the Middle.
A protected page and the top page shared an origin. The untrusted page between them was the problem that a shallow browser check could miss.
History
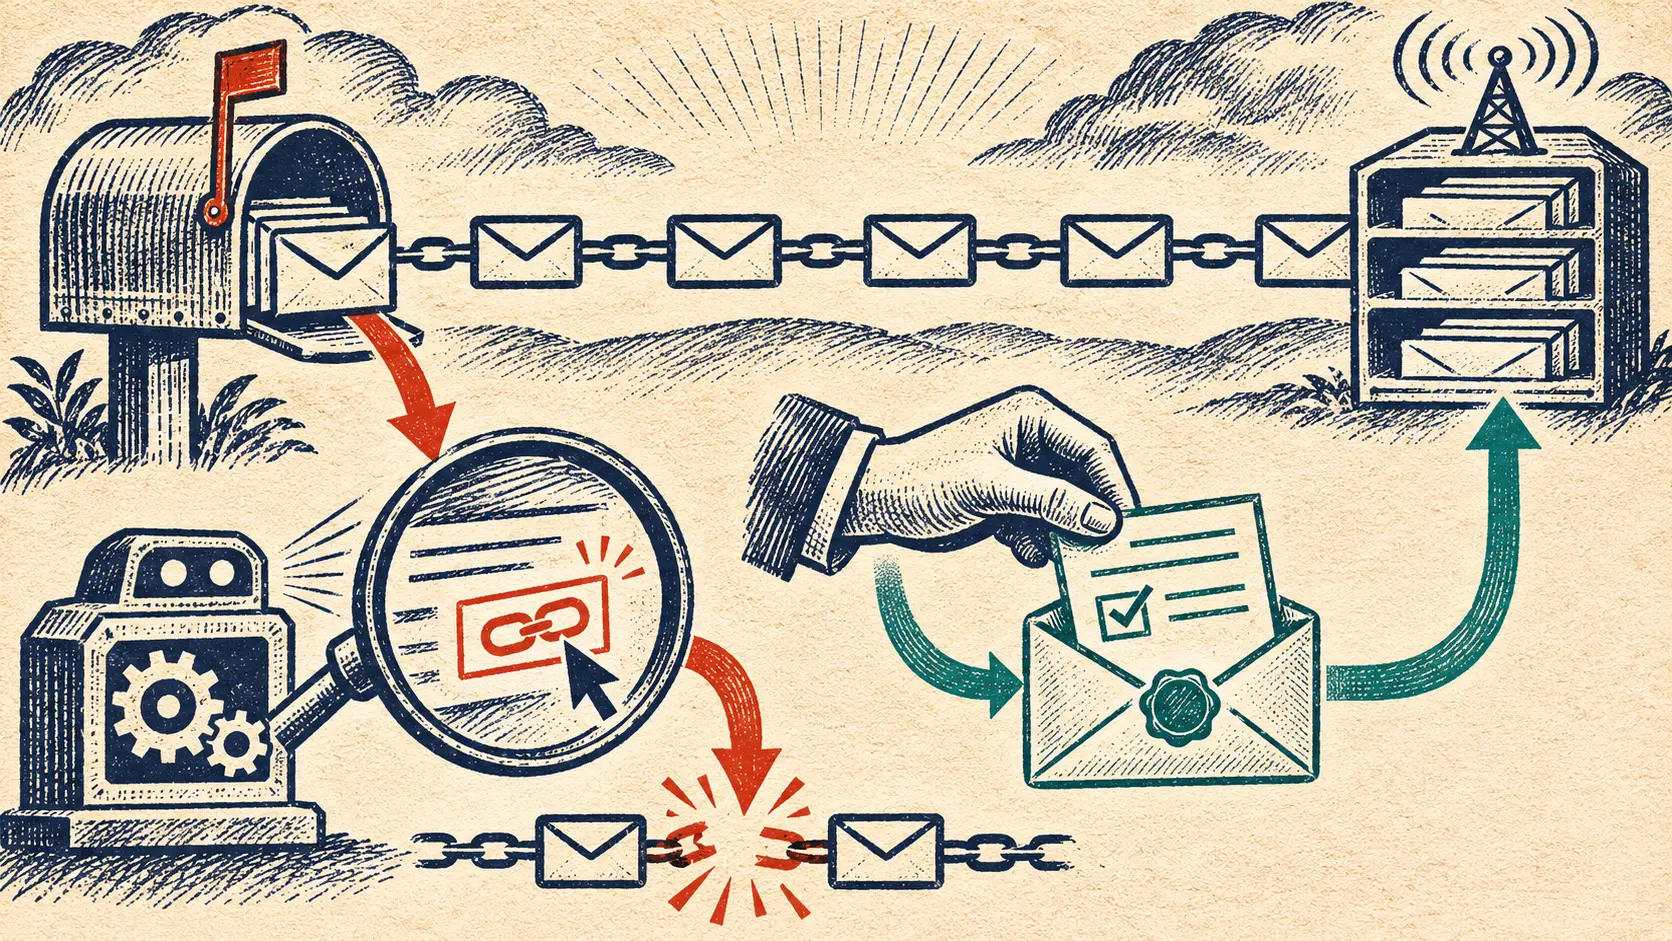
The Spam Filter Opened a Link. The Mailing List Lost a Reader.
An email filter opens a link to inspect it. The mailing list treats the visit as an instruction to remove its reader. No person asked to leave; a machine merely looked. That was the trap behind a convenient feature of email, and it drove a precise repair in January 2017. [RFC…
IETF
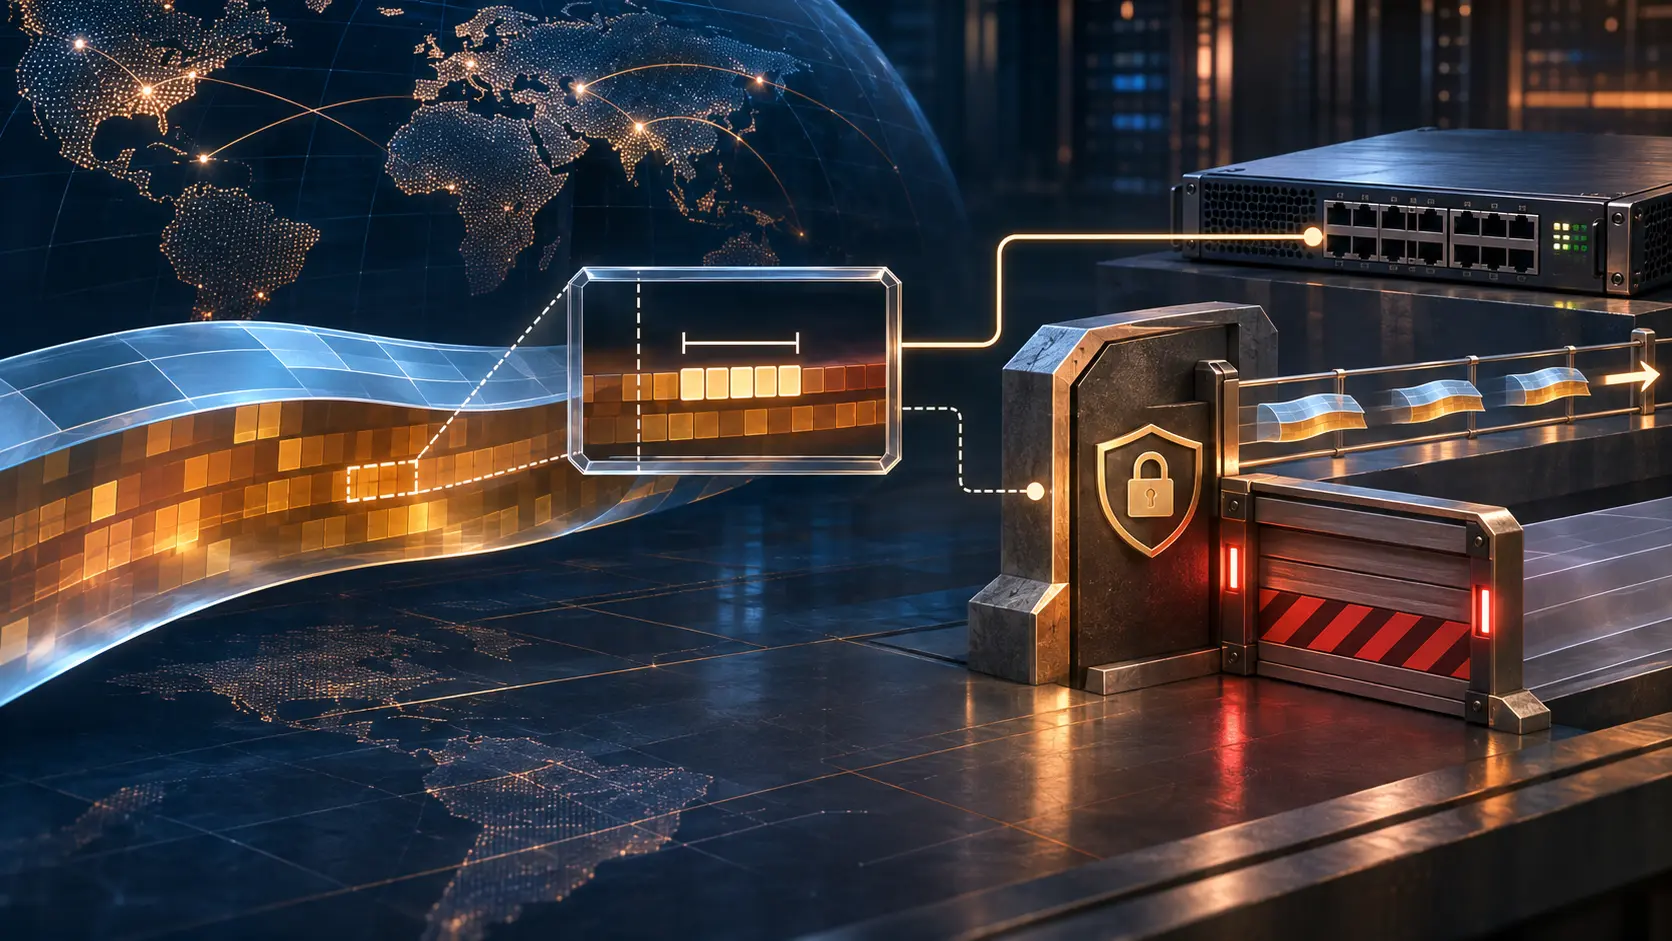
A BGP Rule Can Name Packet Bytes. A Blind Box Must Refuse the Whole Filter.
An IETF working-group draft lets FlowSpec describe a fixed byte pattern inside traffic. The hard rule is what happens when a device cannot inspect it: the remaining, broader filter must stay off.
IETF
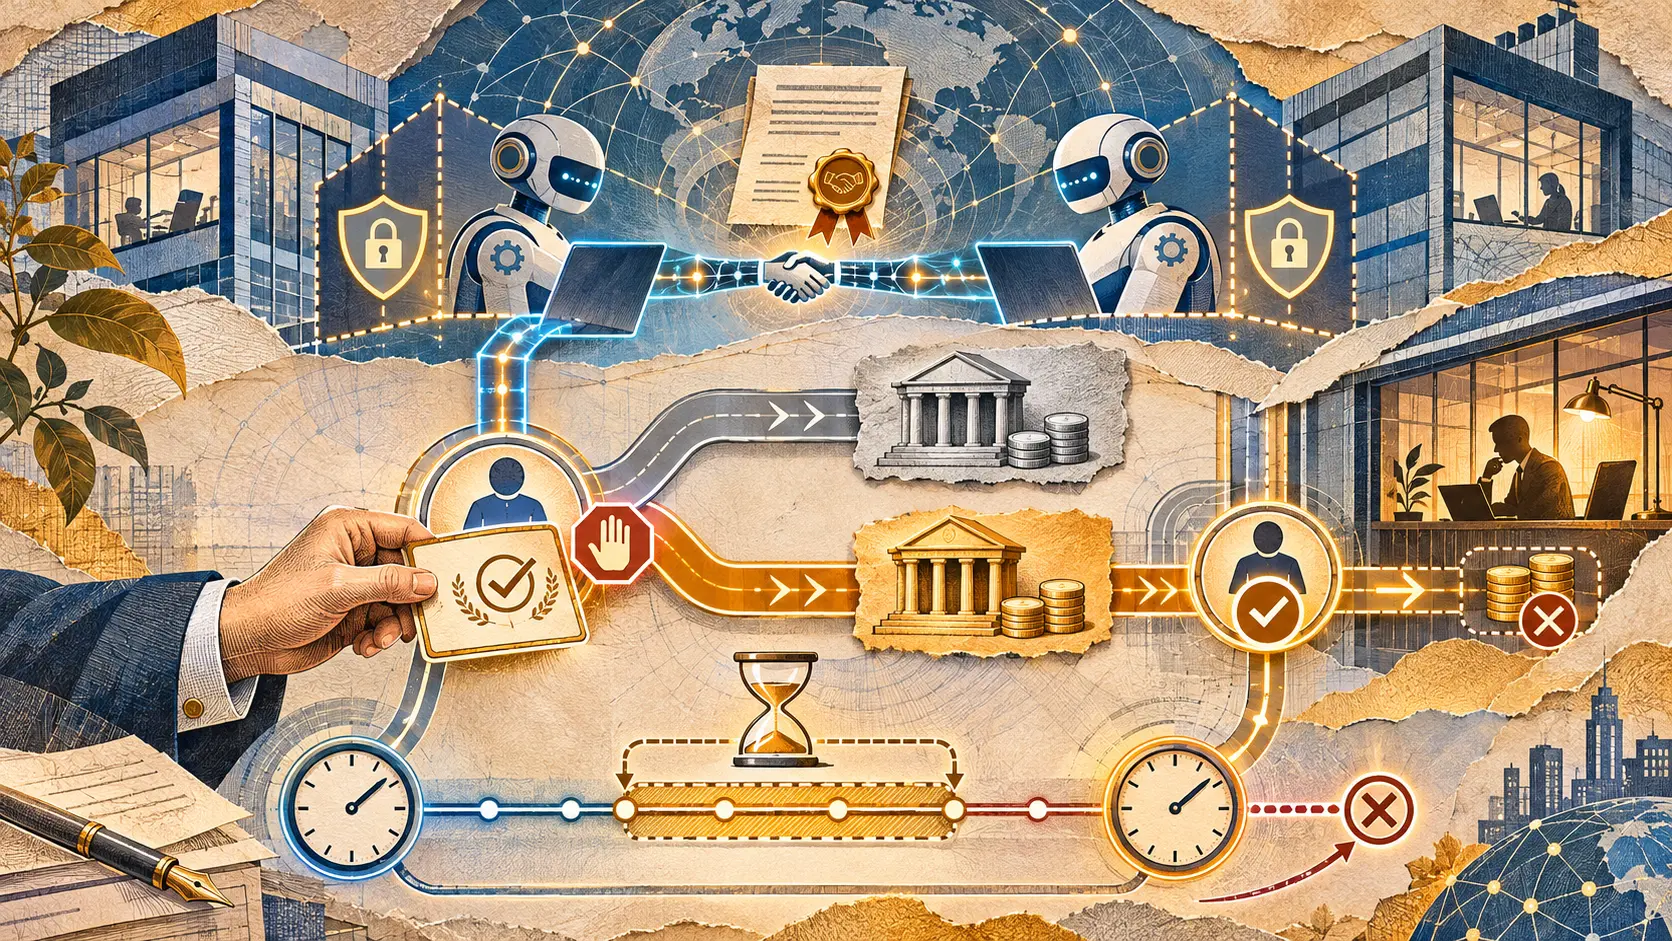
Selo Lets Agents Bargain. Humans Must Move the Bank Details.
Two companies can let software negotiate access to their systems. When the supplier asks to change where the money lands, a new Internet-Draft puts people back between the request and the first payment.
Latin America and Caribbean Institutional Trends
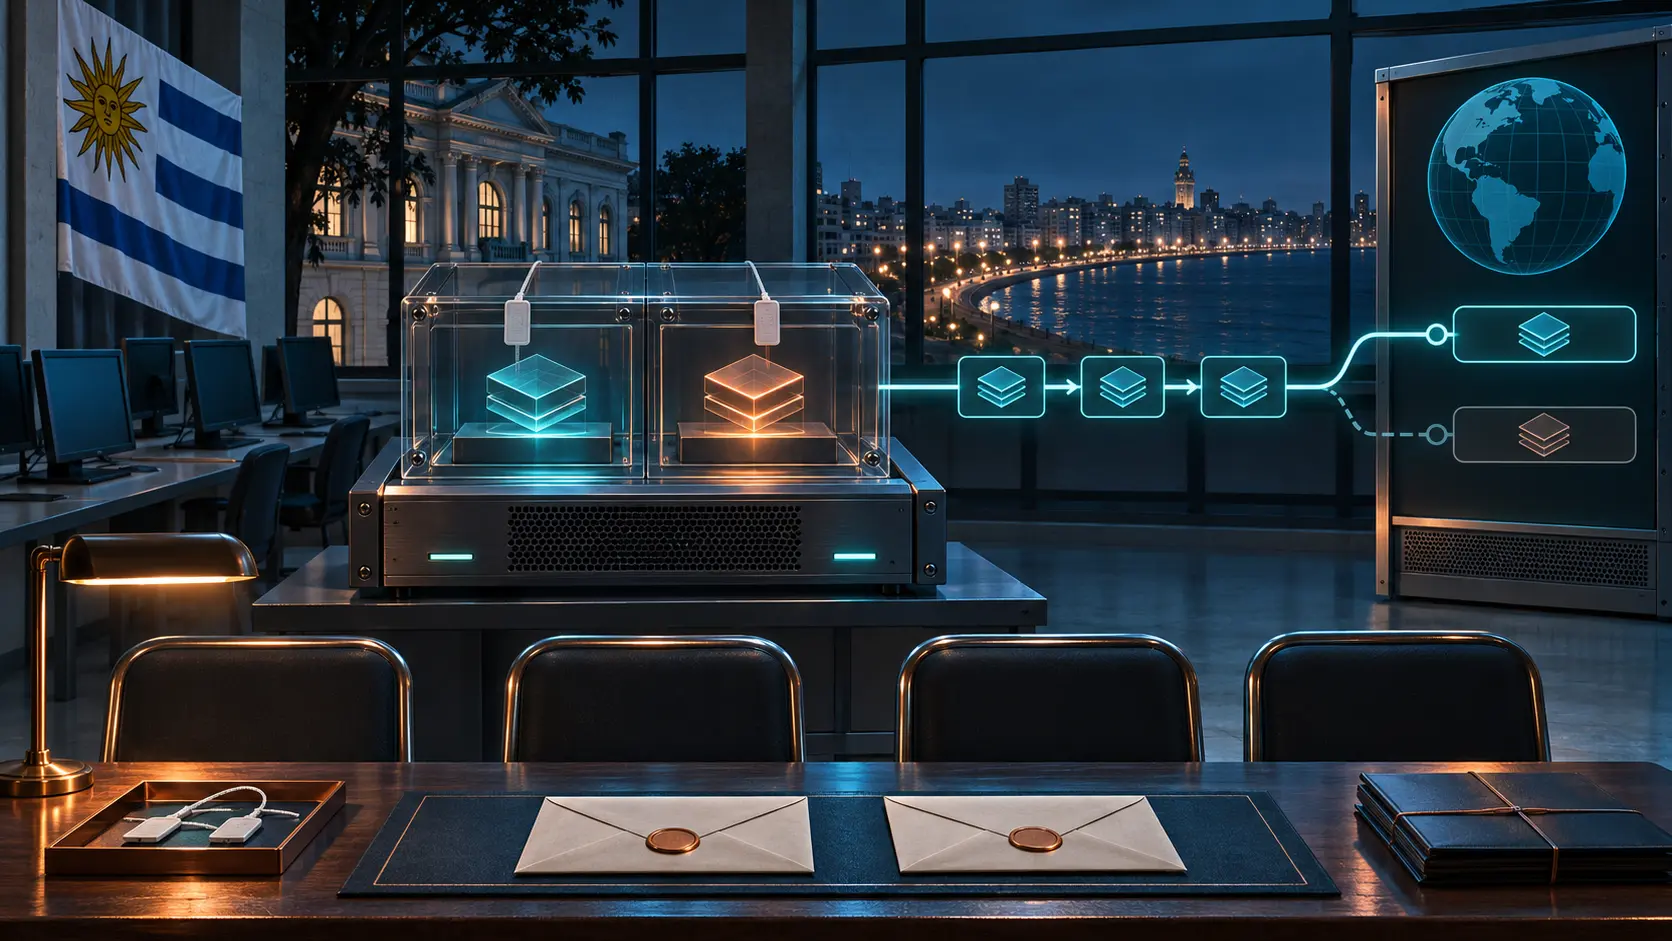
Uruguay Cut Keys for a New DNS Algorithm. Its Root Record Still Says 8.
SeCIU replaced the .uy security module and generated keys for today’s algorithm and a future one. The IANA delegation still displays one algorithm-8 DS record. A key ceremony is the first move, not the cutover.