Summary
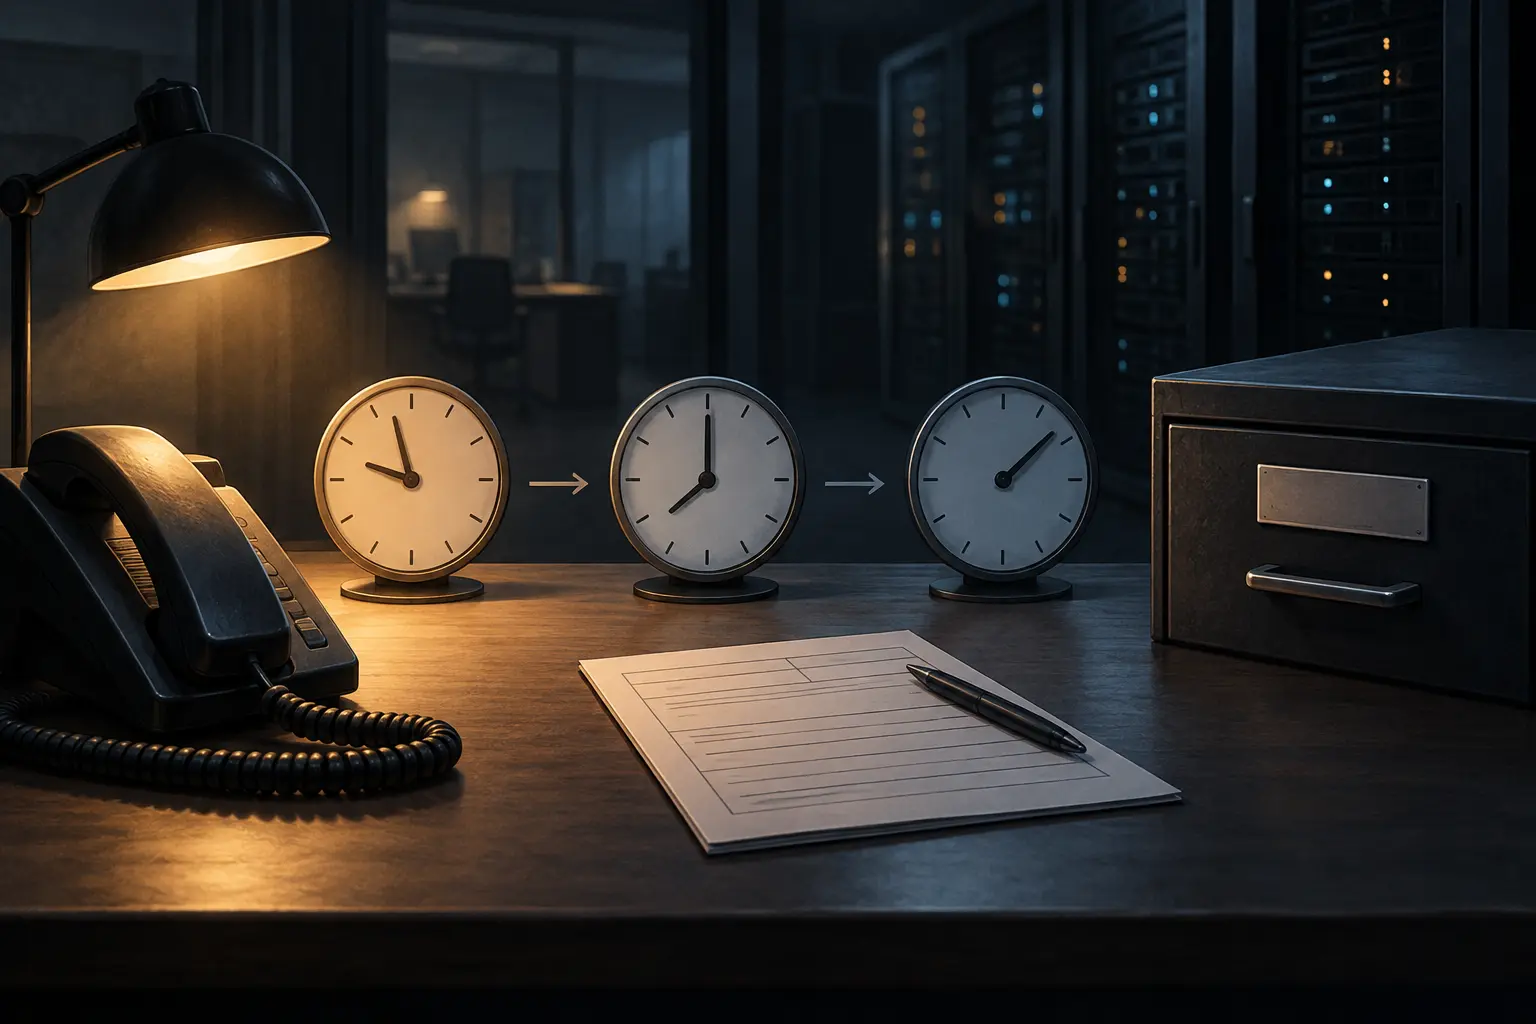
- Singapore’s ESCI regulations took effect on 30 October: an initial report is due within 24 hours of awareness, a written supplement within 72 hours and a final report 30 days after that supplement is submitted.
- The Cybersecurity Act lets the Commissioner designate an entity and system by written notice, but says that notice need not be published in the Gazette. The law makes the clock visible without guaranteeing a public list of who is on it.
A deadline can be public even when the people required to meet it are not. Singapore’s new cybersecurity rules put that tension on the page.
The Cybersecurity (Entities of Special Cybersecurity Interest) Regulations 2026, S 791/2026, came into operation on 30 October. They give the reporting process three stages. An entity must notify the Commissioner within 24 hours after becoming aware of a prescribed incident affecting its system of special cybersecurity interest. The first notice goes by telephone; text or written submission is allowed if a call cannot be made within a reasonable time.
The first report is not a polished post-mortem. It identifies the system, describes when and how the event occurred, says whether data availability, confidentiality or integrity was breached or business operations were significantly affected, describes the data stored there and records the observed impact. It also names the person making the report. Within 72 hours of awareness, the entity must provide a written supplement, to the fullest extent practicable, with updates, the cause, system impact and remedial measures. The final report is due within 30 days after that supplement is submitted; Sundays and public holidays count.
If the first two reports arrive at their latest permitted times, the final deadline falls about 33 days after awareness.
The clock covers a defined class. Under section 18 of the Cybersecurity Act, the Commissioner may designate an entity that stores sensitive information in a system under its control, or uses a controlled system for a function whose disruption would significantly harm Singapore’s defence, foreign relations, economy, public health, public safety or public order. The entity must be incorporated or established under written law. The prescribed incidents include unauthorised hacking, malicious code, interception or session hijacking, and denial-of-service or other unauthorised acts that impair system availability or operation.
Section 18F also requires a qualifying effect: a breach of data availability, confidentiality or integrity, or significant impact on the entity’s business operations.
Here is the governance wrinkle: the written designation notice identifies the entity and system, sets out duties, names a supervising officer and explains representation and appeal routes. Section 18(4) says the notice need not be published in the Gazette. The official material reviewed for this article names no recipients or separate public register; a CSA register or notice would show whether outsiders can identify the entities covered.
Part 3C also excludes an entity in relation to systems already designated as provider-owned or third-party-owned critical information infrastructure. This reporting lane therefore has its own boundary beside Singapore’s CII rules.
The public can now read when a report is due and what it must contain. It cannot infer from S 791 alone which operators have received a designation. A named, bounded register could expose the reach of the regime without publishing sensitive system details. The next useful record is a CSA designation notice or a public explanation of how the agency will disclose the covered class.
Sources
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance