
Content Type
Profile
Within the Content Type facet, Profile intelligence gathers BTW.MEDIA articles that share the same editorial format, helping readers compare briefings, profiles, risk notes, market analysis, and event coverage without mixing different kinds of evidence. The page explains how this content type frames internet infrastructure events, company movements, governance decisions, operational signals, and public evidence across the site. Readers can compare which actors or infrastructure systems appear most often, how source quality changes interpretation, and whether the material is a durable profile, a time-sensitive event, a strategic market signal, or a governance development. The result is a useful search page for operators, investors, customers, analysts, and policy stakeholders who need to understand the consequence, timing, and evidence behind similar article formats.

Global Institutional
FreeRADIUS and the trust decisions behind network access
A network login may be decided in a few packets, but the trust behind it can span certificates, directories, access devices, roaming partners and accounting systems. FreeRADIUS makes that policy inspectable and programmable, while leaving operators responsible for the legacy…

Creators
Dave Maltz and the operating stack behind Azure networking
Dave Maltz’s role at Microsoft is best understood through the breadth of the organisation he leads. Azure Networking spans customer-facing services, DNS, security, distributed control, host offload, switch software, data-centre fabrics, wide-area links and optical systems. That…
Global Institutional
BIRD and the routing policy engine behind internet exchanges
The BIRD Internet Routing Daemon grew from a Czech university project into a control-plane system used in demanding routing environments, including internet exchanges where policy is concentrated and operational mistakes can spread quickly. Its history shows how open routing…

Creators
Jakub Kicinski: How Linux makes network features supportable
A new network card can arrive with an impressive capability and a commercial deadline. Linux has to ask a slower question: can the feature be expressed in a way that other hardware can understand, operators can observe, tests can reproduce and maintainers can still support years…
Global Institutional
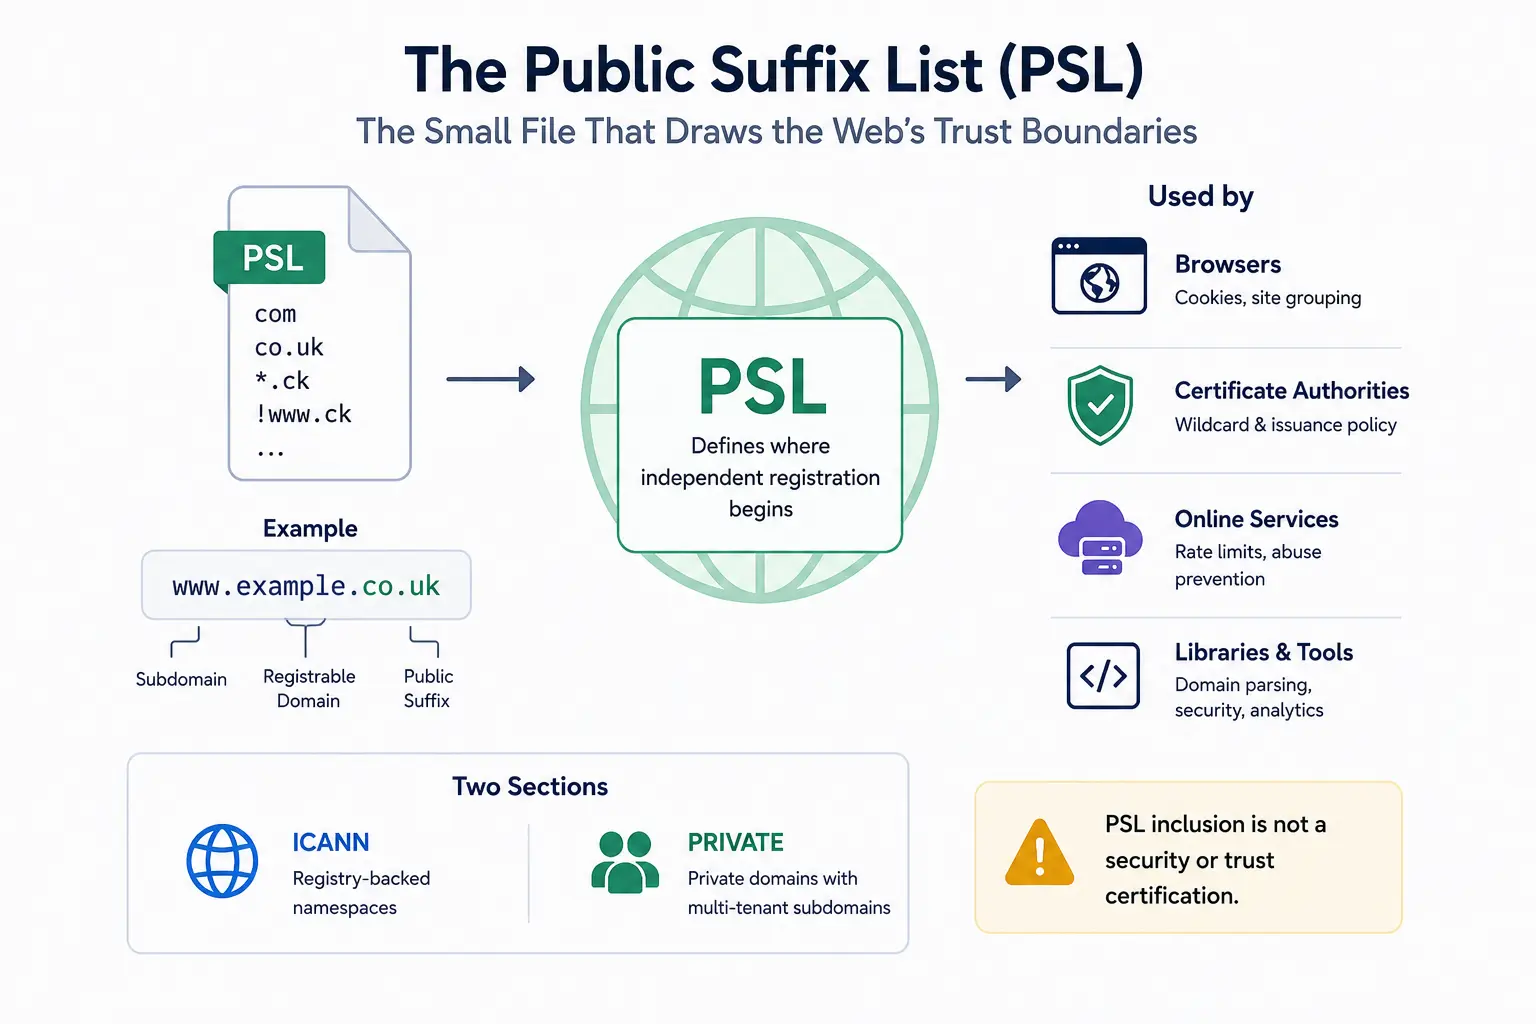
Public Suffix List: The File That Draws Web Trust Boundaries
DNS can show that shop.example.co.uk sits beneath co.uk; it cannot tell a browser where independent registration begins. The Public Suffix List supplies that missing policy map. A volunteer-maintained text file now informs cookies, site grouping, certificates and service limits…

Global Institutional
containerd: the runtime daemon most container users never see
Kubernetes, Docker and managed cloud platforms make containers look like applications, pods and services. Beneath those interfaces, containerd moves images, prepares filesystems, preserves runtime state and supervises processes. Its value comes from being deliberately incomplete…

Global Institutional
DMTF: The Standards That Control Servers Below the Operating System
A server can be powered off, inspected, updated or reconfigured even when its operating system is unavailable. DMTF defines much of the language used for that privileged management plane, from Redfish APIs and MCTP transport to PLDM commands, SPDM identity and SMBIOS inventory.…
Global Institutional
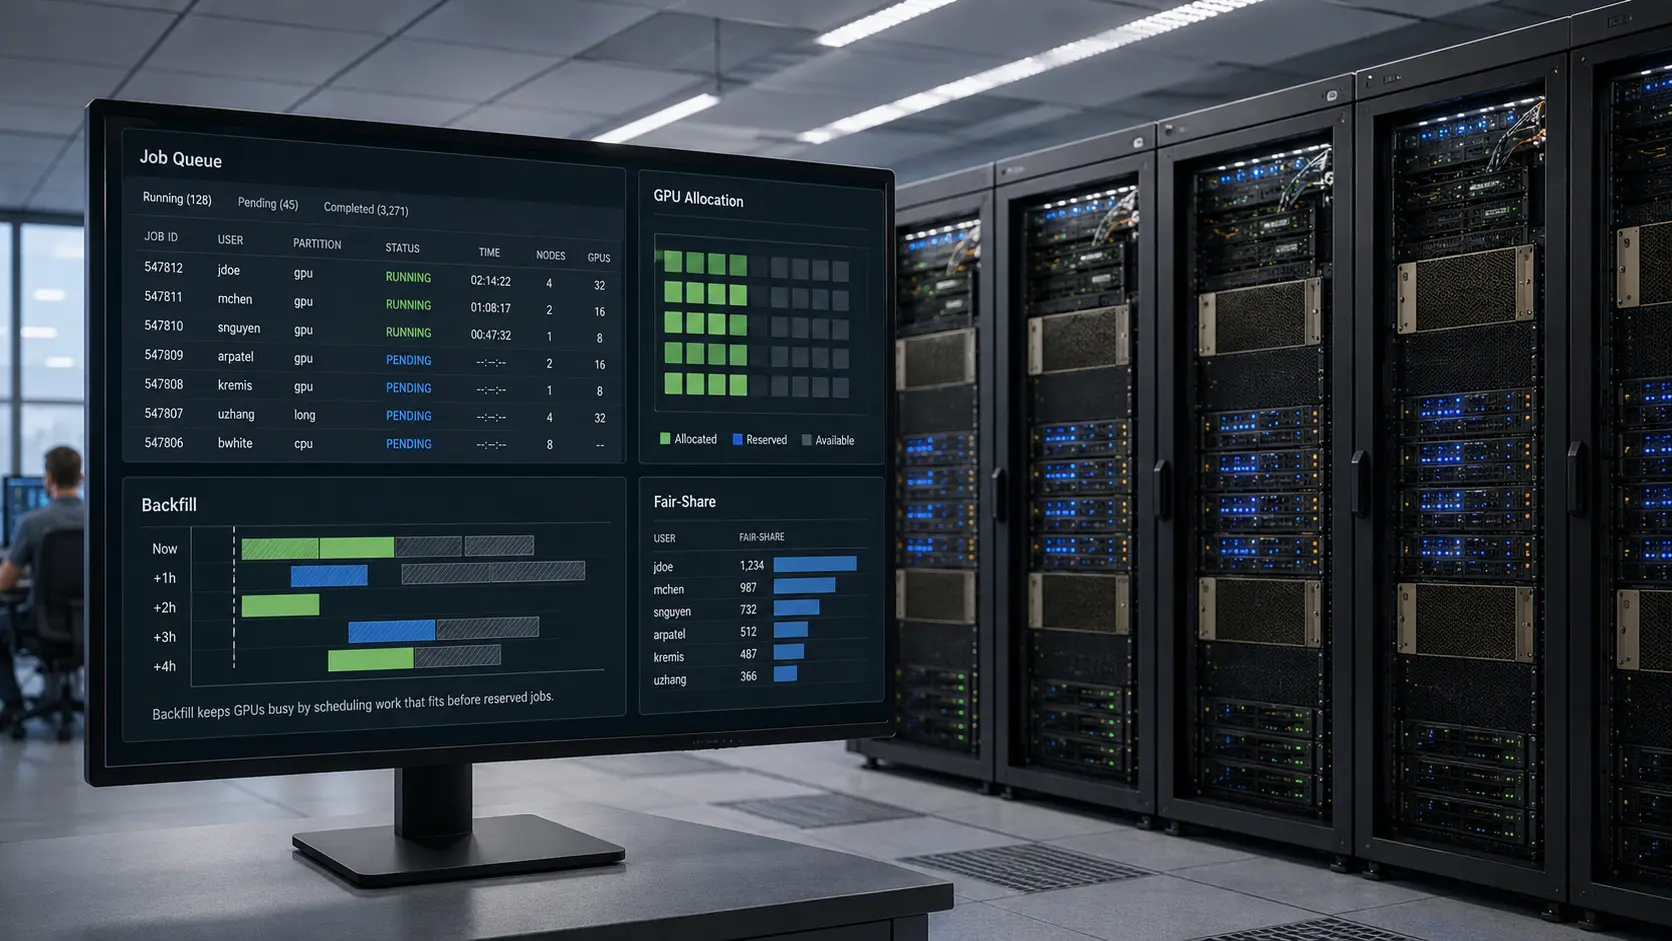
Slurm: The Scheduler That Decides Who Gets the GPU
Slurm allocates scarce compute across HPC and AI clusters, turning queue policy into a practical decision about who gets GPUs and when. NVIDIA’s 2025 acquisition of SchedMD gave the project more resources while making vendor-neutral stewardship a question that now has to be…

Creators
Sage Weil: the engineer who made distributed storage computable
Sage Weil’s most enduring contribution was not a storage device but an architecture. CRUSH calculates data placement, while RADOS distributes storage, repair and movement across the cluster. Ceph enabled ordinary machines to operate as one system, then had to learn to continue…
Creators
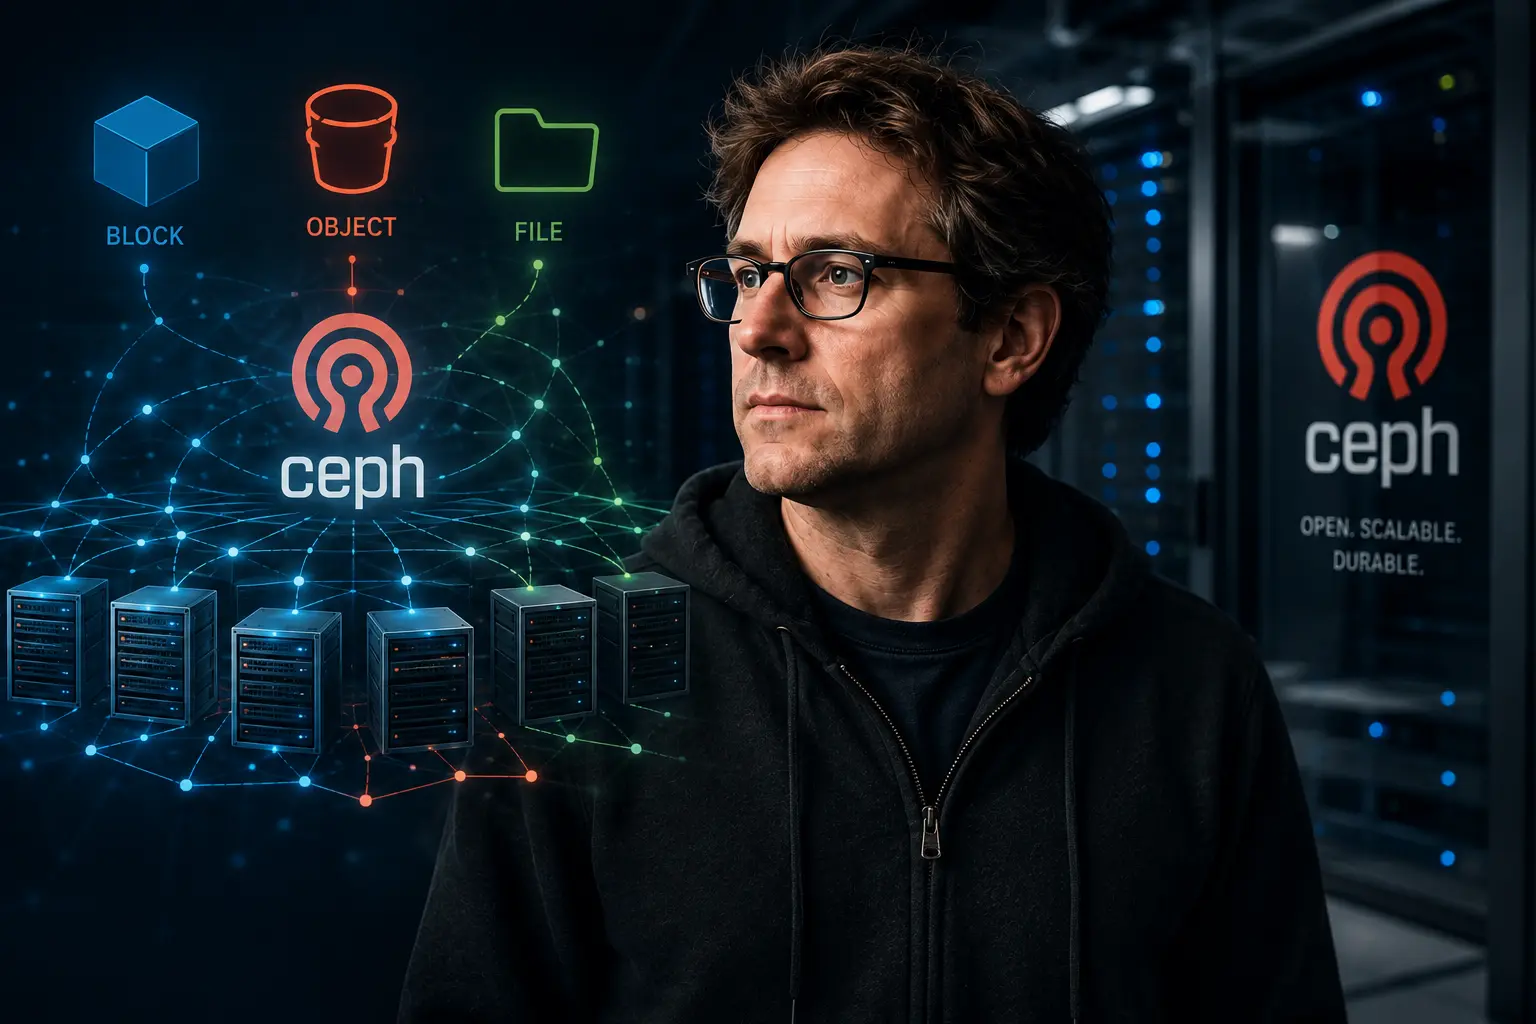
Sage Weil: The Architect Who Made Distributed Storage Calculable
Sage Weil’s most durable contribution to internet infrastructure was not a storage appliance but an architecture. Ceph used CRUSH to calculate where data belongs and RADOS to spread storage, repair and movement across a cluster. The design helped commodity machines behave like…

Global Institutional
NVM Express: how storage became a network protocol
NVMe began as a more efficient way to talk to the flash memory installed in a server. It has become a family of protocols capable of carrying the same command queues and namespaces over PCIe, TCP or RDMA. That continuity has made storage composable, while moving part of its…

Global Institutional
NVM Express: how storage became a network protocol
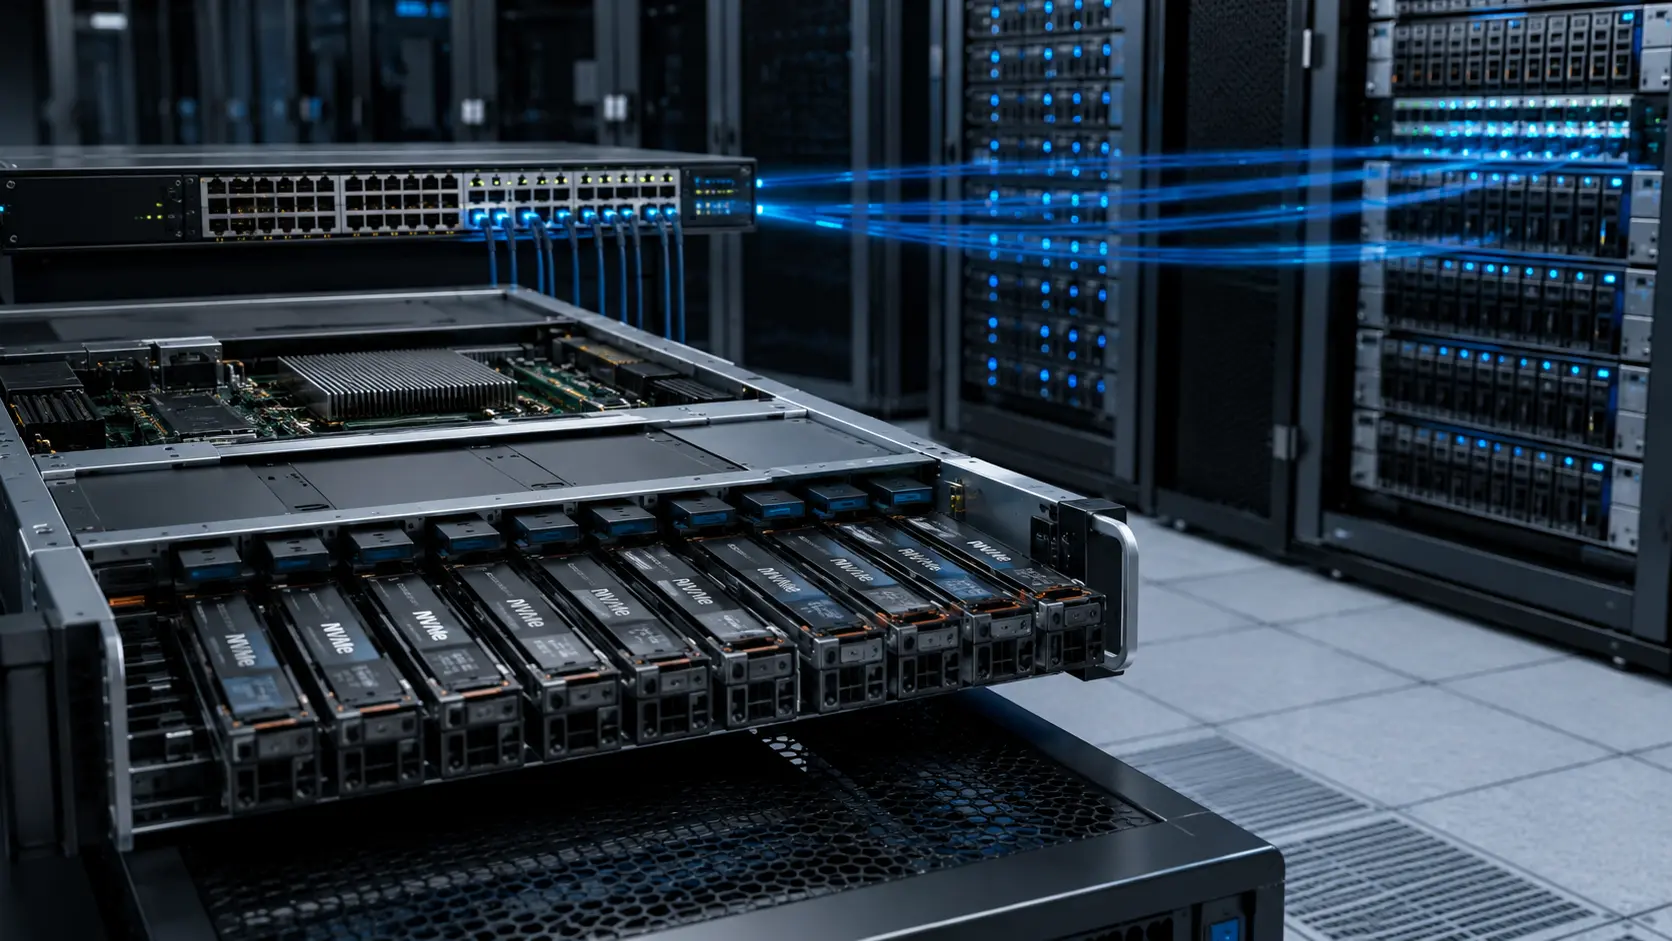
NVMe began as a more efficient way to communicate with flash memory installed inside a server. It became a family of protocols capable of carrying the same queue, controller and namespace model over PCIe, TCP or RDMA. That continuity enabled capacity to be disaggregated, but…
Global Institutional
NVM Express: How storage became a network protocol
NVMe began as a more efficient protocol for accessing flash inside servers and developed into a family of standards that carries consistent queue, controller and namespace semantics over PCIe, TCP and RDMA. It makes storage easier to pool and compose while shifting complexity…

Global Institutional
UCIe's chiplet promise depends on engineering and accountability beyond the link
UCIe has pushed the die-to-die interface to 64 GT/s and added 3D packaging, raw data transport and whole-package management. The real test is whether these rules can support multi-vendor products when power delivery, thermals, yield, software, security and accountability still…

Global Institutional
UCIe’s chiplet promise extends beyond the link
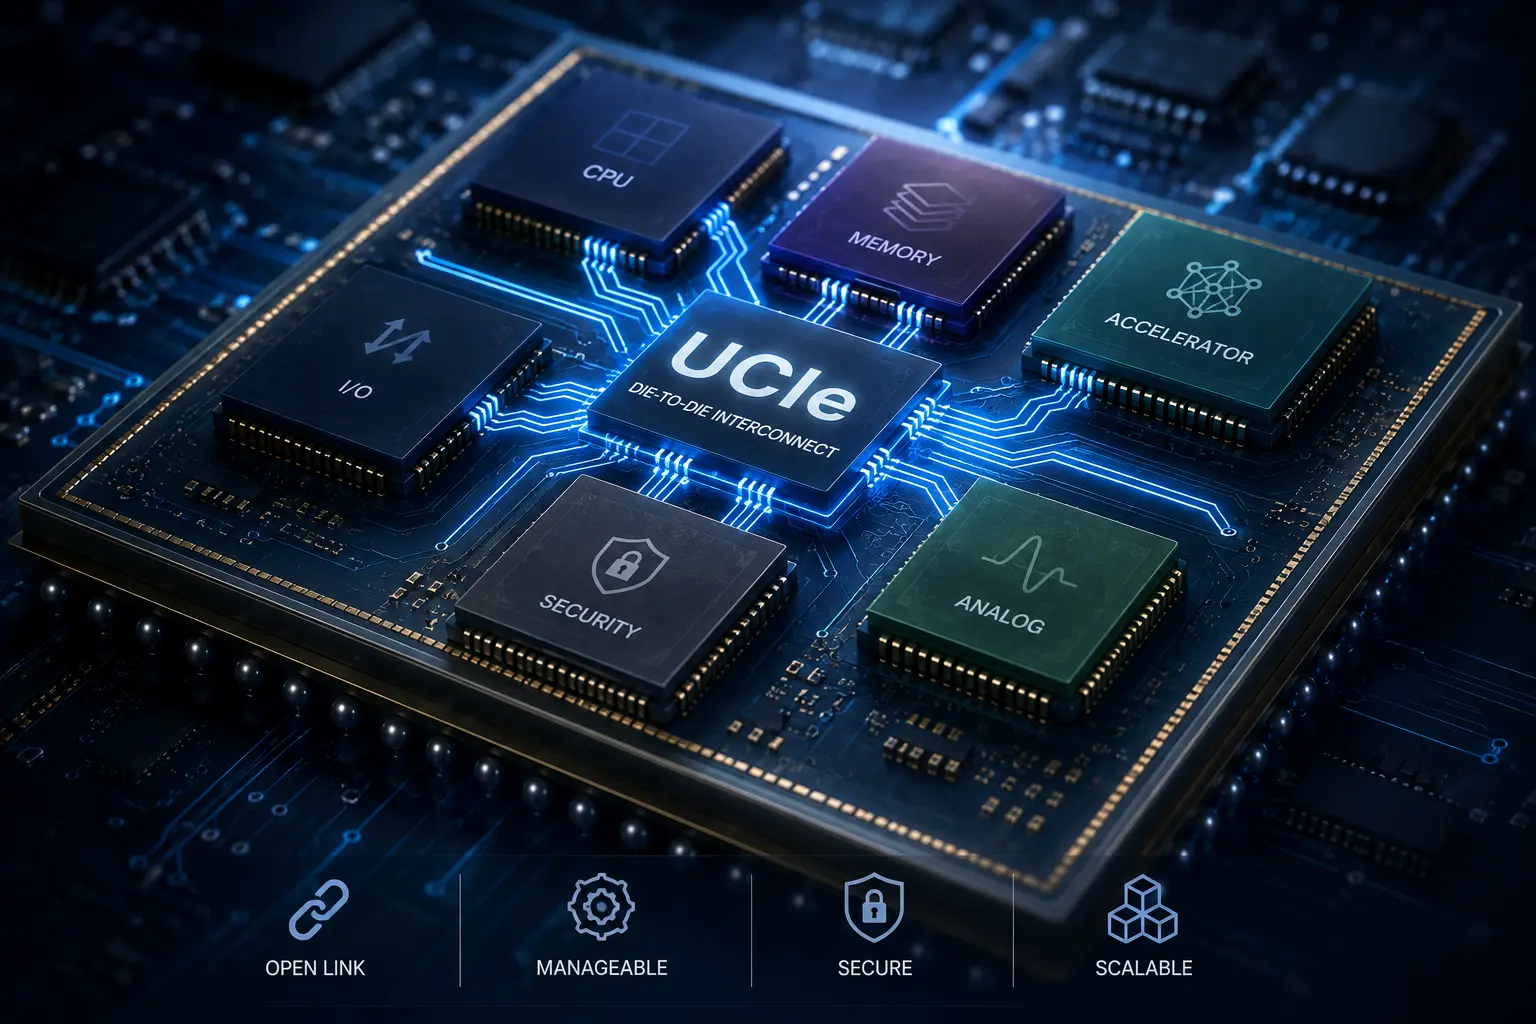
UCIe has defined a die-to-die interface capable of 64 GT/s, 3D stacking, raw traffic and package-wide management. The decisive test is whether those rules enable multi-vendor products while power, thermal design, manufacturing yield, software, security and contractual…
Global Institutional
The promise of UCIe depends on what happens beyond the link
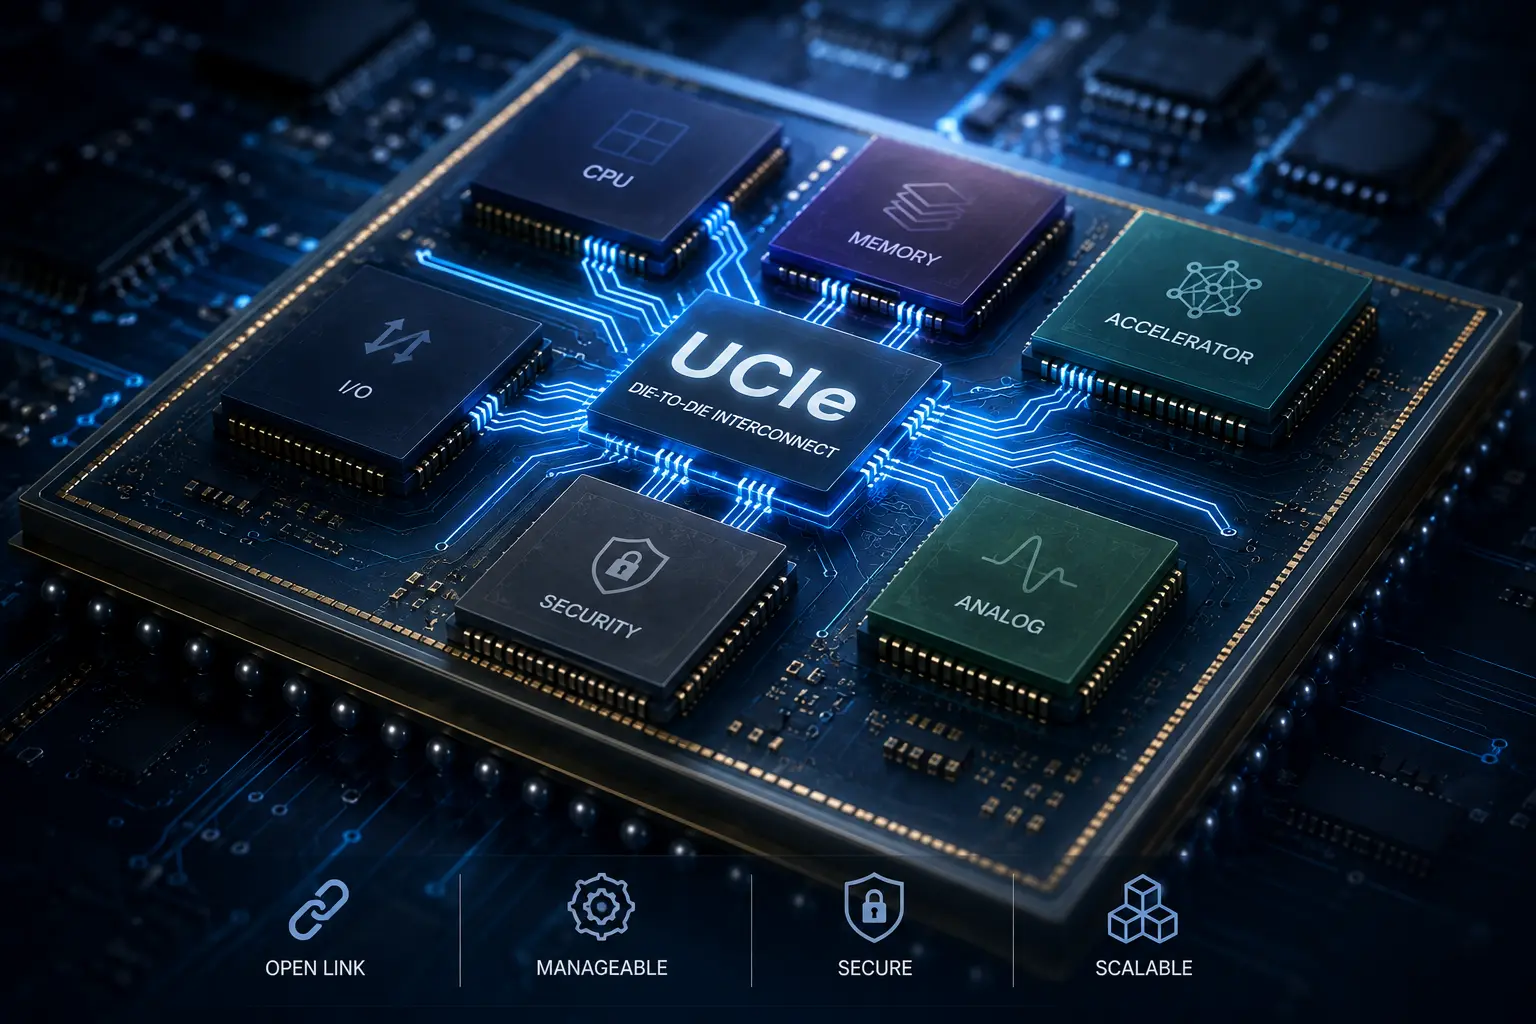
UCIe has defined an inter-chip interface that reaches 64 GT/s and already covers 3D packaging, raw traffic and whole-package management. The decisive test will be whether those rules can sustain multi-vendor products when power, thermals, manufacturing yield, software, security…
Global Institutional
UCIe’s chiplet promise depends on what happens beyond the link
UCIe has defined a die-to-die interface that reaches 64 GT/s and now covers 3D packaging, raw traffic and package-wide management. The consortium’s real test is whether those rules can support multi-vendor products when power, thermal design, yield, software, security and…

Global Institutional
PCI-SIG: The common rules inside AI servers
An AI server may combine processors, accelerators, network cards, storage controllers, switches, retimers and security devices from competing vendors. PCI-SIG maintains a common interface that lets these components be discovered, negotiate capabilities and exchange data, while…

Global Institutional
PCI-SIG: the internal rulebook of the AI server
An AI server can bring together processors, accelerators, network cards, storage controllers, switches, retimers and security devices from competing companies. PCI-SIG maintains the common interface that lets these components discover one another and exchange data, then organises…

Global Institutional
PCI-SIG and the internal rules of the AI server
An AI server can bring together processors, accelerators, network adapters, storage controllers, switches, retimers and security devices from companies that compete with one another. PCI-SIG maintains the common interface that lets these components discover one another and…