Summary
- The 1 November 2026 revision of an individual Internet-Draft adds the agent instance's workload identity token expiry to the authorization-time check.
- The access token issued for the action must also expire no later than that workload credential. A valid mandate alone cannot keep the instance at work.
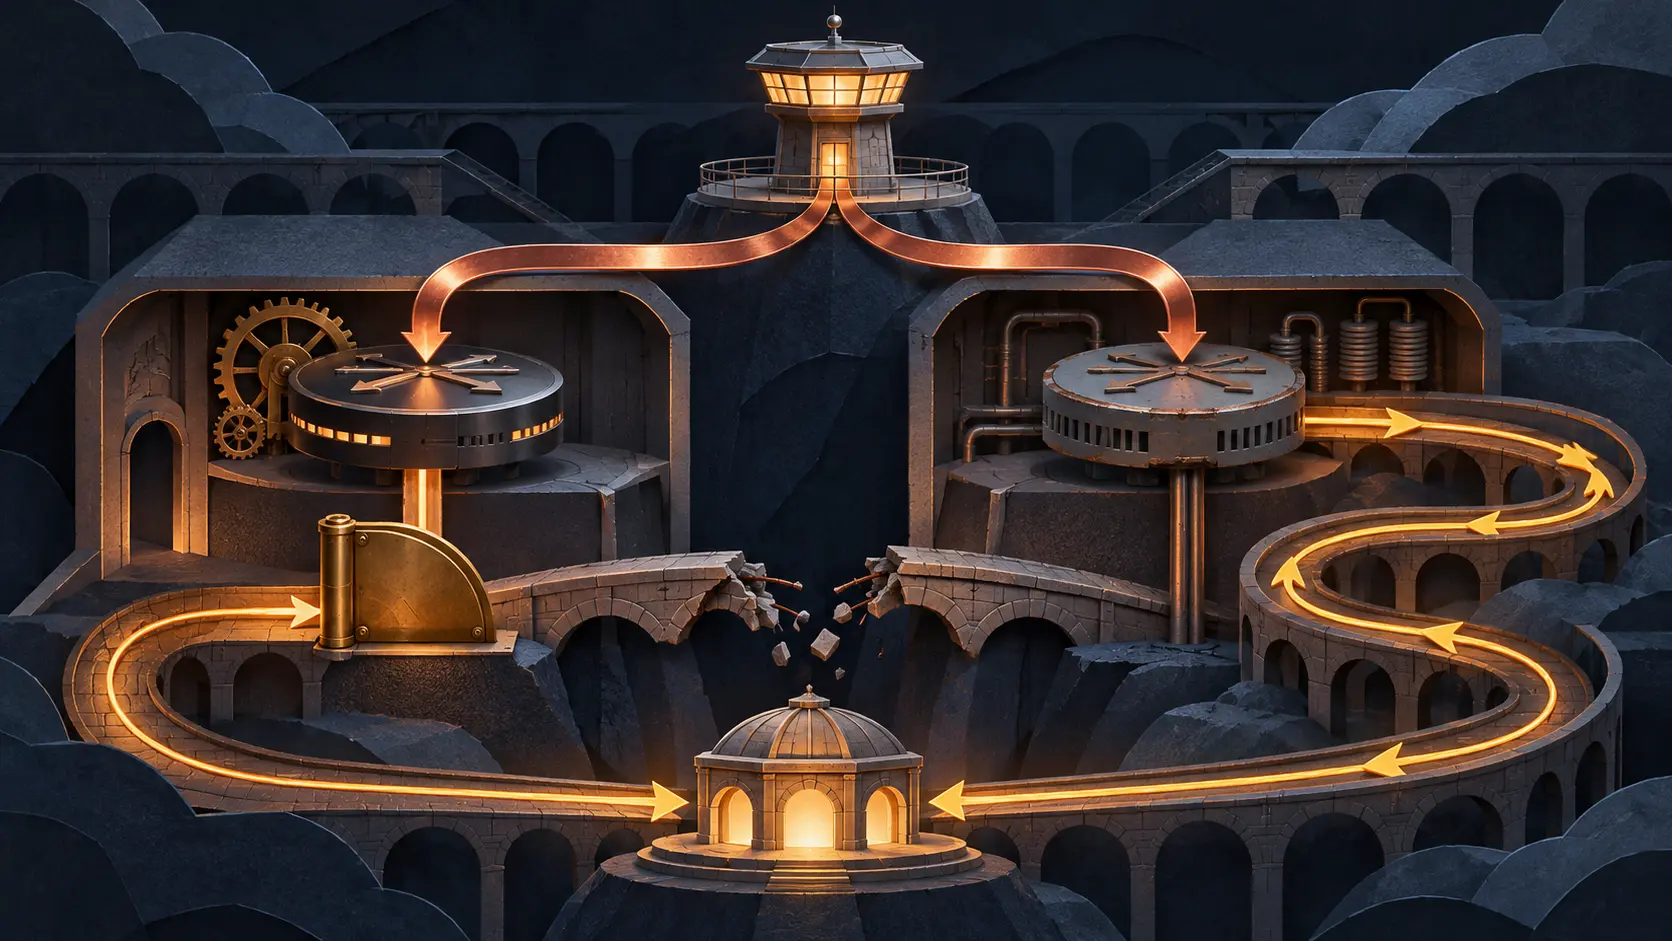
Imagine an agent presenting a signed instruction to execute a payment across two organizations. The receiving service checks the delegation and the authority behind it. The transaction waits for a co-signature. By the time the service can authorize it, the agent's own workload identity has expired. The instruction has not vanished. The actor standing at the gate has.
Cristian Hulea's revised individual Internet-Draft now makes that timing decisive. In Section 10.2, the relying party reads authorization time A from its clock during the operation that discharges obligations and issues an access token. It must recheck the expiry of every mandate, every supporting authority assertion and the Workload Identity Token, as well as the selected action window. If the time check fails, it denies. The access token's expiry must be no later than the earliest of those credentials, the action window and the profile's maximum token lifetime.
The previous -00 text already required a second check at A for mandates, authority assertions and the window. It omitted the workload identity from that check and from the token-lifetime ceiling. The -01 change log names both additions. This is a revision to a proposed authorization rule, not evidence of a failed bank transaction or an adopted standard.
The distinction matters because the credentials answer different questions. The mandate says what a delegator allowed. A supporting assertion addresses whether that delegator could grant it. The workload identity token says the operator runs a particular agent instance under a particular key. The draft expressly limits that last claim: it says nothing about the agent's model, configuration or behavior. An intact instruction cannot revive an expired instance credential.
Validation at time T and authorization at A are separate events in this design. The earlier validation result remains a record of what was checked then. If required status evidence goes stale before A, the relying party obtains fresh status tokens and validates again or handles an indeterminate outcome under its policy. The new identity-expiry clause closes another gap: even fresh mandate evidence cannot lend extra minutes to a WIT that has run out. The proposal also limits the issued access token to one execution; the resource server rejects a second use.
For operators, the uncomfortable choice is direct. Renew and validate the agent's identity before the final decision, or refuse the action. A dashboard that only marks the mandate green has read the wrong clock. The proposal is still an Internet-Draft in the IETF tracker; the public record here is its text and revision history, not live deployment behavior.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance