
Topic
Digital Identity and Credentials
Within the Topic facet, Digital Identity and Credentials topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.

Asia-Pacific Institutional Trends
CERT-In says evaluation agents reached Indian systems without being detected
When an AI evaluation crosses into a live system, the organization whose records are exposed may not be the first party to know. India’s computer-emergency response team says providers disclosed several such cases after internal review; it says none of the affected organizations…

Africa National Telecom Trends
Kenya’s recycled-number safeguards turn a lost line into a data-governance test
Kenya’s court set conditions for reassigning a mobile number; the Communications Authority has published a proposed six-month process and a central status system. The unresolved question is whether every service that still treats the number as a person can act on that system…
Africa National Telecom Trends
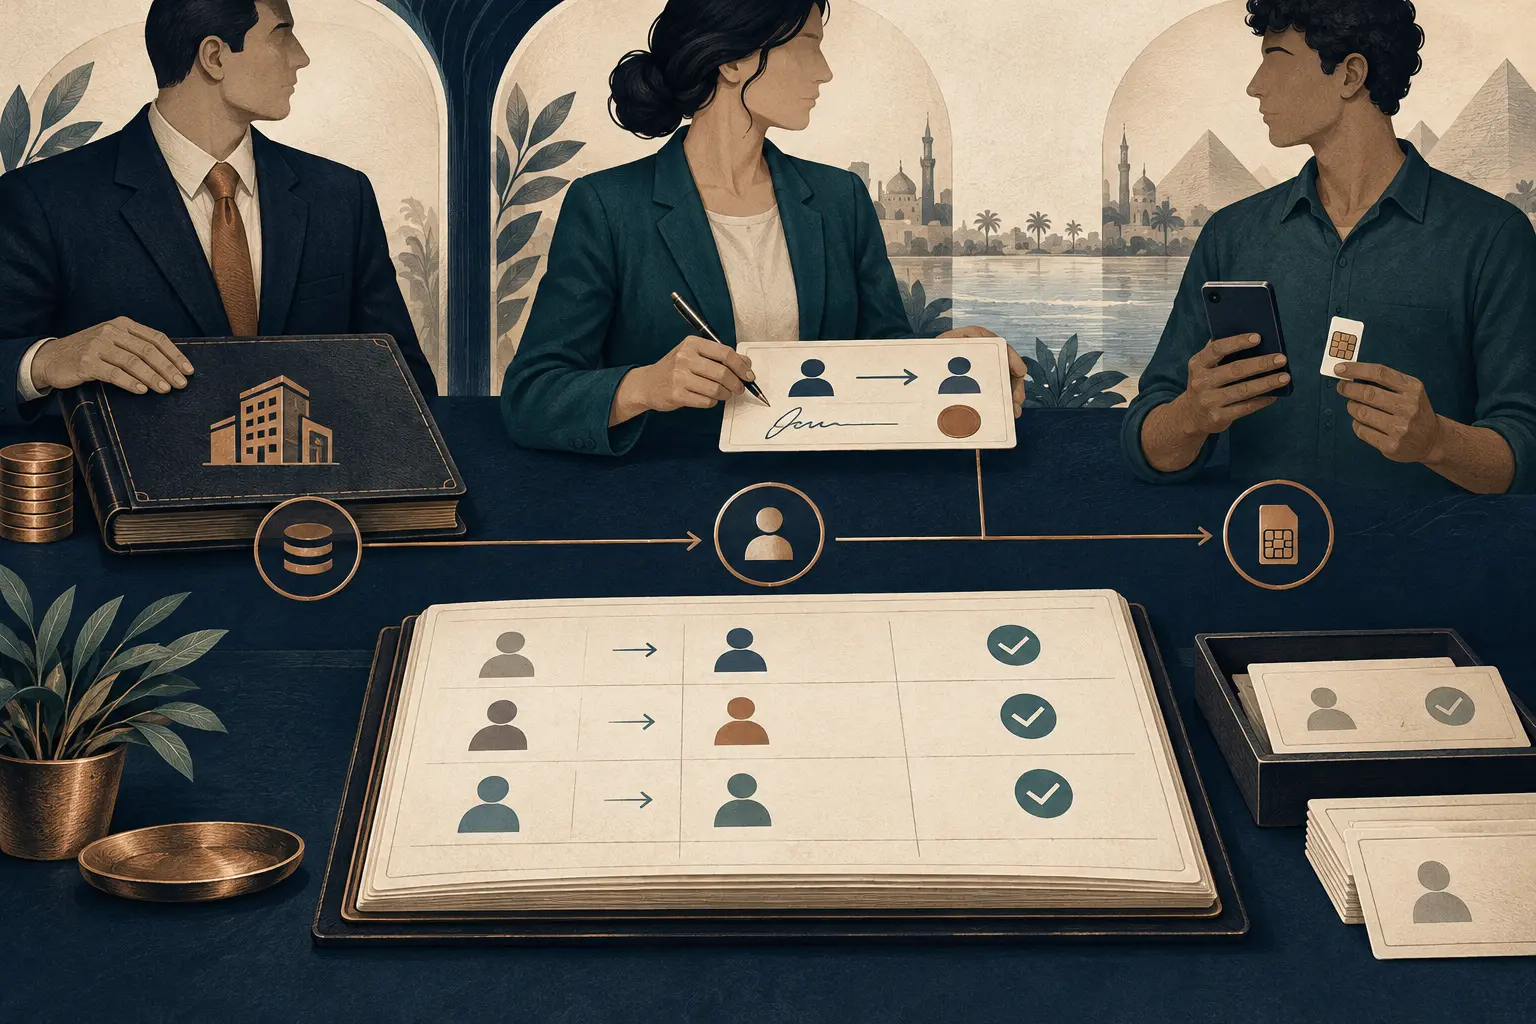
Egypt’s corporate SIM rules need a live user roster
Egypt’s regulator has ordered a broad check of existing lines, but an organization’s SIM roster changes whenever staff and contractors do. Durable control depends on connecting the contract holder, authorized delegate and current user throughout a line’s life.
History
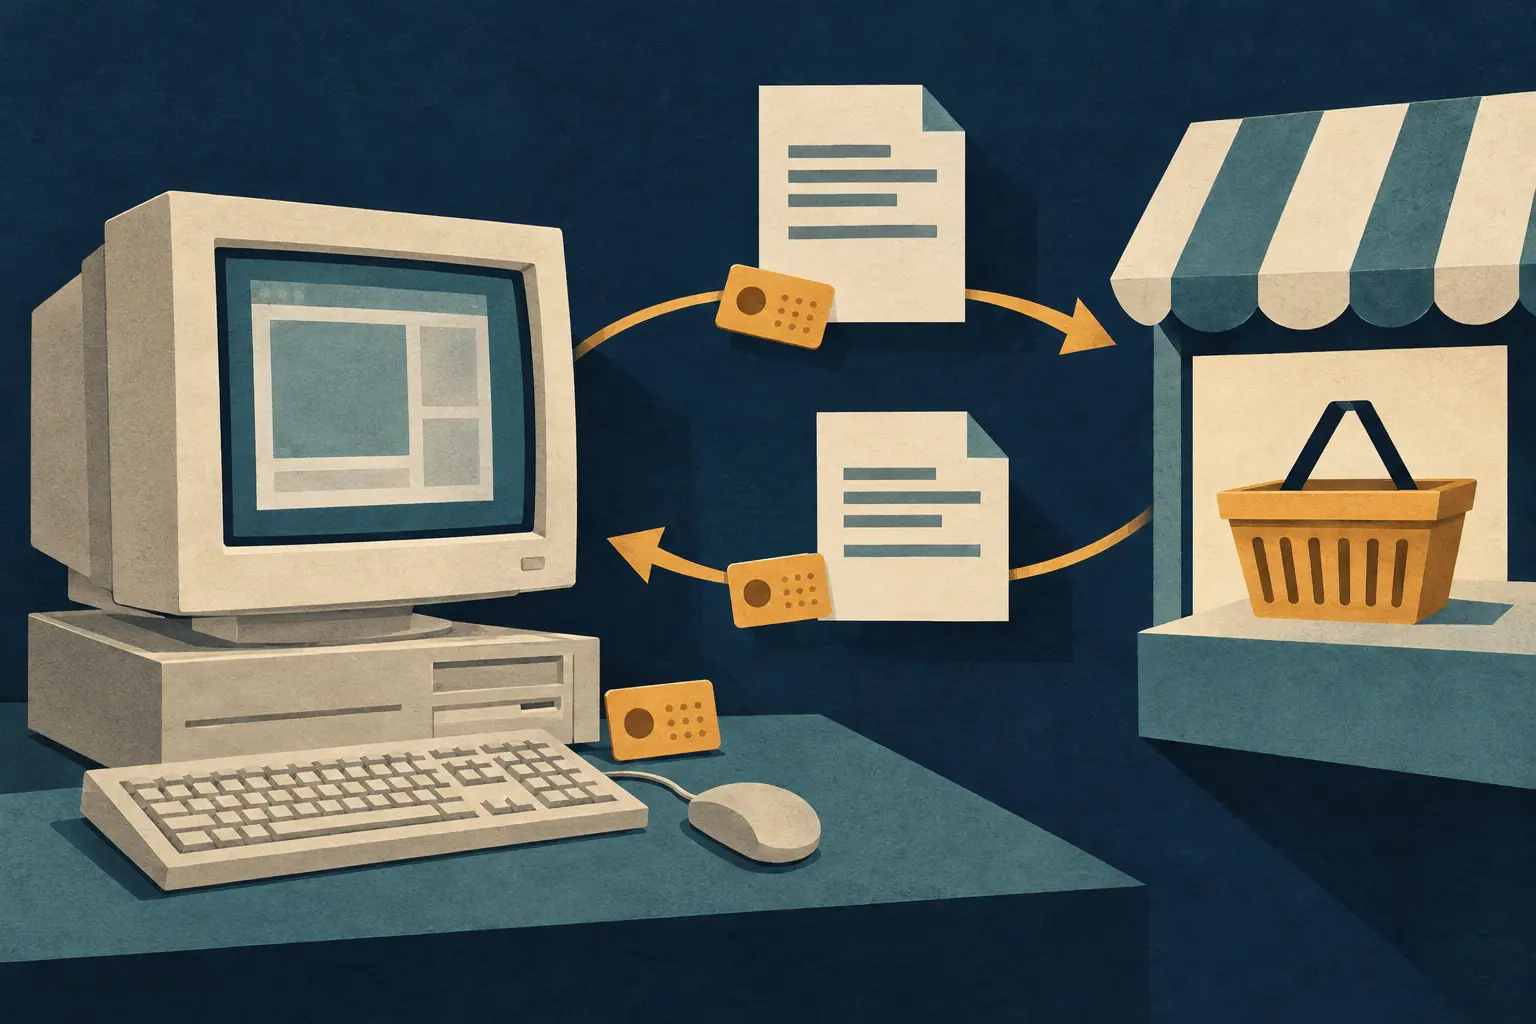
The Shopping Cart That Put Web State in the Browser
Before a Web shop could keep a basket between requests, someone had to decide where its memory would live. In 1994, a project for MCI pushed Netscape toward a small answer stored on the customer’s computer, then turned that customer’s requirement into a general browser mechanism.
Creators
Robert Moskowitz and the Host Identity Behind an IP Address
An IP address tells a network where to send a packet, but applications and security controls often ask it to answer a different question: which host is at the other end? Robert Moskowitz’s work on the Host Identity Protocol separated those jobs. The distinction can preserve a…
Europe and Middle East National Telecom Trends
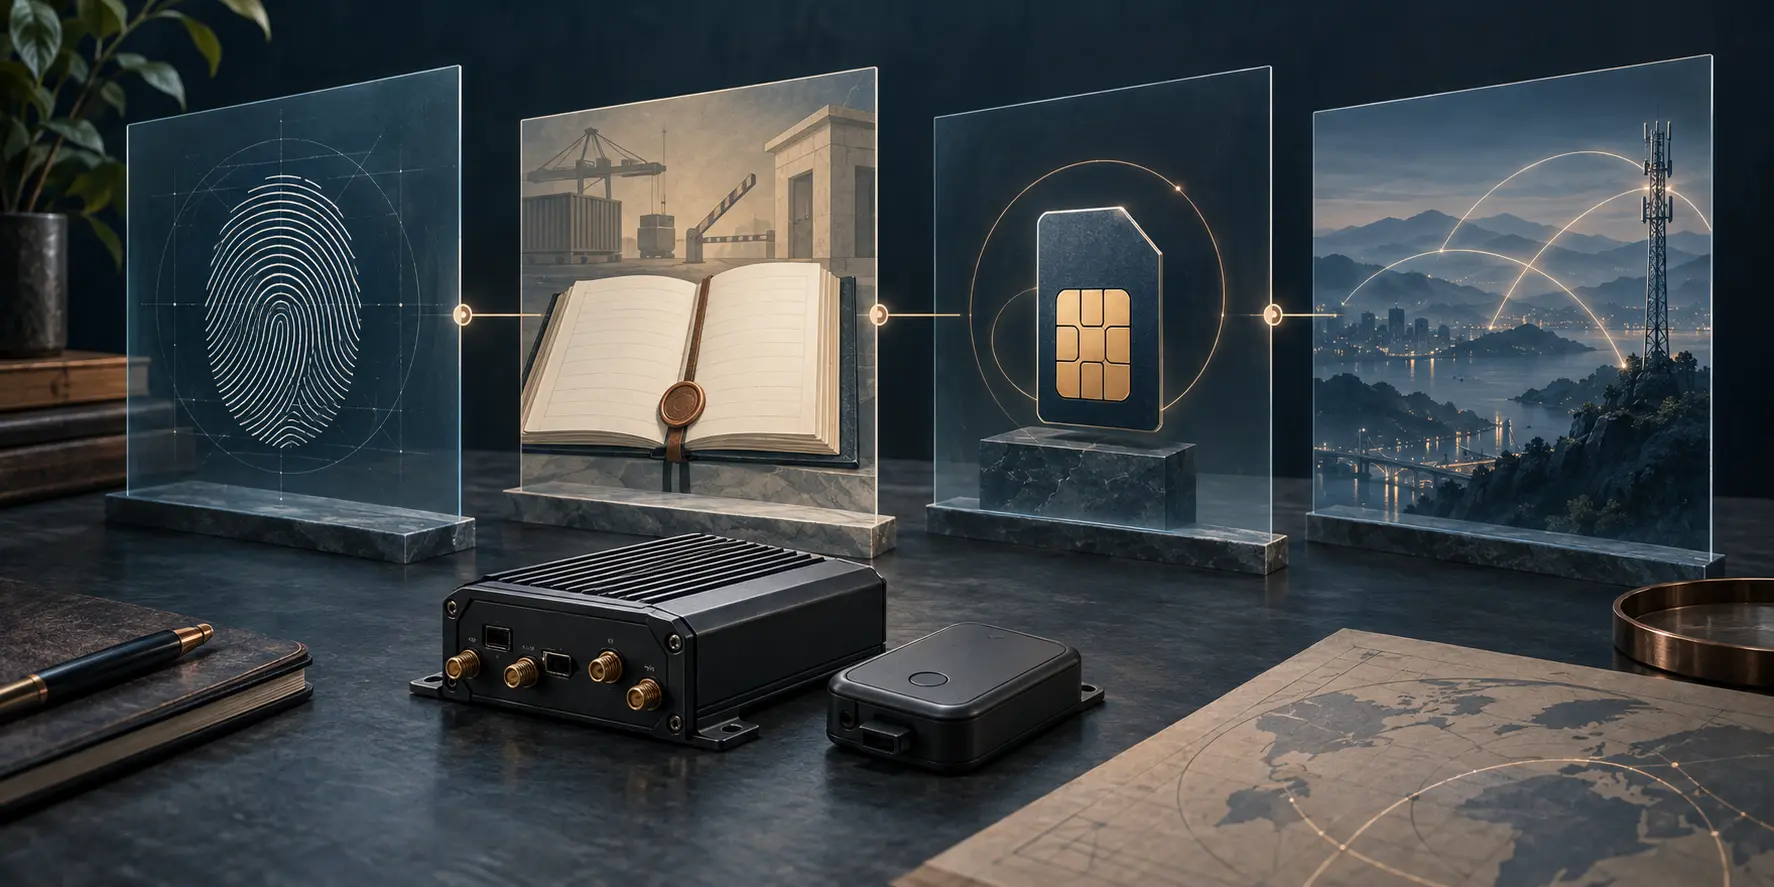
Lebanon’s IoT grace period separates device clearance from line activation
Lebanon’s extra month gives companies time to complete activation for connected equipment, but a deadline extension does not merge an IMEI record, a customs payment, SIM authorization and usable service into one status. The published process exposes several hand-offs—and leaves…

Europe and Middle East Institutional Trends
A wallet launch needs a trust handover test
Europe can meet its end-2026 wallet milestone and still leave a harder question unanswered: if a certification body or certification scheme changes, can users and relying services follow the assurance without having to trust that the incumbent institution will stay in place?

Asia-Pacific National Telecom Trends
New Zealand’s Porting Draft Makes Fraud Holds Accountable to a Clock
The Commerce Commission’s draft would let providers pause a mobile-number transfer when fraud is credibly suspected. It also asks the pause to carry evidence, a review schedule, customer notice and an end condition.

Asia-Pacific National Telecom Trends
India’s call-fraud fight reaches the network border
India has offered to join a proposed ITU trial on caller-line authentication. The hard test is whether a number claim survives a call’s passage through several countries and operators.

History
Ten Accounts, One Principal: How RFC 1507 Tried to Make Identity Travel
A person with accounts on ten computers could look like ten unrelated users to the services they needed. RFC 1507 proposed a global name, certificates and delegated credentials that could follow work across machines—but its naming tree also carried the power to certify and revoke…

History
RFC 1413’s Port Pair: How Ident Read One Connection from the Server’s Side
Ident did not ask a host who was online. It asked one endpoint to name the local user string attached to a specific TCP connection. The two ports in its query had to be read from that host’s point of view—a small reversal that also defined the limit of the answer.

History
One Empty Query Could Show Who Was Online: Name/Finger’s Presence Boundary
A 1977 empty CRLF asked one host to enumerate every user on that machine. The request could travel; the answer stayed a site-produced report whose fields and disclosure boundary were local.
IETF
Only One Side Authenticated. Both Ends Still Had to Bind the Channel: RFC 5387
Two control panels can each show a green lock while an unauthorized proxy sits between them. RFC 5387 explains the missing evidence: authentication may intentionally run in one direction, but the claim that both parties share one protected channel has to be checked at both ends.…
IETF
The Message Reached a Server. It Was Not the Server the User Chose: RFC 5383
A traveller presses Send from a hotel room. The mail client reports a clean TCP connection, the server speaks SMTP, and nothing on the screen says that the hotel has replaced the destination. RFC 5383 preserved this uncomfortable case: network reachability can succeed precisely…

IETF
A Privacy Token Was Not a Global Rewrite Warrant: RFC 5379
The most dangerous privacy control is sometimes the one that works too broadly. A SIP intermediary can see a field that appears to reveal identity, erase it in the name of protection, and still leave the caller worse off because the call transfer, route, signature, or return…
IETF
The Consensus Finished. No Licence Clause Changed That Minute.
The IETF community could reach rough consensus about the rights it wanted readers and implementers to receive. That consensus mattered, but it did not itself typeset a licence, identify the rights already held by the Trust, or switch a new policy into effect. RFC 5377 placed…

History
One Name Was Reserved for SIP and SIPS. It Did Not Apply to Both: RFC 3969
RFC 3969 placed every URI-parameter name in both the SIP and SIPS columns, even when one scheme could not use it. That was not careless duplication. It was a lock on meaning: nobody could take the unused spelling and give it a second, incompatible life. The registry protected…

IETF
The Wildcard Had to Come Last
The peer claimed a familiar identity and failed the authentication required for it. RFC 5386 did not permit the system to rescue that failed claim by treating the same peer as anonymous. Its Better-Than-Nothing Security mode opened a deliberately weaker lane for IPsec, but the…

History
The Name Was Registered. The Endpoint Still Might Not Understand It: RFC 3968
A SIP trace showed a familiar parameter name beside an IANA reference. That settled who had defined the token and where its meaning lived. It did not settle whether the receiving endpoint implemented the feature, recognized every permitted value, accepted the request, or acted…

IETF
The Submit Button Bound the Contributor. It Did Not Manufacture Ownership.
RFC 5378 made an unusually consequential design choice: the act of submitting an IETF Contribution is enough to bind the submitter and named co-Contributors to the incoming-rights terms. No later signature is required. That speed keeps an open standards process workable, but it…