
Topic
Software Lifecycle and Lock-in
Within the Topic facet, Software Lifecycle and Lock-in topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.

IETF
DNS GREASE Needs an Experiment Charter Before It Becomes a Default
A resolver deliberately puts a value with no useful meaning into a DNS query. A correct peer ignores it. A brittle peer may reject the query, stay silent or provoke a retry. The experiment protects tomorrow’s protocol by creating a small inconvenience today. That bargain is…

History
Every Line Returned to ASCII So the Middle Could Be Read: RFC 1922
Open a long Chinese message at line twenty. If that visible line depends on an escape sequence hidden nineteen lines above, scrolling has become a decoding hazard. RFC 1922 answered with deliberate repetition: a Chinese line declared the character set it needed and returned to…

Europe and Middle East Institutional Trends
ENISA confirms manual CRA reporting at launch
ENISA's CRA platform launches without an API, so manufacturers must submit mandatory cyber reports through its interface from 11 September.

History
Who pays while a network upgrade waits for everyone else?
A protocol can coexist with old equipment long before it delivers a return to its first users. The history of Quick-Start exposes the cost of that interval—and why a smaller deployment can sometimes be the more ambitious business.

History
The Second Request Was Deleted. Its Error Had to Wait: RFC 1921
A second printer request arrived before the first had finished. TNVIP did not queue it, number it or let it overtake. The receiver deleted it—and postponed the protocol-violation response until the first request had received its own answer. RFC 1921 used three small, separate…

IETF
A Deprecation Date Retires an RDAP Label, Not Its Clients
An IANA registry can mark an RDAP extension obsolete. An operator can publish an end date. Yet somewhere beyond both records, a client may still ask for yesterday’s interface. That is not a contradiction. It is a map of divided authority—and a warning against treating one date as…

History
Both Networks Were Correct Until They Met: RFC 1918 and the Price of Local Uniqueness
At 09:00, two enterprise networks can each be orderly. Each has one machine at the same private address, one route toward it and one name that resolves correctly. At 09:01, an interconnection comes up. Nothing inside either machine has changed, yet the address can no longer…

Creators
Roy Arends and the hard work of changing DNS safely
Roy Arends helped write the 2005 specifications that made modern DNSSEC interoperable across implementations. Two decades later, his work at ICANN focuses on a harder operational problem: changing keys, error signals and delegation in a global system that no organisation can…
History
Before Renumbering Had a Procedure, It Had a Field Diary: RFC 1916
Most RFCs are remembered for an answer. RFC 1916 deserves attention because it published a question. In February 1996, the IETF's PIER working group needed practical guidance for changing enterprise IP addresses, but it did not pretend that a standards room already possessed the…
Story
RIPEstat Is Rebuilding Routing History to Enable CSP. The New View Needs a Parity Record
A safer browser should not leave an operator wondering whether a changed graph reflects changed routes or changed presentation. RIPE NCC has a sound reason to replace legacy RIPEstat visualisations. Routing History is precisely where the migration needs a small public receipt…
Creators
Roy Arends and the hard work of changing the DNS safely
Roy Arends helped write the 2005 specifications that made modern DNSSEC interoperable. Two decades later, his work at ICANN centres on a harder operational problem: changing keys, error signals and delegations across a global system that no institution can update by command.

History
The Assurance Was Public. The License Form Was Not: RFC 1915
A standard can be open to inspection while a decisive commercial term remains behind the next conversation. In 1996, the IETF published Motorola’s assurance that licences for claimed patents affecting two PPP control protocols would be available on reasonable and…

CASE FILE
The ICMP Error Named a Node. It Did Not Prove Which One
Revision 05 of an IETF draft makes node context harder to omit when an ICMP source address cannot do the diagnostic job alone. It also exposes a less comfortable truth: a more informative error can carry less of the packet that triggered it, and neither piece is authenticated.
History
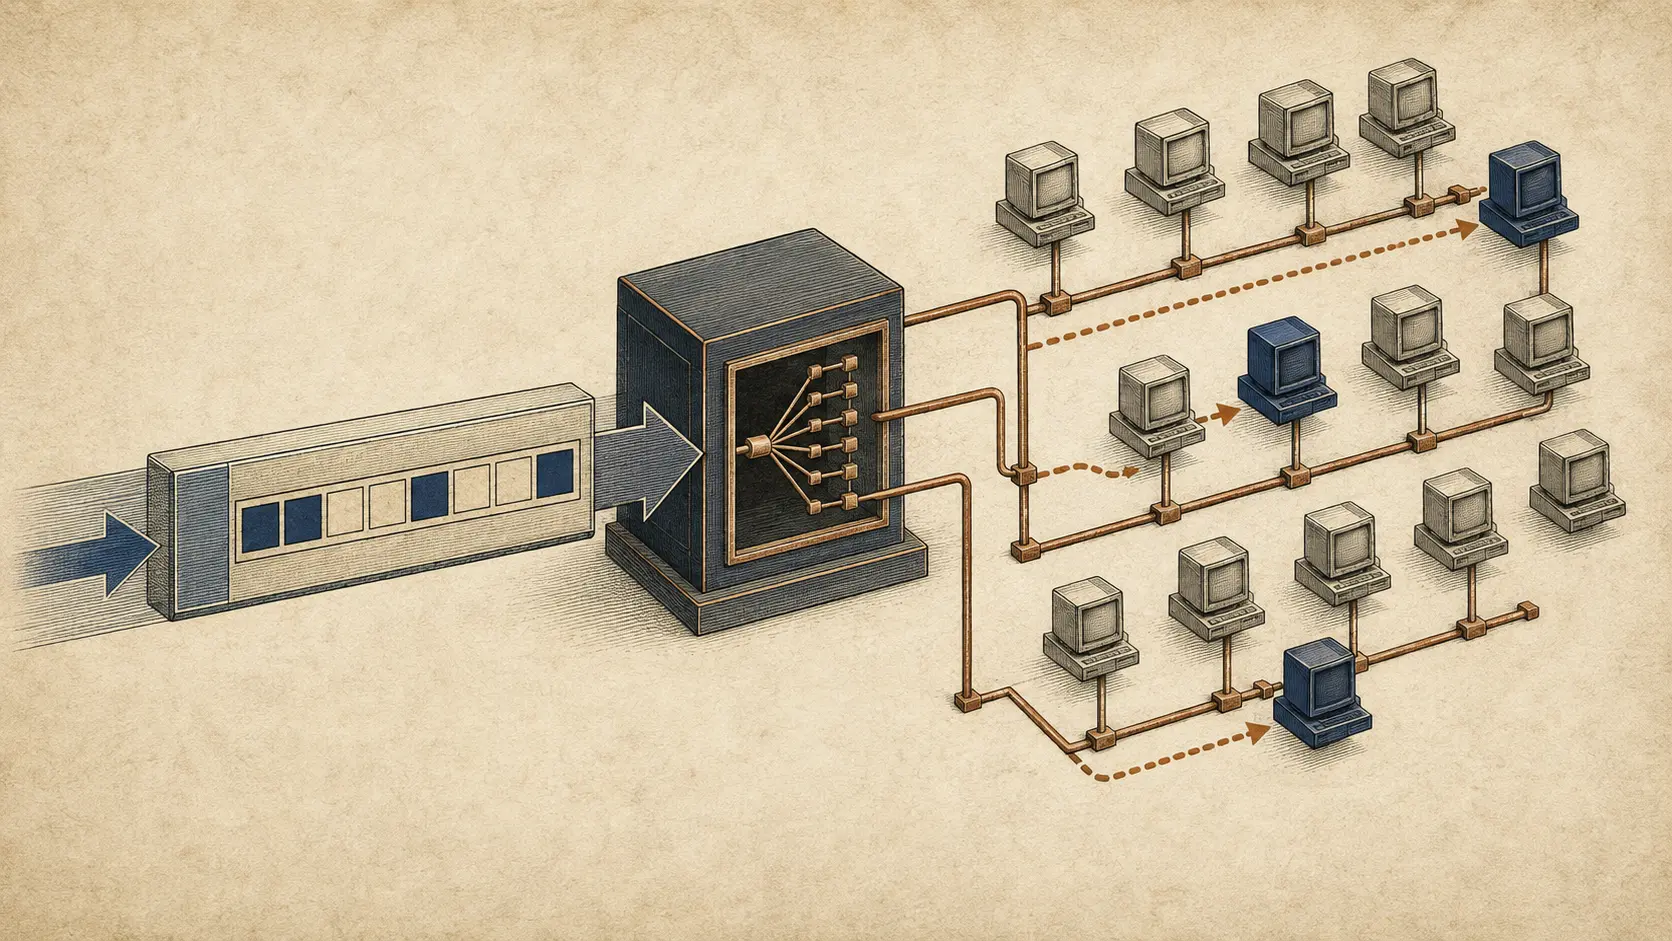
The Broadcast Packet That Carried Its Own Guest List
One UDP datagram approached a remote subnet as a broadcast, yet it carried a private instruction inside its IPv4 header: these hosts may listen; the others must stop. Selective Directed Broadcast Mode tried to make the packet itself serve as a temporary membership list.

CASE FILE
Every Outer Bundle Was Delivered. The Inner Bundle Still Had Not Been Received
Bundle-in-Bundle Encapsulation gives a delay-tolerant network two journeys to observe. The outer bundles can reach their configured endpoint one by one, each with a valid delivery report, while the bundle carried inside them never reaches the Bundle Protocol Agent. The new DTN…

CASE FILE
The Firewall Matched the Return Flow. The Source Still Was Not an Identity
A new SPRING working-group draft proposes a neat repair for a stubborn SRv6 middlebox problem: put the service SID in the outer source address so the two directions form the pair a stateful firewall expects. The packet may then pass. What the address proves, however, has changed.…
IETF
Erik Kline and the DHCP Code That Was Assigned but Not Vacant
A standards registry said 160; a live network said the number already had another life. The resulting collision did not make the registry irrelevant, nor did it make undocumented use legitimate. It showed something more operationally useful: an authoritative assignment can define…
CASE FILE
The Algorithm Name Matched. The Hash Receipt Did Not: RFC 9861
KangarooTwelve and TurboSHAKE give operators fast, extendable cryptographic output, but the label on a library call is only the beginning of the evidence. Reproduction depends on the exact function, byte stream, domain or customization input, output length and execution path that…

CASE FILE
Who Gets to Ask the User to Authenticate Again?
An API can reject a perfectly usable token because the user's authentication does not meet the needs of this particular request. RFC 9470 gives that refusal an interoperable language. It does not settle a more consequential question: who may turn a local risk decision into…

History
The Future Protocol That Hid Inside an IPv4 Option
EIP's version field looked backward while its address space looked forward. RFC 1385 kept the familiar IPv4 header so an old machine would see an ordinary packet with an option it did not understand—and, ideally, keep forwarding it.