
Summary
- RFC 3141 treated roaming as a division of responsibility: a visited wireless system could supply service while one home provider remained the subscriber’s formal customer-service relationship.
- The memo separated radio-resource authorization from data-service authorization and required AAA to work across home, serving and intermediary networks, including cases without a direct business relationship.
Analysis
One subscriber, more than one authority
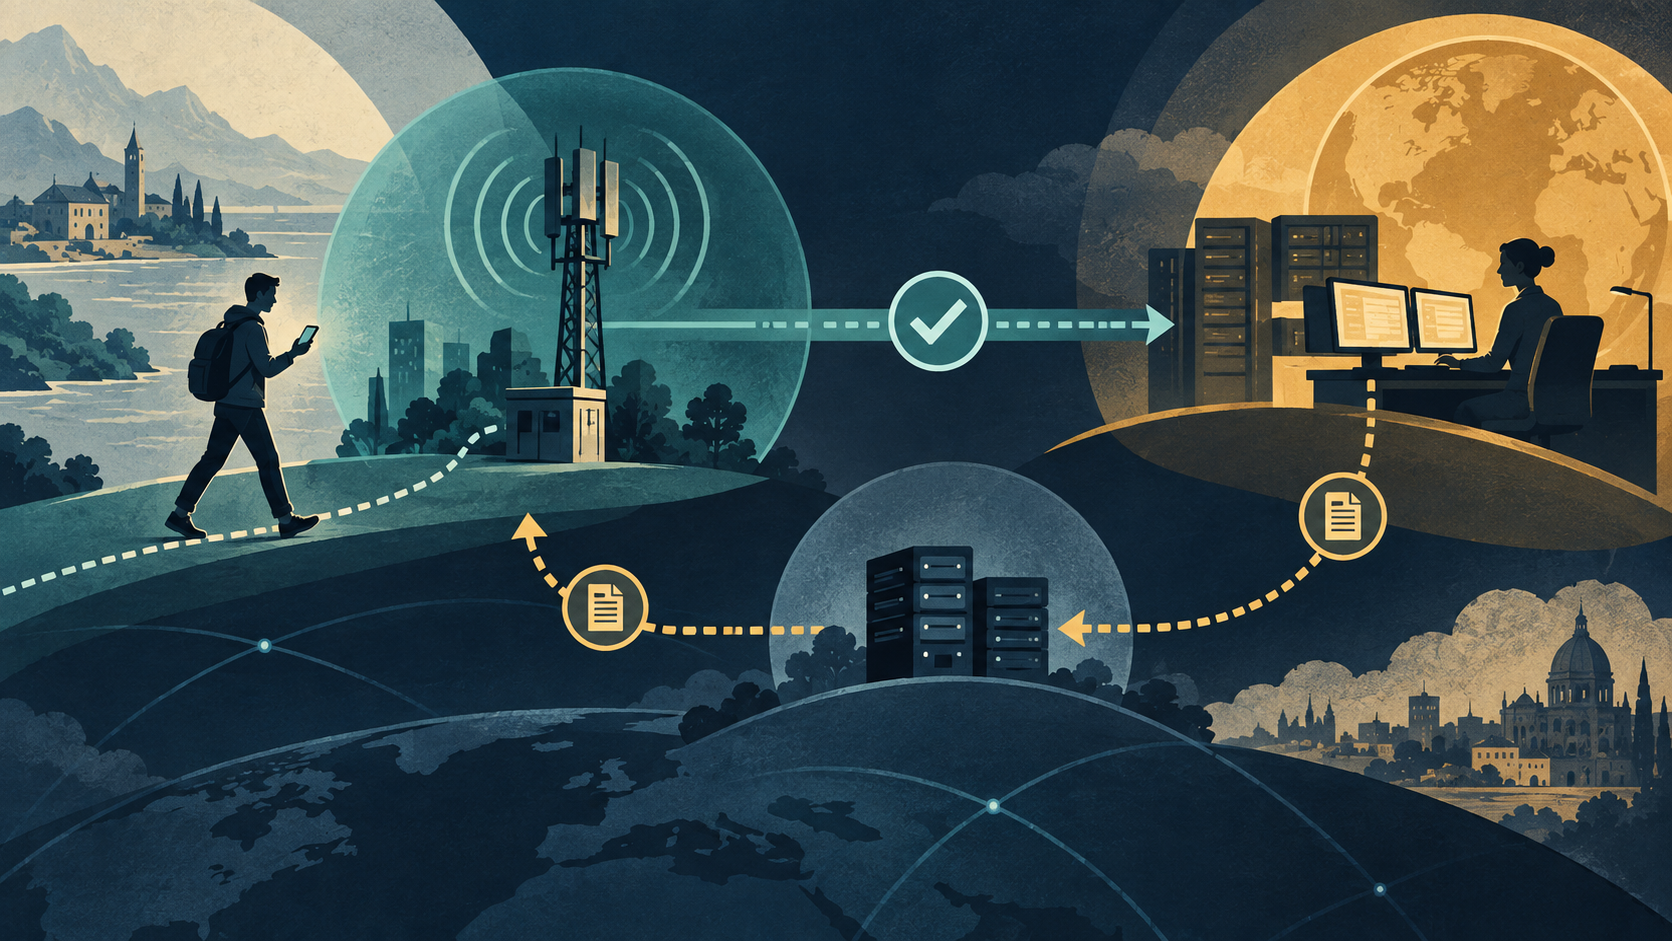
A roaming connection looks like a single act to a user: the phone registers, receives an address and exchanges packets. Behind that surface, several actors answer different questions. Is the device allowed to use this radio channel? May it obtain packet-data service? Which provider holds its customer relationship? Which party records usage and carries the result home?
RFC 3141, published in June 2001, placed those questions inside the CDMA2000 wireless-data architecture. It was an Informational requirements memo, not an Internet Standard and not a report of a particular network deployment. Its stated goal was to support subscribers visiting other wireless systems while keeping a formal customer-service-provider relationship with one provider. That sentence is the document’s most revealing architectural choice: physical access could change without silently transferring the customer relationship.
The visited network did not become the home
The visited system supplied the radio environment and a packet-data entry point. The memo’s architecture described a Packet Data Serving Node (PDSN) connecting radio access to IP service; a home agent maintained Mobile IP registration and redirected packets. The mobile could use PPP, Mobile IP, or both, depending on the service path. Those components were not interchangeable merely because a packet crossed them.
The more important division was between airlink-resource AAA and data-resource AAA. Radio capacity is scarce and locally controlled. IP access is another authorization decision, often anchored in a home provider’s subscriber relationship. Treating them as one “login” obscures who admitted the device to the radio system and who authorized packet service. A successful airlink decision does not, by itself, prove that a data session was accepted; a data authorization does not prove that radio resources remained available.
AAA was an inter-organizational interface
The memo anticipated that a serving network and a home network might have no direct business relationship. AAA therefore could not assume a neat bilateral connection between the two institutions. It had to support relaying requests through other parties, cope with peer or path failure, protect message exchanges against replay, and produce accounting information about use of network resources. RFC 3141 listed requirements for evaluating protocol proposals; it did not select one protocol as the universal answer.
This distinction also disciplines the word “acknowledgment.” The memo required reliable transport behavior, including acknowledgment of receipt even when a relayed message’s options or semantics did not conform—while withholding acknowledgment when authentication failed. Receipt by a peer is not approval of the request. Approval is not allocation of radio capacity. An accounting record is not proof that a bill was correct or settled. Each is a different record, owned by a different part of the chain.
The security language has a similar boundary. Requiring a protocol to support confidentiality does not require every message to be encrypted. A protocol capability, a negotiated protection choice, and observed protection on a specific session are three separate facts. RFC 3141 defines requirements for the first layer, not evidence for the latter two.
The relationship survived the border
Roaming is often narrated as network interoperability. RFC 3141 shows the business and authority structure underneath it. A visited operator can furnish access without becoming the subscriber’s home provider; a home provider can remain accountable to the customer while depending on another network’s radio and packet infrastructure. Proxies and forwarded AAA messages bridge the gap, but forwarding does not erase it.
That makes accounting more than a final log line. It is the return path by which the access provider’s use record can become legible to the party that maintains the customer relationship. The memo’s requirements point toward that need; they do not establish an actual wholesale price, settlement rule, contract, or dispute process. A protocol can carry evidence without deciding what the evidence is worth.
A requirements document, not a deployment receipt
RFC 3141 explicitly says its requirements are intended to evaluate AAA protocol submissions. It cautions that the requirement that a protocol support a capability is not identical to requiring every exchange to use that capability. Later RFCs describe RADIUS and Diameter protocols, and later Diameter applications address mobile IPv4 and network-access service. Their existence supplies protocol context, not proof that RFC 3141’s architecture was universally built, that all providers could roam, or that a particular subscriber received uninterrupted service.
The historical contribution is narrower and more durable: the memo refused to collapse the visited network, the home provider and the authorization server into one actor. Once those roles are separated, the operator can ask who accepted the radio session, who granted data service, which trusted peer forwarded the decision, and where the usage record went. “Roaming succeeded” is a conclusion only after those separate receipts line up.
Sources
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance