
Primary Domain
Internet Infrastructure
Within the Primary Domain facet, Internet Infrastructure intelligence groups reporting by primary domain so readers can follow a focused area of internet infrastructure, governance, connectivity markets, or digital capital. The page brings together related articles, public evidence, institutions, companies, people, regional exposure, operating dependencies, and market context that may otherwise sit across separate category pages. It explains the domain, the likely actor class, the market or governance context, and the source material readers should use when comparing signals. Operators, analysts, and governance readers can see how the same domain appears across events, profiles, market shifts, public-source evidence, regional dependencies, and longer-cycle infrastructure decisions over time.
Europe and Middle East National Telecom Trends
An NG eCall button is not a proven local safety service until the 4G/5G path is ready
A visible SOS control and an eligible registration date can establish that a vehicle may carry Next Generation eCall. They do not prove that the current UK vehicle-to-emergency-service path is ready to rely on.

History
The Back Door Was Not a Route: How RFC 831 Reached a Partitioned SATNET
The emergency machine was allowed to behave like a gateway, but it was forbidden to become one. That distinction carried the whole proposal in RFC 831. A multihomed host at UCL could rewrite a chosen maintenance exchange around a broken SATNET path, yet it would send no routing…

History
The Gateway Could Carry the Bytes. It Could Not Invent the Missing Meaning: How RFC 875 Challenged Protocol Translation
A rectangle labelled “gateway” made incompatible networks look one arrow apart. RFC 875 asked what the rectangle had to remember: two address models, two acknowledgements, two flow-control contracts and exceptional signals that did not command the same actor. Moving data was the…

History
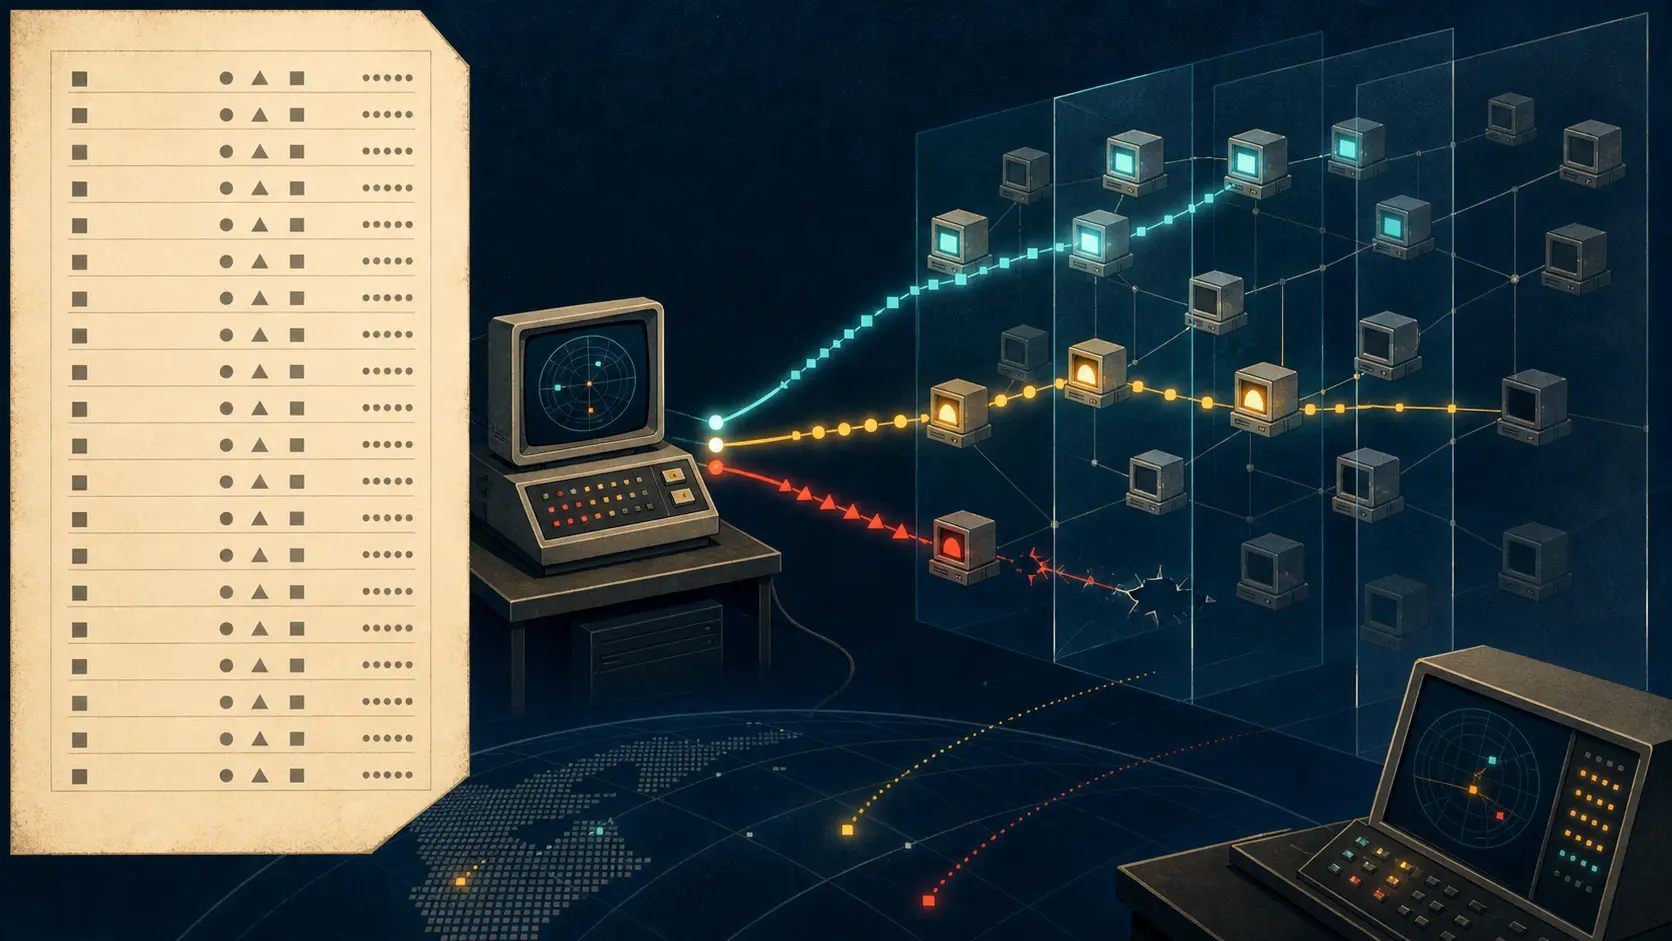
The Master File Could Be Current. The Network Could Still Be Stale: How RFC 849 Split Push from Poll
In May 1983, Mark Crispin described a naming failure that could survive a perfectly updated master file: a host that never learned the file had changed. RFC 849 treated freshness not as a property of the registry alone, but as a chain of version evidence, delivery, integrity…
History
The Host Table Said TCP. The Socket Had to Answer: How RFC 832 Measured Running Code
In December 1982, the Internet already had a list of machines said to support TCP. David Smallberg did not treat the list as deployment. He used it as a set of claims, tried the service ports, named the different ways a connection could fail, retried negative observations, and…
History
The Client Became the Service: How RFC 818 Put User Telnet Behind Port 107
A client normally knocks; a server normally listens. RFC 818 made that picture deliberately unreliable. On a small terminal concentrator, the useful application was the Telnet program that opened connections outward. By placing that User Telnet capability behind a well-known…

History
The Name Service Was Almost a Negotiator: How RFC 830 Separated Domains from Capabilities
A file-transfer program asks for NIFTP. The destination has no NIFTP implementation, but it does offer FTP. In the architecture proposed by RFC 830, that mismatch did not have to end the attempt. One part of the name service found the destination domain; another part asked what…

History
The Number Did Not Make It a Standard: How RFC 825 Made Intent Part of the Record
A procurement clause says a product is “RFC 825 compliant.” The number looks precise, the link is public and the document is real. Yet none of those facts tells the buyer whether the cited memo was a standard, a discussion, a status report or merely information. In 1982, RFC 825…
Europe and Middle East National Telecom Trends
Private 5G equipment is not a local network until the spectrum licence matches the site
Radios, SIMs and a coverage drawing describe a proposed private network. In the United Kingdom, site acceptance still depends on the final spectrum authorisation matching what was actually installed.

History
The Layer Was Not the Module: How RFC 817 Cut Across the Stack
One typed character could make three answers leave a server: a TCP acknowledgement, a window update and a Telnet echo. The protocol layers were each behaving correctly. The implementation was still wasting packets. RFC 817 used that small inefficiency to make a larger…

History
The Error Message Was Advice, Not a Verdict: How RFC 816 Layered Failure Decisions
A gateway that has crashed cannot send the error message explaining why packets disappear into it. RFC 816 began with that silence and built a layered answer: let routing repair distant failures, make the host replace a dead first hop, let TCP expose retransmission and timeout…
History
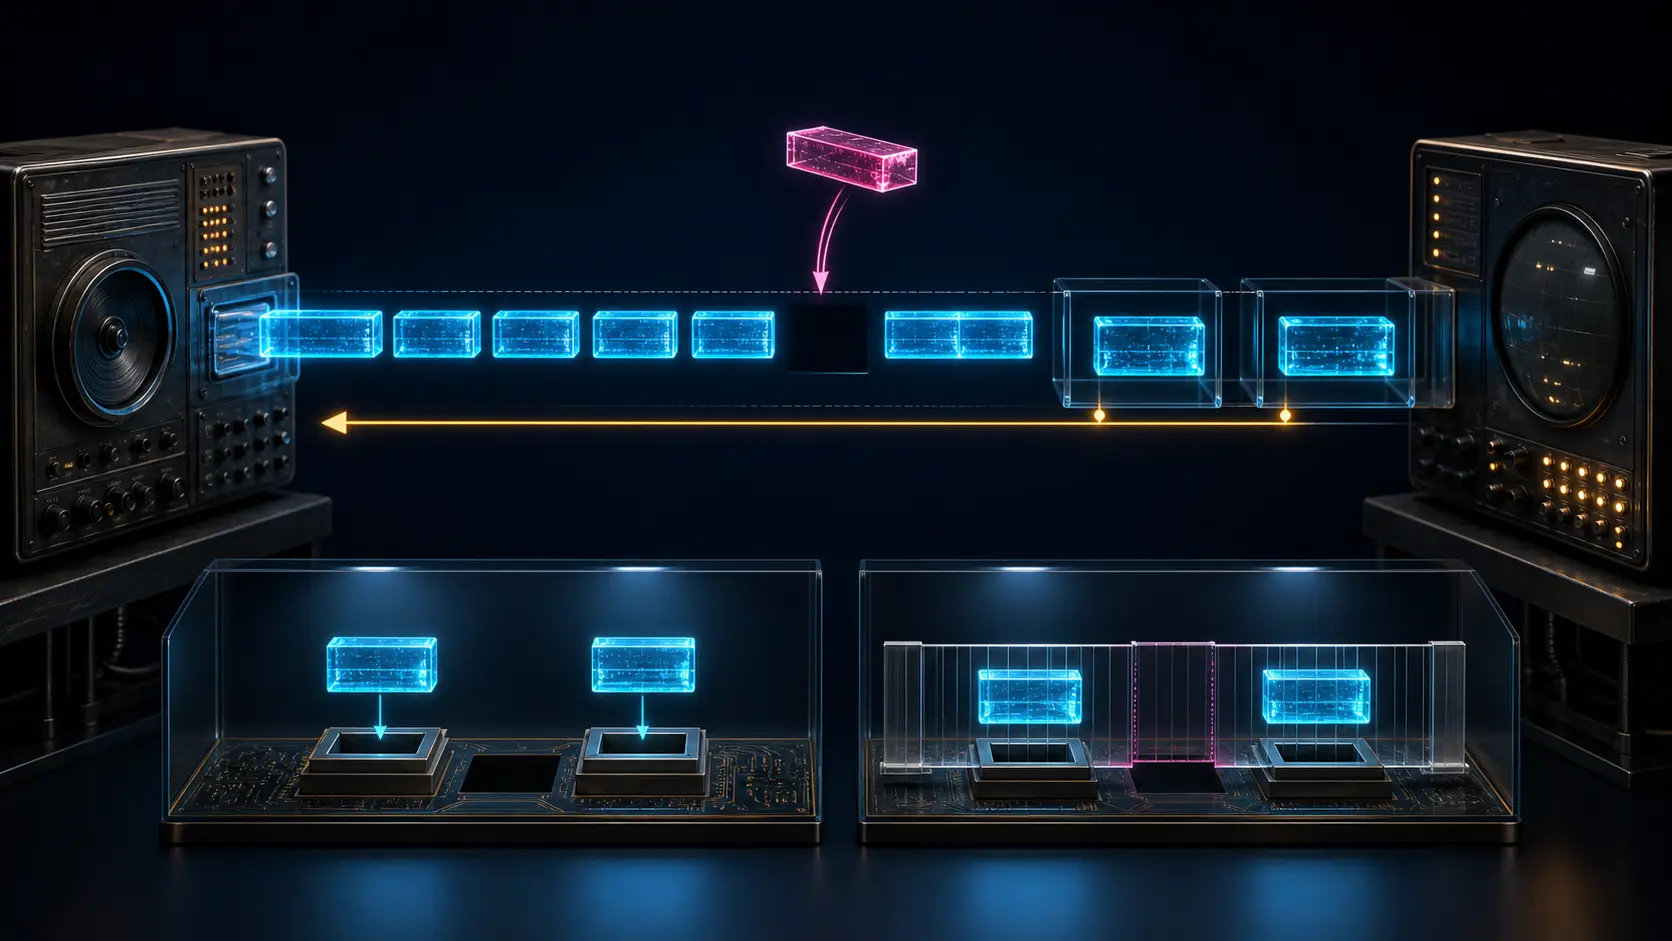
The Missing Segment Did Not Stop the Next One: How RDP Separated Reliability from Order
In 1984, the Reliable Data Protocol made a choice that still unsettles casual descriptions of transport: a later message could be safely received, individually acknowledged and even handed to an application while an earlier message was still missing. Reliability described whether…
IETF
Dieter Sibold and the Cookie That Let the Time Server Forget
Network Time Security performs its expensive act first: authenticate a key-establishment service, derive two directional keys and close the TLS connection. Later NTP requests carry the missing association state back inside an opaque encrypted cookie. RFC 8915 made forgetting…

History
The Name Was Not the Address: How RFC 814 Kept Identity Separate from Route
In 1982, a stale host table could send queued mail to an unexpected machine after the intended host had moved. RFC 814 treated that failure as more than bad data. It exposed four different references—name, address, route and port—and argued that an Internet host should translate…
Europe and Middle East Regional ISP Trends
Two fibre circuits are not diverse until their routes are proven
Two access services can arrive on separate invoices and still disappear in the same civil-works incident. Resilience begins when the shared failure domains are made visible, not when procurement adds a second supplier name.
IETF
David Lawrence and the DNS Answer That Outlived Its TTL
When a DNS answer reaches the end of its TTL, a recursive resolver normally discards or refreshes it. RFC 8767 allows a narrower choice during failure: preserve the expired copy for a bounded time, return it only after a real refresh attempt cannot produce usable data, and keep…

History
The Acknowledgement That Stopped at the Link: How PPP Localized Reliability
In 1994, PPP acquired an optional way to number, acknowledge and retransmit frames across one link. RFC 1663 made that recovery loop precise—and kept its authority deliberately narrow. A returned acknowledgement could establish progress between two adjacent peers; it could not…

History
The Hierarchy Was Really a Graph: How Gopher Put the Next Server Inside Every Menu Line
Gopher made a scattered collection of autonomous machines look like one calm hierarchy. The illusion did not come from a global catalogue or a persistent session. It came from a modest menu line that separated what a reader saw from what a client had to do next: interpret a type…

IETF
Steve Sheng and the Lock That Did Not Stop DNSSEC Maintenance
A domain can display an update lock while its DNSSEC delegation data still changes legitimately. RFC 10026 resolves the apparent contradiction by asking what the lock actually binds: which actor set it, whose command it rejects, and which independently authenticated maintenance…

History
The Report That Could Not Declare the Link Bad: How PPP Kept Quality Policy Local
A PPP peer could say how many packets and octets it had sent, and return what it had seen from the other direction. It could not make the protocol pronounce the link acceptable. Link-Quality-Reports standardized a shared accounting mechanism while leaving the threshold, the…