
Summary
- RFC 1422 made a public key credible through a certificate path, not through message encoding alone.
- Issuance, naming, validation, and revocation remained distinct points of institutional control.
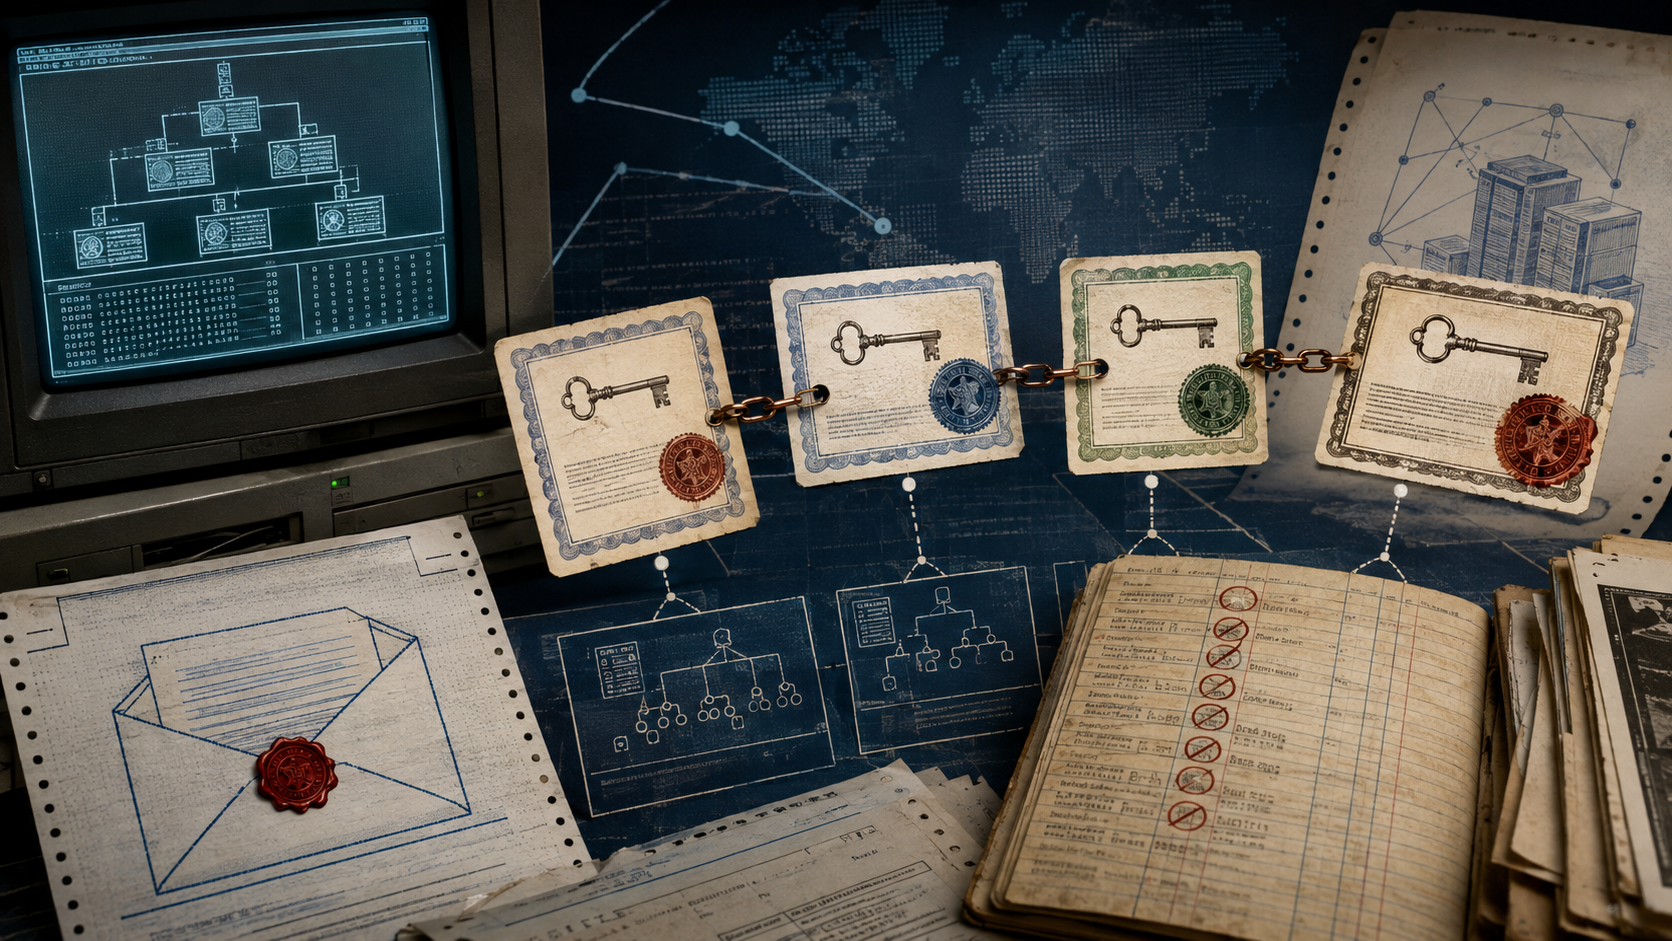
RFC 1421 described how protected mail was represented and processed. RFC 1422 answered a different question: why should a recipient believe that a particular public key belonged to the named sender? Its answer joined signed certificates into a hierarchy whose path could be evaluated by a relying party.
That path turned identity into a sequence of accountable assertions. A certification authority signed the binding between a name and a key; another authority could establish the issuer's place in the hierarchy. Validation therefore depended on more than cryptography. Names had to be interpreted, issuers had to be trusted, paths had to be assembled, and revocation information had to be consulted.
Sources
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance