Summary
- Femi Alla's individual Internet-Draft, revision 02 dated 31 October, proposes a hosted identity document for AI agents. Suspension leaves the hostname allocated but reduces its public document to version, suspended status and hostname.
- The new revision says the provider should answer a fresh key-directory request successfully with an empty key set when an identity is suspended. That lets a verifier replace cached signing keys instead of keeping them after a failed fetch.
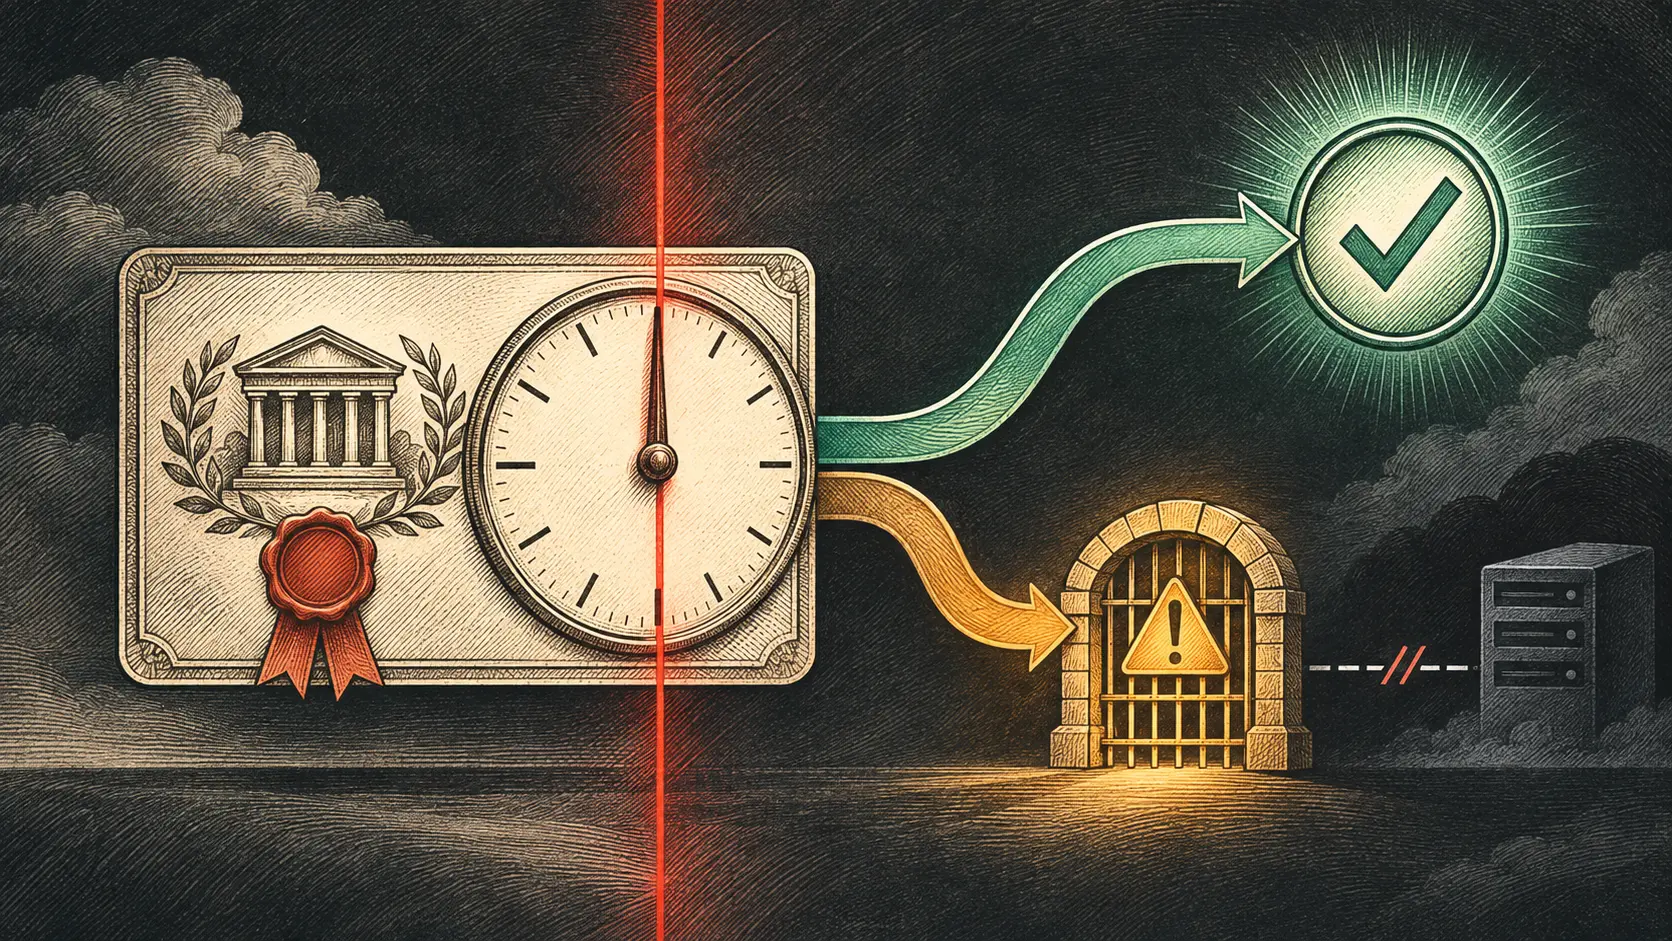
- The effect depends on the verifier fetching again. The draft's reference implementation uses a 60-second identity-document cache lifetime; it does not establish a universal instant at which all old keys disappear.
The public sign comes down; the key may linger
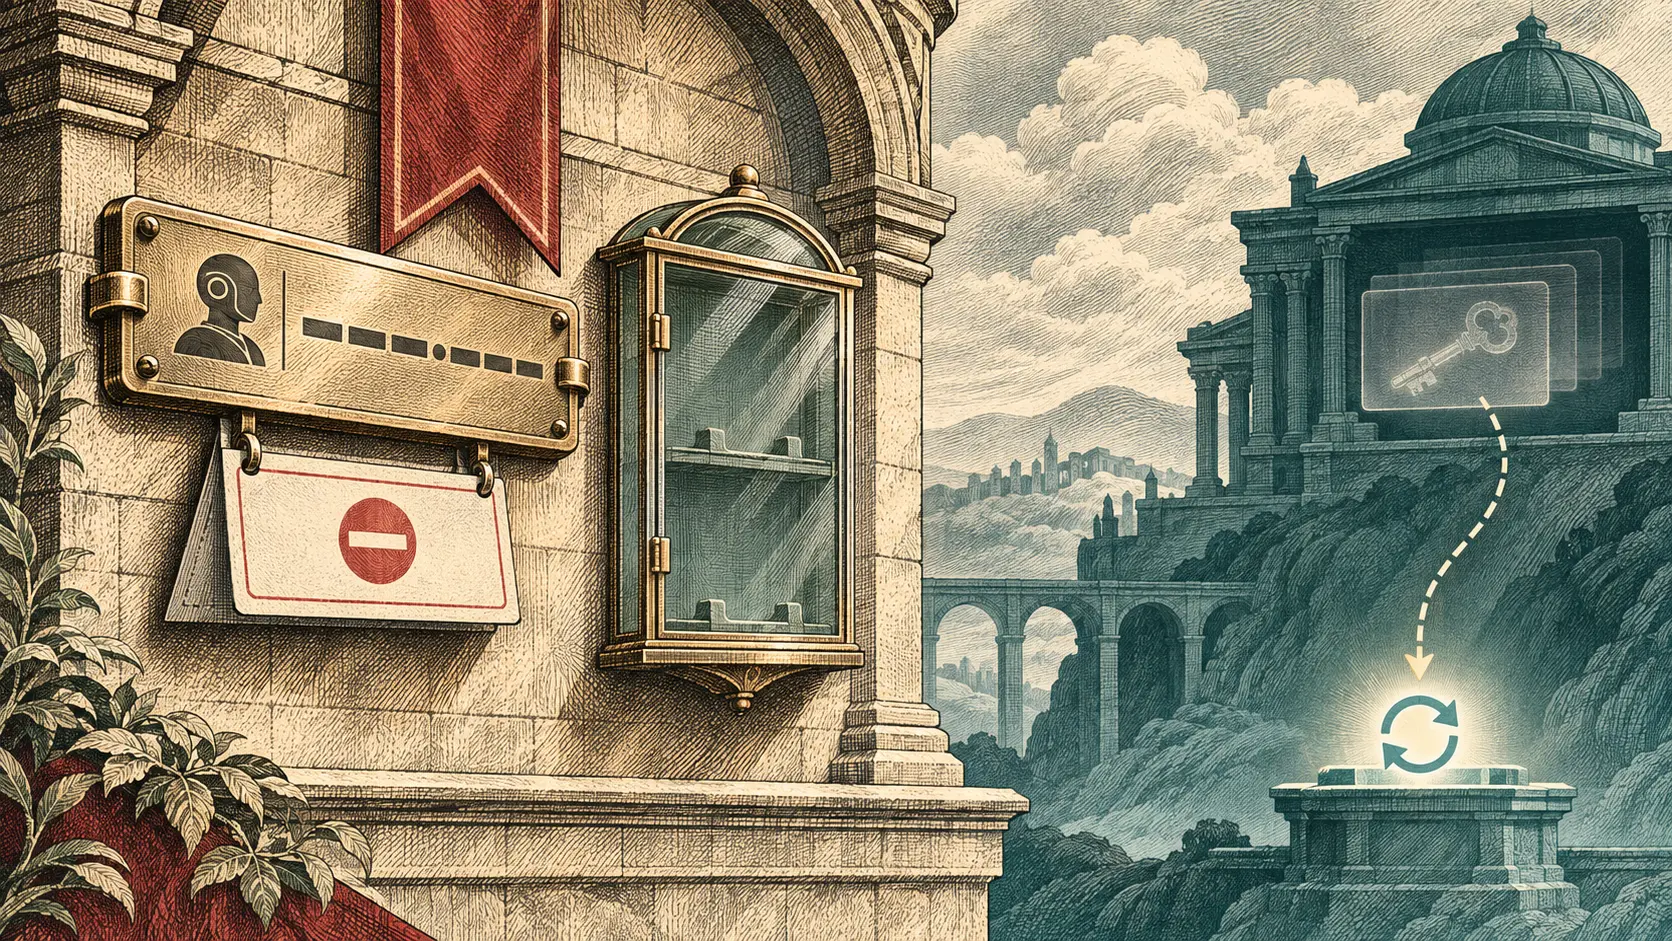
Imagine a provider suspending a hosted agent identity. It changes the public document to a minimal record. No service endpoints, description, contact or owner block remain in it. DNS still points to the provider, and the name stays allocated so another account cannot grab it. A counterparty that reads the document learns the suspension. A counterparty that only looks at a previously cached signing key may be staring at yesterday's authority.
Alla's The Agent Identity Document: A Hosted, Accountable Public Record for AI Agents separates those surfaces. Section 3 says status records a lifecycle decision, not whether the agent is online. A sleeping service can retain an active identity; a suspended identity can retain DNS. The provider controls the record, but a relying party decides when to read it and how long to hold a copy. This makes suspension a sequence of observable steps rather than a magic switch.
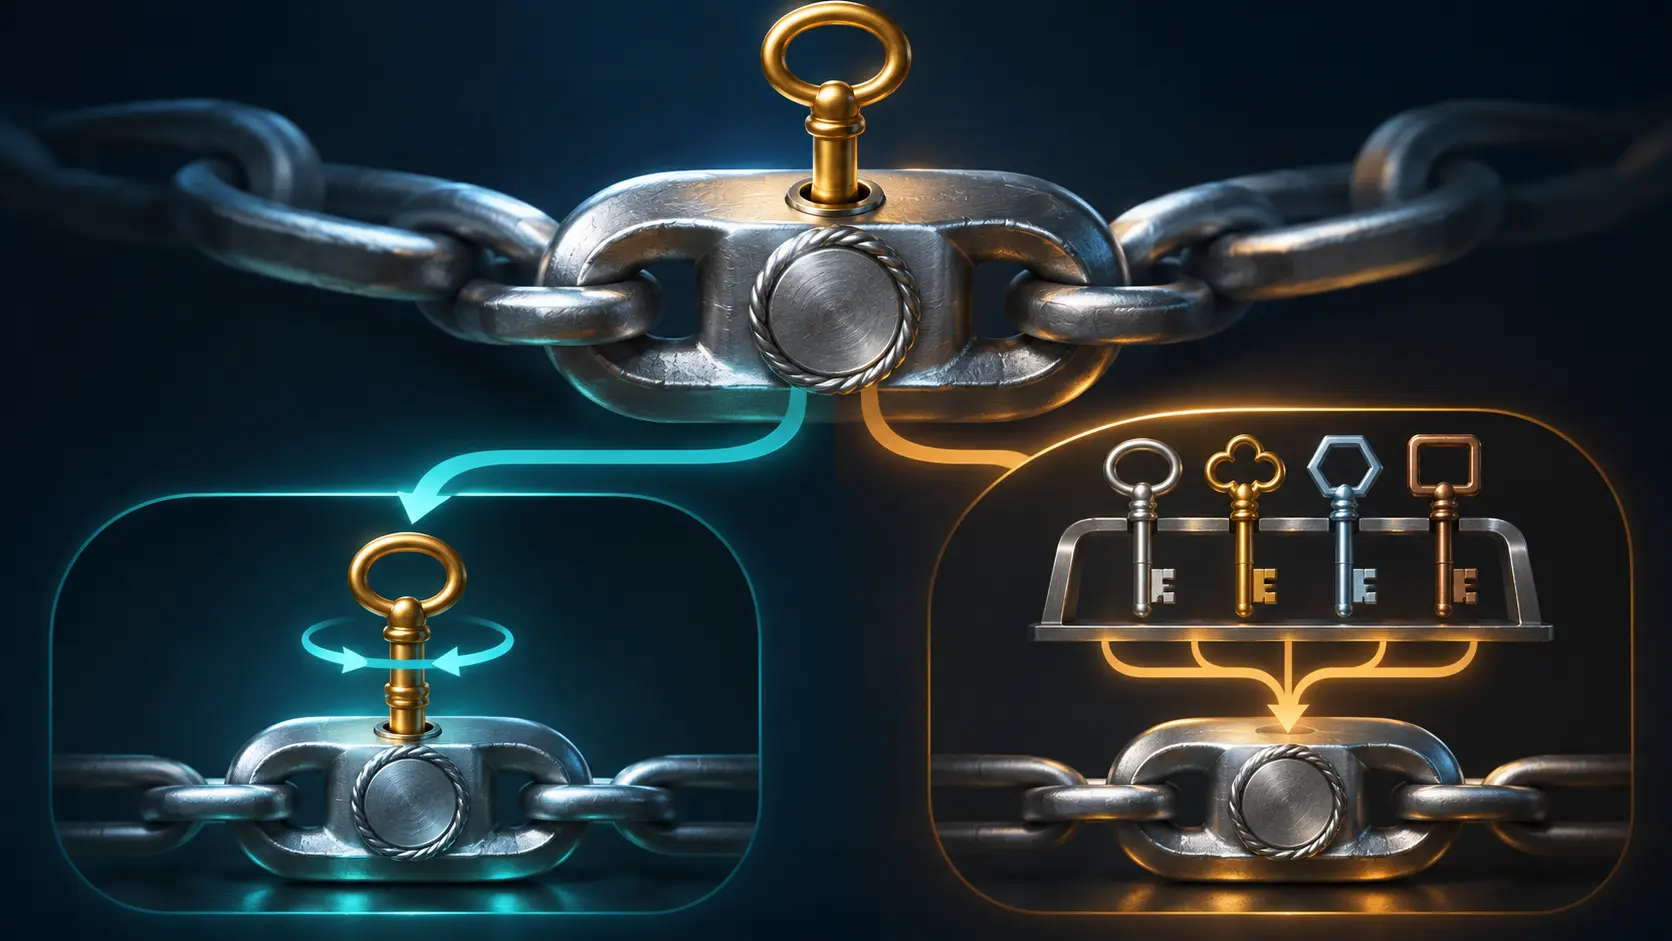
Revision 02 adds a pointed rule for signed requests. Where the provider hosts the key directory associated with the agent's identity hostname, it should return a successful response containing an empty key set after suspension. The success code matters. A verifier that treats an error as a temporary retrieval problem may keep its old keys. An explicit empty set gives a re-fetching verifier a replacement state. The draft specifies no refresh instant for every external verifier.
The proposal also warns against the wrong key. The identity document permits an operator-supplied public_key field, but gives it no verification role. The signing key directory is a separate provider-served resource. A hostname on its own is merely a claim. A signed request whose key can be found in the directory offers evidence the verifier can check. After suspension and a fresh empty-directory read, that evidence is no longer there. The record of suspension, the directory response and the verifier's actual decision need to be examined separately.
The Datatracker lists revision 02 as an active individual Internet-Draft, not an adopted RFC. Its Appendix B identifies the empty successful key set as a change from -01. The precise operational question for any adopter is how soon its relying parties re-fetch both the identity document and the key directory. A documented verifier refresh result would show whether the draft's suspension path works across that particular boundary. Without it, a provider's red status label is only one receipt in the chain.
Official sources
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance