Summary
- An ICANN researcher’s RIPE 93 abstract reports that Category 1 gTLDs had malicious registrations in more months, yet smaller campaigns when abuse appeared; the combined model predicts less malicious-domain volume overall.
- Within Category 1, restricted Level 8 registries showed lower occurrence and smaller campaigns than the more open, self-certified Level 3 group.
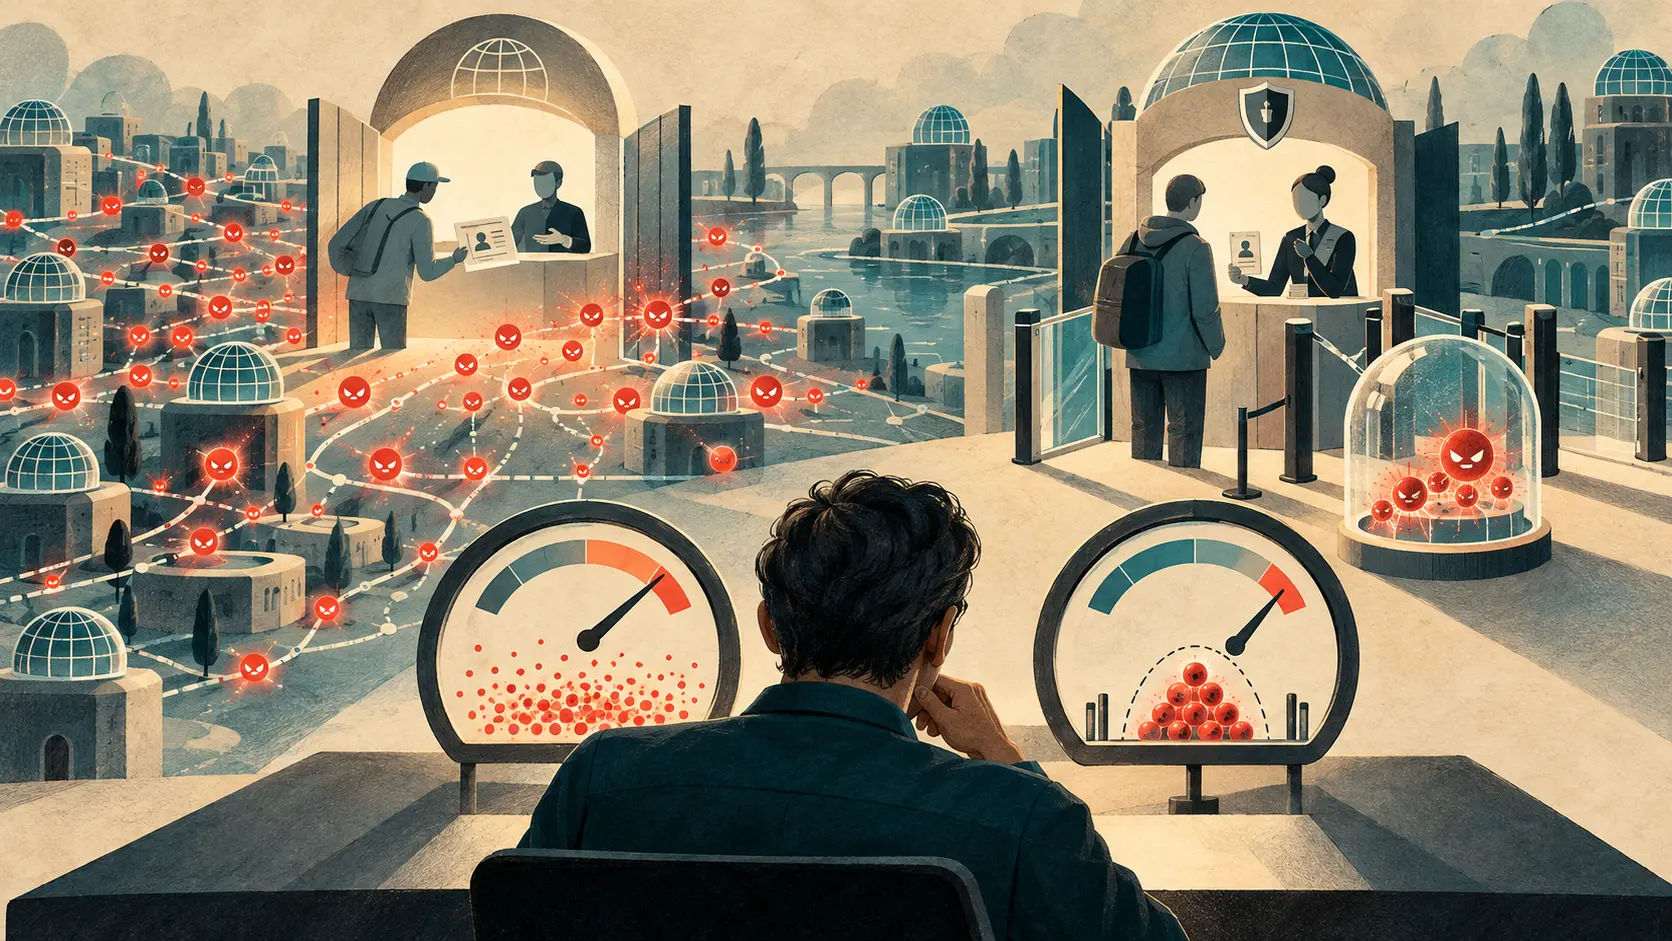
A bouncer who keeps a room at twenty people has done something useful even if somebody troublesome still gets in. That is the two-part scorecard in Carlos Gañan’s RIPE 93 research abstract. His ICANN team analyzed 1,106 new generic top-level domains month by month during 2023–2025. It measured two events separately: whether maliciously registered domains appeared in a gTLD that month, and how large the campaign became once they appeared. The plenary is scheduled for Tuesday afternoon; these are results published in its advance abstract.
The first result may make a press officer reach for a different chart. After accounting for gTLD size, registry architecture and shared monthly conditions, Category 1 namespaces were associated with abuse in more months than the comparison group. When abuse did appear, campaigns were substantially smaller. The combined model predicted a lower malicious-domain volume overall. One average rate would blend the frequency and size into a single reassuring or alarming number; the two-part result tells an operator what kind of work remains.
The comparison inside Category 1 sharpens the point. Registries with restricted Level 8 entry showed lower occurrence, smaller campaigns and lower overall volume than the more open Level 3 group that relies on self-certification. Those labels describe different registration models in the study, rather than a universal ranking of every TLD. The abstract gives directions of association, not percentages or a randomized test, so the mechanism still needs inspection at the registration desk.
ICANN’s original Category 1 policy record explains why the desk exists. Governmental Advisory Committee advice identified strings tied to regulated or sensitive sectors. ICANN’s 2014 implementation placed corresponding safeguards in Specification 11 of affected registry agreements as mandatory public-interest commitments. A contract can require a check; the research now asks how the check shows up in malicious registrations.
For an operator facing phishing domains, the useful dashboard has at least three counters: attempted registration, successful malicious entry and campaign size after entry. Add the time to detection and remediation. If a policy claims prevention while the entry counter rises, its managers need the rejected-attempt and verification records. If containment is the real gain, say so and fund the response path that produced it.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance