
Intelligence
Latest Articles
Latest intelligence on infrastructure operators, policy decisions, market moves, and digital power shifts.
History
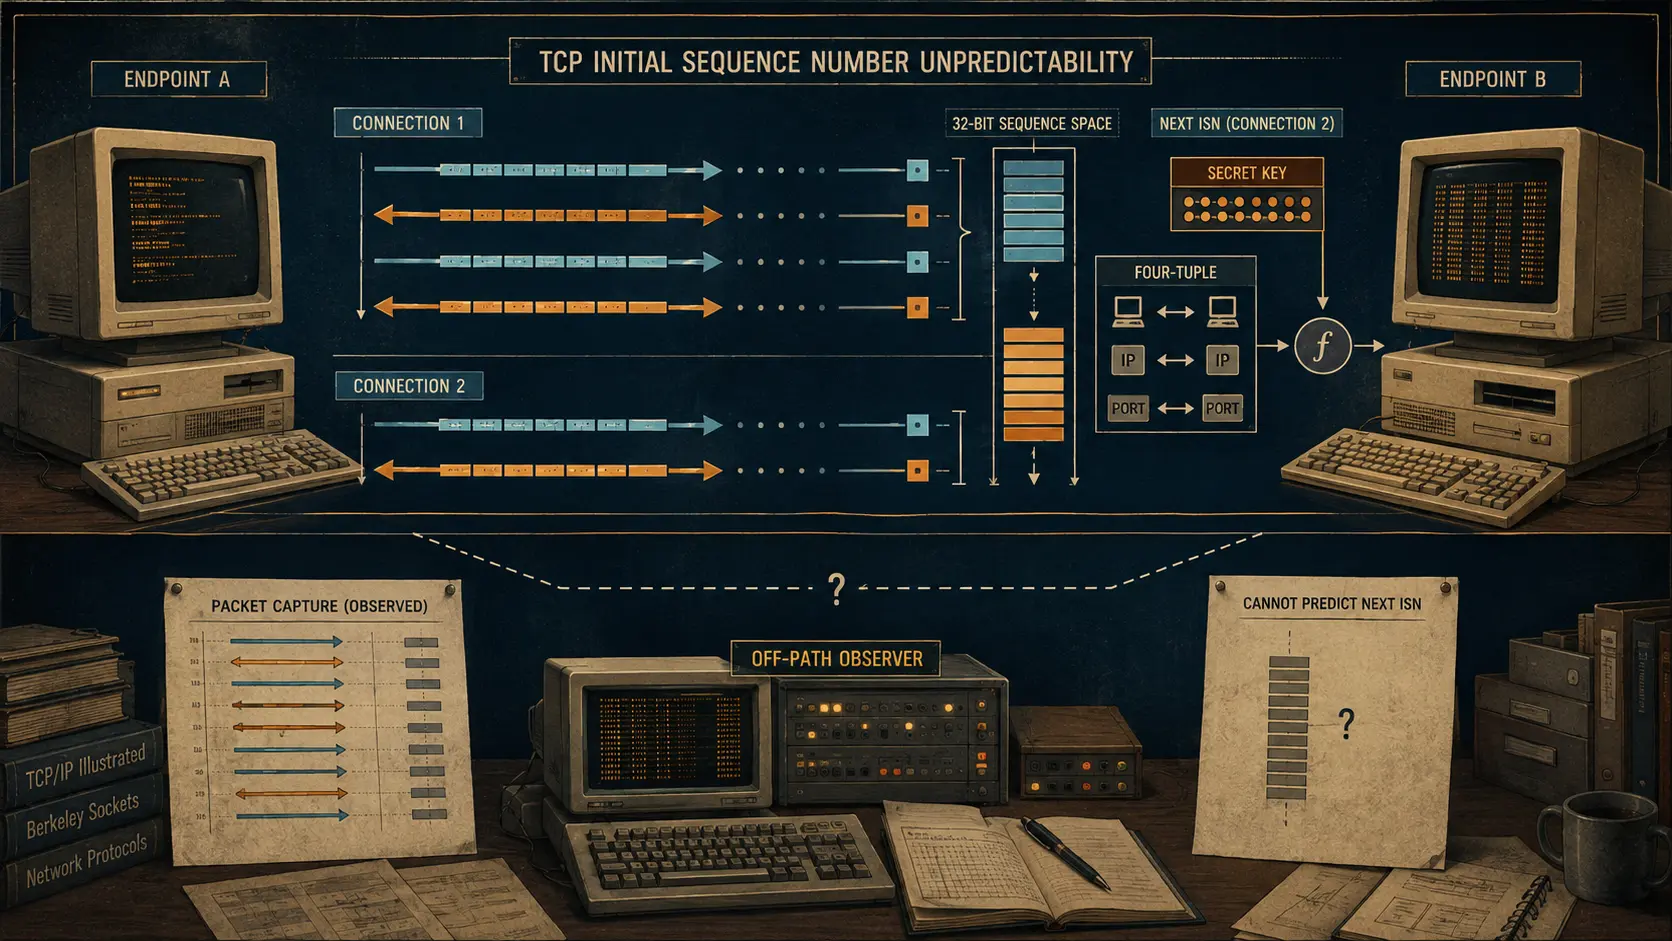
The Number Made Harder for an Off-Path Attacker to Predict: TCP Initial Sequence Numbers
A TCP connection begins by exchanging numbers. The security change was not to hide that exchange, but to stop one visible number from revealing the next connection's starting point.
Global Institutional Trends
A Valid Software Signature Is Not a Durable Authority Record
A green verification result can survive long after the authority that made a release legitimate has changed. The cryptography may still be sound. The missing evidence is organisational: who was permitted to sign, under which role, at what time, and what later revocation or…
ICANN
A Zone File Is Shared Access, Not Permission to Republish the Namespace
At 09:00, an approved researcher downloads a gTLD zone file through ICANN's Centralized Zone Data Service. The archive is complete enough for the contracted transfer, and its checksum matches. Those facts establish delivery. They do not establish who owns every listed domain, why…

IETF
One Delete Command Can Break Someone Else's Domain: RFC 9874 and EPP Dependency Control
A destructive EPP transition is not necessarily local to the client that requests it. When a subordinate host is still associated with domains sponsored by other clients, deleting that host can alter their DNS dependencies, consistency, and ability to resolve. RFC 9874 is a…
Story
AFRINIC Received 1,024 ASNs. The Public Record Separates Inventory from Allocation
IANA recorded a new 1,024-number block for AFRINIC on 25 February 2026, and AFRINIC announced the addition to its inventory on 27 March. Those records establish upstream custody, not downstream allocation of every number to operators.

Global Regional ISP Trends
A Graceful BGP Restart Can Lengthen a Blackhole
Graceful Restart is meant to keep traffic moving while a BGP process returns. Its safety depends on a fact the surviving session cannot prove by itself: whether the restarting router still has the forwarding state needed to carry packets. When a helper retains a route longer than…

IETF
The Second Address Became the Primary One: What RFC 9873 Changes in EPP Contact Data
RFC 9873 turns a contact update into a more explicit state transition: an EPP contact may carry one additional email address, and an optional `primary` attribute says which address is to be treated as primary. The protocol records that relationship; it does not certify the…
IETF
Default Reject Turns Missing EBGP Policy from Silent Authority into an Explicit Failure
An external BGP session can be established while its authority to receive or advertise routes remains undefined. RFC 8212 changes the default at that boundary: without import policy, accept no routes; without export policy, announce none. The leadership question is not whether a…

CASE FILE
Sixty Names Were Defendants; the Statute Still Defined the Claim: Harrods v Sixty Internet Domain Names
The caption did something unusual: it named sixty domain names as defendants. That procedural choice made a dispute over the Harrods name look, for a moment, like a dispute over things rather than people. The Fourth Circuit’s answer was narrower. The names could be before the…

History
The Chain That Made a Public Key Believable: PEM Certificate Management
A public key does not identify its owner by itself. RFC 1422 addressed that gap for Privacy Enhanced Mail by specifying certificates, certification authorities, validation paths, and revocation information—the institutional machinery needed before a relying party could treat a…

IETF
Enhanced uRPF Lets an Operator Admit Feasible Source Paths Without Trusting Every Route
A valid packet from a multihomed customer can arrive on a link that the receiving router would not choose for the return journey. Strict reverse-path forwarding may discard it; loose checking may accept any routed source. RFC 8704 defines a narrower middle ground: build an…
IETF
The Prefix Arrived Before the Query: How RFC 9872 Changes NAT64 Discovery
An IPv6-only host that must reach IPv4 services needs to know which IPv6 prefix its network uses for address synthesis. RFC 9872 turns that knowledge into an access-network signal: learn PREF64 from Router Advertisements first, and use DNS discovery only when that signal is…

Global Regional ISP Trends
A Fast IPv4 Fallback Can Make Broken IPv6 Look Healthy
A dual-stack service can answer every ordinary check while its IPv6 path is unusable. The availability result is real, but the protocol-family conclusion is not: a client may have escaped through IPv4 before the dashboard noticed what failed.
History
The Pointer That Was Never Out of Band: TCP Urgent Data
TCP urgent data is a small control surface with a long history. The URG flag makes a 16-bit urgent pointer meaningful, but RFC 793 described the boundary it marks in two contradictory ways. That ambiguity crossed from the specification into implementations and application APIs.

IETF
ZONEMD Lets a Secondary Verify the Zone After the Transfer Ends
A completed zone transfer proves that a delivery procedure finished. It does not, by itself, prove that the receiver assembled the exact zone the publisher intended. ZONEMD adds a digest over the zone as a whole, creating a verification boundary after transport and before a…

IETF
The Bitmap Says a UDP Option Appeared—not What It Did: RFC 9870
RFC 9870 gives IPFIX exporters a compact way to report which UDP Option kinds appeared in a Flow. Its bitmaps are useful precisely because their claim is narrow: they preserve observed presence, not a packet history, a receiver’s processing decision or an application outcome.

Global Cloud Services Trends
Backblaze's customer-held keys change who operates the second copy
Keeping encryption keys can be a deliberate purchase of control. In Backblaze B2, it also changes which copying service a customer can use—and where the continuing operating work has to sit.

Story
A Failed RIPE Database Update Can Still Change Records
RIPE NCC's documentation describes an update message whose entities can finish differently. The useful response is therefore not just a verdict on the message: it is an account of the changes already made, those rejected and those the caller still cannot confirm.

Story
LACNIC’s IPv4 transfer market and the price of scarcity
IPv4 exhaustion does not end allocation politics. It changes the place where they happen: from the distribution of a free pool to the rules governing transfers of resources that are already held.
IETF
Maciek Konstantynowicz and the Benchmark Result That Was Not a Service Guarantee
A network benchmark earns its value by saying exactly what it measured. RFC 9971 makes that discipline explicit: its MLRsearch result is a bounded result from stated trials and goals, not a transferable promise about every customer path, application or production hour.