
Policy continuity, legitimacy, and accountability signals across internet governance institutions.
Governance
Governance
Internet governance intelligence tracks institutions, policy processes, standards activity, registry operations, accountability disputes, and implementation signals that affect internet infrastructure. BTW.
RIR WatchdogCase FileNumber Resource SocietyICANNIETFHistory of InternetNOGs

RIR Watchdog, Case File, NRS, ICANN, IETF, History of Internet, and NOG sessions.
Coverage prioritizes implementation evidence and institutional behavior over declarative positions.
Latest Coverage
Latest from Governance
7,610 articles
IETF
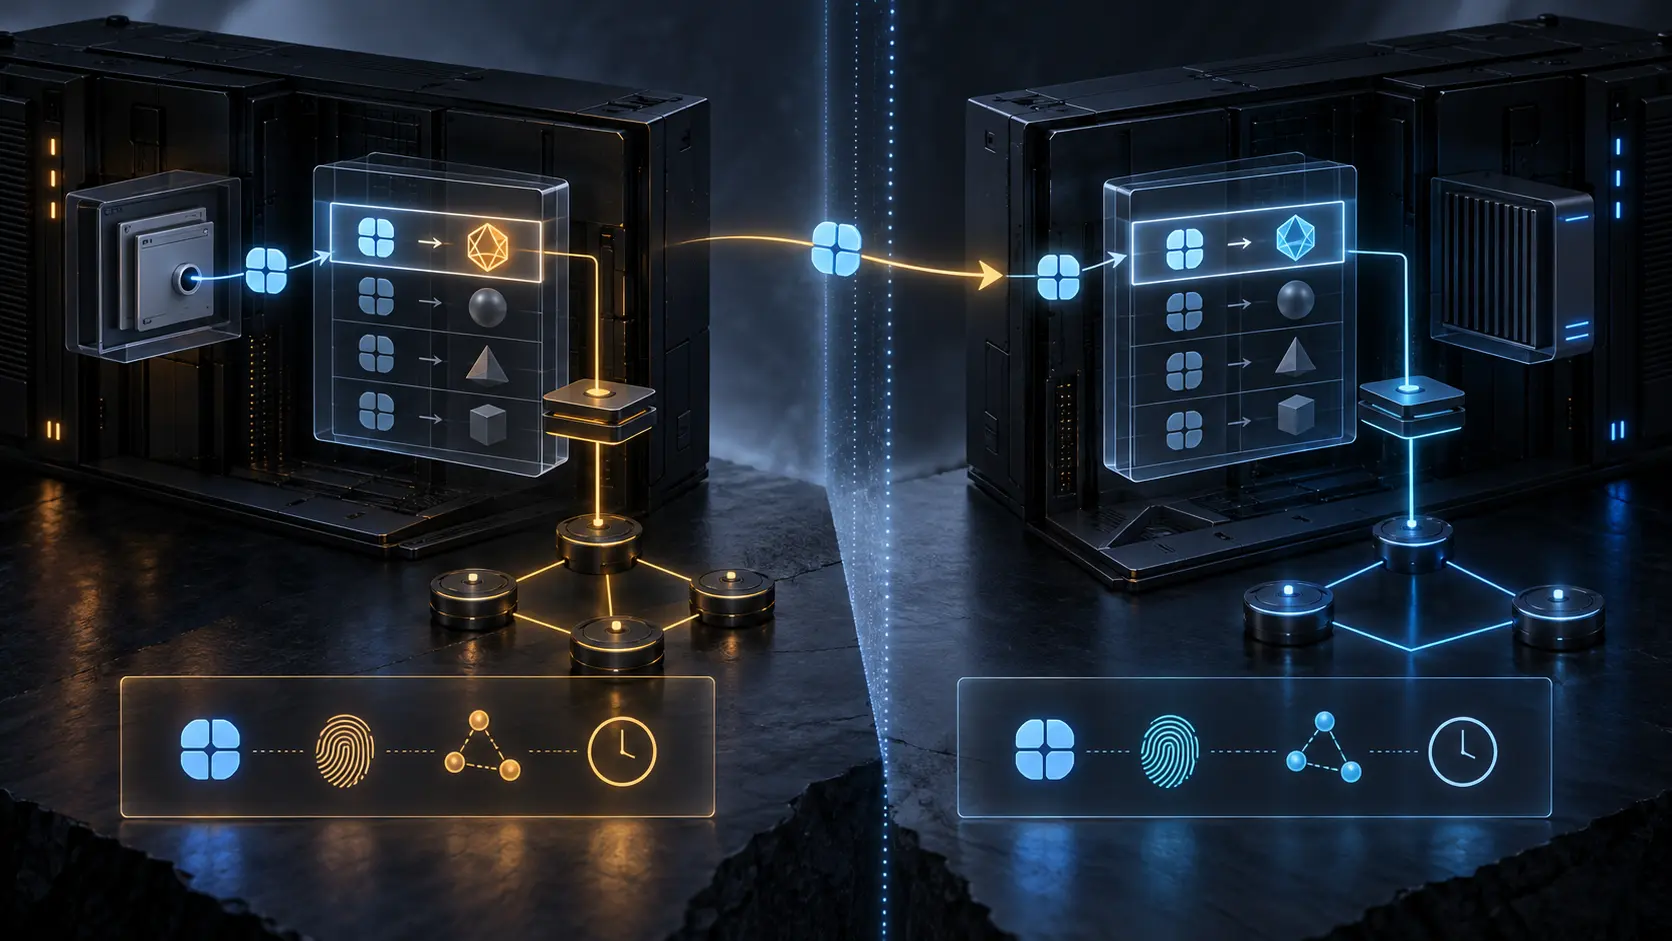
The Address Worked Here. On the Next Host, It Named Someone Else.
A legacy program saw an IPv4-shaped value and did what programs have done for decades: cached it, logged it, and handed it to a peer. The value was a HIP Local Scope Identifier. Its meaning ended at the machine that created it.
History
Same Cipher, Three Parameter Rules: Camellia in CMS
CMS does not identify encryption with a cipher name alone. RFC 3657 gave Camellia different algorithm identifiers for protecting content, wrapping a content key and announcing capability—and each context treats parameters differently.
IETF
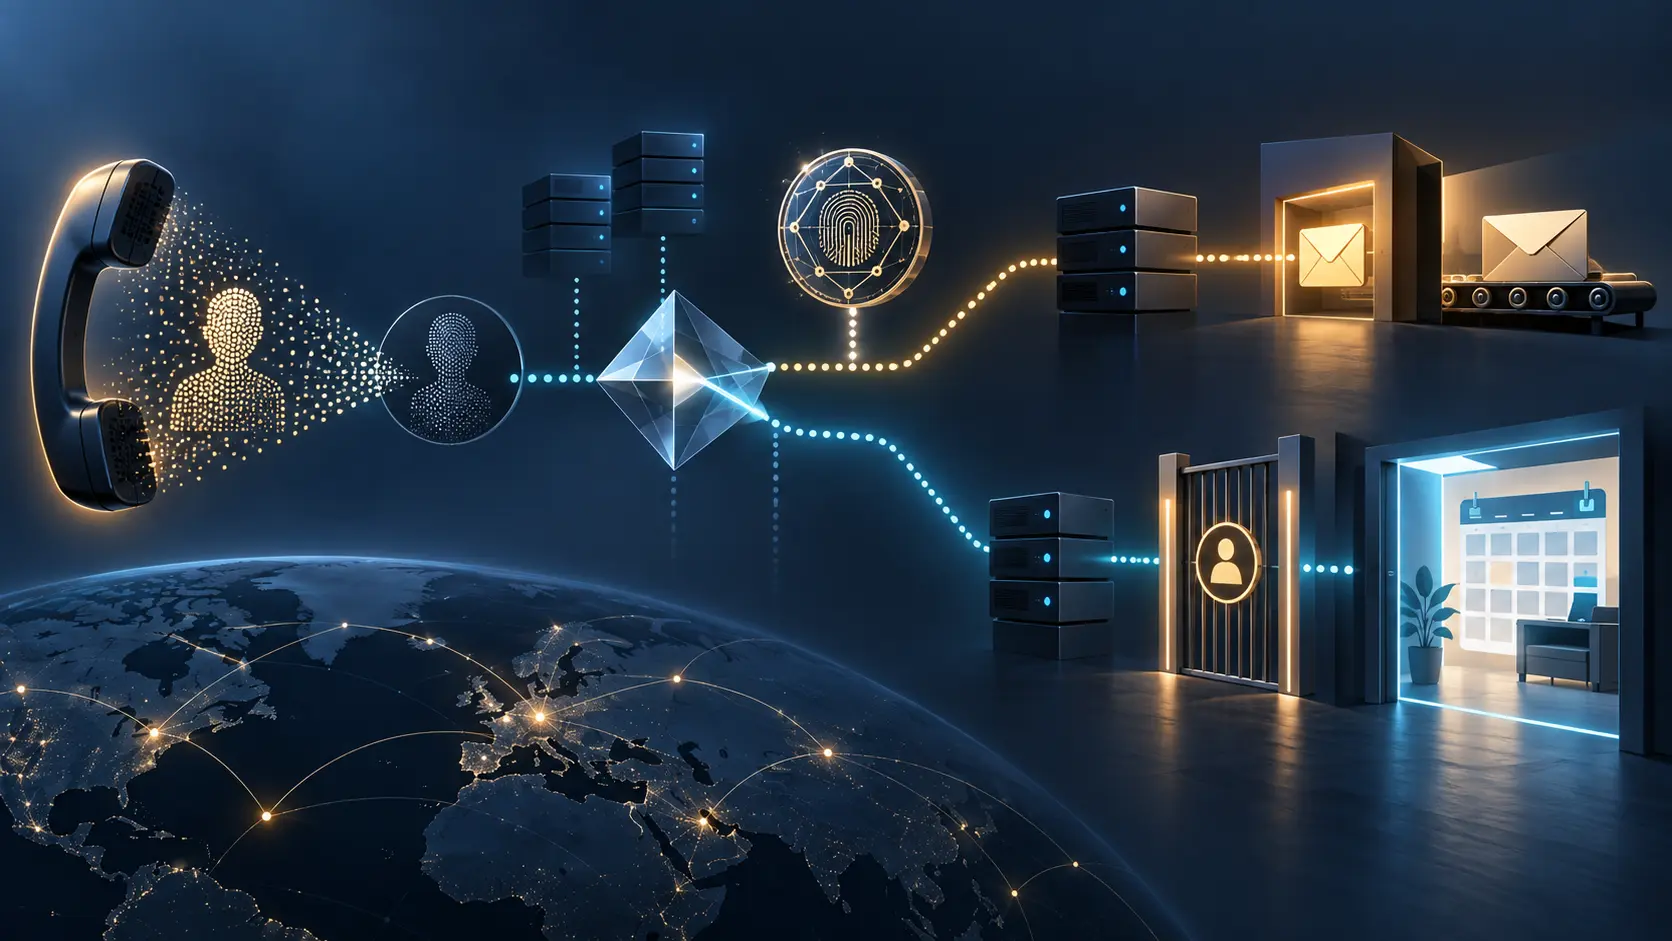
A Phone Number Found Two Calendar Doors. It Scheduled Nothing.
One ENUM lookup can return an HTTPS calendar resource and a mail address for scheduling. Both are useful discoveries. Neither says that the caller may enter the calendar, that an invitation reached the intended person, or that a meeting now exists. RFC 5333 is valuable precisely…
History
A Name Was Reserved. The Mailbox Was Not Ready: RFC 3656
In a distributed mail service, preventing two servers from claiming one mailbox name is only half the job. RFC 3656 separated that namespace claim from the later state in which clients could actually use the mailbox.

IETF
The Multicast EtherType Stopped Meaning “Multicast”
A trace decoder sees Ethernet type `0x8848` and prints “MPLS multicast.” That label looks harmless because it repeats the old registry name. Under RFC 5332, however, the decisive fact is different: on the specified multicast Ethernet path, the top MPLS label was…

History
The TCP Counters Stayed Shared. The Connection Needed a Fifth Coordinate: RFC 2452
An IPv6 transition did not force the TCP management model to start over. RFC 2452 kept most transport counters common, then added one interface coordinate where an IPv6 connection row could otherwise be ambiguous.

IETF
The Header Said Audio. The Container Still Held More Than Sound.
A correct label can still be an incomplete inventory. RFC 5334 designed `audio/ogg`, `video/ogg`, and `application/ogg` around the container’s predominant use, while leaving every logical stream to be identified and processed separately.
IETF
The Count Fell. The LSPs Did Not.
Consider a migration in which one link's advertised unconstrained-TE-LSP count drops from 84 to 51 while every expected tunnel remains in service. Nothing has to be removed for that change to occur. A new originator can stop counting LSPs provisioned through the management…

History
The RFC Number Looked Like a Standard. The IESG Said It Wasn't: RFC 3924
RFC 3924 placed a vendor architecture for lawful interception inside the RFC Series, then put an unusually plain warning above it: Informational, not an Internet Standard, and not reviewed by the IETF for security or protocol interaction.

IETF
The Outer Label Was Removed One Hop Early. The Inner Label Lost Its Table.
Penultimate-hop-popping is normally an efficiency: remove an MPLS tunnel label before the egress so the last router has less work. RFC 5331 identifies the case where that optimization destroys evidence. An upstream-assigned inner label has meaning only inside the label space…

History
A Gateway Could Change the Wrapper, Not the Message: RFC 3923
In 2004, RFC 3923 gave XMPP a way to carry signed or encrypted messages through a gateway to another messaging system. Its most consequential instruction was also its narrowest: translate the envelope, never the protected entity.

IETF
Every Router Carried the Advertisement. Not Every Router Understood It.
RFC 5329 deliberately lets an OSPFv3 Traffic Engineering LSA cross an area through routers that do not recognize its type. That is a compatibility achievement, not a semantic receipt. The same packet trail can prove excellent flooding and still leave the TE database empty…

History
RMON Could Name MPLS, Not Its Children: RFC 3919
An RMON probe could distinguish two MPLS entry types, yet RFC 3919 stopped short of giving the label stack a universal protocol family tree. The contrast with IPv6 shows where an identifier can travel—and where its meaning must stop.
IETF
The Name Survived. One Resolver Path Did Not.
RFC 5328 gave DVB metadata a persistent, location-independent name. It did not make that name a live route, an authenticated entity or proof that a receiver used the resource. A `urn:dvb` string can remain valid while one discovery path fails, another returns a new locator and a…
IETF
The Retransmission Was Byte-Perfect. Its Cookie Was Already Obsolete.
RFC 5327 gives an LTP session a security state that can change while a signal is still crossing the link. A cookie may grow after the original segment leaves, and a retransmission must carry the value current now, not the value that was correct then. Authentication can protect…

History
One Tagged Frame, Many Multicast Clocks
In a multicast test, one packet leaves one ingress and arrives at many exits. RFC 3918’s key measurement choice was to keep those arrivals separate: a headline latency number could not tell an operator which branch had paid the delay.

IETF
The Sender Finished the Session. The Green Bytes Were Never Confirmed.
RFC 5326 designed a transport for links where a reply might take minutes, interruptions are scheduled and retransmission capacity is expensive. Its completion notice is exact: every byte was transmitted, and the receiver reported the reliable red prefix. It does not say the…
IETF
The Policy Row Existed. The Fabric Had Not Activated It.
RFC 5324 gives an operator a large management surface for Fibre Channel security: editable policy entities, activation controls, negotiated Security Association pairs, traffic selectors, counters and bounded event history. Those records describe different stages. A configured row…

History
DHCP Gave Vendors Separate Option Spaces, Not IANA-Defined Meanings
In 2004, DHCPv4 gained a way to place several vendors’ configuration data in one exchange without pretending that a shared packet made their private option vocabularies the same. RFC 3925 widened the envelope; it did not standardize everything inside it.

IETF
The Fragment Was Feedback. It Was Not Proof of the Path.
RFC 5320 proposed an experimental tunnel layer that lets IPv4 fragmentation occur, observes it, and then tunes future packet sizes. Its SEAL_ID and feedback window can associate a report with recent traffic, but they do not identify the constraining link or prove reassembly…
Session Map
Governance Branch
RIR Watchdog
Five regional sessions tracking allocation policy, board legitimacy, and institutional continuity.
Open RIR WatchdogCase File
Long-cycle governance dossiers with legal, election, and institutional stress analysis.
Open Case FileNumber Resource Society
Membership, charter, and resource-governance intelligence from the NRS ecosystem.
Open NRS SessionICANN
DNS coordination, accountability frameworks, and global multi-stakeholder process dynamics.
Open ICANN SessionIETF
Protocol standardization trajectory and interoperability risk under fragmented policy conditions.
Open IETF SessionHistory of Internet
Long-cycle infrastructure history used for governance interpretation and structural forecasting.
Open History SessionNOGs
Operator-level implementation intelligence from APRICOT plus regional and national NOG ecosystems.
Open NOGs Session