
Summary
- RFC 5328 registers
dvbas a formal URN namespace and puts individual assignment under DVB’s standards process. A well-formed string becomes evidence of a valid assigned name only after the namespace rules and the relevant DVB catalogue agree. - Resolution then follows receiver-dependent broadcast, multicast, HTTP or DNS-discovered paths. Authentication of the name or resource travels as separate information, so persistence, reachability, authenticity, rendering and use must never share one green state.
A durable name is designed to outlive a route
The attractive sentence is also the dangerous one: the identifier persists. It invites a dashboard to treat continued recognition of a name as continued operation of everything behind it.
That is not what RFC 5328 specifies. The declared form is urn:dvb:<NSS>. DVB assigns individual names through its standards-development process and may delegate portions of the namespace to other parties operating under its regime. It promises not to reassign an assigned string and commits to maintaining accessibility and persistence for officially assigned resources.
Those are governance properties of a naming system. They do not constitute a probe result from a television receiver, a DNS answer, a multicast observation, an HTTP response or a resource-authentication event. Indeed, the point of a location-independent name is that the current location can change without changing the name.
A monitoring system that couples name persistence to one resolver endpoint reverses that design. It converts a stable identifier into a brittle alias for the infrastructure seen on one day.
Syntax does not complete assignment
The string can parse perfectly and still lack the record that makes it an assigned DVB name. RFC 5328 says that presence in a DVB-maintained URN catalogue indicates validity. Its registration template lists no intrinsic validation mechanism beyond that catalogue practice.
The later general URN specification, RFC 8141, makes the boundary explicit: syntactical correctness of a string beginning with urn: is insufficient. The Namespace Identifier must be registered, and the assigned-name portion must comply with the rules of that namespace.
An evidence chain therefore starts with exact input octets and parsing, then records the IANA NID registry version, the DVB namespace rules, the assigning authority or delegation, the catalogue consulted, its version and the membership result. valid=true without those coordinates is an unrepeatable conclusion.
Even catalogue membership answers only the assignment question. It does not say which resolver a particular receiver can reach, what that resolver returned or whether the returned resource is authentic.
Case folding is not content equivalence
RFC 5328 declares the Namespace Specific String case-insensitive. That tells implementations how to compare names. It does not say that every representation retrieved for two lexically equivalent forms is byte-identical, fresh or trustworthy.
Lexical equivalence closes one identity comparison. It does not close the catalogue version, resolver policy, locator selection, cache state, content hash or trust chain. If two systems normalize the same input and obtain different resources, the problem cannot be explained away by saying that the URNs compare equal.
The receipt should preserve both the literal form supplied and the normalized comparison form. Otherwise an investigation cannot distinguish harmless case variation from a resolver or catalogue divergence that occurred after comparison.
There was deliberately no single resolver
RFC 5328 anticipated implementations with sharply different access methods. It therefore points to no universal resolution or delegation mechanism.
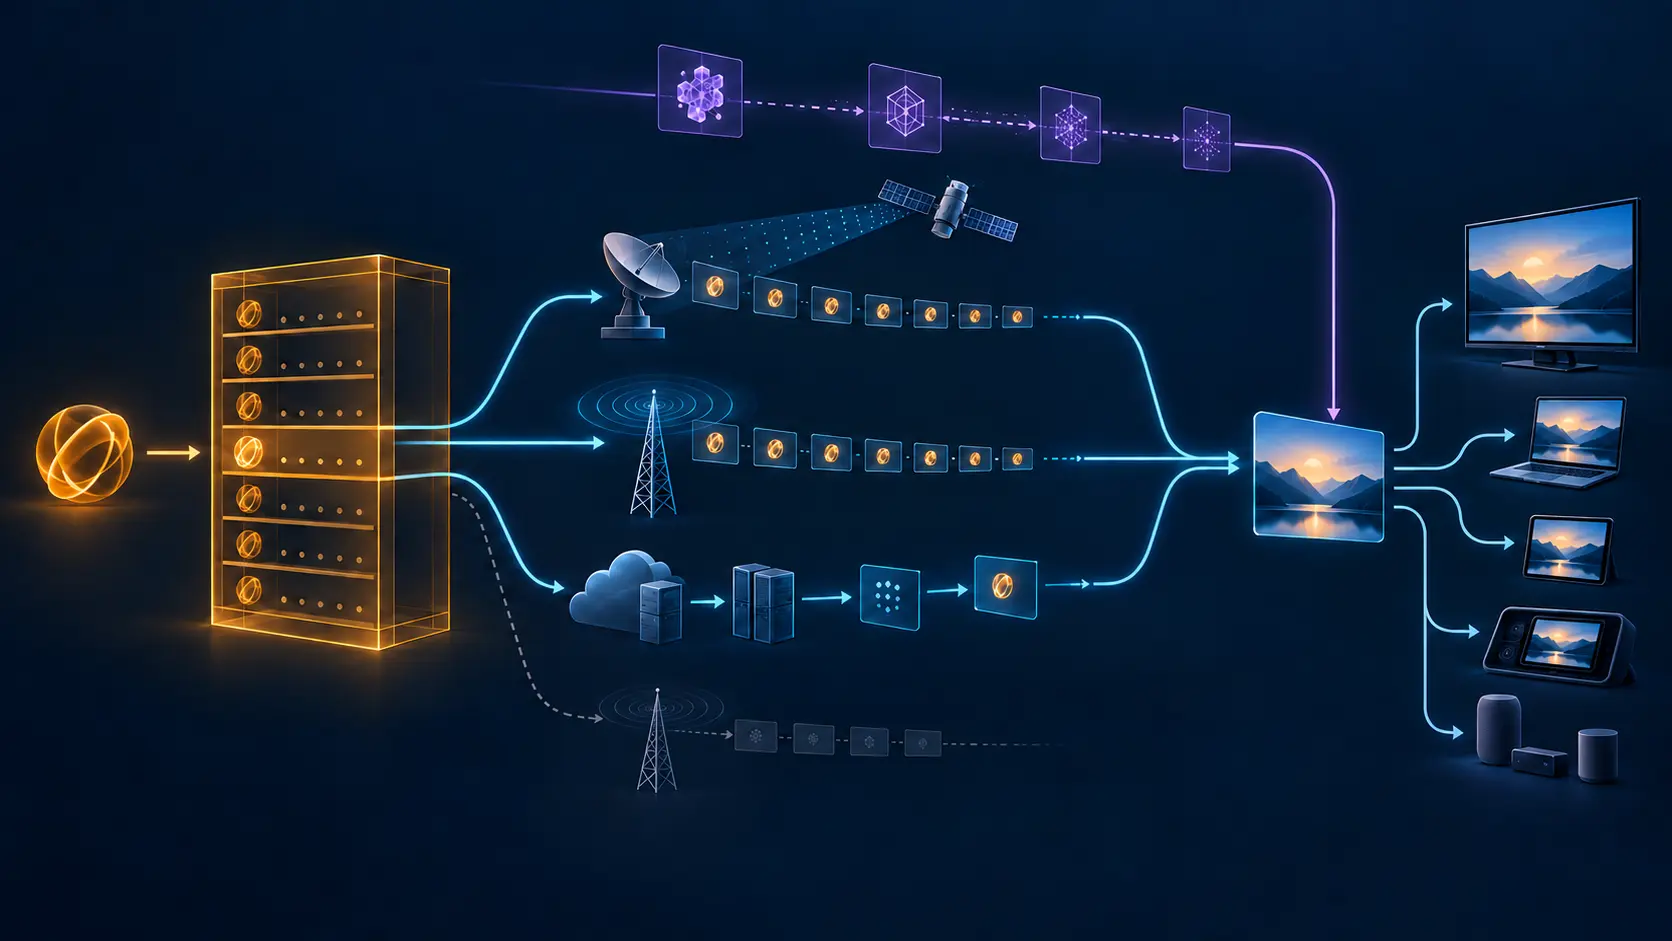
A receive-only broadcast set-top box cannot ask an arbitrary Internet service the same way as a home-network device behind an IP gateway. The first needs resolution information carried in service-discovery data in the broadcast stream. The second may discover and contact a network service.
The document describes several conveyance paths: repeated cyclic Resolution Authority Records and Resolution Records in broadcast streams; repeated cyclic multicast Resolution Records through DVBSTP; and unicast Resolution Records returned by an HTTP request to /dvb/sdns.
These paths are not redundant checkboxes attached to one abstract success. They have different transports, observation points, caches, delay profiles and failure modes. Success through unicast HTTP cannot stand in for the broadcast carousel available to a receive-only device. Receipt of a multicast record does not prove that another receiver joined the same group or trusted the same authority.
Bootstrapping is another decision surface
Before resolving a name, a client needs an entry point for Service Discovery and Selection. RFC 5328 describes defaults that use the dvbservdsc service, TCP and UDP port 3937 and registered multicast addresses. It also describes non-default discovery through DNS SRV records beneath services.dvb.org.
Each coordinate proves less than its name suggests. An IANA service or port assignment establishes a shared numeric and symbolic meaning; it does not prove a listener. A registered multicast address does not prove membership, routing or packet reception. A DNS SRV answer can point to an endpoint without proving that the endpoint answers, carries current authority or returns a usable Resolution Record.
The bootstrap receipt must therefore end where its evidence ends: discovery method, queried owner, DNS or multicast observation, returned entry point and timestamp. Resolution begins after that. Retrieval begins after resolution. Use begins later still.
RFC 8553 subsequently aligned underscored DNS node-name use in RFC 5328 and many other documents with an integrated IANA registry model. That maintenance coordinates the meaning of a DNS label. It is not retroactive availability evidence for a DVB service.
A catalogue is not a resolver health check
Catalogue membership can remain correct while a resolver is unreachable. A resolver can answer while serving an older catalogue projection. Two resolver paths can be reachable and disagree because they observe different policy epochs or caches.
Those are not contradictions in the persistent identifier. They are separate operational facts around it.
Useful telemetry records catalogue publication time, version and signer or authority; resolver discovery source; selected resolution authority; cache age; returned locator set; and the receiver class that made the attempt. A final boolean discards the exact boundaries that explain why one device works while another does not.
The design should also tolerate the retirement of a current location. The durable name can continue while its resolution data moves. Declaring the URN dead because one locator disappeared confuses the named resource with one historical access path.
Authentication does not fit inside the name
RFC 5328 says that when a URN is resolved into a location, the resource may need authentication. Information authenticating either the name or the resource should be carried separately with the URN rather than inside the URN itself.
That sentence is the authority boundary. A formal namespace registration does not sign every assigned name. A catalogue entry does not authenticate every object returned through every resolver. An HTTP success does not establish that the object is the one an authorized DVB authority intended. Neither a recognizable prefix nor a familiar resource type supplies a trust anchor.
The security receipt must identify what was authenticated, by which mechanism, against which trust material, under which policy and at what time. It must not inherit authority from urn:dvb, from IANA’s NID row, from the resolver transport or from a successful parse.
RFC 5328 also leaves the security consequences of special character meanings inside the NSS to DVB specifications. A generic parser cannot infer authorization from the apparent internal structure of the string.
Contact maintenance is not semantic proof
RFC 7354 updated the declared registrant and registration contact information, using a role-based email address to reduce later churn. It explicitly left all other registration fields unchanged.
That makes the document useful governance evidence: the contact record was refreshed without replacing the namespace. It does not prove that catalogues, DNS, multicast, HTTP endpoints or named resources were refreshed at the same time.
Conflating administrative contact currency with operational state creates a particularly persuasive false green. The registry looks maintained, so the service is assumed healthy. The actual service evidence has not been collected.
The examples are not inventory
RFC 5328 includes two example names and warns that they are pedagogical and not guaranteed to be real. Copying them into a scanner or asset list would manufacture an operational claim from documentation syntax.
Examples prove how a name may look. They do not prove assignment, catalogue membership, resolution, resource existence or permission to use a resource. Documentation extractors should tag them as examples and prevent their promotion into inventory without a separate catalogue receipt.
The same discipline applies to a valid IANA registry row. It establishes a coordinate in a public control plane. It does not populate the namespace beneath that coordinate.
Retrieval still does not finish the chain
A resolver may return a locator, metadata or a representation. A client may retrieve bytes. Neither event establishes that the bytes were parsed, rendered, authorized for the intended application or used successfully.
RFC 5328 discusses metadata for multimedia and interactive services across devices with different capabilities. That diversity increases the gap between retrieval and outcome. A resource usable by one receiver class may need transformation for another; an object can be authentic but unsupported; a representation can render while an interactive service still fails.
Keep retrieval status, content hash, freshness, parser result, rendering result, application authorization and user or service outcome as later receipts. The URN is the durable join key among them, not permission to collapse them.
The minimal receipt is longer than the name
For a claimed urn:dvb use, preserve the exact input and normalized comparison form; NID registry version; namespace-rule result; assigning authority and delegation; catalogue identity, version and membership; receiver class; available access channel; discovery and bootstrap evidence; Resolution Authority and Resolution Records; selected authority; returned locator or representation; independent authentication result; retrieval hash and freshness; parser and renderer results; application authorization; and observed outcome.
This looks expensive only when compared with a boolean that cannot be audited. The additional fields are the minimum needed to distinguish a persistent name from a working and authorized service.
Sources
- https://www.rfc-editor.org/rfc/rfc5328.html
- https://www.rfc-editor.org/rfc/rfc5328.txt
- https://www.rfc-editor.org/info/rfc5328/
- https://datatracker.ietf.org/doc/rfc5328/
- https://datatracker.ietf.org/doc/rfc5328/history/
- https://datatracker.ietf.org/doc/rfc5328/references/
- https://datatracker.ietf.org/doc/rfc5328/referencedby/
- https://www.rfc-editor.org/errata/rfc5328
- https://www.rfc-editor.org/rfc/rfc7354.html
- https://www.rfc-editor.org/rfc/rfc8553.html
- https://www.rfc-editor.org/rfc/rfc8141.html
- https://www.rfc-editor.org/rfc/rfc3406.html
- https://www.rfc-editor.org/rfc/rfc1737.html
- https://www.rfc-editor.org/rfc/rfc2276.html
- https://www.iana.org/assignments/urn-namespaces/urn-namespaces.xhtml
- https://www.iana.org/assignments/service-names-port-numbers/service-names-port-numbers.xhtml
- https://heng.lu/running-code-primary-the-patch-needed-to-preserve-the-internet-original-design/
- https://heng.lu/on-reality-layers-symbolic-power-and-why-clarity-feels-so-hostile/
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance