
Policy continuity, legitimacy, and accountability signals across internet governance institutions.
Governance
Governance
Internet governance intelligence tracks institutions, policy processes, standards activity, registry operations, accountability disputes, and implementation signals that affect internet infrastructure. BTW.
RIR WatchdogCase FileNumber Resource SocietyICANNIETFHistory of InternetNOGs

RIR Watchdog, Case File, NRS, ICANN, IETF, History of Internet, and NOG sessions.
Coverage prioritizes implementation evidence and institutional behavior over declarative positions.
Latest Coverage
Latest from Governance
8,175 articles

SANOG
SANOG’s Six-NOG Committee Does Not Cover Its Eight-Country Map
SANOG describes a region of eight countries. Its published future governance strategy, however, routes local-NOG representation through six named forums. That leaves Afghanistan and Maldives without the same visible institutional path into the Core Committee.

History
A Local Service Was Not Control of the Network: RFC 1291’s Mid-Level Boundary
In 1991, a mid-level network could make the Internet more usable without becoming the Internet's owner. RFC 1291 proposed local DNS capacity, software-discovery pointers, time servers, news feeds, mailing-list relays, testbeds, information services and NOC contacts. Its design…

Story
AFRINIC Says It Added JSContact. Its RDAP Guide Does Not Say Which One.
AFRINIC’s public record contains a useful sentence and an unfinished question. The current release entry for WHOIS 2.10.7 says that an RDAP feature called JSContact was added. The current RDAP guide tells a reader where the service is, which resources may be queried, which…
CASE FILE
The Inventory Found the Algorithm. It Did Not Migrate the System: RFC 9958 and Cryptographic Agility
An organisation can catalogue every algorithm name it knows and still be unable to say which cryptographic path protects a consequential transaction. RFC 9958 makes the inventory indispensable. It does not allow the inventory to pronounce a migration complete.
CASE FILE
W3C’s Profiles Draft Can Inherit Conformance. The Proof Layer Is Still Unsettled
A machine can follow two RDF links and produce a third: a resource conforms to a profile; that profile is a profile of a specification; therefore the resource conforms to the specification. The W3C’s new Profiles Vocabulary draft makes that inference explicit. It also exposes why…
History
It Worked at NASA. That Did Not Make It Safe for the Internet: RFC 1106 and RFC 1110
June 1989 produced an unusually honest sentence in protocol history: two experimental TCP extensions had been implemented and shown to work using NASA resources. Two months later, another RFC explained why one of them still could not be adopted for the general Internet. The test…

CASE FILE
The Color Reached PCEP. It Did Not Reach the Service: RFC 9863
RFC 9863 lets PCEP carry a color for a TE path. That is useful coordination data. It is not a guarantee that a service was mapped, a latency objective was met, or a customer received a result.

Story
RIPE’s IRR Study Says RPKI Can Replace a Route Object, Not a Customer Cone
A new RIPE Labs study makes a useful distinction that is easy to lose in general talk about replacing the IRR. A prefix–origin record and the policy information used to discover a customer cone are not the same operational entity, so they cannot share one retirement decision.
ICANN
ICANN’s DNS-Abuse Debate Turns One Blocklist Count Into a Floor and a Ceiling
Interisle looked at names created in 2025, found 8.5 million that entered selected blocklists and called the result a floor. ICANN answered that reported-abuse statistics are, at best, an upper limit on confirmed abuse. Both descriptions can be logically coherent, but only if the…

History
A Pointer Was Not the Information: RFC 1290 Had Not Made the Route Invisible
In 1991, the problem was not a lack of material on the network. RFC 1290 described the opposite: information and file repositories so abundant that browsing could consume a lifetime. The problem was how a person crossed from abundance to something usable. The document separated…

CASE FILE
The UUID Sorted. The Event Was Not Proven: RFC 9562 and the Boundary Between Identifier Order and Evidence Time
At 14:03, a review screen puts two rows in an immaculate order. The smaller UUIDv7 belongs to `reversal-requested`; the larger one belongs to `reversal-completed`. It looks like a ready-made account of what happened. But the first identifier may have been allocated before a…
CASE FILE
DNS Received the Hint. The Parent Still Had to Decide: RFC 9859’s Delegation Boundary
RFC 9859 can make delegation maintenance faster. It cannot make a notification into a parent-side decision, or turn a received response into proof that DNSSEC or delegation state has changed.

History
Changing the Route Was Not the Same as Filtering the Packet: RFC 1104
In June 1989, RFC 1104 divided “policy routing” into mechanisms that were already easy to confuse. A network could change which reachability it disclosed, inspect a particular packet, assign scarce bandwidth or buffers, and record usage for later accounting. Each act could be…

History
A SHUT State Was Not an Off Node: RFC 1289 Kept the Existing Links
The word “shutdown” invites a clean story: an operator chooses a state, a node stops, and the work is over. RFC 1289 preserves a more demanding chronology. Its DECnet Phase IV MIB did not treat every admission restriction as an OFF node. `SHUT` allowed no new logical links, but…
IETF
Todd Herr and the DMARC Pass That Did Not Make the Message Safe
The green word `pass` can be perfectly correct and dangerously misunderstood. In DMARC it certifies a narrow relationship between domains. It does not certify the person in the display name, the proposition in the message, the attachment behind the button or the wisdom of putting…

CASE FILE
The Router Repaired the Path. It Did Not Restore the Service: RFC 9855 and TI-LFA’s Local Boundary
A router can react to a directly attached failure in milliseconds and still know nothing about whether a customer service has recovered. RFC 9855 gives Segment Routing deployments a disciplined way to precompute and activate a loop-free repair path at the Point of Local Repair.…

CASE FILE
WCAG-EM’s 10% Random Check Is Not 10% of the Product
An accessibility report can contain a precise percentage and still leave its denominator invisible. W3C’s new WCAG Evaluation Methodology says the random part of a representative sample should equal 10% of the structured part. It does not say that evaluators inspect 10% of the…
CASE FILE
The Collector Received a Delay. It Did Not Receive a Verdict: RFC 9951
At 09:17, a collector receives a Flow Record with a mean delay, a maximum delay and an identifier for the transit point that exported them. By 09:20, someone wants the record to settle three larger questions: whether a customer suffered, whether a path changed, and which team…
NPNOG
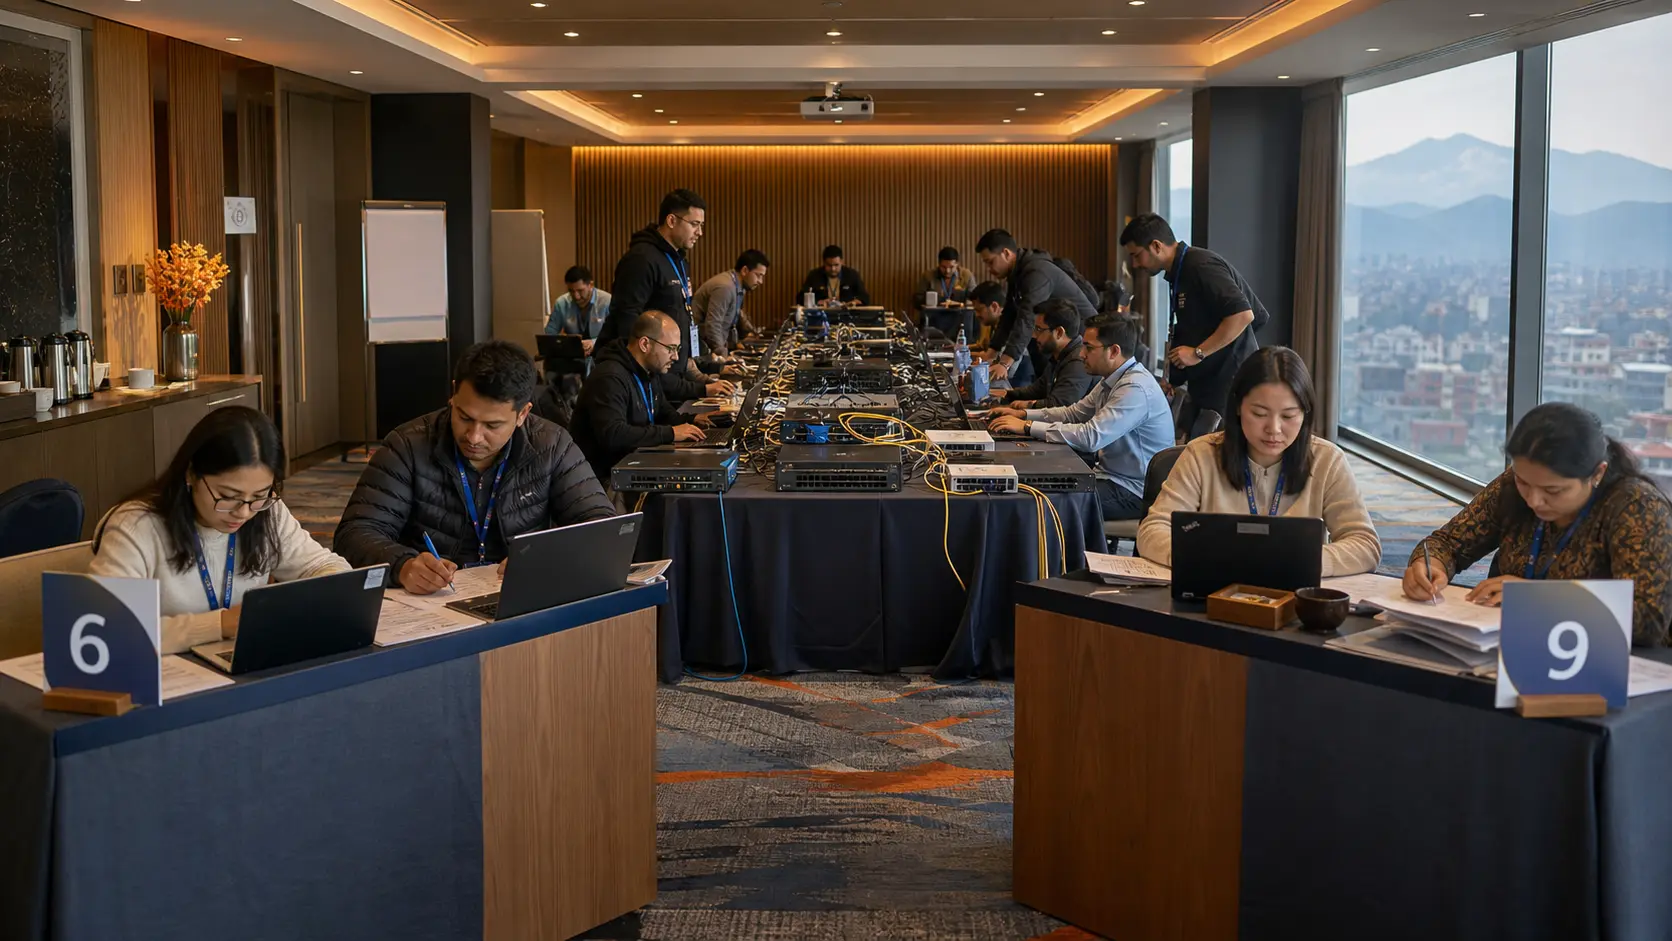
One Week, Two Institutions—and Two Edition Numbers: Untangling npNOG and SANOG-38
In July 2022, operators arriving at the Kathmandu Marriott encountered one technical week: four workshop days followed by a conference. The surviving institutional record is less unified. npNOG calls the event NPNOG-6 with SANOG-38. SANOG's contemporaneous pages called the same…

History
The Architecture Retreat Named Five Problems. It Did Not Pick the Next Internet: RFC 1287
In 1991, a group of Internet architects looked at growth, address exhaustion, multiple protocol suites, security, real-time traffic and the next generation of applications. RFC 1287 is the record they left behind. It is tempting to read such a record backwards: it discusses…
Session Map
Governance Branch
RIR Watchdog
Five regional sessions tracking allocation policy, board legitimacy, and institutional continuity.
Open RIR WatchdogCase File
Long-cycle governance dossiers with legal, election, and institutional stress analysis.
Open Case FileNumber Resource Society
Membership, charter, and resource-governance intelligence from the NRS ecosystem.
Open NRS SessionICANN
DNS coordination, accountability frameworks, and global multi-stakeholder process dynamics.
Open ICANN SessionIETF
Protocol standardization trajectory and interoperability risk under fragmented policy conditions.
Open IETF SessionHistory of Internet
Long-cycle infrastructure history used for governance interpretation and structural forecasting.
Open History SessionNOGs
Operator-level implementation intelligence from APRICOT plus regional and national NOG ecosystems.
Open NOGs Session