
Policy continuity, legitimacy, and accountability signals across internet governance institutions.
Governance
Governance
Internet governance intelligence tracks institutions, policy processes, standards activity, registry operations, accountability disputes, and implementation signals that affect internet infrastructure. BTW.
RIR WatchdogCase FileNumber Resource SocietyICANNIETFHistory of InternetNOGs

RIR Watchdog, Case File, NRS, ICANN, IETF, History of Internet, and NOG sessions.
Coverage prioritizes implementation evidence and institutional behavior over declarative positions.
Latest Coverage
Latest from Governance
8,021 articles
CASE FILE
OpenJS CPC's New Community Vote Needs a Transition Receipt
This autumn, OpenJS Foundation’s Cross Project Council will replace two separate non-Impact voting paths with one Community Voting Member class. The Charter is unusually clear about the planned change: it names the effective election cycle, caps the new class at five seats and…

ICANN
ccNSO Draws a Boundary for ICANN’s IDN Follow-Up
The Council’s July answer permits enquiries prompted by a reasonable basis, while rejecting active compliance policing. A September Board discussion will consider the next steps for the still-pending recommendations.

IETF
BGP Roles Turn a Peering Relationship into a Route-Leak Boundary
Before two networks exchange a single route, each can state what kind of neighbour it believes it has. RFC 9234 turns that bilateral statement into a control: incompatible roles can stop the session, while the Only-to-Customer attribute can stop a marked route from crossing the…
IETF
Rich Salz and the TLS 1.3 Requirement That Was Not a Deployment Receipt
A standard can make a demanding rule without manufacturing the evidence that the rule has become true in every running system. That distinction is not a loophole; it is how an operator can tell a sound protocol decision from an unsupported deployment claim. Rich Salz’s…

History
The Module Kept Its Name. The Device Did Not Prove Its Version: RFC 1442
A monitoring console can display a MIB module's latest revision date with complete confidence and still know almost nothing about the code answering from a particular device. RFC 1442 gave SNMP information modules a stable identity and a disciplined memory of change. It also drew…
IETF
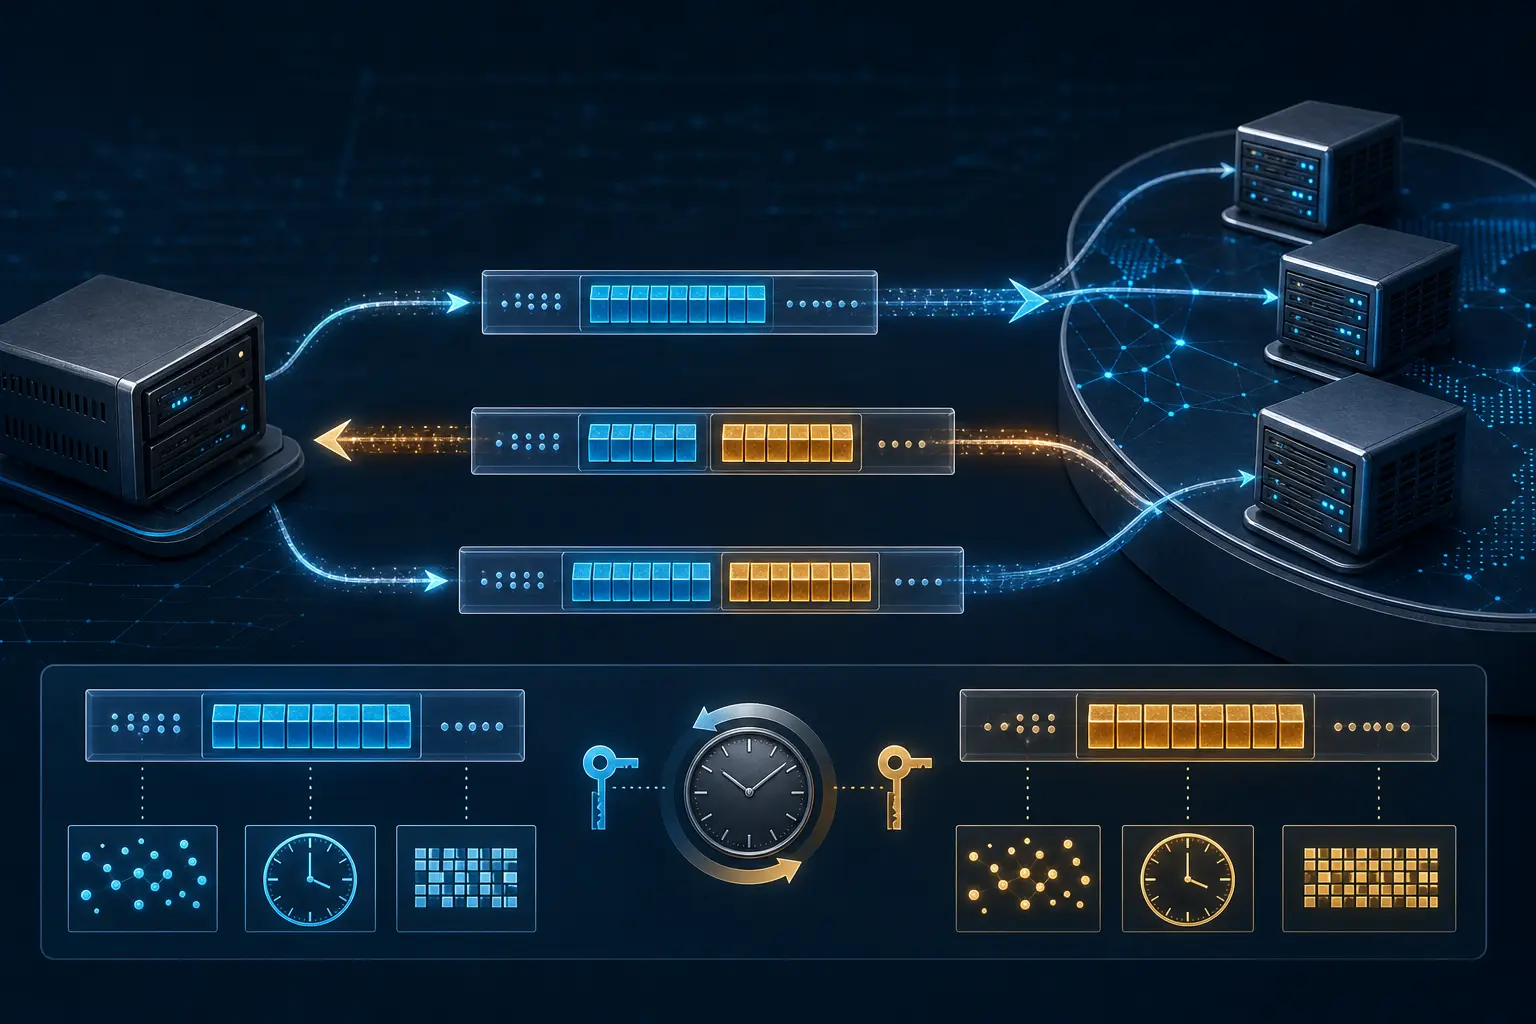
A DNS Cookie Supplies Return-Path Evidence, Not Client Identity
A valid DNS Server Cookie can show that a requester at a source address is returning a value issued in an earlier exchange. That is useful evidence against off-path forgery. It is not a login, a durable device identifier or permission to attach a person’s name to the query.

Story
ARIN’s Reverse-DNS Controls Follow the Parent Block
A customer’s address range does not tell an operator where the reverse-DNS handoff belongs. ARIN’s direct-allocation rules put the editing boundary higher in the tree than a downstream inventory may suggest.

ICANN
ICANN’s NextGen Call Qualifies Its First-Come Rule
The new nomination call offers three mentor places and three selection-committee places. Arrival order matters, but so does whether a community group has held the particular role before.

History
The Same Application Crossed Two Versions. The Proxy Changed the Operation: RFC 1452
The application asked for a bulk retrieval. The old agent never saw one. Between them, a bilingual manager consulted a local database, selected SNMPv1, zeroed two fields and changed the PDU into a single next-step request. RFC 1452 called the result transparent to the…

Story
What Comes After ARIN’s Empty Whois Replies
ARIN resolved a problem with some Whois queries in August. For anyone whose tools retained a suspect result, the next task is different: checking the local copy without turning a failed observation into a registration verdict.
IETF
Nancy Cam-Winget and the SCIM Event That Was Not a Reconciliation Receipt
An identity system can tell another domain that something changed and still leave the receiving domain with consequential work to do. It must decide whether the resource is the one it knows, whether the schemas align, whether a callback is needed, what local rule applies, and…
CASE FILE
CNCF's TAG-to-TOC Move Needs an Exit-and-Continuity Receipt
Three former Technical Advisory Group leaders entered the Cloud Native Computing Foundation's 2026 Technical Oversight Committee cohort. CNCF says they stepped down from TAG leadership because TOC members may not hold TAG lead positions at the same time. That is a useful public…
IETF
Chris Wendt and the Signed Response That Did Not Authenticate the Media
A telephone caller needs more than a signal that looks official. The practical question is whether the party reached is the intended party, what evidence supports that conclusion, and what a device should do when the evidence does not arrive. Chris Wendt’s co-authored RFC 9970…

IETF
IETF’s Vienna Space Squeeze Tests the Forecast Behind Venue Selection
A popular meeting can still run short of places to work between sessions. The IETF’s Vienna review exposes the timing problem behind a venue decision: a forecast can change after the room for adjustment has narrowed.

CASE FILE
The Slice Identifier Reached the Transport Edge. The Guarantee Still Had to Be Built: RFC 9889
RFC 9889 turns 5G network slicing into a chain of accountable translations: the mobile domain can name a slice, but the transport domain must still classify traffic, allocate resources, install state and prove the resulting service.

IETF
Michael Prorock and the Algorithm Identifier That Did Not Choose a Trust Policy
An algorithm label can make two implementations speak precisely about the same kind of key. It cannot tell a verifier why that key arrived, who stands behind it, which claims it may support, or what action the verifier should take. RFC 9964, co-authored by Michael Prorock and…
Story
APNIC’s Automation Workshop Has a Second Job: Teaching Its Successors
The Mumbai course is meant to prepare engineers to teach and rebuild their own training labs. That makes it part of a practical handoff before network automation leaves APNIC’s instructor-led curriculum at the end of 2026.

Story
APNIC REx: When a Date Becomes a Matching Key
Three historical address records changed their dates without changing their ranges. The case shows why reconstructing a resource's past also requires understanding the past of the fields used to identify it.

IETF
The IETF Trust Has a Final Chair. Its Exit Still Needs an End-State Record.
A transition can be described truthfully and still be incomplete as a public record. A named final chair tells readers who is carrying a residual office. An asset-transfer announcement tells them that an important legal step happened. Neither statement, by itself, tells them…
CASE FILE
The Token Arrived Before the Call. Verification Still Had to Wait: RFC 9888
The signed identity token reached the destination service first. The telephone call was still crossing a path that could not carry that token with it. RFC 9888 makes this split useful for legacy networks, but it also leaves an operational obligation: two arrivals on two channels…
Session Map
Governance Branch
RIR Watchdog
Five regional sessions tracking allocation policy, board legitimacy, and institutional continuity.
Open RIR WatchdogCase File
Long-cycle governance dossiers with legal, election, and institutional stress analysis.
Open Case FileNumber Resource Society
Membership, charter, and resource-governance intelligence from the NRS ecosystem.
Open NRS SessionICANN
DNS coordination, accountability frameworks, and global multi-stakeholder process dynamics.
Open ICANN SessionIETF
Protocol standardization trajectory and interoperability risk under fragmented policy conditions.
Open IETF SessionHistory of Internet
Long-cycle infrastructure history used for governance interpretation and structural forecasting.
Open History SessionNOGs
Operator-level implementation intelligence from APRICOT plus regional and national NOG ecosystems.
Open NOGs Session