
Summary
- RFC 9888 sends signed PASSporT evidence through a separate service when it cannot travel with the call.
- Verification waits until the token is fresh, authorized and matched to the arriving call.
A verification service had everything it expected from the cryptographic side. The PASSporT was signed. Its issuing credential validated. A mutually authenticated connection had delivered it to the designated Call Placement Service, or CPS. The token was fresh enough to remain in storage.
What it did not yet have was the call.
This is the problem RFC 9888 solves without pretending to abolish it. STIR ordinarily carries a PASSporT in a SIP request. That works when the signaling path preserves the relevant header end to end. It does not describe every telephone network. Border policy may remove material, a call may traverse the public switched telephone network, and a legacy provider may receive no end-to-end SIP request at all. An out-of-band service gives the signed assertion another route.
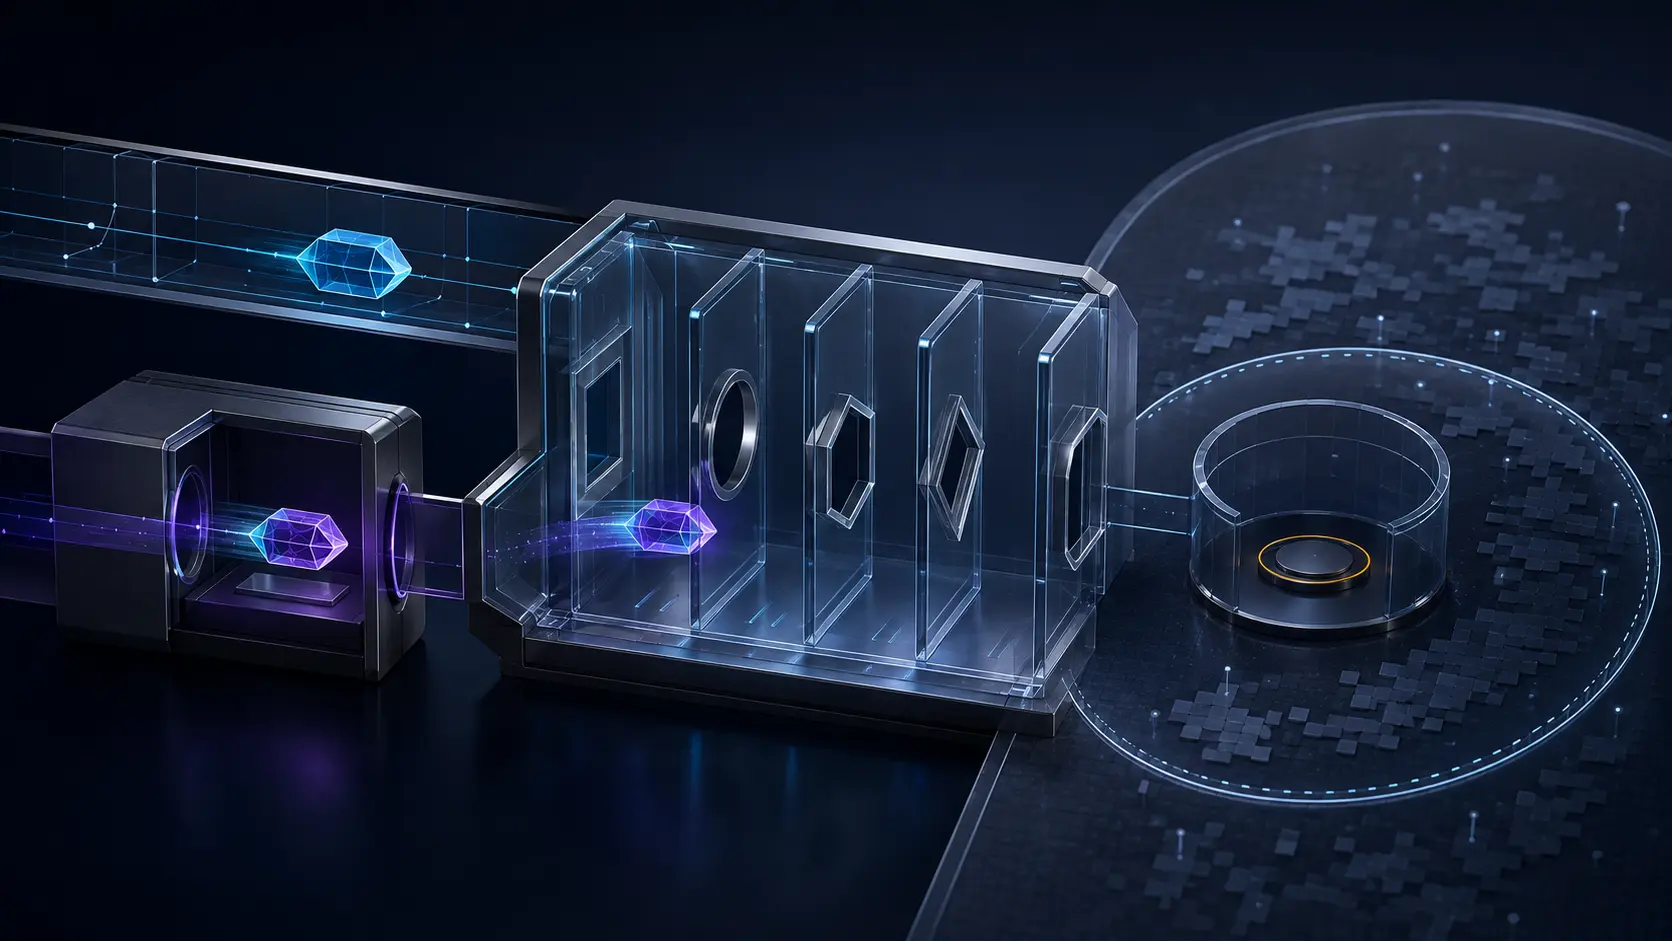
The architecture assigns each participating destination provider one or more CPS instances. A caller's out-of-band authentication service can deposit the PASSporT there as the call is placed. The terminating provider's verification service can pull it after the call arrives or receive it through a subscription. The CPS can be run by the destination provider, by a contractor on its behalf, or as a shared and geographically distributed service.
That flexibility creates interoperability. It also creates a join. The call and the assertion no longer occupy one message whose transport order supplies an obvious association. They become separate events with separate paths, delivery failures, access decisions and timestamps.
An advertisement points to custody
An originating service first needs to know where to submit a token. RFC 9888 defines a CPS advertisement: a JSON mapping from telephone-network authority entries to HTTPS CPS locations. The advertisement can be signed with a STIR credential. Its TNAuthList can then be compared with the scope being advertised.
The result is a bounded proof. A credential holder can show authority to advertise a CPS for stated telephone-number resources. That does not show that the CPS received a particular token, that a particular subscriber is currently called, or that the advertised service may disclose every token it stores. Discovery may be bilateral, consortium-based, database-driven, assisted by DNS or bound into a certificate. Whichever method is chosen, an advertisement is a routing statement about evidence custody, not the evidence verdict itself.
The distinction is especially important in shared services. If several providers use one CPS, the service must determine which terminating verification service is entitled to receive which PASSporTs. RFC 9888 notes that it may inspect the dest element and compare the requested scope with the relying provider's authority. A STIR credential is not a universal library card for calls in progress.
A secure submission closes one path
The originating out-of-band authentication service forms a protected connection to the CPS. RFC 9888 recommends mutual TLS with its STIR credential. That allows the CPS to recognize a submitting provider, protect the transfer and reduce replay and flooding risks. The CPS still decides, under local policy, which originators it accepts and at what volume.
Those facts should remain separate in the record. HTTPS protects a connection. Mutual authentication identifies the connection's peers under a trust configuration. A valid PASSporT signature binds the assertion's claims to its signer. The CPS acceptance decision admits the object. None of these events demonstrates that an unsigned call now arriving on another path is the event described by that object.
Storage is deliberately short. A submitted PASSporT remains only long enough for retrieval and never beyond its own freshness interval, which RFC 9888 caps at sixty seconds. That limit reduces an old token's usefulness, but it does not perform correlation. Two different calls can occur inside one minute. Clocks can disagree. A retry can reorder delivery. A gateway can deposit material while call routing later fails.
Fresh means eligible for the next test, not matched.
Pull and push move the timing problem
In pull mode, the terminating side receives a call lacking an in-band PASSporT and asks the CPS for applicable tokens. In push mode, it subscribes to a range and may receive tokens before or after signaling. Both modes can work. Neither supplies a universal rule for when a reader-visible badge should appear.
RFC 9888 says the terminating side may need to delay the verification indicator while it waits for the token. It leaves the exact timing and interaction with substitution attacks for future work. That is not an omission an interface may silently fill with optimism. It is a local decision boundary that needs explicit evidence and failure behavior.
A robust join needs more than approximate simultaneity. It should retain the called and calling identifiers as represented on each path; the signer and certificate scope; issue and arrival times; the CPS instance and retrieval principal; the token identifier or safe fingerprint; the actual call leg; gateway transformations; signature and freshness results; duplicate candidates; and the rule that chose one token over another. If several tokens remain plausible, the state is ambiguous rather than verified.
The negative cases deserve equal precision. A call with no token may mean that no assertion was created, submission failed, the wrong CPS was discovered, access was denied, the object expired, delivery was late or the call is outside the deployment. A token with no call may precede a legitimate arrival, outlive a failed route, result from duplication or be unmatched. Neither absence has one universal meaning.
The privacy model changes with the operator
RFC 9888 intentionally differs from the open out-of-band architecture in RFC 8816. It assumes the CPS is operated by the terminating provider, or for that provider, and therefore sees call metadata the provider would receive through call setup anyway. This permits a simpler architecture than one designed to hide caller and callee identities from an unrelated public service.
“Would know anyway” is an institutional statement, not a property of the bytes. If the provider outsources the CPS, another organization can observe the metadata. Shared CPS operation may concentrate visibility across providers. PASSporT extensions may expose information beyond ordinary SIP signaling. Contracts, retention limits, access logs and purpose restrictions therefore remain part of the technical design's real control surface.
The out-of-band path is valuable precisely because it does not require every telephone hop to adopt the same transport. Its success depends on preserving the boundaries the alternate route introduces. The token arrived. The call had not. Verification still had to wait for the system that could truthfully connect them.
Sources
- RFC 9888 — service-provider out-of-band STIR
- RFC 8816 — STIR out-of-band architecture
- RFC 8224 — authenticated identity in SIP
- RFC 8225 — PASSporT
- RFC 8226 — STIR certificates
- RFC 9325 — TLS guidance
- RFC 7258 — pervasive monitoring
- Heng Lu — running code is primary
- Heng Lu — minimum initial specification
- Heng Lu — reality layers and symbolic power
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance