
Policy continuity, legitimacy, and accountability signals across internet governance institutions.
Governance
Governance
Internet governance intelligence tracks institutions, policy processes, standards activity, registry operations, accountability disputes, and implementation signals that affect internet infrastructure. BTW.
RIR WatchdogCase FileNumber Resource SocietyICANNIETFHistory of InternetNOGs

RIR Watchdog, Case File, NRS, ICANN, IETF, History of Internet, and NOG sessions.
Coverage prioritizes implementation evidence and institutional behavior over declarative positions.
Latest Coverage
Latest from Governance
7,980 articles

Story
ARIN’s RDAP Remarks Qualify This Object, Not Every Registry Record
Human-readable text inside an RDAP response can look like a general registry instruction. Its location matters. In ARIN’s live entity response, Registration Comments sit inside a particular entity entity, while service terms and reporting notices occupy the response’s top level.

BDNOG
bdNOG Publishes Who Oversees Its Executive Committee, Not How
bdNOG’s public governance pages draw a clean line: the Board is the highest authority, while the Executive Committee (EC) manages the community’s work. The Board page says it approves yearly activities and holds the EC accountable. The EC page names the operating committee and…

IETF
A Resolver Can Choose Encryption Before DNS Operators Coordinate
Encryption between a user and a recursive DNS resolver does not protect the next hop. The resolver may still send the resulting query in cleartext to an authoritative server, exposing another part of the path to passive observation. RFC 9539 proposes an experimental compromise…

History
The Window That Closed Without Ending the Connection: TCP Persist
When a TCP receiver says it has no room left, the sender stops sending ordinary data. The harder question is how either side escapes that pause if the one message announcing new room never arrives.

IETF
One Header Can Invalidate a Whole Site Section: RFC 9875 and HTTP Cache Groups
A response can label related stored responses inside one cache and one URI origin, while a later unsafe request can name those labels for possible invalidation. The useful boundary is local coordination, not a promise of synchronization across caches, CDNs, or origins.
CASE FILE
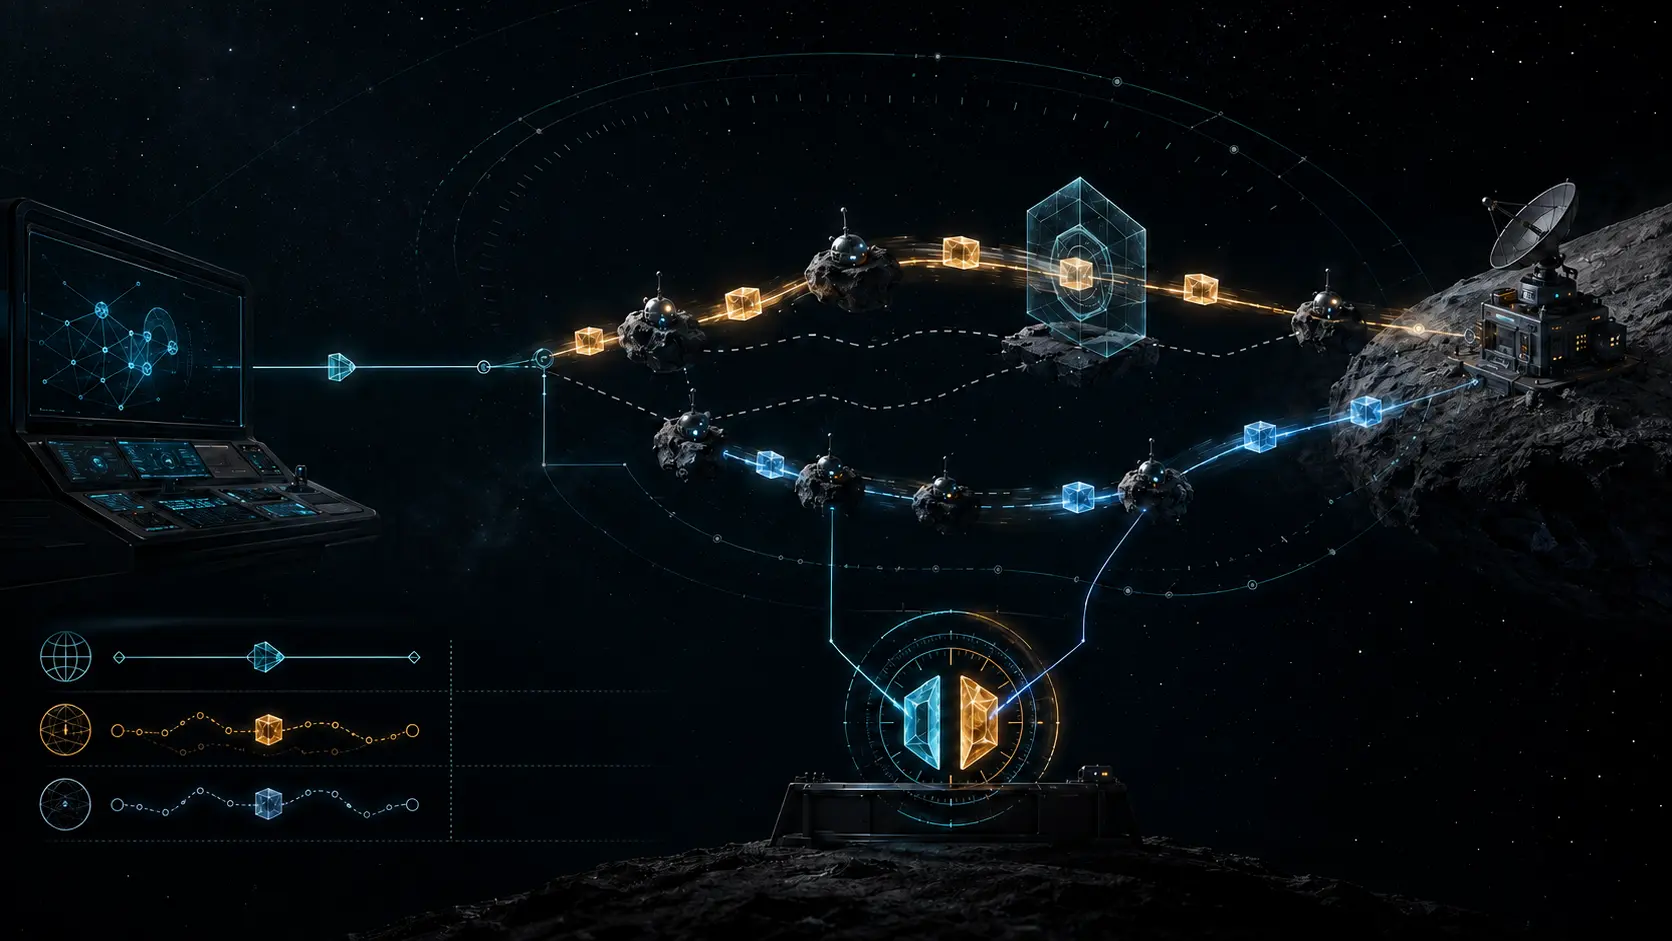
The Certificate Challenge Crossed the Delay. Authority Did Not: RFC 9891
RFC 9891 carries an ACME proof through a delay-tolerant network, but it carefully stops the proof at control of a Node ID during one policy-bound exchange. Everything beyond that boundary still needs its own evidence.

Story
LACNIC’s RDAP Self Link Locates the Record, Not the Network’s Serving Infrastructure
A URL inside a registry response can look like an infrastructure clue. In LACNIC’s RDAP output, however, `rel: self` tells a client where to retrieve the registration entity; it does not say where the registered network’s traffic, applications or authoritative services run.

Story
AFRINIC Named Five Fellowship Recipients from a Pool Above 1,700. The Selection Record Is Not Public
AFRINIC’s announcement identifies five people and describes a highly competitive programme. It does not publish the exact applicant total, the scoring method, the assessors or the decision record, so the notice proves an outcome without making the selection reproducible.

IETF
Catalog Zones Turn a DNS Member List into Fleet-Wide Provisioning Authority
An empty file is usually absence. An empty DNS catalog can be an instruction. If a generator accidentally publishes a catalog without its members, every consumer that originally provisioned those zones from that catalog may begin removing them and their associated state. RFC 9432…
History
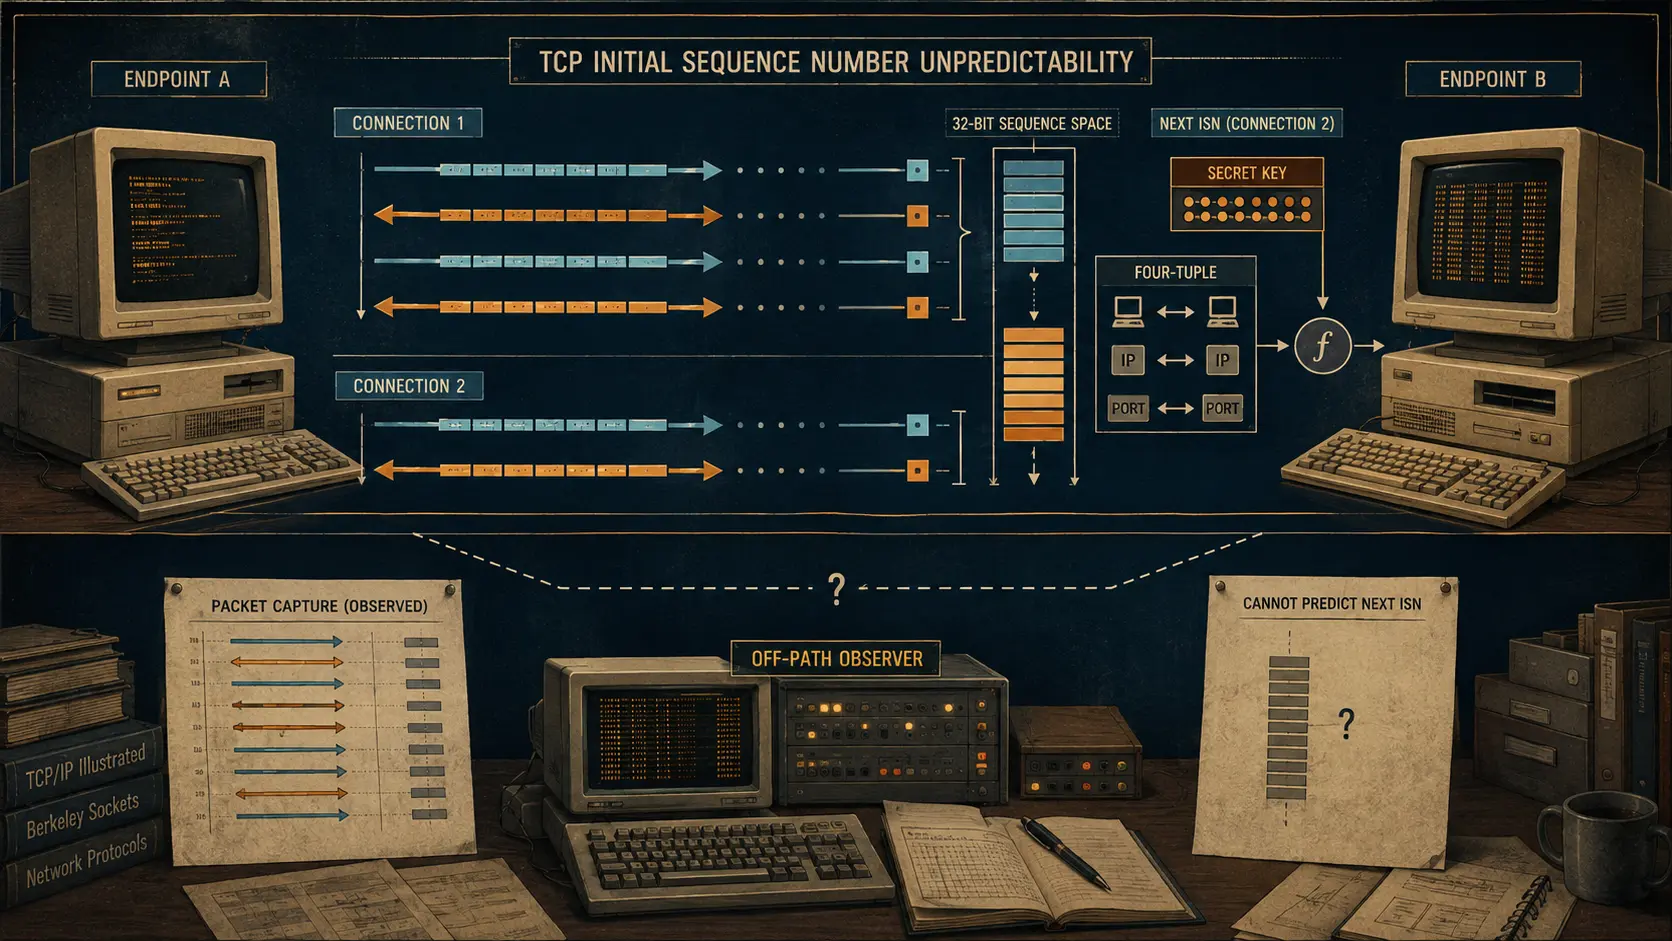
The Number Made Harder for an Off-Path Attacker to Predict: TCP Initial Sequence Numbers
A TCP connection begins by exchanging numbers. The security change was not to hide that exchange, but to stop one visible number from revealing the next connection's starting point.

ICANN
A Singular/Plural Risk Does Not Self-Execute: The 30-Day ICANN Notification Record
In the 2026 Round, a grammatical pair becomes a program decision only through a timely notification backed by verifiable dictionary evidence.
ICANN
An ICANN Objection Appeal Is Not a Retrial: What the Clearly Erroneous Standard Can Change
The 2026 Round appeal process reviews an identified objection error; it does not reopen the entire dispute from the beginning.

Story
AFRINIC’s RDAP ipVersion Describes This Record, Not IPv6 Readiness
An IPv4 lookup naturally returns an IPv4 entity. That simple fact becomes misleading when `ipVersion: v4` is promoted from a property of one AFRINIC record into a verdict on an organisation’s entire network.
ICANN
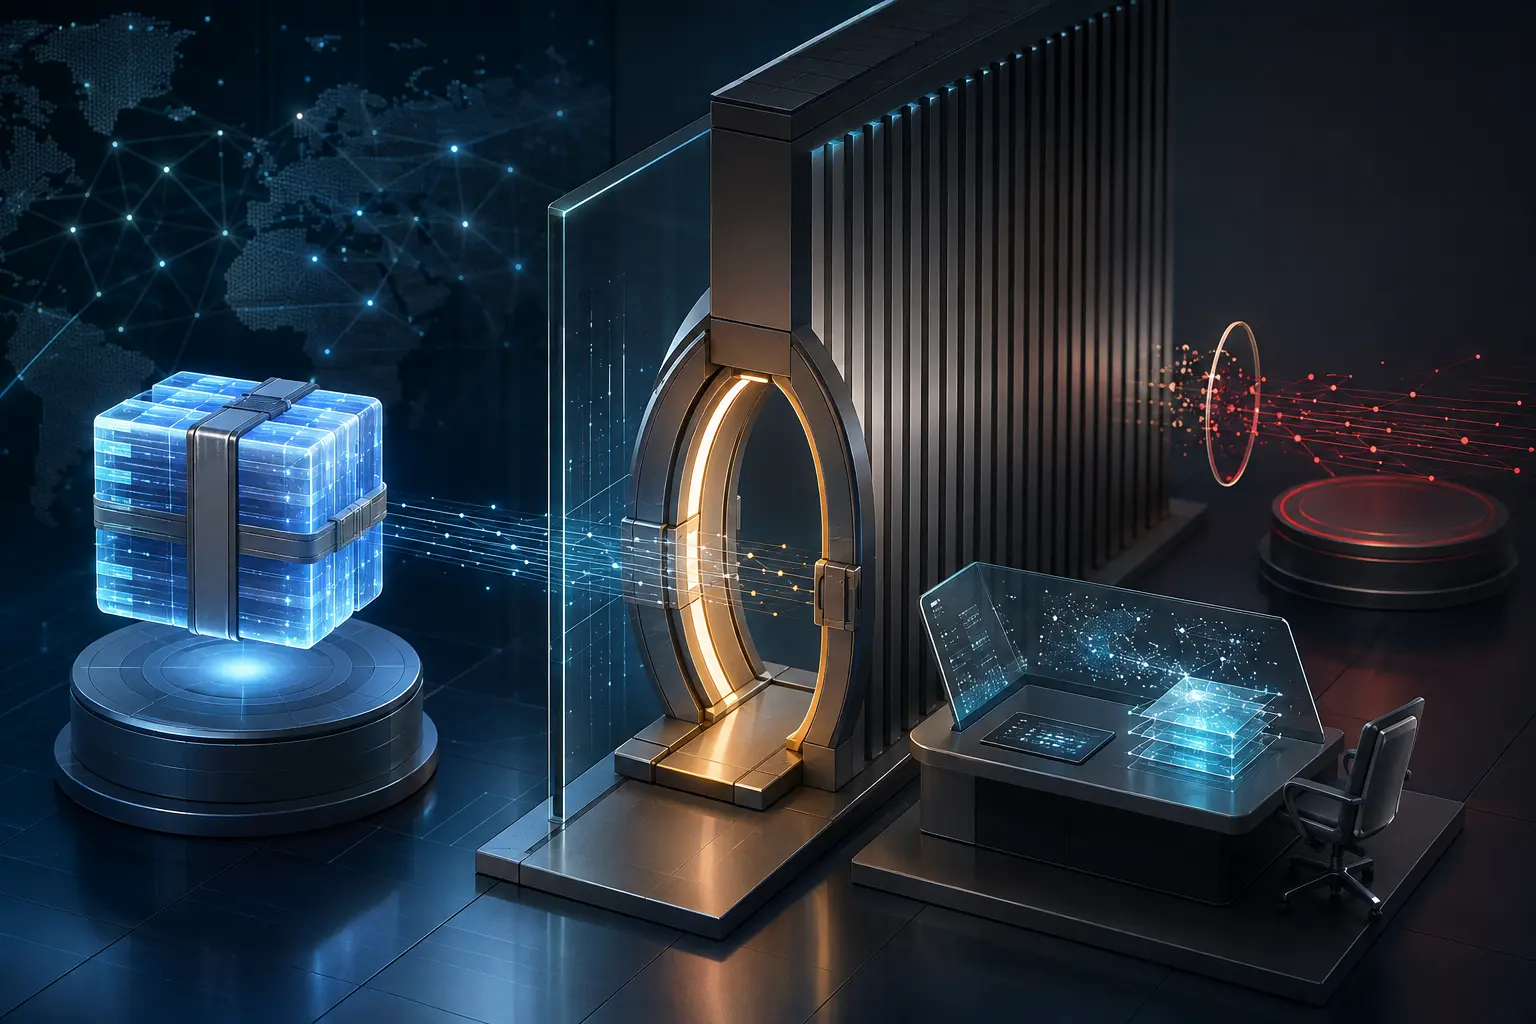
A Zone File Is Shared Access, Not Permission to Republish the Namespace
At 09:00, an approved researcher downloads a gTLD zone file through ICANN's Centralized Zone Data Service. The archive is complete enough for the contracted transfer, and its checksum matches. Those facts establish delivery. They do not establish who owns every listed domain, why…

ICANN
Community Objection Is Not CPE: Two ICANN Procedures That Test Different Claims
The word “community” appears in both names, but the procedures ask different questions, involve different parties and create different records.

Story
RIPE’s RDAP Type Classifies a Registration, Not the Route Origin
RIPE’s RDAP Type Classifies a Registration, Not the Route Origin intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The…

IETF
One Delete Command Can Break Someone Else's Domain: RFC 9874 and EPP Dependency Control
A destructive EPP transition is not necessarily local to the client that requests it. When a subordinate host is still associated with domains sponsored by other clients, deleting that host can alter their DNS dependencies, consistency, and ability to resolve. RFC 9874 is a…

Story
APNIC's IPv4 Needs Test Should Match the Delegation Under Review
APNIC prop-169 would replace a fixed `/23` reference in an IPv4 LIR usage-plan test with the delegation actually being assessed. It is a narrow wording repair, but it matters because evidence should measure the request an applicant is making, not a larger block the policy no…
Story
AFRINIC Received 1,024 ASNs. The Public Record Separates Inventory from Allocation
IANA recorded a new 1,024-number block for AFRINIC on 25 February 2026, and AFRINIC announced the addition to its inventory on 27 March. Those records establish upstream custody, not downstream allocation of every number to operators.

IETF
The Second Address Became the Primary One: What RFC 9873 Changes in EPP Contact Data
RFC 9873 turns a contact update into a more explicit state transition: an EPP contact may carry one additional email address, and an optional `primary` attribute says which address is to be treated as primary. The protocol records that relationship; it does not certify the…
Session Map
Governance Branch
RIR Watchdog
Five regional sessions tracking allocation policy, board legitimacy, and institutional continuity.
Open RIR WatchdogCase File
Long-cycle governance dossiers with legal, election, and institutional stress analysis.
Open Case FileNumber Resource Society
Membership, charter, and resource-governance intelligence from the NRS ecosystem.
Open NRS SessionICANN
DNS coordination, accountability frameworks, and global multi-stakeholder process dynamics.
Open ICANN SessionIETF
Protocol standardization trajectory and interoperability risk under fragmented policy conditions.
Open IETF SessionHistory of Internet
Long-cycle infrastructure history used for governance interpretation and structural forecasting.
Open History SessionNOGs
Operator-level implementation intelligence from APRICOT plus regional and national NOG ecosystems.
Open NOGs Session