
Topic
Network-resource Evidence
Within the Topic facet, Network-resource Evidence topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.

History
The URL Carried a Query, Not Its Authority: RFC 1959
In 1996, a directory lookup could be folded into a string short enough to paste into a document or hand to a web client. That convenience was exact but narrow. RFC 1959 could name a server, a place in the directory, the attributes to request, a search scope and a filter. It could…

IETF
Nathaniel Borenstein and the Base64 Encoding That Never Promised Confidentiality
A Base64 string can cross a transport that would damage the original bytes. It cannot tell an operator who made those bytes, who may read them, whether they changed, or whether opening them is safe.
CASE FILE
Two Sources, One Election, No Continuity Verdict: RFC 9856
RFC 9856 gives an EVPN fabric disciplined ways to choose among redundant multicast sources. The useful discipline begins by refusing a tempting shortcut: the chosen path is not the received service.

Story
RIPE NCC Finished the RIS Bare-Metal Move. That Does Not Close the Pipeline
RIPE NCC’s newest RIS plan uses “finished” and “in progress” in the same paragraph, without contradicting itself. The data moved; processing assurance, storage choices, Kafka renewal and a consumer’s latency response sit on different clocks. The useful public record is not one…

CASE FILE
Sirius Telecom’s missing operating chain
The public record places Sirius Telecom in the Directory as a global network operator and links the name to PeeringDB network 1283. It does not yet establish the chain that would turn that label into an independently verifiable operating business: a legal entity, a functioning…

Global Institutional Trends
Utherverse Network Operations: What AS33169 Can—and Cannot—Show About Continuity
A forensic examination of the public record around Utherverse Network Operations finds a network identity, but not yet an auditable picture of who controls prevention, detection, response or durable repair.

Story
A Scan Found 4,611 Exposed BGP Routers in APNIC. It Cannot Say Why They Were Open
At APNIC 62, researchers put a regional number on a quiet control-plane problem: 4,611 routers across 1,343 APNIC-region autonomous systems answered an unsolicited BGP OPEN exchange in a February IPv4 scan. That is firmer evidence than a port banner, but it is neither a breach…
Number Resource Society
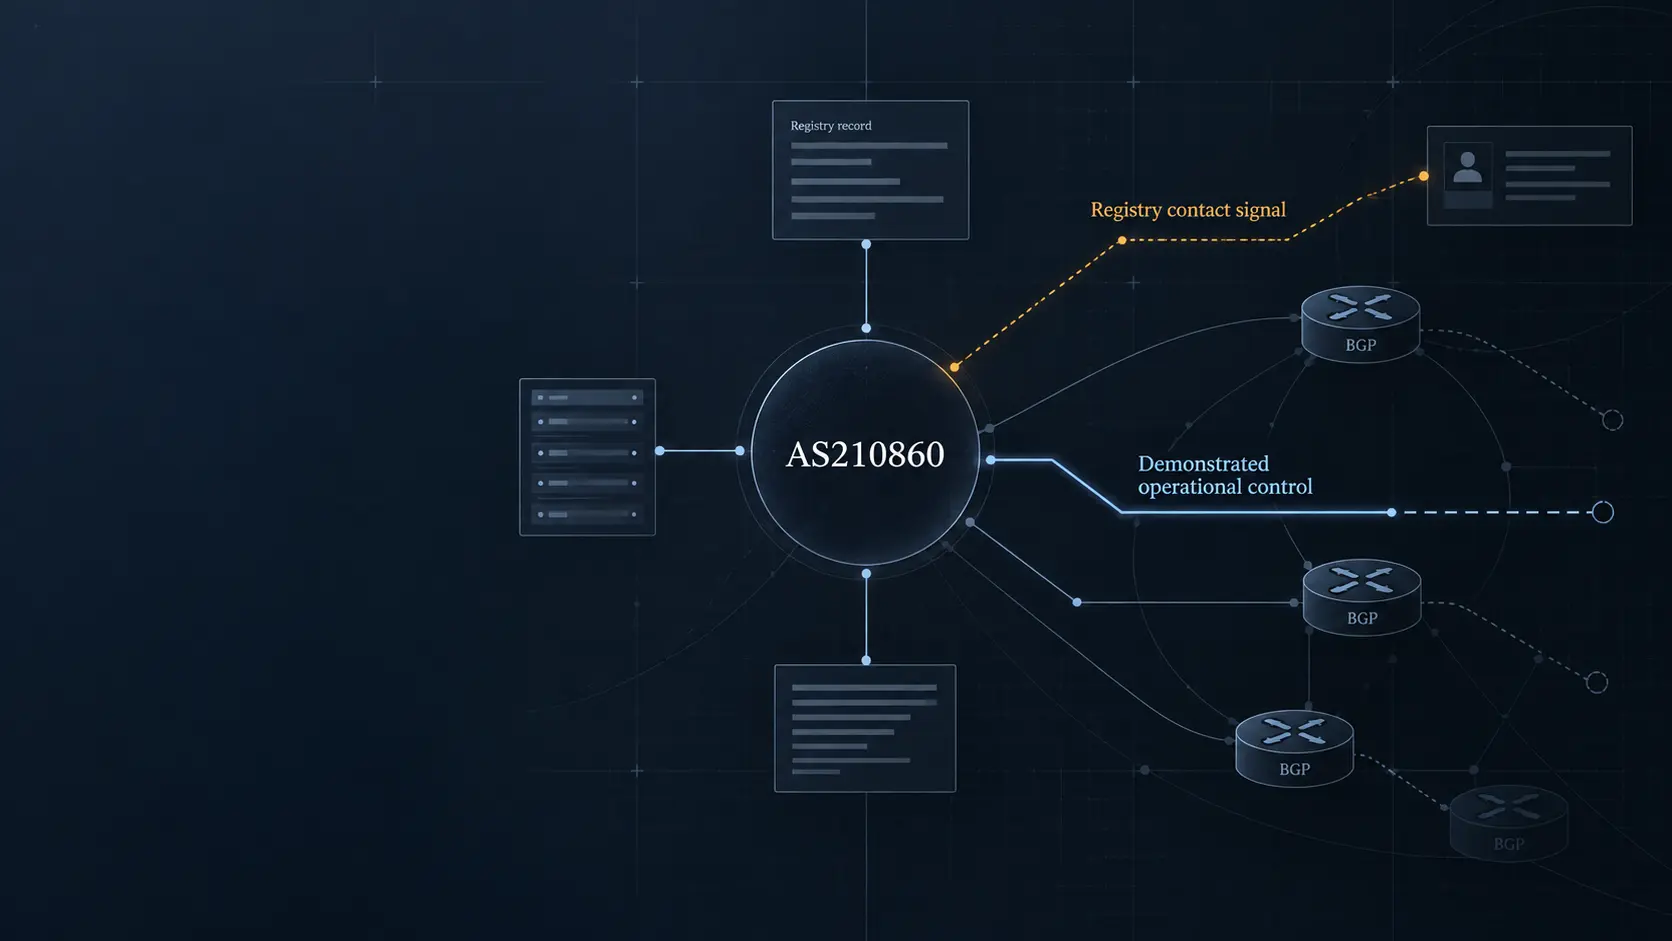
DFINFRA and AS210860: the registry signal still stops short of operational control
DFINFRA and AS210860: the registry signal still stops short of operational control intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that…

IETF
A D-PATH Stops Loops Only When Gateways Agree on the Domain
A BGP attribute can carry a domain history, but it cannot decide what a domain is. RFC 10039 makes that prior decision operationally consequential: the same configured identifier that lets a gateway reject a returning route can also discard a legitimate route when the gateways…

Leaders
Osipenko Alexander Nikolaevich: The Control Question the Public Record Still Cannot Answer
Osipenko Alexander Nikolaevich: The Control Question the Public Record Still Cannot Answer intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure…

Global Institutional Trends
AS210057: What the Public Record Can—and Cannot—Prove About Routing Control
A forensic briefing on the difference between registry records, routing authorization, observed BGP visibility and durable operational control around the frozen INFINITYWIFI directory entity.
IETF
The Route Carried a Domain Path. The Tenant Still Needed Proof: RFC 10039
RFC 10039 arrives with a practical answer to a dangerous ambiguity: when tenant reachability is re-originated between EVPN and IPVPN domains, redundant gateways need a way to recognize that a route has come back. Its new D-PATH attribute records the declared domain sequence and…

IETF
Cyrus Daboo and the PARTSTAT=ACCEPTED Status That Did Not Prove Attendance
An accepted invitation is useful evidence of a calendar decision. The standards Cyrus Daboo helped shape also show why it is not evidence that the invited person later appeared, stayed, listened, contributed, or completed anything.

CASE FILE
The Repair Path Was Ready. The Multicast Service Was Not Yet Proven: RFC 9860
RFC 9860 gives multicast operators a more capable way to build a standby tree from a TI-LFA repair list. It also draws a useful boundary: a route calculation can accelerate local recovery, but the service verdict still belongs to evidence collected after the calculation.

IETF
RFC 7506 Is Historic. Router Alert 69 Can Still Be on the Wire
A standards register can retire a behavior without touching a single router. RFC 7506 is now Historic, its MPLS OAM Router Alert value is deprecated, and RFC 9570 says new LSP Ping implementations must not set it. None of those facts proves that value 69 has disappeared from an…

History
The Proposal Added a Header. It Refused to Rewrite the Address: RFC 1955
RFC 1955 described a way to make the Internet's routing problem look smaller without pretending that its addressing problem had disappeared. At an entrance border, the proposal would place the original IPv4 datagram inside a second IP header addressed to an autonomous domain. At…
History
The Cell Carried a Label. It Did Not Carry a Verdict: RFC 1954
In Ipsilon's 1996 ATM design, a flow label did not decorate an IPv4 packet. It changed the virtual channel and, for two flow types, changed which IPv4 fields crossed the link at all. That economy made forwarding state executable—and made the limits of the resulting evidence…
IETF
Mark Crispin and the \Seen Flag That Did Not Prove a Human Read the Message
An email turns from bold to ordinary type, and a shared mailbox quietly acquires a fact: `\Seen`. The interface calls the message read. The server can prove that a flag changed. Between those statements sits the question Mark Crispin’s IMAP makes unavoidable: what, exactly…
IETF
A NAT64 Mapping Is Not a Filtering Policy
A repeatable public tuple can prove how a stateful NAT64 translator allocates an address and port. It cannot prove which IPv4 sources are allowed to use that state on the way back. Treating those two facts as one control turns an interoperability test into a security verdict it…
IETF
The disclosure rule that does not travel alone
An incident report can inherit its sharing conditions from the structure around it. Turning that report into a convenient extract is therefore a policy decision, even when none of its factual fields changes.