
Topic
Network-resource Evidence
Within the Topic facet, Network-resource Evidence topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.

IETF
Keith Moore and the Encoded Word That Changed the Display, Not the Sender
Two ASCII header lines can open into the same accented name on screen. That visual agreement is useful, but it is the end of a decoding process—not a receipt for who sent the message.
CASE FILE
The Cookie Returned. The Service Had Not: RFC 9853
RFC 9853 lets a DTLS endpoint test a peer address after a Connection ID recovers an existing security context from a datagram whose source has changed. The returned cookie can justify one binding decision at one moment. It cannot explain the change, promise a stable path, or…
History
The Ticket Arrived. The Receipt Did Not: RFC 1964’s Authentication Boundaries
RFC 1964 gave Kerberos V5 a disciplined GSS-API wire vocabulary: a mechanism identifier, typed tokens, a digest for caller-supplied channel bindings, service flags and an optional delegated credential. The design is valuable precisely because each item stops at a boundary. A…

History
The Header Came Last: How RFC 1963 Reassembled Serial Frames over PPP
RFC 1963 made an unusual bargain with time: send the serial data first, postpone the adaptation header until the packet's end, and let the transmitter decide on segmentation only after compression had revealed the size. What reached the receiver was a grammar for reconstruction…

IETF
The verifier subscribed. The evidence chain still had seven tests
An IETF draft turns device attestation from a polling exercise into a stream. That is a useful change in tempo, but a signed notification is still only one link between a measurement and a decision.
Story
RIPE NCC Says Its 2027 Invoicing Changes Are Complete. The Bill Still Waits for 31 December
RIPE NCC has finished the applications work for its 2027 charging scheme before the data that will determine the first bills exists. That is sensible project management. It is also why “complete” needs a second, more operational meaning in January: can each charge be reproduced…

Story
ARIN’s RPKI Constraint Is Only as Current as the Package That Ships It
A trust boundary can be carefully designed, correctly signed and still arrive too late. ARIN’s planned RPKI constraint work makes that mundane distribution problem part of routing-security policy.

CASE FILE
AlmazCloud’s ASN Is Registered. What Can Be Shown as Operating?
AlmazCloud’s ASN Is Registered. What Can Be Shown as Operating? intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The…

Number Resource Society
AS210837’s Continuity Question Is an Evidence-Chain Problem
AS210837’s Continuity Question Is an Evidence-Chain Problem intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The Number…

CASE FILE
The Paths Were Paired. The Round Trip Was Not Proven: RFC 9854
RFC 9854 gives a low-power network two related route discoveries when one radio direction cannot stand in for the other. That pairing prevents control state from being confused; it does not turn two temporary graphs into evidence that a request went out, a response came back, and…

Number Resource Society
AS210057’s visible network footprint still stops short of proving who operates it
AS210057’s visible network footprint still stops short of proving who operates it intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that…

IETF
Roberto Peon and the HPACK Table That Remembered Fields but Never Cached a Response
A small integer can recover a long HTTP field inside one connection. It cannot say whether a response is fresh, reusable, authentic or even stored anywhere.

History
One Direction Lost the Dictionary. The Other Kept Moving: RFC 1962
A PPP link in 1996 could agree to compress traffic without pretending that its two directions were identical. RFC 1962 let each receiver say what it could decompress, let the reverse path make a different choice, and gave a damaged direction a reset exchange of its own. That…

Story
ARIN’s Open 1,024-Character Ticket Is Really About a Private Routing Grammar
An open ARIN suggestion asks for more room in an IRR remarks field. Its motivating case is not really about storage. Lumen documents a parser that can turn a marked remark into the effective membership of an AS-SET, overriding the field that ordinary RPSL readers expect to carry…
Story
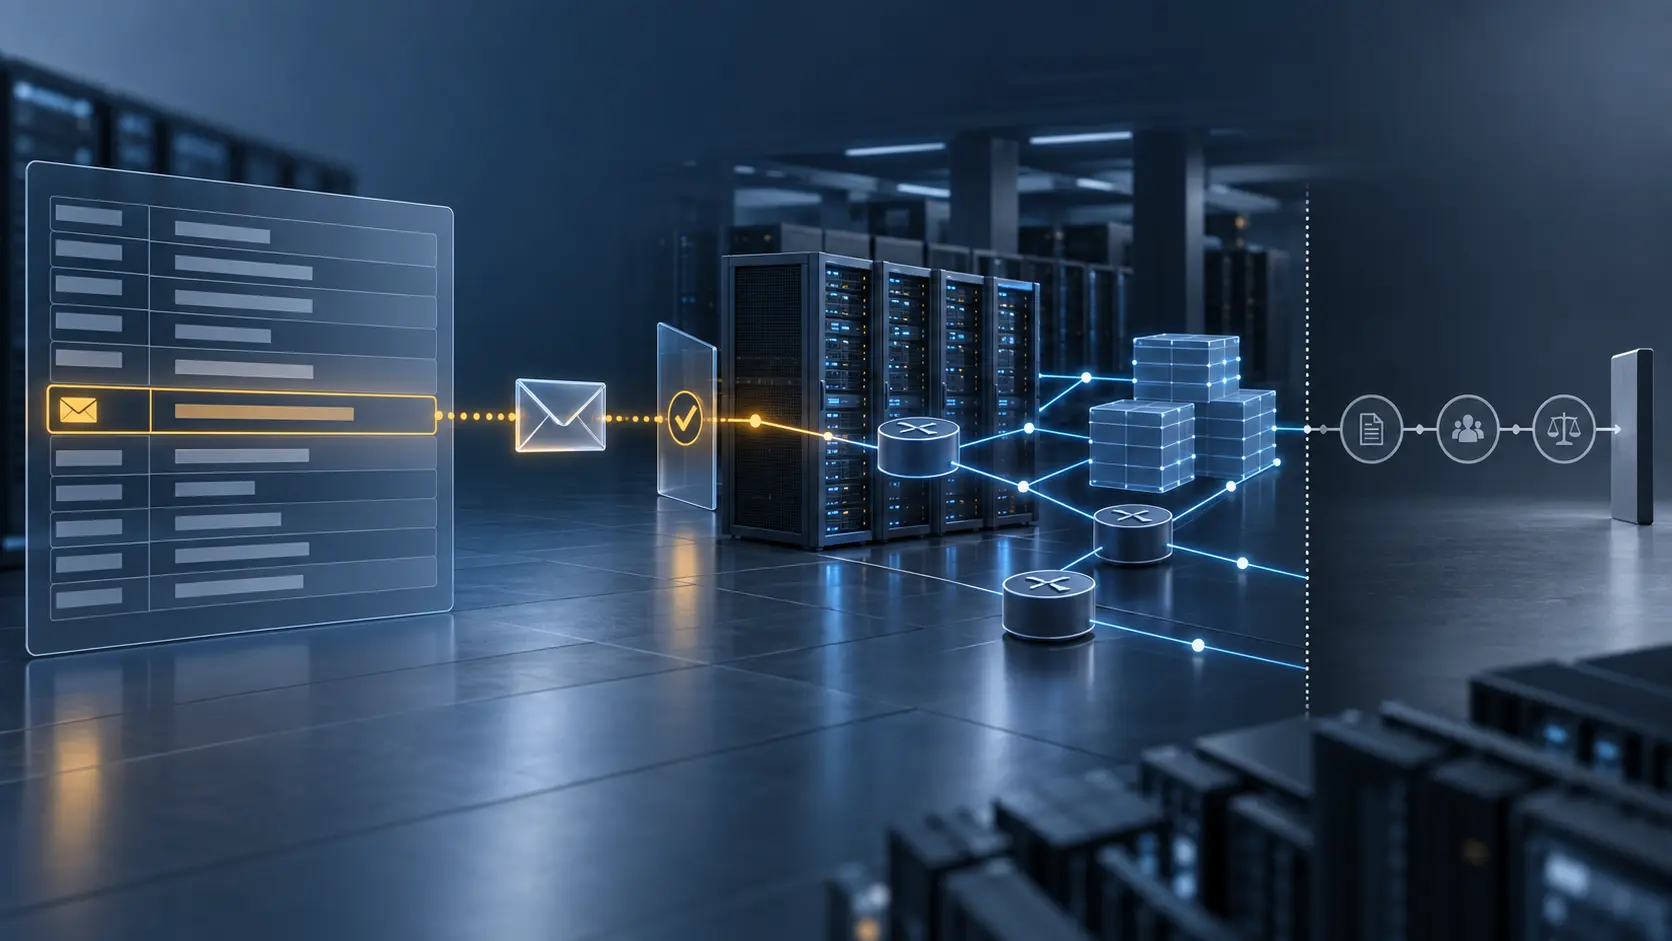
RIPE ABUSE: Who Controls the Next Step After a Report?
RIPE ABUSE is often described as a contact point. That is accurate, but incomplete. The published abuse-c field creates a route into a responsibility chain: a report can be addressed to a resource holder or designated organisation, the mailbox can be tested by RIPE NCC, and a…
Story
APNIC and NIXI Cannot Close India’s ROV Plan With One Percentage
On 8 September, APNIC Labs could describe India’s observed ROV filtering as 1.14% or 6.03%. Both figures came from the same dated record. The difference was the window—and it is exactly why a national routing-security promise needs a receipt, not a headline number.

CASE FILE
The Controller Received the State. It Still Needed a Clock: RFC 9857
RFC 9857 gives external controllers a structured view of Segment Routing candidate-path state. The harder operational question begins after receipt: whose observation was it, which generation did it describe, and what later evidence shows that the reported state still governed…
IETF
Jon Callas and the OpenPGP Key ID That Never Identified One Unique Key
An eight-byte label can help a verifier find a key. It cannot make the candidate unique, bind the key to a person, or authorize the action that follows.

Europe and Middle East Regional ISP Trends
ROYA Communications and AS210837: How to Test Network Continuity Without Mistaking Visibility for Proof
ROYA Communications and AS210837: How to Test Network Continuity Without Mistaking Visibility for Proof intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the…

IETF
Fresh Entropy Entered the Session. Recovery Still Needed Proof in Both Directions
TLS 1.3's ordinary KeyUpdate advances a secret already known to the current chain. The active Internet-Draft for Extended Key Update proposes something stronger: rerun the negotiated key exchange inside a live session and mix fresh input into the next traffic secrets. That can…