
Topic
Institutional Legitimacy
Within the Topic facet, Institutional Legitimacy topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.

AFNOG
AIS 2026 Promises Selected Recordings Without Naming the Selector
AIS 2026 is presented as a hybrid summit whose virtual entities will receive live-streamed sessions, interactive discussions and access to selected recordings. The word “selected” creates a governance question: who decides which sessions become part of the accessible record…

AFNOG
AfNOG Publishes Fellowship Criteria, Not the Procedure That Applies Them
AfNOG’s published Abha Ahuja Bursary application page tells candidates what the fellowship is looking for. It identifies a selecting committee, lists eligibility criteria and says incomplete applications will not be considered. The reviewed page does not set out how those…
CASE FILE
The Trace Linked the Action. It Did Not Prove the Authority
A new IETF discussion list asks how an agent’s intent, delegation, changing permissions and external actions can be followed across services. The hard part is not inventing a universal trace identifier. It is preventing that identifier—and the agent’s own account of events—from…
IETF
The IETF Approved Dynamic Flooding as an Experiment. “Acceptable” Still Needs a Measure
The IETF has authorized a test, not crowned a winner. Dynamic flooding may give dense link-state networks a much smaller graph over which to distribute updates, but the approved draft leaves operators with the hardest word in the evaluation: what counts as acceptable when the…
CASE FILE
The Token Authorized the Tool. It Did Not Authorize These Arguments
OAuth can establish that an agent may call a payment, messaging or infrastructure tool. The dangerous decision comes one layer later: whether the exact destination, amount, command and live form state produced by the model are the act a principal or governed policy approved. An…

History
The RFC Published a Straw Poll. It Did Not Create a Constituency: RFC 1501
Two electronic addresses at the end of a two-page RFC offered individual OS/2 users a way to be counted. They were doors into a proposed organisation, not proof that the people behind those doors had already become members, chosen representatives or moved IBM.

IETF
The IETF Approved an IoT TLS Profile. It Still Does Not Authorize the Device
A constrained device can complete the right handshake, present an accepted credential and still have no right to perform the next action. The newly approved IETF profile makes that separation unusually explicit. It standardizes a secure transport baseline; it does not inherit the…
CASE FILE
The Older Service Record Won. The Service Had Already Moved
A name collision is supposed to stop a newcomer from impersonating an established local service. Put two registration proxies between the service and that local link, however, and the same safeguard can protect yesterday’s address from today’s legitimate update. DNSSD’s proposed…

IETF
MOPS’ Draft Drops the Experimental Clause Without Recording the Verdict
The IETF is reviewing a light recharter for its Media OPerationS Working Group. The draft preserves the venue and its work, but removes the sentence that made the group an experiment. The old review is marked complete; the public change does not say what was learned.

ICANN
ICANN’s New “Time to Mitigation” Metric Does Not Time a Mitigation Act
Domain Metrica now estimates how long a reported domain keeps resolving. Its label sounds like an intervention stopwatch, but its start and finish are DNS observations—not the report and not the responsible actor’s action.

History
The Table Moved the Service. It Did Not Rename It: RFC 1498
A 1993 RFC recovered an older lesson: a table can change where a service runs while its name survives. Reaching it still requires separate evidence for the node, attachment point and path—and none of those bindings alone proves identity, authority or delivery.

History
The Code Was Available. The Original Specification Was Not: RFC 1492
The original TACACS specification existed, and the author of RFC 1492 could not obtain it because of copyright issues. What reached the public record in July 1993 was therefore an Informational reconstruction, constrained by running code and candid about the possibility that the…
History
The Damaged Text Became Readable Latin. It Did Not Become the Russian Original: RFC 1489
When the eighth bit disappeared from a KOI8-R message, Russian letters could fall into a strange, case-reversed Latin shadow. A reader might still guess the words. That humane failure mode did not restore the erased bits, certify the charset or turn recognition into proof of the…
History
The MX Record Found a Gateway. It Did Not Prove the Fax Machine Existed: RFC 1486
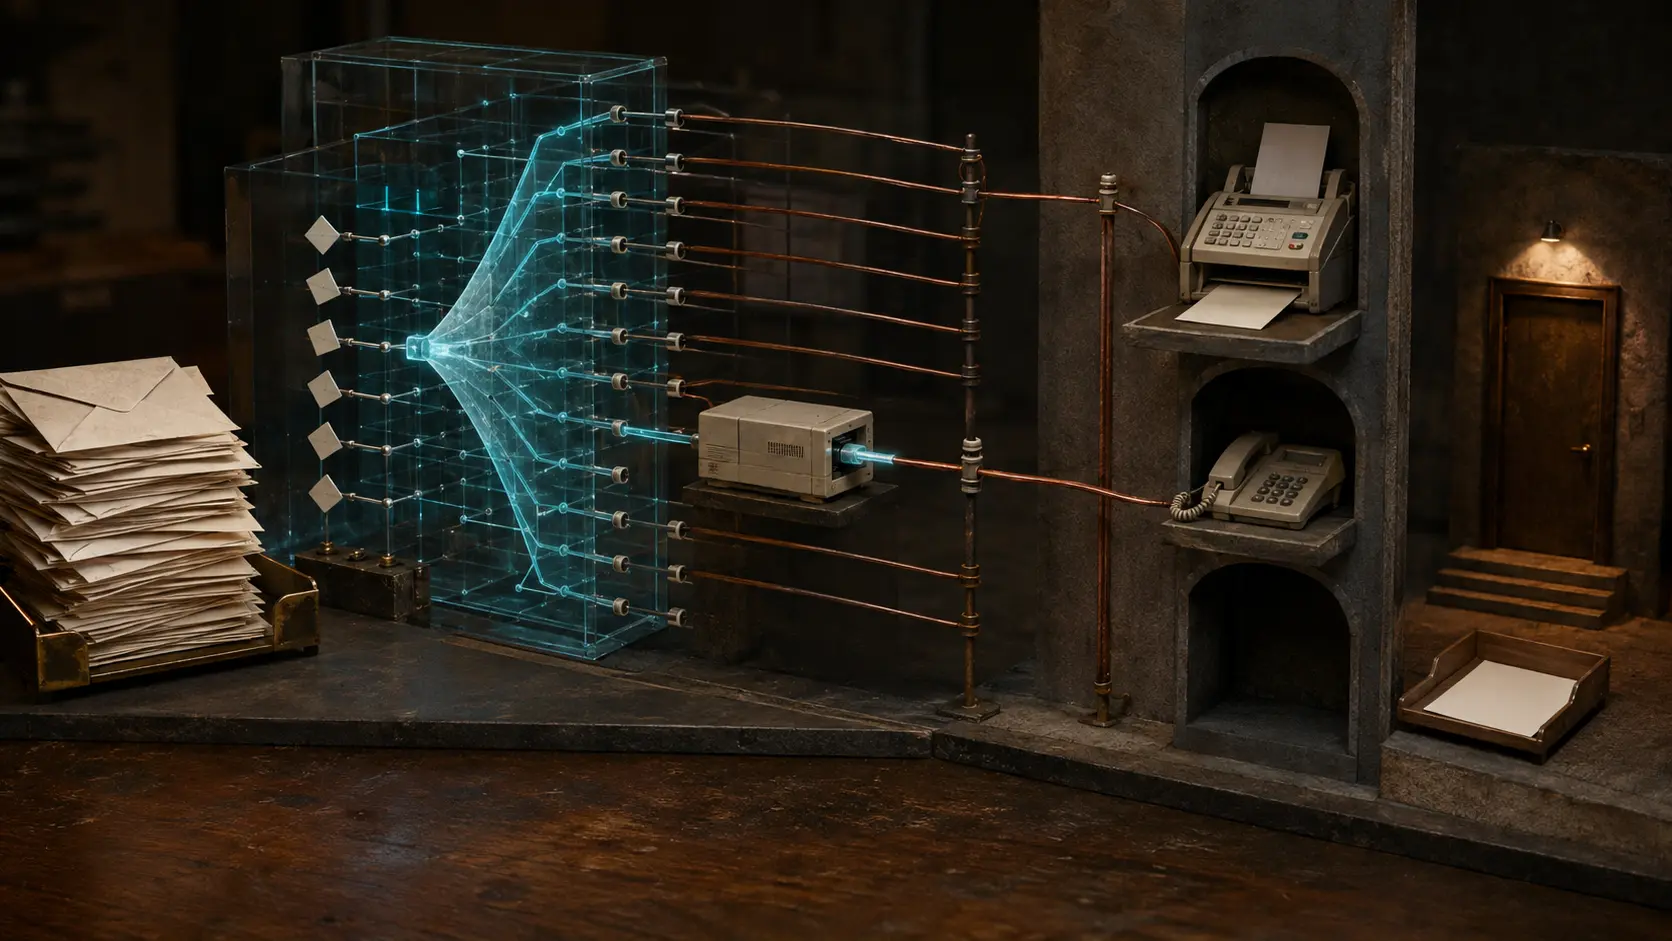
A wildcard in the Domain Name System could announce that a mail gateway was willing to serve thousands of telephone numbers. It could not say whether any one of those numbers existed, answered, belonged to a fax machine or put a page into the intended person's hands. RFC 1486…

History
The String Carried the Distinguished Name. It Did Not Become the Directory Entry: RFC 1485
The String Carried the Distinguished Name. It Did Not Become the Directory Entry: RFC 1485 intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure…

History
The String Could Be Parsed Without Ambiguity. It Still Was Not the Directory Entry: RFC 1485
The String Could Be Parsed Without Ambiguity. It Still Was Not the Directory Entry: RFC 1485 intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure…
History
The Name Was Easy to Type. Its Identity Still Depended on the Directory Around It: RFC 1484
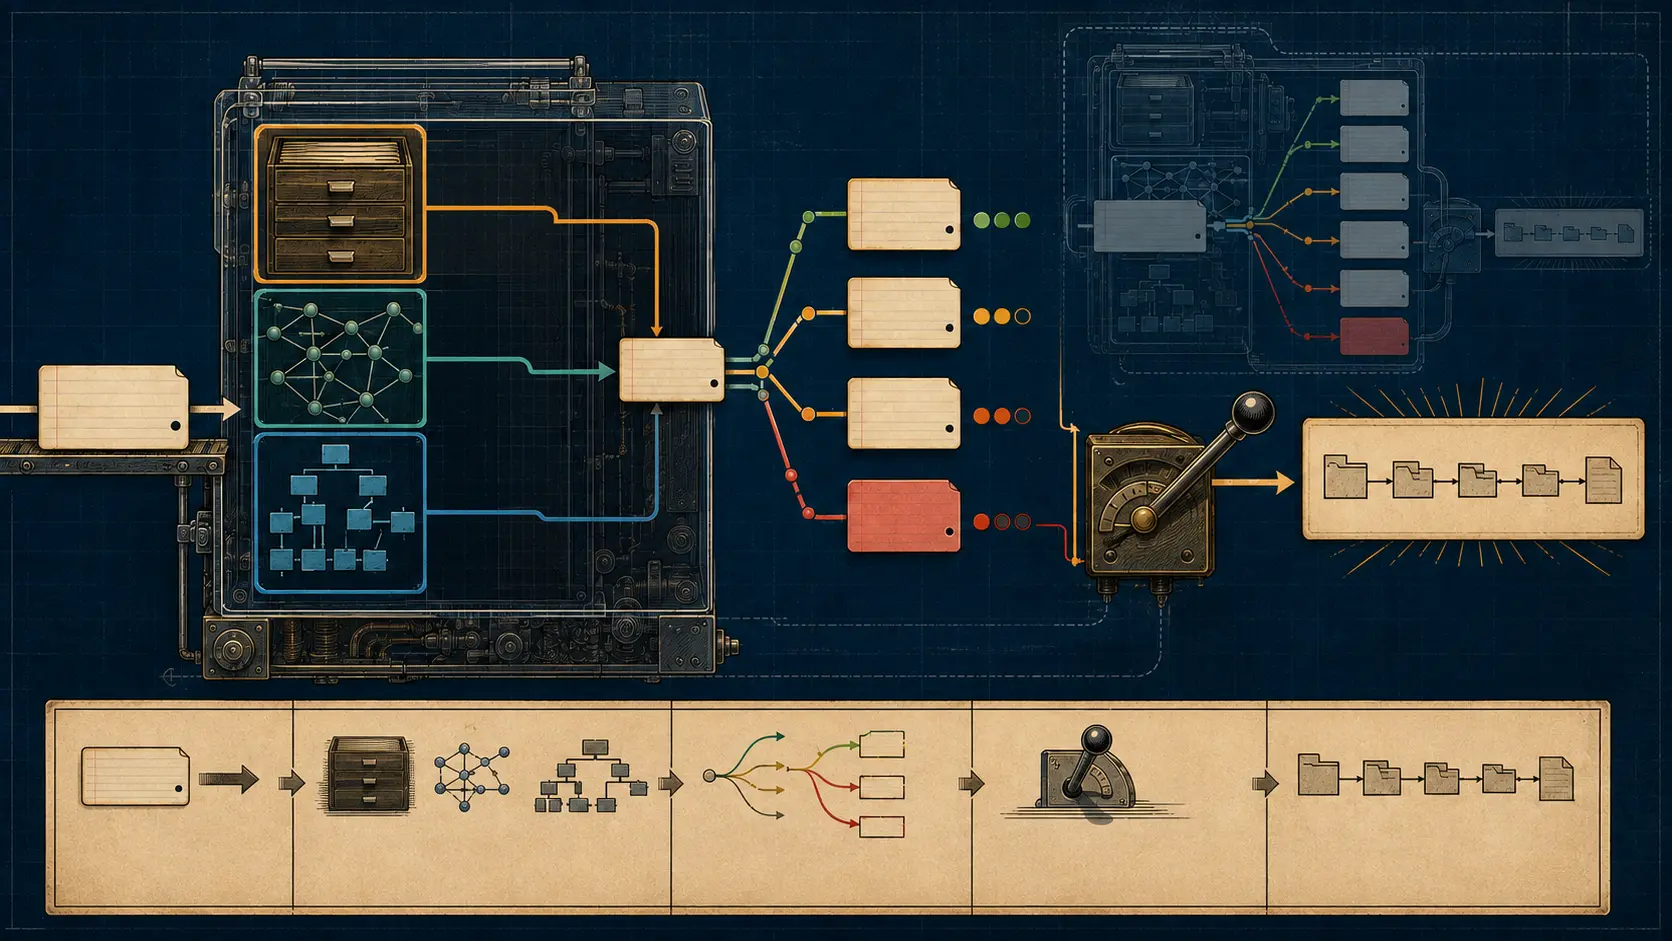
A person could say a short, natural name and let the directory fill in types, hierarchy and spelling. The convenience was real because the omitted context still existed: inside the local environment, current entries, matching rules and the user’s final choice.
CASE FILE
The Space Was Reserved. One Executive Approval Was Still Too Weak: RFC 9812
Nearly seven-eighths of IPv6 address space was being held for a future that had not arrived. The registry called it reserved, but the rule for releasing a major piece could still be satisfied by an executive approval with no RFC. RFC 9812 repaired that mismatch without pretending…

History
The IAB Endorsed CIDR. Four Different Actors Still Had to Make It Real: RFC 1481
In July 1993, the Internet Architecture Board used a sentence that sounds like a finish line: it “endorses the CIDR architecture and its implementation.” The sentence mattered. It still did not allocate an address block, add classless code to a router, install that code in a…
History
The Name Existed in .US. That Did Not Mean the Zone Had Been Delegated: RFC 1480
Two names could appear equally real beneath `.US` in 1993. One might be a direct MX entry for a UUCP host; another might sit inside a branch whose manager ran its own name servers. The resolver made both names visible. RFC 1480 did not give them the same authority, network…