
Topic
Digital Identity and Credentials
Within the Topic facet, Digital Identity and Credentials topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.

IETF
The Handshake Got Smaller. The Missing Certificates Became Onboarding State
An IETF draft proposes taking bulky intermediate certificates out of post-quantum TLS-based EAP handshakes. The bytes do not disappear. They move to an earlier EST retrieval, a local cache and an administrator's decision that both sides are ready to proceed without them.

IETF
An Agent Signature Is Not an Archive of Its Authority
A new individual Internet-Draft asks what an auditor could still prove years after an agent's signing key has vanished. The answer depends on evidence that a valid signature need not carry: the origin of the key and a trustworthy account of time.

IETF
The Priority Attribute Arrived. The Airtime Was Still Contended
An adopted IETF working-group draft gives RADIUS a vocabulary for emergency-priority authorization on Wi-Fi. It does not make the authorization server, the access point, the radio channel and the application one machine—or one receipt.

CASE FILE
The Signature Passed. The Workload Was Still Not Authorized
A cryptographic check can say who formed a workload request and which parts survived transit. It cannot decide whether that workload may perform the operation. Revision 07 of the WIMSE HTTP-signature draft makes this boundary unusually visible—especially when a replay reaches a…
IETF
The Abort Arrived After the Asset Was Burned
SATP Core revision 17 gives cross-network asset transfer a precise point of no return. Before the sender extinguishes the origin asset, abort can still restore local state. After `Commit-Final`, the same command is only a message about an outcome it can no longer undo.

IETF
The ACME Key Rotated. Yesterday's DNS Authorization Still Works
The newest ACME DNS persistence draft turns routine key rotation into an accounting problem. A retired signing key may be unable to place another order while its public thumbprint still keeps an earlier DNS authorization usable.

IETF
Who Owns the Label After the Proof Verifies?
A Key Transparency proof can establish that a directory answered consistently and still leave an operator with the wrong question. The IETF’s latest review asks who is acting, who owns the binding and who must keep watching after access has changed.
CASE FILE
The Signature Verified. The Resource Server Still Had a Decision to Make: RFC 9701
A signed token-introspection response can prove which authorization server issued a particular answer for a particular resource server. It cannot decide what that server should let a caller do now. RFC 9701 strengthens the receipt between two authorities; it does not merge them.

IETF
The Certificate Shrunk. The Trust Decision Did Not
The Certificate Shrunk. The Trust Decision Did Not intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The IETF…
IETF
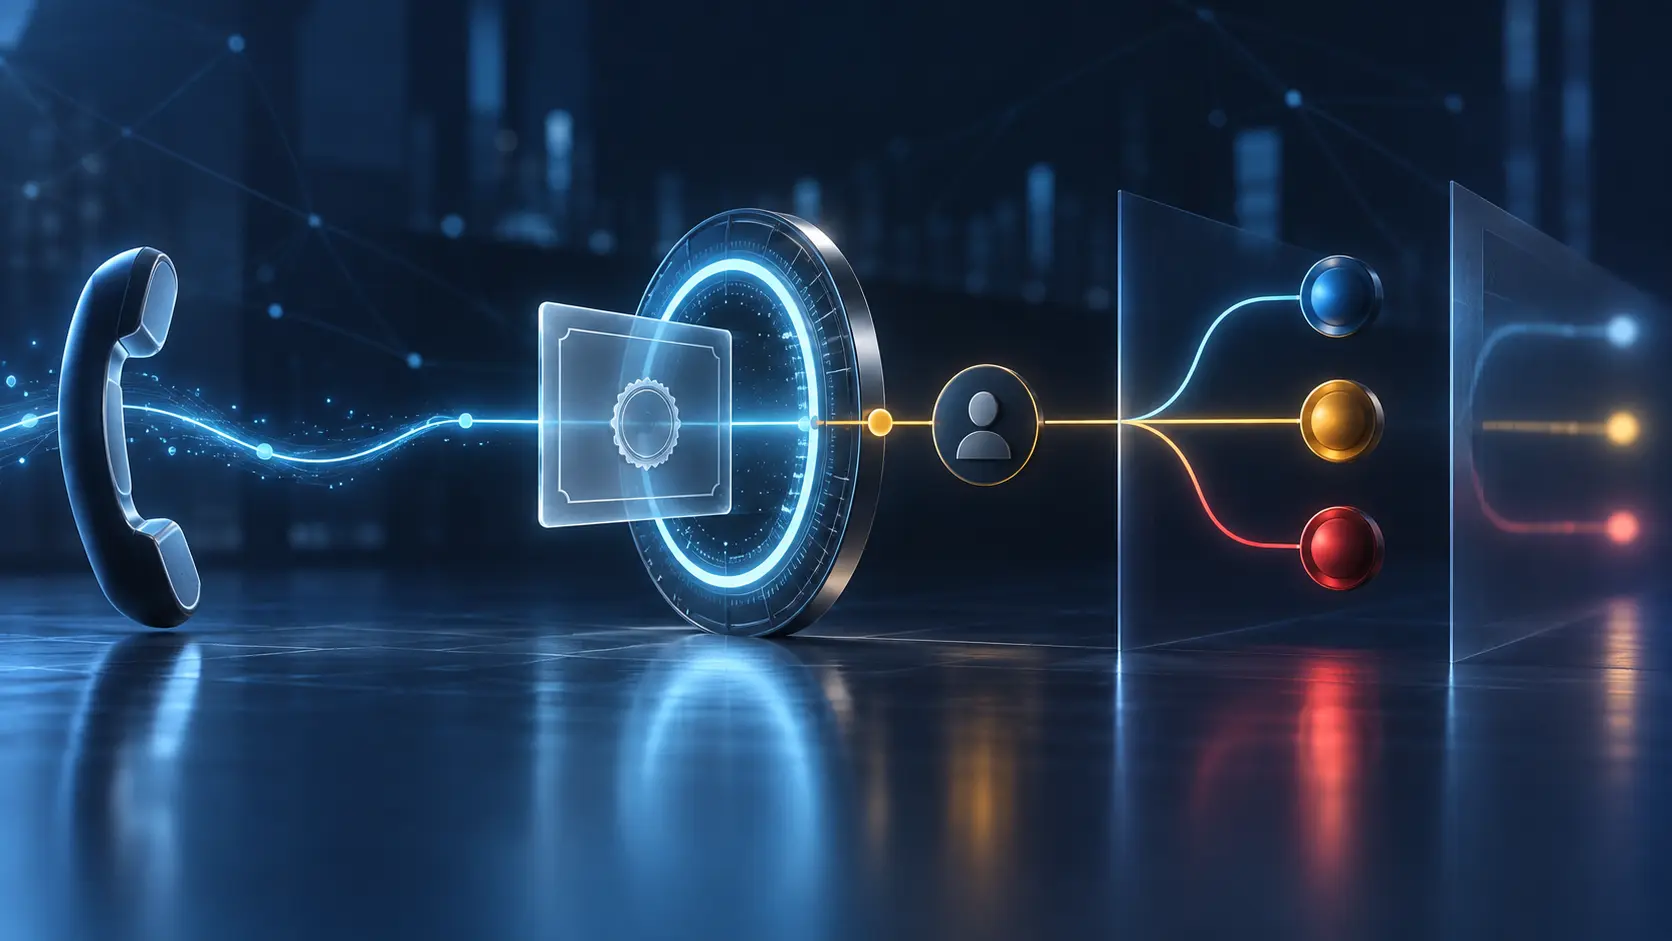
The Certificate Was Good for the Number. The Call Still Needed a Decision
STIR’s new OCSP profile can make a narrow and valuable statement in real time: this certificate is still valid for this telephone number. The discipline begins where that statement ends. It does not certify the human speaker, the purpose of the call, the safety of the request or…

CASE FILE
The OID Was Right. One Missing NULL Changed the CMS Contract
Two systems can display the same friendly label—“RSA with SHA3-256”—and still disagree about the entity in front of them. RFC 9688 makes the reason unusually crisp: in CMS, the algorithm number is only one part of the wire contract, and the presence, absence or exact contents of…

IETF
No Standards Conflict Was Found. The Factory Key Still Has No Security Grade
The IESG has found no standards conflict that would prevent publication of an IRTF taxonomy for manufacturer-installed keys and trust anchors. That decision clears a process boundary. It does not rank the five manufacturing methods, certify a factory or prove that a key stayed…

IETF
One Recipient Decrypted the JWE. The Recipient Policy Was Still Undecided
The new HPKE profile for JSON Web Encryption can return plaintext after one recipient path succeeds. In a multi-recipient envelope, that is the cryptographic floor. It is not yet the organisation’s answer to who was required to succeed, which algorithms were acceptable, or…

IETF
SATP’s Final Receipt Is Signed. The Proof Beneath It Is Still Network-Specific
An auditor can reconstruct SATP’s gateway conversation from a chain of signed, hash-linked messages. The harder question begins one layer lower: which record proves that each asset network actually reached the state the gateways asserted, and which record lets a replacement…
CASE FILE
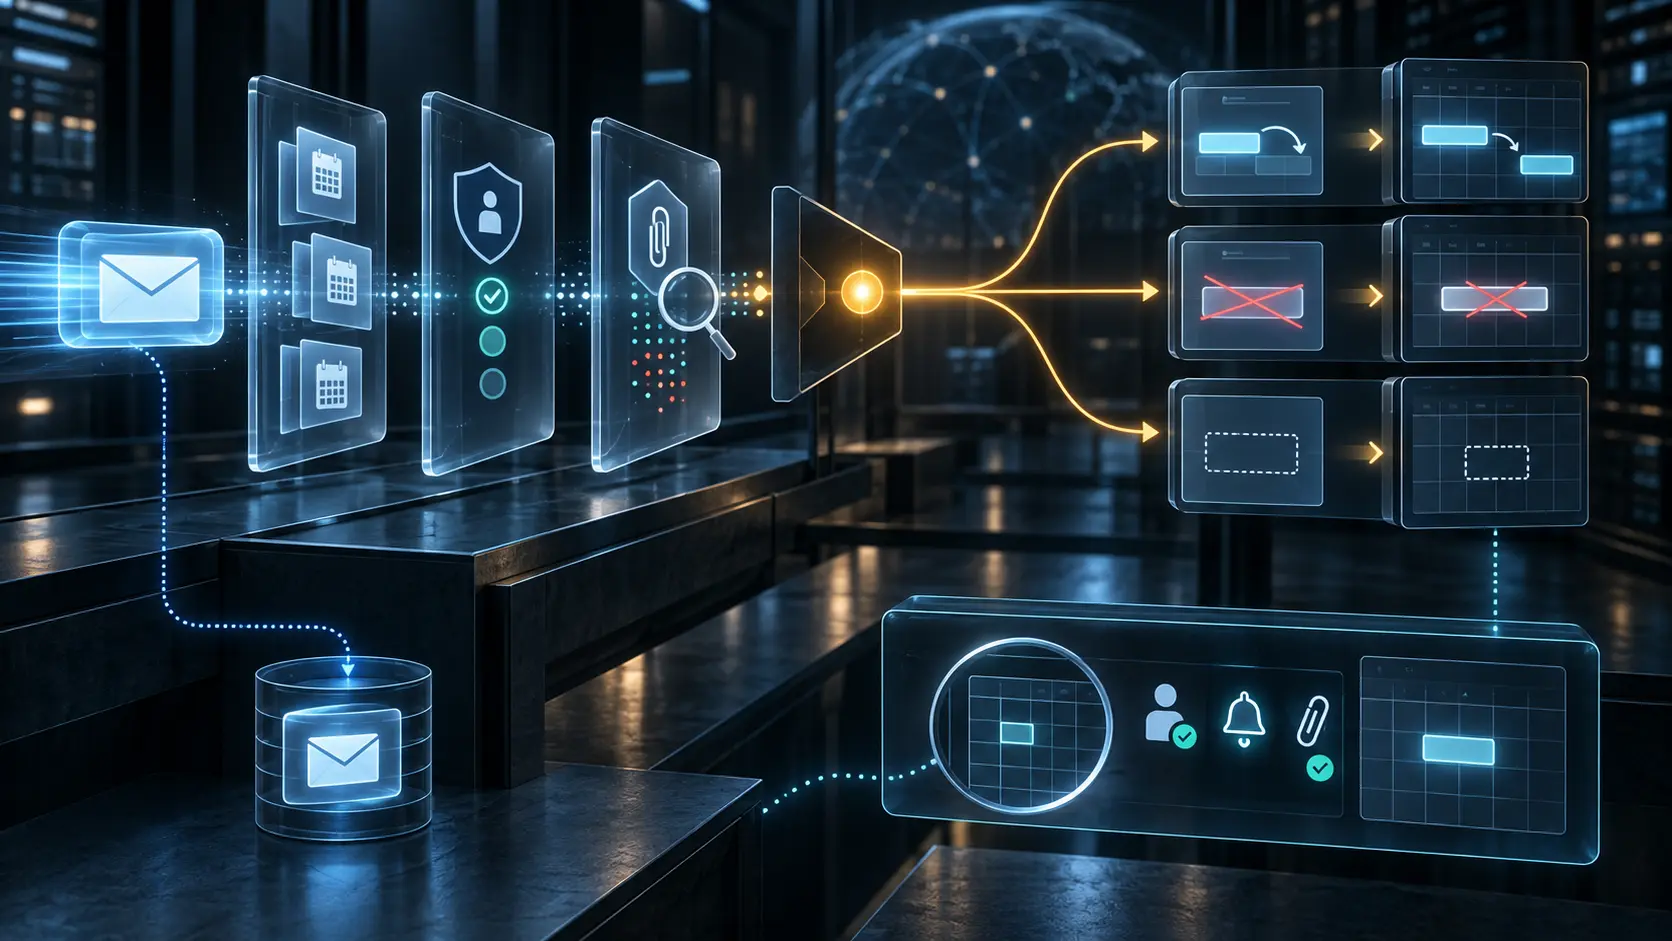
The Outcome Said Updated. The Event Had Actually Been Deleted
RFC 9671 gives Sieve a disciplined way to process calendar attachments, but its `updated` result deliberately covers update, cancellation and removal. For leadership, that is the point where a useful automation signal must stop pretending to be a complete mutation receipt.

CASE FILE
The Share Was Saved. The Intended User Still Could Not Open the Object
RFC 9670 gives collaborative systems a common JMAP vocabulary for Principals, rights and sharing changes. Its cleanest operational lesson is also its limit: a stored share is one control-plane fact, not proof of identity, visibility, enforcement, revocation or user outcome.

Number Resource Society
How a Passkey Setup Guide Became a Directory 'Institution'
A directory card listing an organisation called "Setting up 2FA with Passkey" in Taiwan points, in reality, at a section heading inside RIPE NCC's login-security documentation. The gap between the label and the underlying entity is itself the story: it shows how automated…
IETF
The certificate arrived. The delivery chain did not
RFC 9538 gives an authorized downstream CDN a disciplined route to its own certificate key. That achievement ends before DNS direction, fleet installation, TLS selection, content correctness and the user’s first successful request.

CASE FILE
RFC 9646: A 400 Response Can Request a CSR but Cannot Authorize an Identity
The monitoring system saw `400 Bad Request` and opened an incident. The device, however, had reached exactly the transition RFC 9646 expected: the bootstrap server was asking it to create a key and return a particular kind of certificate request. The status code described one…

CASE FILE
RFC 9645 and the Authentication Path That the Configuration Cannot Prove
The control plane can show four legitimate ways to establish a TLS identity: a certificate, a raw public key, a TLS 1.2 pre-shared key, or a TLS 1.3 external PSK. A live session uses one path—or a resumption path with different evidence. When an incident review asks who…