
Topic
Digital Identity and Credentials
Within the Topic facet, Digital Identity and Credentials topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.

CASE FILE
RFC 9644 and the Missing Receipt for an SSH Algorithm Decision
A green configuration diff is a comforting artefact. It can show that a device accepted an ordered list of SSH algorithms, that the names were valid, and that an approved policy reached the intended node. It cannot show which algorithms two peers offered, which intersection won…

CASE FILE
The Backup Loaded. The Keys Did Not Return to Work: RFC 9642
RFC 9642 gives network systems a shared YANG model for central and inline keys, certificates, encrypted values and built-in key state. It can make a restored configuration look complete. Recoverability still depends on the exact KEK and primary-key graph, destination binding…
CASE FILE
The Trust Anchor Was Referenced. The Peer Was Not Yet Accepted: RFC 9641
RFC 9641 gives network-management systems a common way to name and reuse certificates and public keys as trust anchors. A valid reference can prove that a configured entity exists. It cannot, without the verifier’s decision trace, prove which bytes were used, whether the peer’s…

CASE FILE
A Credential Threat List Is Not a Control Ledger
W3C has expanded the risks around verifiable credentials into a separate draft note. Its most useful distinction is not a new cryptographic promise, but a map of decisions that issuers, wallet makers and verifiers still have to make.

CASE FILE
The Data Was Split. The Operator Could Still Reassemble the Person: RFC 9614
The relay could identify the client but could not read the request. The gateway could read the request but could not see the client's address. Then one operator aligned the two logs by time and size. Every box kept its local promise; the system did not keep the privacy promise.…

IETF
The safer password exchange failed. The fallback exposed the guess
RFC 9588 protects one Kerberos password exchange from offline testing, but the protection can disappear at the moment a client falls back to the older method.
CASE FILE
W3C’s Shorter Status Pointer Leaves a Larger Verification Decision
A new draft pares a credential’s status reference down to a base address and an index. The verifier must still decide what question it is asking and which signed list can answer it.
CASE FILE
The Domain Was Canonical. The Local-Part Was Not Normalized: RFC 9598
Two email addresses can look identical on a screen and still name different certificate identities. RFC 9598 makes that uncomfortable result deliberate: prepare the domain under IDNA2008, preserve the UTF-8 Local-part exactly, and never let visual similarity stand in for byte…

History
One Record, Five Different Directories: RFC 2378
RFC 2378 described a people directory in which a field could exist without being discoverable, be discoverable without being searchable, be searchable without being returned, and be editable without being changeable over the network. The important invention was not a phone book.…

History
The Identifier Looked Like Email. It Was Not a Mailbox: RFC 2377
RFC 2377 tried to make LDAP naming deployable by borrowing names the Internet already had. Its most revealing warning concerned a value that looked perfectly familiar: `uid=mailbox-shaped-identifier` could name a directory entry without being a working email address. Reuse…

IETF
RFC 9797: A Randomized MAC Address Can Reduce Linkability Without Becoming Device Identity
A support desk can see the same laptop twice: once under yesterday’s MAC address and once under today’s. That does not mean there are two devices, and seeing one address twice does not prove there is only one. RFC 9797 makes this mundane ambiguity a governance problem: privacy…

Global Cloud Services Trends
Bird’s $450 million debt finances shareholder liquidity, not proof of agent demand
Bird has paired a dividend recapitalisation with an ambitious communications layer for AI agents. The first transaction can be completed by banks and shareholders; the second becomes valuable only when authorised machine actions survive consent, delivery, carrier charges, abuse…
North America Institutional Trends
EigenQ’s $45 million headline buys a conditional commercialisation clock
The quantum-security company has not received a $45 million operating cheque. Its filed financing is a two-stage, discounted and secured bridge in which cash, closing risk, dilution and collateral must be reconciled before the valuation story can be judged.

IETF
The Dialog Continued. The Authority Did Not Travel With the Identifier
Agentproto's proposed dialog context can keep one interaction legible across agents, tools, networks and interruptions. That continuity is operationally valuable precisely because it is narrow: a shared identifier can correlate a dialog without proving who was entitled to act…

ICANN
4.3 Million IDNs Are a Registration Count, Not a Universal Acceptance Result
A name can exist in the DNS, appear in a registry total and still be rejected by the first sign-up form that asks for its email address. ICANN’s new annual report makes both sides visible: multilingual identifiers are widely available, while the software path that must use them…

History
One Clean Match Hid the Hard Questions: RFC 2345 and the Company-Name Lookup
A company name went in; a name and a URL came back. RFC 2345 made that exchange intentionally small enough for a 1998 browser add-in and a port-43 server. The economy was the point. Yet the response line carried no proof of who registered the domain, which legal entity the name…
CASE FILE
WebAuthn’s Remote Client Can Validate the RP ID. The Local Permission Cannot Prove It Did
The first public draft of WebAuthn Level 4 proposes a careful handoff for remote-desktop sign-ins: a local browser may use client data supplied by a remote machine, but only after a per-origin grant. That grant opens the local capability. It does not preserve evidence of the…

IETF
One Bearer Token, One Audience: WIMSE Revision 07 Draws the Receiver Boundary
An external identity provider that accepts the same bearer token as a Kubernetes API server does not merely validate the workload. It acquires a credential it can present back to the API server as that workload. Revision 07 of the WIMSE practices draft turns the separation of…
Story
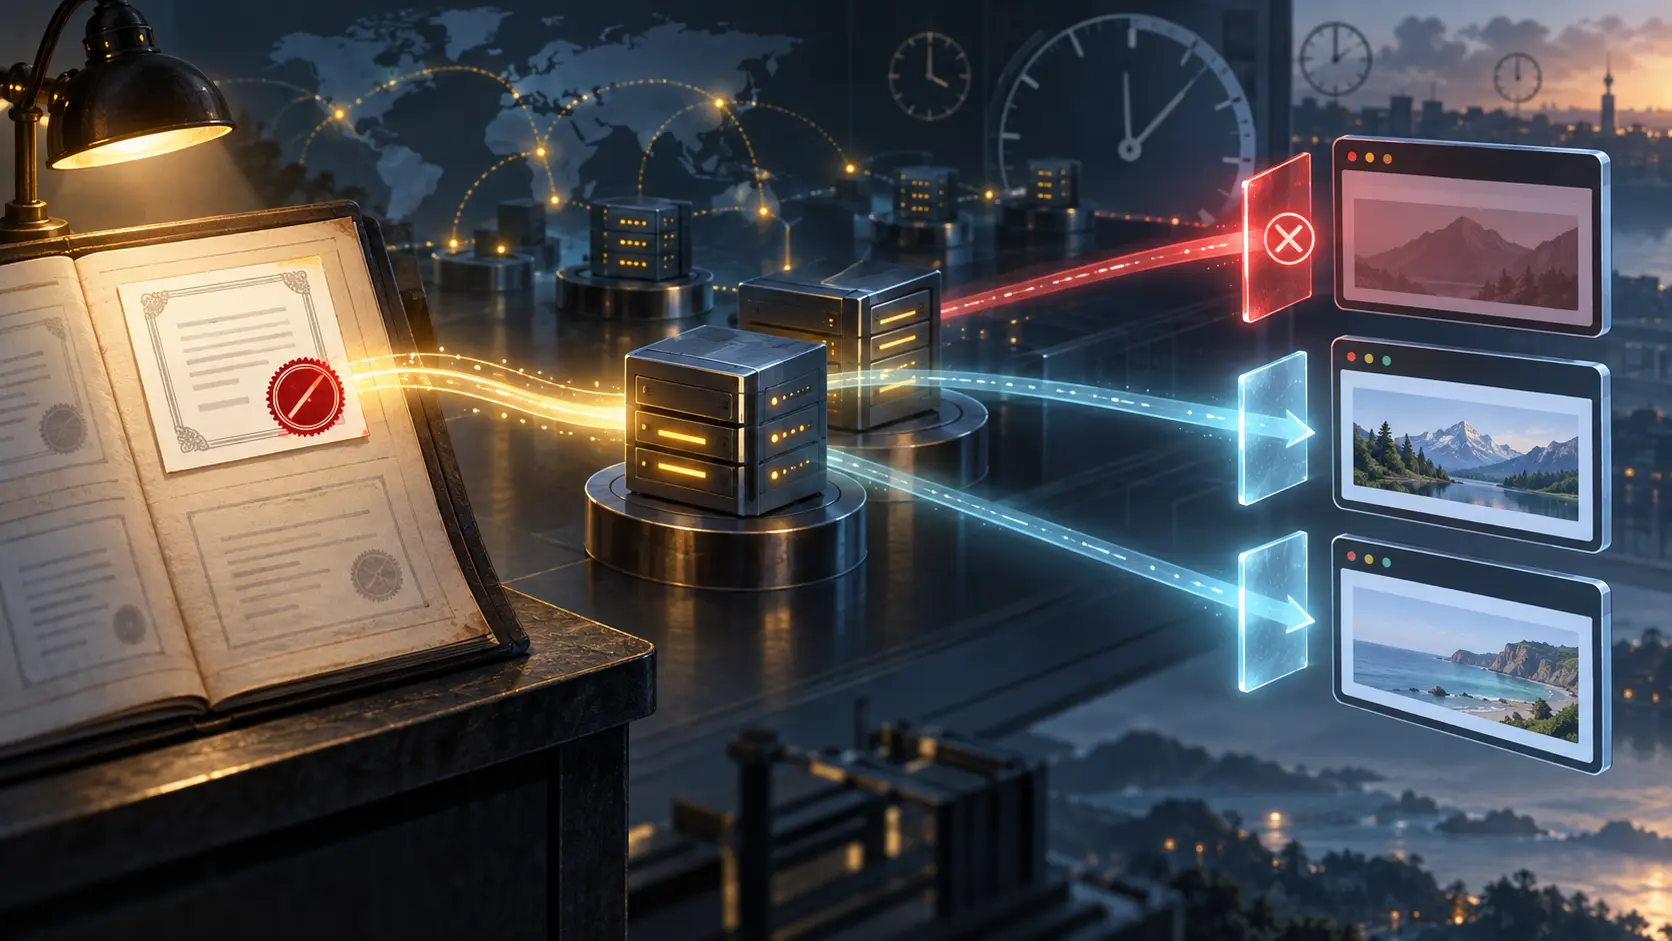
One Revoked Certificate, Three Browser Outcomes at APNIC 62
The certificate was on the revocation list. That was not the end of the story. Geoff Huston's APNIC 62 demonstration put the same adverse record in front of three browser policies and obtained different results—a useful warning about the distance between publishing a security…

IETF
WebAuthn’s 2026 Rejoin Handoff: The Governance Receipt Behind a New Participation Cycle
The Web Authentication Working Group’s 11 September 2026 recharter begins a new institutional phase for WebAuthn. The central challenge is not simply continuing technical discussion; it is preserving a reliable record of how an approved charter becomes active participation and…