
Summary
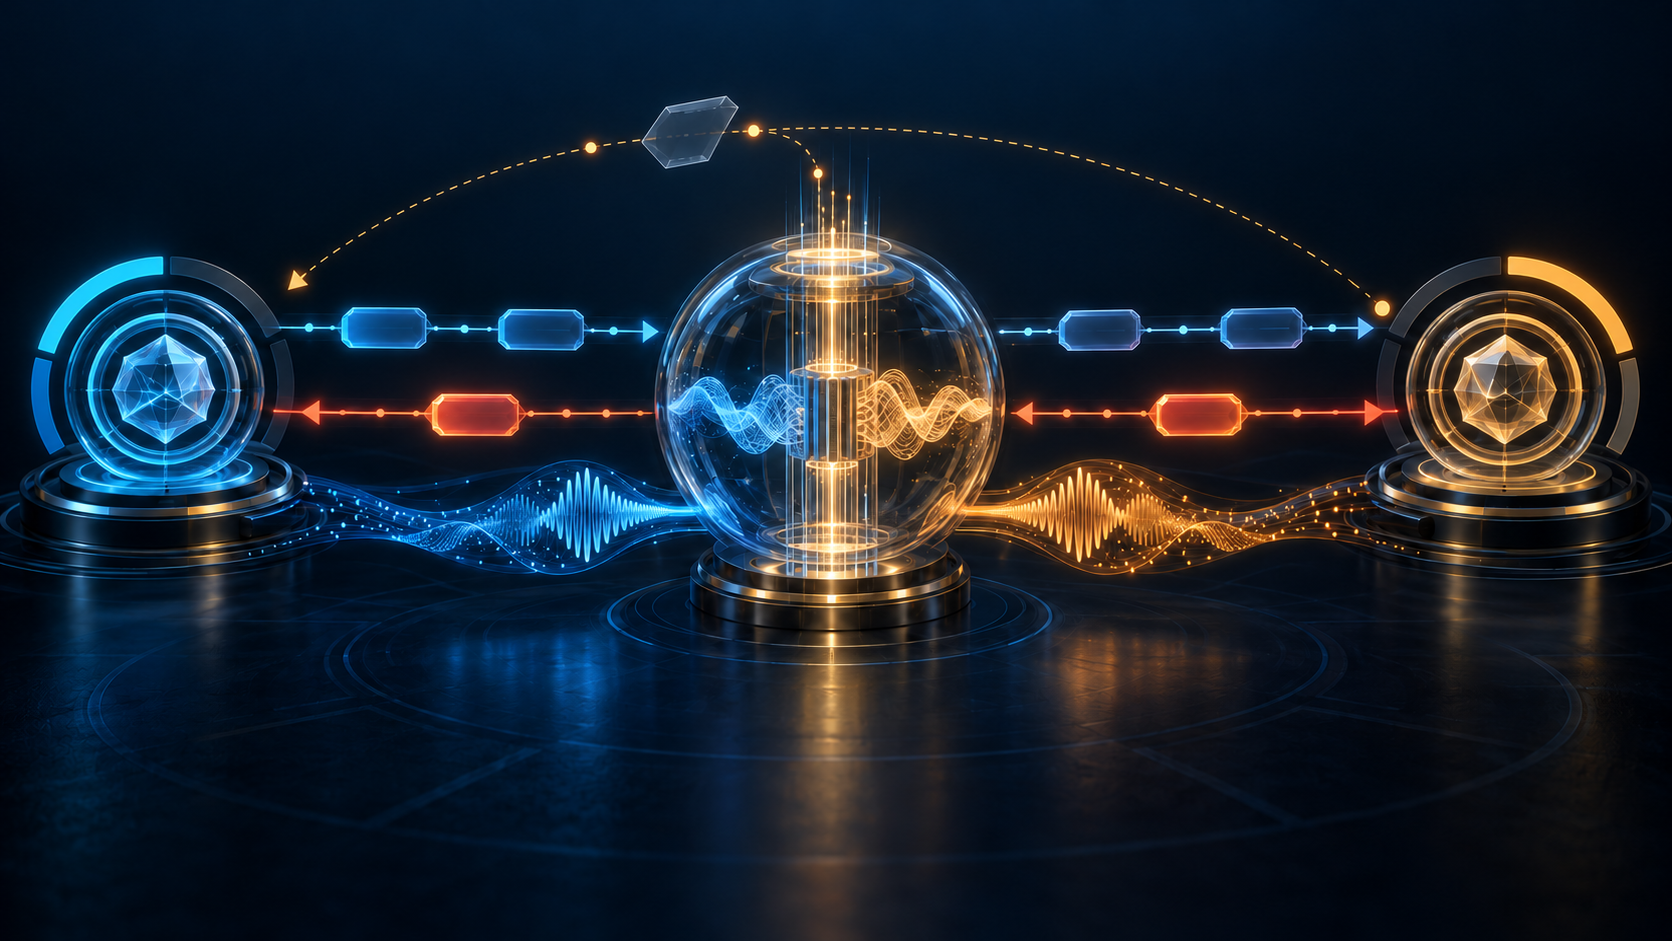
- RFC 5370 specifies the SIP conference-bridge model for invoking a transcoding service. The transcoder is a B2BUA, not a proxy: it terminates one transaction and creates another even when it preserves visible caller information and returns the same final status code.
- If a provisional response is lost, an upstream
603 Declinecannot by itself show whether the transcoder rejected the caller or the callee rejected the transcoder. The specification uses History-Info to restore the missing attribution. - Its exception from URI-list opt-in depends on a narrow structure: one caller-named target, one generated INVITE and caller identity present downstream. Authentication, successful signalling and media flow still do not prove correct transformation or accessible communication.
One decline had two possible authors
A sent an INVITE to transcoder T. T sent an INVITE to B. B returned 603 Decline, and T generated a 603 Decline toward A. The line that operations wanted to read as a single causal chain was, in protocol terms, two chains joined by an application decision.
RFC 5370 is explicit about the boundary. T acts as a back-to-back user agent, not as a proxy. The outgoing INVITE belongs to a different transaction from the incoming one. The final response toward A is newly generated, although it should use the status code received from B.
That distinction becomes operational when the provisional 183 Session Progress from T to A is lost. A sees a final 603, but the code alone cannot distinguish rejection of the first leg by T from rejection of the second leg by B.
The same symbol can therefore report two different exercises of authority. A status code is a classification. It is not, by itself, a provenance record.
The bridge did not forward a transaction
Calling T a bridge can suggest that it passes signalling through. RFC 5370 denies that picture. T terminates the A–T relationship and originates the T–B relationship.
The transaction identifiers, dialog state, routing surface, SDP and authentication context on one side do not automatically continue onto the other. T builds an outgoing session description appropriate to the transcoding service it provides. An audio transcoder, for example, advertises the codecs it supports toward B.
This allows T to negotiate independently on each leg. It is also why an investigator cannot join records merely because the upstream and downstream messages are close in time or carry matching response codes.
A reliable receipt needs both transaction identities and T's correlation decision. Without them, a monitoring system can count two events as one, assign B's rejection to T, or assign T's policy refusal to B.
Visible caller identity was not transaction continuity
RFC 5370 requires T to form the outgoing From header from the incoming From value, subject to the privacy requirements expressed by the incoming request. It immediately excludes the tag parameter from that reuse.
The exclusion is not decorative. The tag participates in dialog identity. Keeping a displayable address while changing the tag is consistent with the larger architecture: the downstream request can represent the original caller while remaining T's newly generated transaction.
Four facts must stay separate. A string can be visible in From. T can have authenticated the user who invoked it. T can have authorized that user to request a service. A downstream identity mechanism can convey an assertion about the original sender. None of these facts turns the downstream INVITE into the packet A sent.
Privacy adds another decision surface. T must respect the incoming privacy requirements when constructing the outward identity. A log that records only the displayed From cannot prove which private identity T received, which credential it authenticated, or which disclosure rule it applied.
History was an evidentiary dependency
RFC 5370 says use of History-Info between T and A resolves the ambiguous failure flow. The choice reveals what the final code lacks: a trace of how the request reached the response.
If the 183 is present, A has some evidence that T accepted enough of the request to begin downstream processing. If that provisional evidence disappears, the final 603 loses an important discriminator. History information restores a path-level account rather than changing the meaning of 603 itself.
This is a general lesson for automated evidence systems. Optional or lossy intermediate events may carry the only observation that separates service admission from target outcome. Retaining only terminal state can erase authority.
RFC 5370 cited the then-current RFC 4244. RFC 7044 later revised the History-Info specification. That documentary evolution matters to an implementer, but it does not prove that a particular network emitted or retained adequate history. Support, configuration, privacy policy and captured trace remain separate evidence.
The rejected alternative made attribution more expensive
The RFC considered another design. T could act as a pure conference bridge, answer A with 200 OK, invite B separately, and let A subscribe to conference state for the result of the second invitation.
That structure would separate admission to T from admission by B more visibly. A successful first leg would no longer be made to resemble a successful end-to-end establishment, and downstream state would arrive through an observation channel.
The document rejected the alternative for this transcoding service because it required more messages, more complexity and longer setup delay. The selected flow reduced coordination cost and accepted dependence on History-Info to disambiguate failure.
This is not a timeless declaration that fewer messages are always better. It is a recorded trade in a specific October 2008 design. Leadership should read it as an allocation: latency and implementation simplicity were purchased partly with a stronger provenance requirement.
One target was a control boundary
Caller A invokes T by sending an INVITE that contains SDP and a recipient-list body. The URI-list holds B's URI. T uses the request-contained-list procedures of RFC 5366 to generate the downstream INVITE.
RFC 5370 narrows this service to one URI. If T receives more than one, it should return 488 with an explanation that at most one URI is allowed. The limitation is not a general claim that request-contained lists cannot establish multiparty conferences. It is the boundary of this two-party transcoding model.
The single target changes the security analysis. T is not allowed to turn one request into an unbounded fan-out. The caller names the same destination it intends to reach. A record of the exact recipient-list is therefore authority-bearing evidence, not incidental MIME payload.
Protecting only the SDP while leaving the target list mutable would protect the media proposal but not the decision about whom T should contact. Each body part answers a different control question.
The consent exception depended on three facts
RFC 5363 treats unsolicited requests and list amplification as serious risks. RFC 5370 nevertheless says this specific transcoding service need not use opt-in lists.
Its reasoning has three linked premises. T generates only one INVITE. The caller already knows and supplies B's URI rather than asking T to translate an opaque identity into an unknown target. The caller's identity is present in T's outgoing request.
Remove one premise and the conclusion must be reconsidered. A service that expands one name into many destinations, substitutes a target the caller did not name, or obscures the invoking identity is no longer the structure the RFC analyzed.
“No opt-in list required” is therefore not a generic consent waiver for intermediated communications. It is a scope result tied to cardinality, target knowledge and identity presentation.
The governance receipt should store those premises explicitly. Otherwise a later feature can broaden fan-out while inheriting an exception whose factual basis has disappeared.
Integrity protected the instruction, not the outcome
The security section emphasizes integrity for URI-lists and mentions S/MIME or TLS, which can also provide confidentiality when needed. The immediate object is the caller's target instruction.
Integrity can show that the protected list was not altered within the mechanism's trust assumptions. It does not show that T authorized the caller correctly, constructed the right SDP, reached the intended user behind the URI, transformed media accurately or deleted retained content.
Transport protection likewise has a leg and endpoint. The A–T protection context does not automatically become T–B protection, and T must see enough media to provide its service. The conference-bridge model concentrates signalling and media at T by design.
Historical references need restraint. RFC 5370 cited TLS 1.2 in RFC 5246 and S/MIME material current at publication. A current system must evaluate its present protocol and policy context; the 2008 citation is not a configuration recommendation.
A redirect delegated a new act
RFC 5370 also lets callee B invoke transcoding. If B receives an unacceptable session description, it can return 302 Moved Temporarily with a Contact pointing to T and a ?body= parameter containing a recipient-list body with B's URI.
The response does not cause T to transform media by itself. A acknowledges the failed attempt and generates a new INVITE to T. T then creates another INVITE toward B.
The redirect is thus a delegation and routing instruction. It is evidence that B proposed a path, not proof that A followed it, T accepted it, both legs negotiated, media flowed or the transformation served the user.
The RFC calls the body-in-URI encoding complex, noting the need to escape carriage returns and line feeds, and says the 3pcc model is simpler for callee invocation. Complexity here is not cosmetic. Encoding errors can change the target instruction or prevent the new attempt before T is involved.
Accessibility began the requirement, not the proof
The specification says its invocation model meets SIP transcoding-service requirements that support deaf, hard-of-hearing and speech-impaired people. Speech-to-text is one example of the service T may provide.
The protocol can establish A–T and T–B signalling, negotiate two media legs and carry transformed output. Those observations still do not establish that the language was correct, latency tolerable, direction appropriate, text intelligible or communication equivalent for the participant.
A status report saying “bridge established” is therefore infrastructure evidence. An accessibility outcome requires user-level evidence and should preserve uncertainty when that evidence is absent.
The risk is especially sharp because both signalling legs can succeed while transformation quality fails. Success codes may prove that the system crossed its control surfaces and still say nothing about whether the human purpose was achieved.
Later identity work changed context, not history
RFC 5370 allowed T to provide information about the original sender using the SIP identity mechanism then specified by RFC 4474. RFC 8224 later obsoleted RFC 4474.
That lineage should prevent present-tense overclaiming. The article can say what RFC 5370 required and permitted in 2008. It cannot infer which identity mechanism a current deployment uses or whether a downstream recipient verified it.
The durable idea is the separation of roles. The B2BUA owns the downstream transaction. It may carry an assertion about an upstream originator. The assertion, the presenter and the transaction originator are related but not interchangeable.
Systems that reduce them to one “caller identity” field lose the ability to explain privacy transformations, verification failures and intermediary authority.
The bridge concentrated decisions
RFC 5369 compared 3pcc and conference-bridge topologies. RFC 5370 specifies the bridge path in detail. A simpler invoking endpoint delegates more work to T.
T receives the target list, authenticates and authorizes the invoker, applies privacy, constructs identity presentation, generates SDP, originates the downstream transaction, receives the downstream result, creates the upstream result, and transforms media.
Each action needs evidence at its own boundary. One audit event called “transcoding session” is too coarse to reconstruct which policy or external party produced a failure.
This concentration is precisely why the RFC 5370 thesis does not duplicate RFC 5369. The framework asks which topology to choose and when transcoding is justified. The model shows what evidence is broken and remade after the bridge is chosen.
A minimum record can remain small
Lu Heng's Minimum Initial Specification is useful here as a disclosed analytical lens. A system does not need to preserve every packet forever to maintain authority. It does need a stable minimum: authenticated invoker, authorization decision, protected single target, privacy instruction, upstream transaction, downstream transaction, leg-attributed result, service identity and negotiated media boundary.
Future implementation choices can remain local as long as they emit that minimum record. The standard can define the interoperability surface without pretending to know every jurisdiction, retention rule or accessibility workflow.
Reality Layers supplies the second lens. A visible From, credential decision, SIP transaction, response code, media path, transformation output and human understanding are different kinds of reality. Clarity comes from preserving the boundaries, not from forcing them into one success field.
RFC 5370's most consequential sentence is therefore architectural rather than numeric: T is a B2BUA, not a proxy. Once that is true, every apparent continuation must be proven as a correlation.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance