
Primary Domain
Infrastructure
Within the Primary Domain facet, Infrastructure intelligence groups reporting by primary domain so readers can follow a focused area of internet infrastructure, governance, connectivity markets, or digital capital. The page brings together related articles, public evidence, institutions, companies, people, regional exposure, operating dependencies, and market context that may otherwise sit across separate category pages. It explains the domain, the likely actor class, the market or governance context, and the source material readers should use when comparing signals. Operators, analysts, and governance readers can see how the same domain appears across events, profiles, market shifts, public-source evidence, regional dependencies, and longer-cycle infrastructure decisions over time.

Europe and Middle East Institutional
Subsea Cable Assets launches carousel rental service
The new service gives subsea contractors temporary access to 4,000- and 6,000-tonne cable carousels, with a first European contract already secured.
IETF
Pradosh Mohapatra and the Bandwidth Value That Was Not Available Capacity
A route can advertise a perfectly valid bandwidth number while the usable path behind it is smaller, older or defined by an entirely different rule. RFC 10005 makes the number portable. It does not make it a measurement of capacity now available to traffic.

CASE FILE
The DNS ID Was Zero. The Cache Still Needed a Clock: RFC 9953 and DoC Evidence
A cache can make a constrained network quieter without becoming the authority that decided what the answer means. RFC 9953 makes that line unusually precise: it lets equivalent DNS-over-CoAP requests share a representation, then requires a separate clock before anyone may rely on…

CASE FILE
The Receipt Put a Statement on the Ledger. It Did Not Decide to Trust It: RFC 9943 and SCITT
A software-supply-chain record can look like a conclusion when its machinery is working well. A statement is signed. A transparency service accepts it. A receipt carries a verifiable proof. An auditor can replay a sequence and a dashboard can show a reassuring green line. The…
IETF
Hooman Bidgoli and the Leaf Set That Was Not a Delivered Multicast Service
The control plane can produce an orderly list of intended receivers while the data plane is still divided across controller state, replication segments, service context and receivers that have not seen a packet. RFC 10018 makes the list useful. It does not make the list a…
CASE FILE
The Forum Could Suspend a Post. It Could Not Claim the Network: RFC 9945 and the Boundary of IETF Moderation
A forum needs a way to stop disruption without mistaking that housekeeping power for a title over everything discussed there. RFC 9945 makes that distinction unusually visible: it gives the IETF a shared procedure for its public online spaces, while repeatedly locating the…

IETF
Carlos Pignataro and the Watt Reading That Did Not Prove a Greener Network
A power meter can report a precise number while leaving the environmental claim undecided. Turning that number into energy, emissions or permission to switch off spare capacity requires separate evidence—and a record of who accepted the trade.

CASE FILE
The Multicast Request Reached the Group. It Did Not Authorize the Action: RFC 10020 and CoAP Evidence
One protected request can look wonderfully decisive. A controller addresses a CoAP group, the network fans it out, several endpoints answer, and the panel records a quiet burst of acknowledgements. In a constrained environment, that economy matters. It is also exactly where an…

CASE FILE
The Group Key Reached the Devices. It Did Not Assign the Act: RFC 10020 and CoAP Group Authority
A protected message can leave one sender and be intelligible to a group. It cannot make five receivers one decision-maker. RFC 10020 matters because it gives constrained systems a disciplined way to speak to a group without erasing the separate evidence required for membership…
CASE FILE
What the Aggregate Report Actually Knows: RFC 9990 and the Boundary Before Enforcement
A DMARC dashboard can make a narrow observation look like a verdict. One receiver reports a large count from a source range, records an evaluated policy and shows a disposition. That is valuable operational evidence. It is not a global traffic census, proof of a sender's intent…

JPNOG
JANOG Gives Officers a Separate Route to Rewrite Its Rules
JANOG’s public rules make mailing-list subscribers members, but they also let an officer supermajority amend the rules—or dissolve the voluntary association—without using the separate membership-approval route.

ICANN
ICANN’s Name Collision Assessment Is Not a Delegation Decision. What Does a High-Risk String Need to Prove Next?
An ICANN name-collision assessment is a risk-management step in the 2026 New gTLD Program, not a confirmation that a proposed label will—or will not—reach the DNS. Its practical importance is in the next gate: a string identified as high risk can require a mitigation plan that…

MYNOG
MYNOG Can Rewrite Attendance Terms After Registration
MYNOG’s published registration terms do more than set an entry price. They let the organisers amend the terms through publication on the conference website, treat later attendance as acceptance, and retain discretion to exclude a entity without refunding the registration fee.

ICANN
ICANN Names a Safeguard Assessment Provider. When Does String Review Become a Registry Agreement Obligation?
ICANN has appointed Mirror Group LLC for 2026 Round Safeguard Assessments. The important boundary is between a string-risk assessment and a safeguard that becomes part of a Registry Agreement.

CASE FILE
The Model Could Explain the Network. It Could Not Authorize the Change: NEMOPS and the Boundary Between Visibility and Control
The NEMOPS workshop report asks for better models, observability, tooling and verification in network management. Those are valuable improvements in what an operator can see and test. They do not decide whose service may be changed, which risk is acceptable, or who bears the cost…

LKNOG
The Institution Born After APNIC 42: Why Sri Lanka Built LKNOG
APNIC 42 brought the regional internet operations community to Colombo in 2016. LKNOG's own early record suggests that the more consequential question began after the conference ended: who would maintain a place for Sri Lankan operators to exchange practice when the next…

CASE FILE
An OAM Requirement Was Written Down. It Did Not Prove a Working Diagnostic: RFC 9974 and BIER Evidence
A requirements catalogue can sharpen an engineering question. It cannot, on its own, answer whether a particular network can run the test, what the test observed, or who may act on it.
CASE FILE
The Signed Time Saved a Transfer. It Did Not Prove a Moment: RPKI, RFC 9589 and the Switchover Boundary
A RPKI relying party can keep validating useful repository material after its preferred delivery path fails without pretending that a signed timestamp is a trustworthy clock. RFC 9589 makes that distinction operational: one CMS attribute can align filesystem comparison across…

CASE FILE
Four Thousand Was a Prefix Claim, Not a Rate-Limit Mandate: RFC 9977 and the Evidence Boundary
A prefix file can make an address range easier to group. It cannot convert a count of end sites into a command to relax a local risk control.
Europe and Middle East Institutional Trends
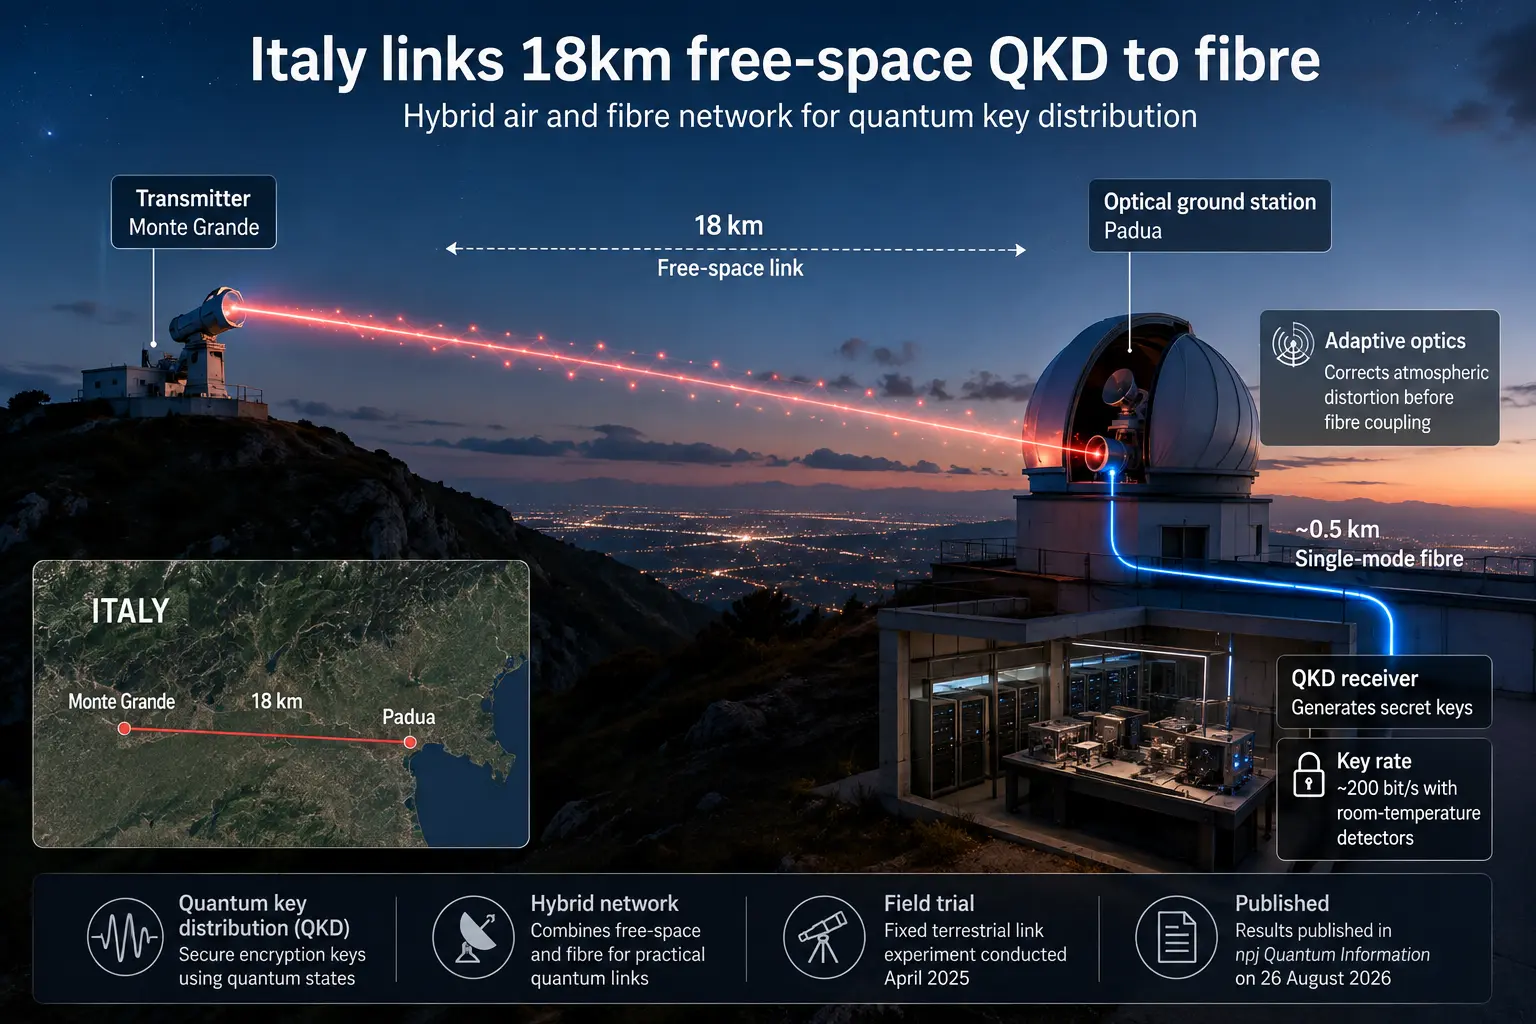
Italy links 18km free-space QKD to fibre
Researchers linked an 18km free-space quantum channel to single-mode fibre, showing how adaptive optics can bridge atmospheric and terrestrial quantum links.