Summary
- GAO identified 117 established federal cybersecurity regulations across 37 agencies and nine critical-infrastructure sectors as of June 2026. Eighty required at least one of three kinds of proactive report; 48 included cyber incident reports.
- The audit found potential overlap in incident definitions, reporting triggers, deadlines, content and delivery routes. The 80-rule figure measures reporting types, not 80 proven duplicate submissions by any one operator.
- ONCD had the federal coordinating role, yet GAO found limited harmonization progress. As of July 2026, the new national cyber strategy still lacked a published implementation plan assigning lead roles and next steps.
The attacker sees one incident; the operator sees several forms
A report can save time. The right agency learns that a bank, carrier, pipeline or contractor has a problem before the effects spread. A report can also consume the same time the defender needs to work out what has happened. The operator cannot safely choose the first clock by looking at an agency seal. The decision depends on which legal rule covers the service, what counts as a reportable event under that rule, when the threshold was crossed and where the notice must go.
The Government Accountability Office's July 2026 report gives this problem a count. Its auditors found 117 established federal regulations containing cybersecurity requirements for private entities, issued by 37 agencies across nine critical-infrastructure sectors. Eighty required at least one of three proactive reporting types. Forty-eight covered cyber incidents, 52 covered cyber plans or other technical information, and 25 covered completed reviews, audits or assessments. A regulation can appear in more than one of those three columns. Together the 80 contained at least 125 type-specific reporting requirements.
The more revealing number is 48. Those incident-reporting regulations came from 27 agencies. GAO found different definitions of a reportable cyber incident, different thresholds and triggers, different clocks and different demands for content. An operator deciding whether to isolate a system has to translate an uncertain technical event into several legal vocabularies. One regulator may ask when a breach was discovered; another may require an assessment of impact before notice. If the submission destinations differ, the same discovery can begin several administrative journeys.
GAO did not observe 48 notices filed for a single incident. Its 80-of-117 statistic groups rules with similar types of reporting and flags possible conflict or duplication. It does not measure the exact number of forms a particular operator must file, a dollar cost, or lost minutes in an actual response. The missing evidence is specific: a rule-by-rule crosswalk for one covered operator and one incident, with each trigger, deadline, payload and receiving agency identified. That crosswalk would show where separate reporting protects a distinct public interest and where it simply asks for the same fact twice.
Fifteen financial rules illustrate the trap
GAO's original report identifies 15 existing financial-sector regulations under which a private entity may have to report a cyber incident, depending on its business and the rules that apply. Their agencies include banking, securities, commodities and consumer-protection regulators. A proposed cross-sector rule under the Cyber Incident Reporting for Critical Infrastructure Act, or CIRCIA, added another prospective handoff in the July 2026 audit. The proposed rule was outside the count of 117 established regulations.
The important word is may. A bank, exchange, contractor and payments firm do not carry the same regulatory bundle. A sensible common system would start by identifying the applicable rules, then map which facts and acknowledgement each one needs. Filing one report can satisfy multiple obligations only when the agencies have made that equivalence valid and operational. CISA had explored a substantially similar reporting exception that could let one submission serve two regimes; GAO described that as a possibility in the proposed-rule process.
The problem extends beyond incidents. A federal contractor serving more than one agency may be asked to provide similar security plans or audit documentation more than once. A transportation operator may need cybersecurity plans under as many as seven federal regulations, depending on its activity. GAO's categories capture the wider temptation to solve each agency's information problem by adding another request to the operator's desk. The agency receives a form. The operator keeps the reconciliation bill.
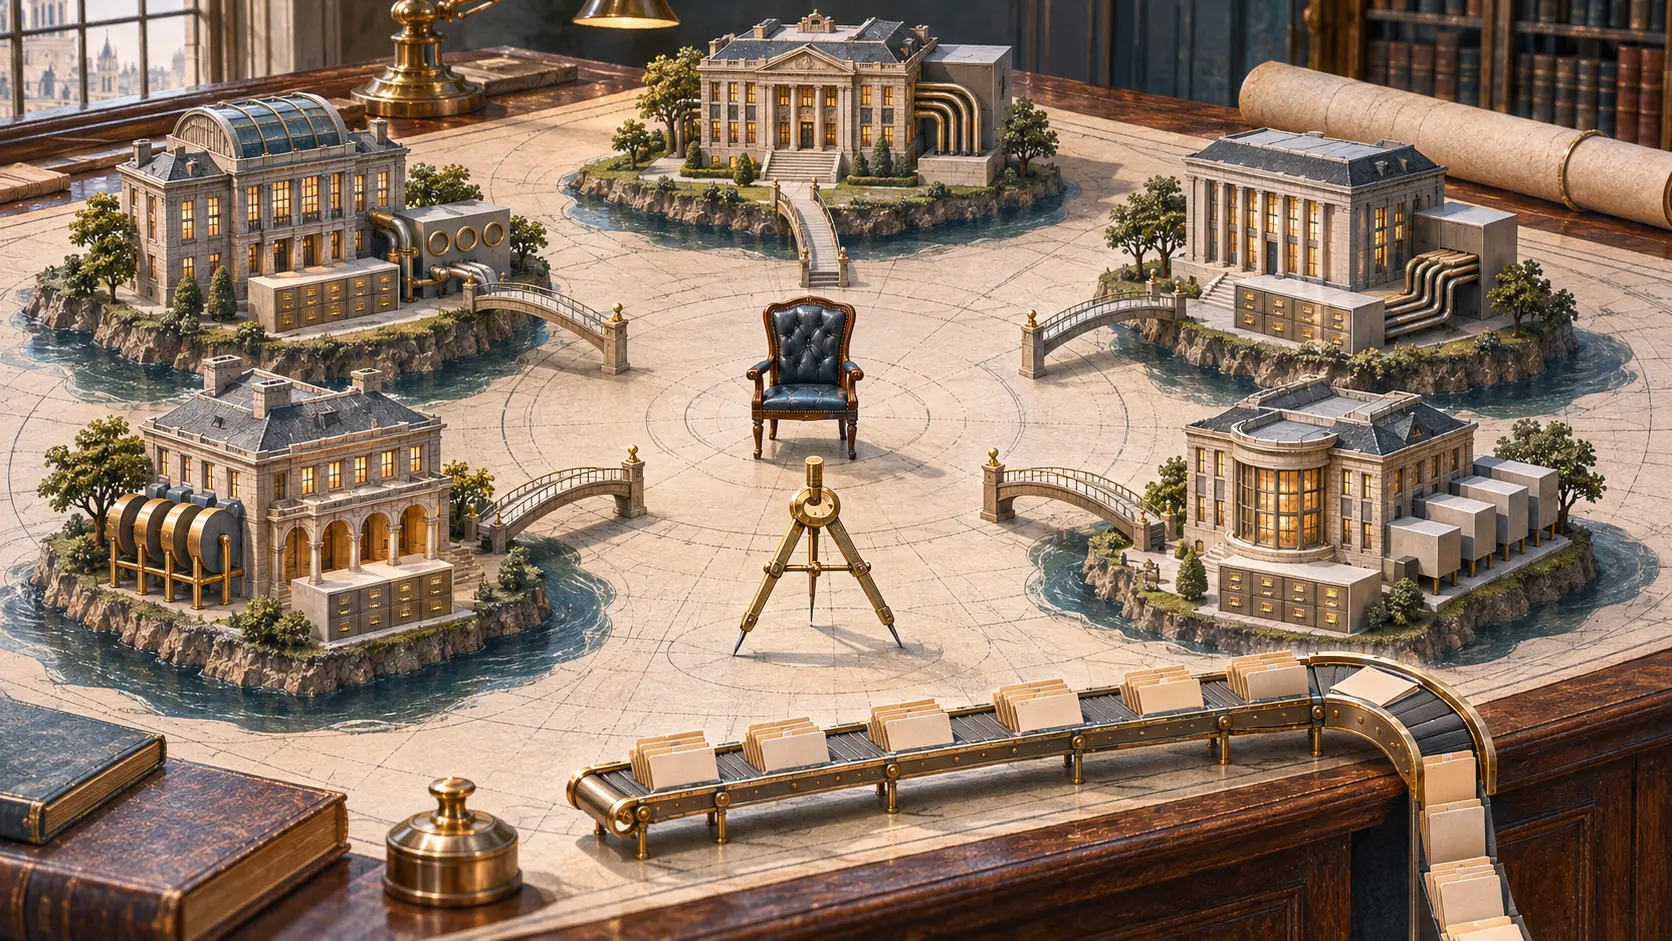
The harmonizer has no published operating map
Congress assigned the Office of the National Cyber Director, ONCD, a coordinating role in streamlining federal cyber regulations. Other parts of government also took up the problem. The Cyber Incident Reporting Council produced recommendations; the Department of Homeland Security issued a 2023 report with eight of them, including model definitions of reportable incidents, reporting timelines and triggers. A separate interagency regulator forum explored alignment. The March 2026 national cyber strategy made reducing burdens and aligning regulators a stated priority.
GAO's chronology is less impressive than the institution chart. The interagency forum had been inactive since late 2024. By May 2026, DHS had not reported the status of work on its eight recommendations. GAO sought information from ONCD in September 2025 and June 2026 and had received none by that June. As of July 2026, the administration had not released implementation plans for the new strategy. The unresolved questions were who leads which change, what agencies must agree on and how an operator will know the result has reached its reporting desk.
The public test is plain. Publish the crosswalk: the rule, covered entities, trigger, deadline, required fields, receiving agency and lawful reuse of a submission. Name the office that maintains it when a rule changes. Show how one incident report is accepted, routed and acknowledged across agencies where the law permits. Then run an exercise with an operator whose services cross two sectors. The exercise should record the technical response and the reporting path separately, so an administrative success cannot masquerade as a security outcome.
A cyberattack does not wait for a federal org chart to settle. The clock that matters first is the one protecting the service. Washington can demand the information it needs. It can also make the route to deliver that information legible before the next alarm sounds.
Sources: US GAO report page; GAO original 36-page report.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance