
Summary
- RFC 3617 registered a common syntax for TFTP references while strongly discouraging continued use of the underlying protocol. Standardization made legacy behavior legible; it did not endorse its security or suitability.
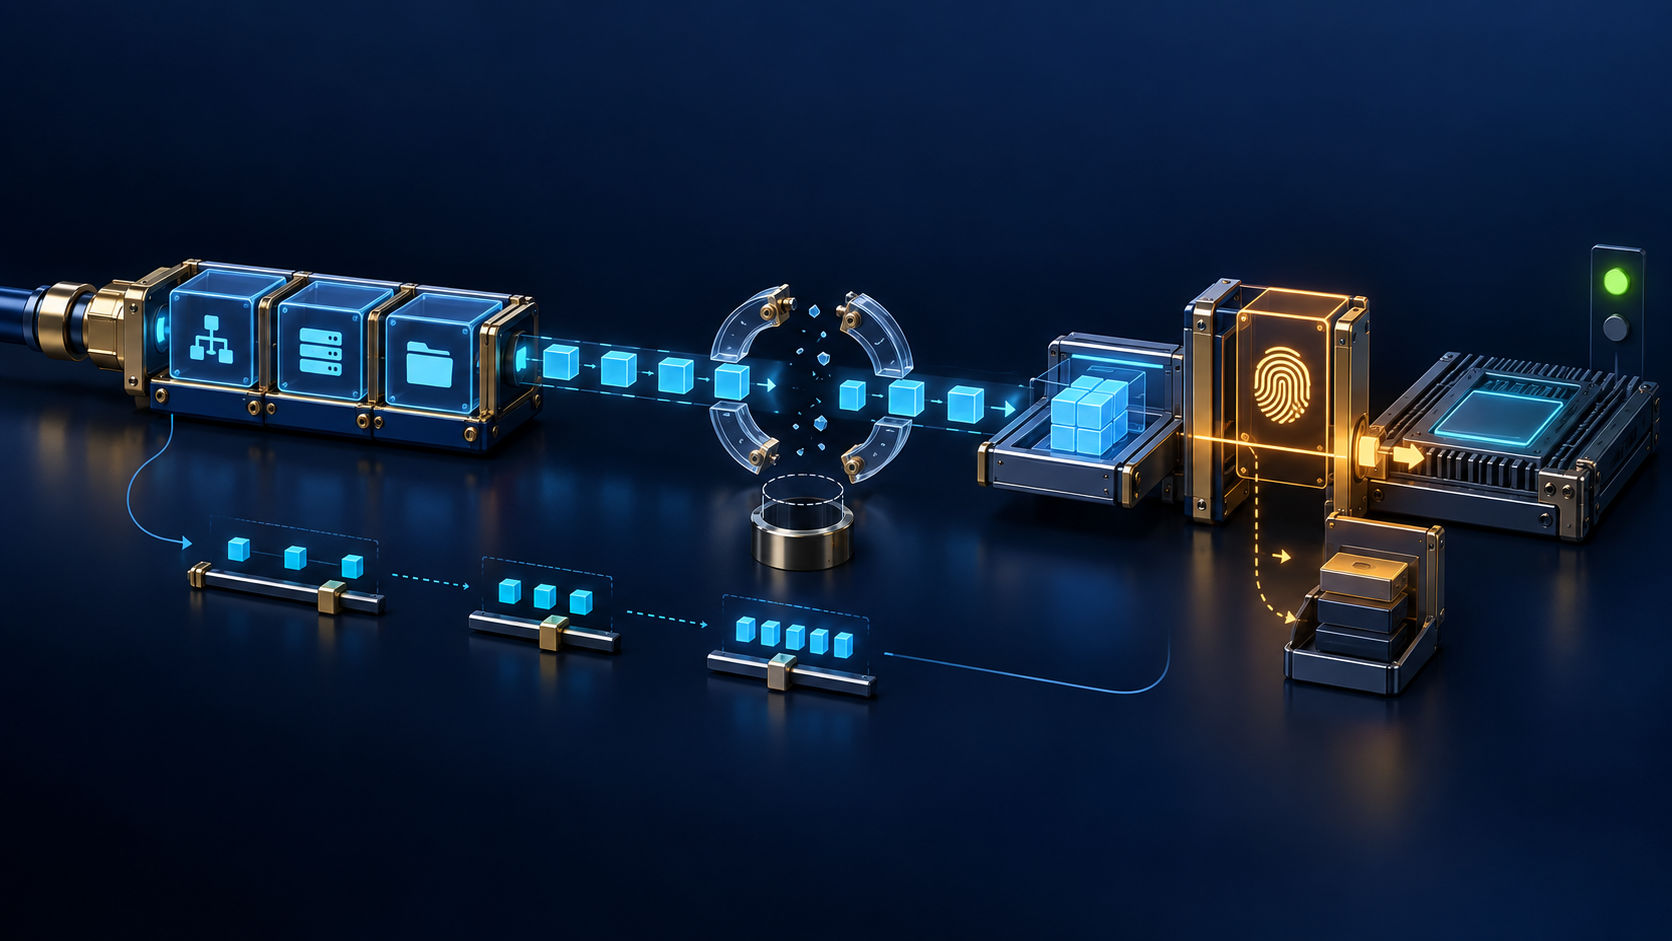
- A parsed URI, negotiated option, final ACK and successful boot belong to different evidence layers. TFTP itself supplies no access control, publisher authentication, confidentiality or inherent content-integrity proof.
The safest sentence in the document was the warning
A procurement inventory shows a neat value: tftp://boot.example/edge.img. The string parses. The scheme appears in the IANA registry. A compliance scanner recognizes the RFC. Those three facts can easily be promoted into one comforting word—standard—then promoted again into approved.
RFC 3617 refuses that promotion. Published in October 2003 as an Informational RFC, it says it does not specify an Internet Standard. Its introduction defines the URI because existing equipment and software need a common way to describe TFTP use, then strongly recommends against continuing that use. The standard name was intended partly to ease transition toward better transfer mechanisms.
That combination is not contradictory. Coordination sometimes has to describe a weak dependency before operators can find and remove it. A shared syntax helps an asset inventory distinguish a TFTP reference from an HTTP or FTP reference. It helps parsers expose the host, file and mode. It does not transform the referenced mechanism.
The distinction matters most when a label in a registry is consumed as an institutional blessing. IANA records the tftp scheme and points to RFC 3617. That entry proves a coordination act: this token has an identified specification and change-control lineage. It does not prove that a server exists, that a file is authorized, that the transport is protected, that a vendor conforms, or that a current deployment is safe.
The URI carries fewer facts than the dashboard suggests
RFC 3617 defines a compact grammar: tftp://, a host, a slash, a file and an optional ;mode= parameter. The permitted modes are netascii and octet; omission selects octet. The former mail mode was already deprecated and is not included.
Those fields describe how a client should approach a transfer. They do not carry an artifact version, expected length, digest, signer, approval ticket, expiry time, deployment ring or rollback slot. Even the apparent file path is a name interpreted by the server, not a portable proof of one immutable object.
Read and write are the two operations contemplated by the URI. That symmetry raises an authority question often hidden by boot-focused diagrams. A string that identifies a write target does not grant permission to write. Nor does a readable reference prove the requester was allowed to obtain the bytes. Access policy lives outside the syntax.
The RFC is explicit that existence and permissions cannot be determined before transfer through this interface. It also says files may fail to arrive intact and that reliability or completeness is not guaranteed. A parser can therefore accept a perfectly valid URI whose endpoint refuses the operation, returns different content, disappears behind a firewall or produces an incomplete stream.
netascii adds a representation boundary. The mode permits text-oriented conversion; the bytes on one side need not be identical to the bytes on the other. octet avoids that conversion but supplies no cryptographic commitment. Mode selection and artifact identity are separate decisions.
Protocol completion is not content truth
The base TFTP exchange in RFC 1350 uses read or write requests, numbered DATA blocks, acknowledgements and errors. This is sufficient for a small lock-step transfer. It is not sufficient to authenticate the publisher or bind the result to an approved software release.
A final ACK is evidence about a protocol conversation. It can show that the peer reached the expected terminal exchange for the observed blocks. It cannot show that the first block came from the intended origin, that an on-path party did not substitute content, that a local file name still maps to the approved image, or that the receiving process stored the bytes in the intended slot.
RFC 3617 lists the missing properties without euphemism. TFTP has no protocol access control, no protection against a man in the middle and no inherent integrity check. Transfers cannot resume from a midpoint. The original flow is lock-step, with one packet in flight, simple timeouts and no slow-start or sophisticated backoff. The protocol has no safe caching semantics and is poorly suited across administrative domains, where UDP handling, NATs and firewalls add more uncertainty.
The absence of a pre-transfer size also creates a resource boundary. Implementations must defend memory and disk limits rather than trust the name. A file called edge.img is not evidence that its length fits the target or that its declared purpose is honest.
Negotiation improves mechanics, not provenance
RFC 2347 lets a client append options to a read or write request. A supporting server can return an OACK containing the subset and values it accepts. Unsupported options can be omitted; the client and server then behave as though those options were never requested.
That makes OACK a useful receipt for negotiated mechanics. It should be recorded exactly because the requested configuration and the effective configuration can differ. But an OACK does not authenticate the server and does not validate the file. It says which parameters this peer accepted for this exchange.
RFC 2348 adds block-size negotiation. RFC 2349 adds timeout and transfer-size options. Knowing an expected size can prevent some capacity mistakes, and a suitable timeout can improve operation. Neither value is a content digest. A malicious or mistaken endpoint can state a plausible size for the wrong object.
RFC 7440 later adds a window-size option, permitting more than the original single-block lock step and improving throughput in suitable environments. Its security section still says the extension adds no security controls. Faster receipt of untrusted bytes does not reduce the provenance problem; it can enlarge the blast radius before an external verifier intervenes.
Bootstrapping makes the missing receipt more consequential
TFTP's historical attraction was small implementation cost. BOOTP and later DHCP environments could tell constrained machines where to obtain an initial file. Recovery networks and provisioning enclaves still value simple dependencies. The sources here establish that architectural lineage, not the prevalence or behavior of any named current product.
When the transferred object influences boot, the evidence gap expands. A successful download is followed by local storage, parsing, signature or hash validation if provided elsewhere, installation, selection of an activation slot, restart and observed runtime state. Each stage can fail after the previous stage reports success.
The dangerous shortcut is to attach the word “standard” to the first stage and let it authorize the rest. RFC 3617 supports the opposite conclusion. It standardizes the minimum common description precisely while exposing why local operators must own the surrounding safety decision.
A defensible receipt begins before the URI. It records who approved the artifact, its immutable digest and signer policy, the expected size, the intended device class and the rollback target. It then records the exact URI, DNS answer or literal address, network segment, server identity established by whatever external control exists, requested mode and options, accepted options, observed block and byte counts, independently verified digest, installation slot and post-boot measurement.
No field should be allowed to impersonate the next one. Registry presence is not endpoint authorization. Endpoint reachability is not artifact provenance. OACK is not integrity. Final ACK is not installation. A restarted device is not proof that it runs the intended image. A green service probe is not proof that every fleet member crossed the same chain.
Standardize the exit as carefully as the name
Replacement cannot be managed by deleting every tftp: value on sight. Some constrained recovery paths may be the only way to restore a device after the richer stack fails. The local risk owner must know which dependencies are ordinary provisioning, which are emergency-only and which have no tested substitute.
The migration record should therefore separate discovery, containment, replacement and retirement. Discovery finds every URI and server. Containment limits interfaces, clients, files and network reach. Replacement introduces an authenticated transfer and independently verified artifact pipeline. Retirement proves that devices no longer request TFTP in normal and recovery scenarios, then preserves a tested alternative.
Heng Lu's running-code discipline is useful here because it resists symbolic promotion. The RFC and registry provide a thin common language. The decision to accept a transfer remains local to the operator who bears the loss. Adoption is shown by deployed behavior, not by publication. Safety is shown by a chain of receipts, not by the familiarity of the scheme name.
RFC 3617 did not fail by registering tftp. It succeeded by making two truths visible at once: legacy behavior needed a common description, and a common description did not deserve trust.
Sources
- https://www.rfc-editor.org/rfc/rfc3617.html
- https://www.rfc-editor.org/rfc/rfc3617.txt
- https://www.rfc-editor.org/info/rfc3617/
- https://datatracker.ietf.org/doc/rfc3617/
- https://www.rfc-editor.org/errata_search.php?rec_status=0&rfc=3617
- https://www.rfc-editor.org/rfc/rfc783.html
- https://www.rfc-editor.org/rfc/rfc1350.html
- https://www.rfc-editor.org/rfc/rfc2347.html
- https://www.rfc-editor.org/rfc/rfc2348.html
- https://www.rfc-editor.org/rfc/rfc2349.html
- https://www.rfc-editor.org/rfc/rfc7440.html
- https://www.rfc-editor.org/rfc/rfc951.html
- https://www.rfc-editor.org/rfc/rfc2131.html
- https://www.rfc-editor.org/rfc/rfc3986.html
- https://www.rfc-editor.org/rfc/rfc7595.html
- https://www.iana.org/assignments/uri-schemes/uri-schemes.xhtml
- https://heng.lu/running-code-primary-the-patch-needed-to-preserve-the-internet-original-design/
- https://heng.lu/minimum-initial-specification-localized-future-decision-voluntary-adoption-internet-coordination-system/
- https://heng.lu/on-reality-layers-symbolic-power-and-why-clarity-feels-so-hostile/
- https://heng.lu/on-authority-belief-and-the-internets-addressing-system/
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance