
Summary
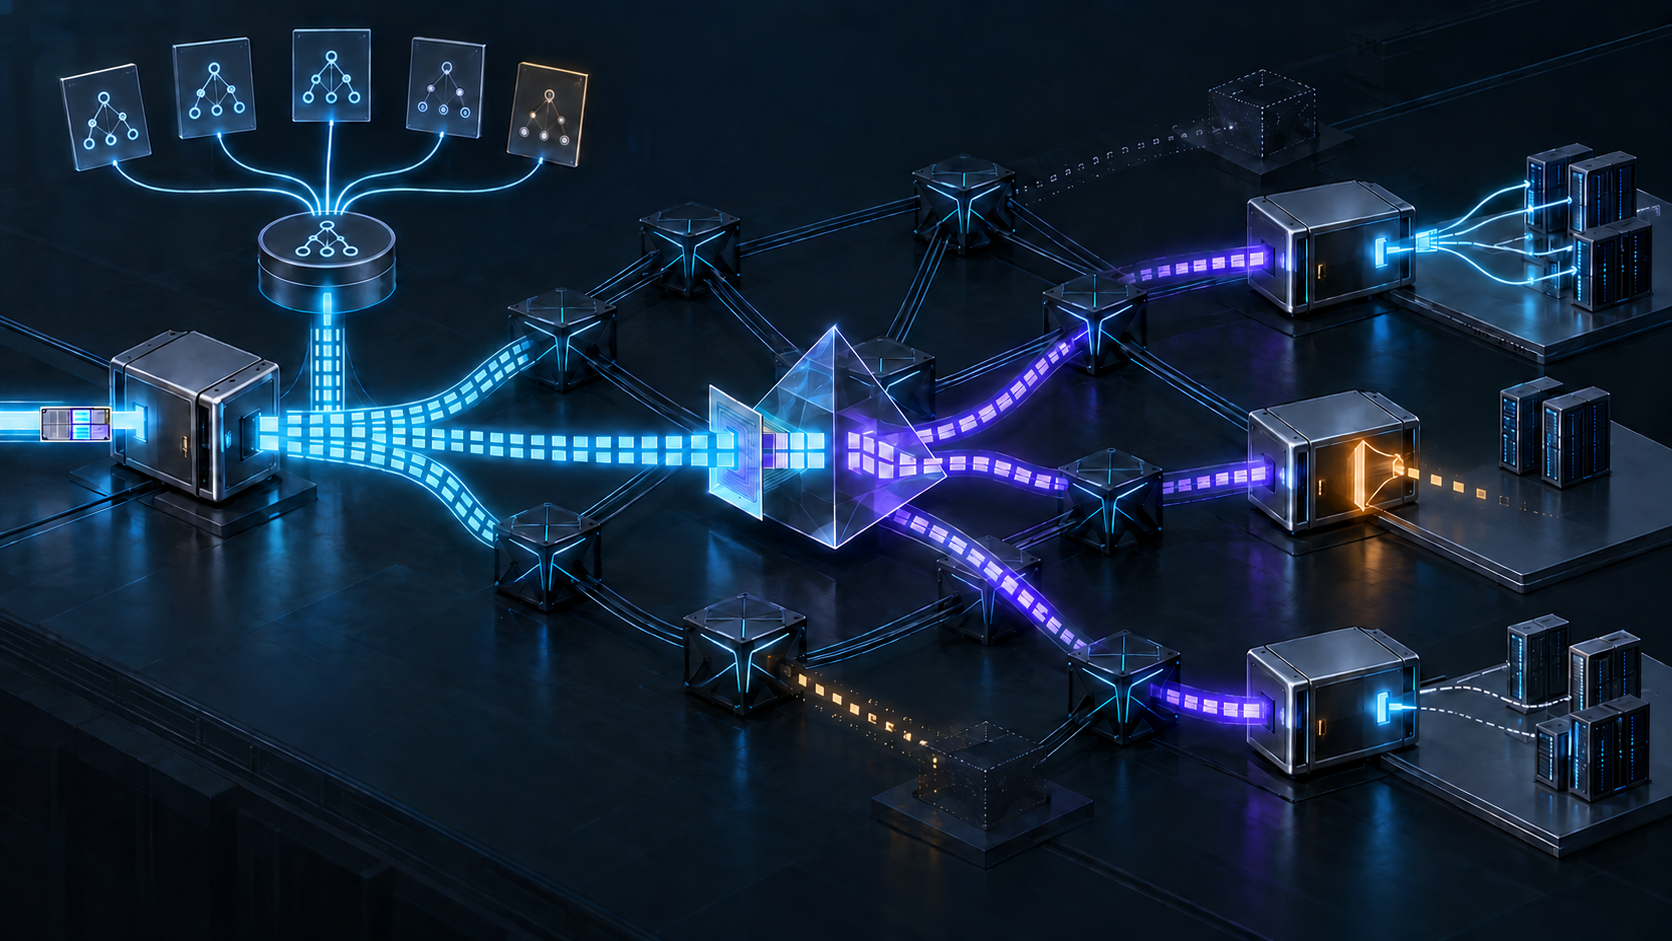
- RFC 9624 combines EVPN control-plane routes with BIER replication so an ingress PE can derive the BFERs intended to receive a BUM packet without intermediate routers holding per-flow multicast state.
- IMET, SMET, S-PMSI and Leaf A-D state can define an intended receiver set, while a PTA supplies tunnel, sub-domain, origin and payload context; neither layer proves that current customer membership or actual delivery matched that plan.
- Reliable operations need separate receipts for route epoch, packet classification, BFER-set derivation, imposed BitString, core replication, segmentation handoff, egress disposition, split-horizon decision, attachment-circuit transmission and customer reception.
The receiver set looked complete
An ingress PE held IMET routes for the broadcast domain. The relevant selective routes were present, the PMSI Tunnel Attribute named BIER, and every expected egress PE had a leaf-tracking route. The resulting BitString contained each intended BFER. On a control-plane screen, the replication plan was complete.
A customer site still missed the frame. The BitString could not say whether one route was stale relative to local membership, whether the ingress classified the packet under the intended rule, whether a core branch failed, whether a segmentation point rebuilt the downstream context correctly, whether the egress chose the expected broadcast domain, whether split horizon suppressed the wrong local copy, or whether the final attachment-circuit transmission succeeded.
RFC 9624 solves an important interoperability problem. It specifies how EVPN BUM procedures and BIER forwarding meet. Its precision should not be diluted by making a replication instruction speak as a delivery receipt. The intended set and the observed outcome occupy different layers.
BIER removes tree state, not the need for evidence
BIER forwards multicast through a domain without requiring intermediate routers to maintain per-flow multicast state or participate in an explicit tree-building protocol. A BFIR places the intended egress set into the BIER header, and BFRs replicate according to that encoding and the Bit Index Forwarding Table.
The architectural economy is real. It changes where forwarding intent is carried and avoids one class of state in the core. It does not make the core self-proving. A stateless intermediate hop can still discard a packet, use inconsistent forwarding information, encounter capacity pressure or send a copy onto the wrong next hop. The absence of per-flow state is an implementation property, not evidence of successful execution.
For an operational record, the relevant question is not merely whether the architecture needed a multicast tree. It is which BIER forwarding epoch each branch used, what copies were emitted, where loss or duplication occurred and whether the intended BFER observed the packet.
The PTA defines a forwarding context
The PMSI Tunnel Attribute identifies tunnel type 0x0B for BIER. Its tunnel identifier carries the sub-domain ID, the constructing router's BFR-id and its BFR-Prefix. Its label field carries an upstream-assigned MPLS label for EVPN-MPLS or a globally significant VNI or VSID for VXLAN, NVGRE or GENEVE. LIR and LIR-pF flags participate in leaf tracking.
Those fields bind a route to a forwarding context. They do not prove that all receivers interpret the context identically. The BFR-Prefix need not equal addresses in other route fields. Route Targets constrain distribution, and a BIER PTA must not escape the domain in which the BFR-Prefix uniquely identifies the originator. A syntactically valid advertisement outside the correct operational scope would not become safe merely because its fields decode.
Preserve the exact route, PTA bytes, Route Targets, origin, receiving peer and BIER-domain epoch. A rendered control-plane summary is too compressed to prove that the intended scope survived distribution.
Leaf tracking is a snapshot of intent
For an inclusive PMSI, the BFER set contains the originators of the other IMET routes for the broadcast domain. For selective operation, matching SMET routes or S-PMSI and Leaf A-D procedures can supply the leaves. The precise rule depends on whether selective forwarding applies to all flows, whether the LIR or LIR-pF flag is set and whether a corresponding SMET route substitutes for a Leaf A-D route.
The route set is therefore part of the forwarding decision, not background inventory. A late withdrawal can leave an unwanted receiver in one epoch. A delayed join can omit a receiver. Source and group matching can select a different leaf set from the operator's broad view of the broadcast domain. Route presence also says that a PE advertised interest under protocol rules; it does not prove that a customer port still had a listener when the packet arrived.
The receipt must capture the packet key and the exact leaf-tracking set used at decision time. Reconstructing the set later from current BGP state can silently replace historical intent with present state.
No matching leaves means no provider-tunnel transmission
RFC 9624 makes a negative branch explicit. If no route matches for transmission, the packet is not forwarded onto a provider tunnel. If the chosen tunnel requires leaf tracking and there are no leaf-tracking routes, the packet is also not forwarded onto a provider tunnel.
That outcome can be correct under the available state and still surprise the customer. A counter saying “zero BIER packets” cannot distinguish no incoming BUM traffic from a classification miss, absent transmission route, empty leaf set or a prior drop. Likewise, the existence of a route does not prove the packet matched it.
An ingress receipt should join frame identity, broadcast domain, packet type, source and group when applicable, transmission-route match, leaf-set result, interoperability choice under RFC 9251, imposed labels or VNI, BIER header and transmit result. Without that join, control-plane readiness and data-plane nonexecution are indistinguishable.
The BitString is an instruction created at one moment
The BFIR must know all BFERs that need the packet and derives them from the leaf-tracking routes. It then constructs the BIER header and sends the packet under RFC 8279 and RFC 8296 procedures. Protocol identifiers distinguish EVPN-MPLS from VXLAN, NVGRE and GENEVE payload forms.
A correct BitString proves that certain bit positions were requested under a particular sub-domain, set identifier and BitString length. It does not prove that the set contained every current receiver, that each bit mapped to the intended BFER under a consistent epoch, or that the corresponding branch completed. A packet can carry a perfect representation of stale intent.
This is the central evidentiary boundary. The bit is evidence of inclusion in the replication request. A BFER arrival record is evidence that a branch reached an endpoint. The two should share a correlation value but should never be collapsed into one status.
Segmentation creates a new decision boundary
A P-tunnel segmentation point is not a transparent wire. It receives a packet whose upstream encapsulation and label identify the route matched for reception. It has re-advertised that route into one or more downstream regions, each with its own PTA. For a downstream BIER region, it removes the upstream encapsulation, swaps the context label to the upstream-assigned label in the downstream PTA, derives the downstream leaves and imposes a new BIER header.
Every verb can succeed independently. The upstream packet can arrive while the downstream route is stale. The label swap can select the wrong broadcast domain. The local leaf set can omit a new egress. A new BitString can be valid within its region yet no longer represent the upstream service intent.
Treat the segmentation point as a custody transfer. Record upstream packet identity and context, reception time, matched route, removed fields, downstream region and epoch, replacement label, computed leaves, new BIER header and transmit results. End-to-end delivery cannot be inferred by checking only one side of the boundary.
Disposition still has to recover the right service
At an egress PE, the upstream-assigned label or VNI/VSID identifies the corresponding EVPN broadcast domain. Ordinary EVPN forwarding procedures then decide what happens next. Receipt at the BFER is therefore not yet receipt by a customer edge.
The egress can fail to map the context, reject the payload form, find no eligible local attachment circuit or encounter a local forwarding problem. Even a successful decapsulation and broadcast-domain lookup establishes only the next decision surface. A useful receipt records BIER decapsulation, payload protocol, label or VNI lookup, selected broadcast domain, local replication list, port transmissions and queue outcomes.
The distinction matters most when a BIER counter and an EVPN customer report disagree. Both can be accurate: the provider tunnel delivered to the PE, while the service disposition failed later.
Split horizon correctly suppresses some copies
Multihomed Ethernet segments make “not forwarded” ambiguous by design. For EVPN-MPLS, an upstream-assigned ESI label identifies the source segment so the receiving PE does not send the packet back there. For VXLAN, NVGRE and GENEVE, local bias uses the BFIR-id to recognize the ingress PE and avoid duplicate delivery to multihomed segments that ingress already served.
Suppression is part of correct forwarding, not necessarily loss. Yet a correct split-horizon mechanism can be misapplied if the BFIR identity, ESI label, multihoming state or Designated Forwarder context is wrong. One segment's intended suppression also does not prove that every other eligible local segment received a copy.
The evidence should name the segment, ingress identity, ESI or local-bias input, decision reason, suppressed port set and forwarded port set. Aggregate egress counts cannot distinguish correct loop prevention from accidental service denial.
Build the receipt chain from intent to reception
Start with the effective route epoch: IMET, SMET, S-PMSI and Leaf A-D records, Route Targets, PTA fields and BIER domain. Join the packet to the actual transmission rule and leaf set. Preserve the imposed BFIR-id, sub-domain, BitString parameters, protocol field, labels, VNI or VSID and any ESI context.
Then observe the forwarding chain. Relevant BFR or bounded fault-domain counters show replication. Segmentation points issue new custody records. Each BFER records arrival and decapsulation. EVPN disposition records broadcast-domain selection, local replication and split-horizon decisions. Attachment-circuit transmission and customer-edge reception complete the network portion. Application consumption and service outcome remain later facts.
RFC 9624 gives operators a precise way to construct the intended replication set. Its operational value increases when that set is preserved as the first receipt in a chain, rather than mislabelled as the final result.
Sources
- https://www.rfc-editor.org/rfc/rfc9624.html
- https://www.rfc-editor.org/info/rfc9624/
- https://www.rfc-editor.org/rfc/rfc9624.txt
- https://www.rfc-editor.org/rfc/rfc9624.xml
- https://datatracker.ietf.org/doc/rfc9624/
- https://datatracker.ietf.org/doc/rfc9624/history/
- https://www.rfc-editor.org/errata/rfc9624
- https://www.rfc-editor.org/rfc/rfc8279.html
- https://www.rfc-editor.org/rfc/rfc8296.html
- https://www.rfc-editor.org/rfc/rfc7432.html
- https://www.rfc-editor.org/rfc/rfc8365.html
- https://www.rfc-editor.org/rfc/rfc8556.html
- https://www.rfc-editor.org/rfc/rfc9572.html
- https://www.rfc-editor.org/rfc/rfc9251.html
- https://www.rfc-editor.org/rfc/rfc6514.html
- https://www.rfc-editor.org/rfc/rfc8534.html
- https://www.rfc-editor.org/rfc/rfc8926.html
- https://www.iana.org/assignments/bgp-parameters/bgp-parameters.xhtml
- https://heng.lu/running-code-primary-the-patch-needed-to-preserve-the-internet-original-design/
- https://heng.lu/minimum-initial-specification-localized-future-decision-voluntary-adoption-internet-coordination-system/
- https://heng.lu/on-reality-layers-symbolic-power-and-why-clarity-feels-so-hostile/
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance