
Summary
- RFC 9533 creates one OWAMP or TWAMP micro session for every physical member of a Link Aggregation Group; a bundle-level address and five-tuple do not prove that every member was measured.
- TWAMP's Sender and Reflector Micro-session IDs are locally scoped join keys. Each endpoint must correlate them with the physical member that actually received the packet and discard a mismatch.
- A validated probe can support performance-based steering, but it does not prove that production traffic used that member, that a controller acted, or that the service result improved.
One green bundle, four different links
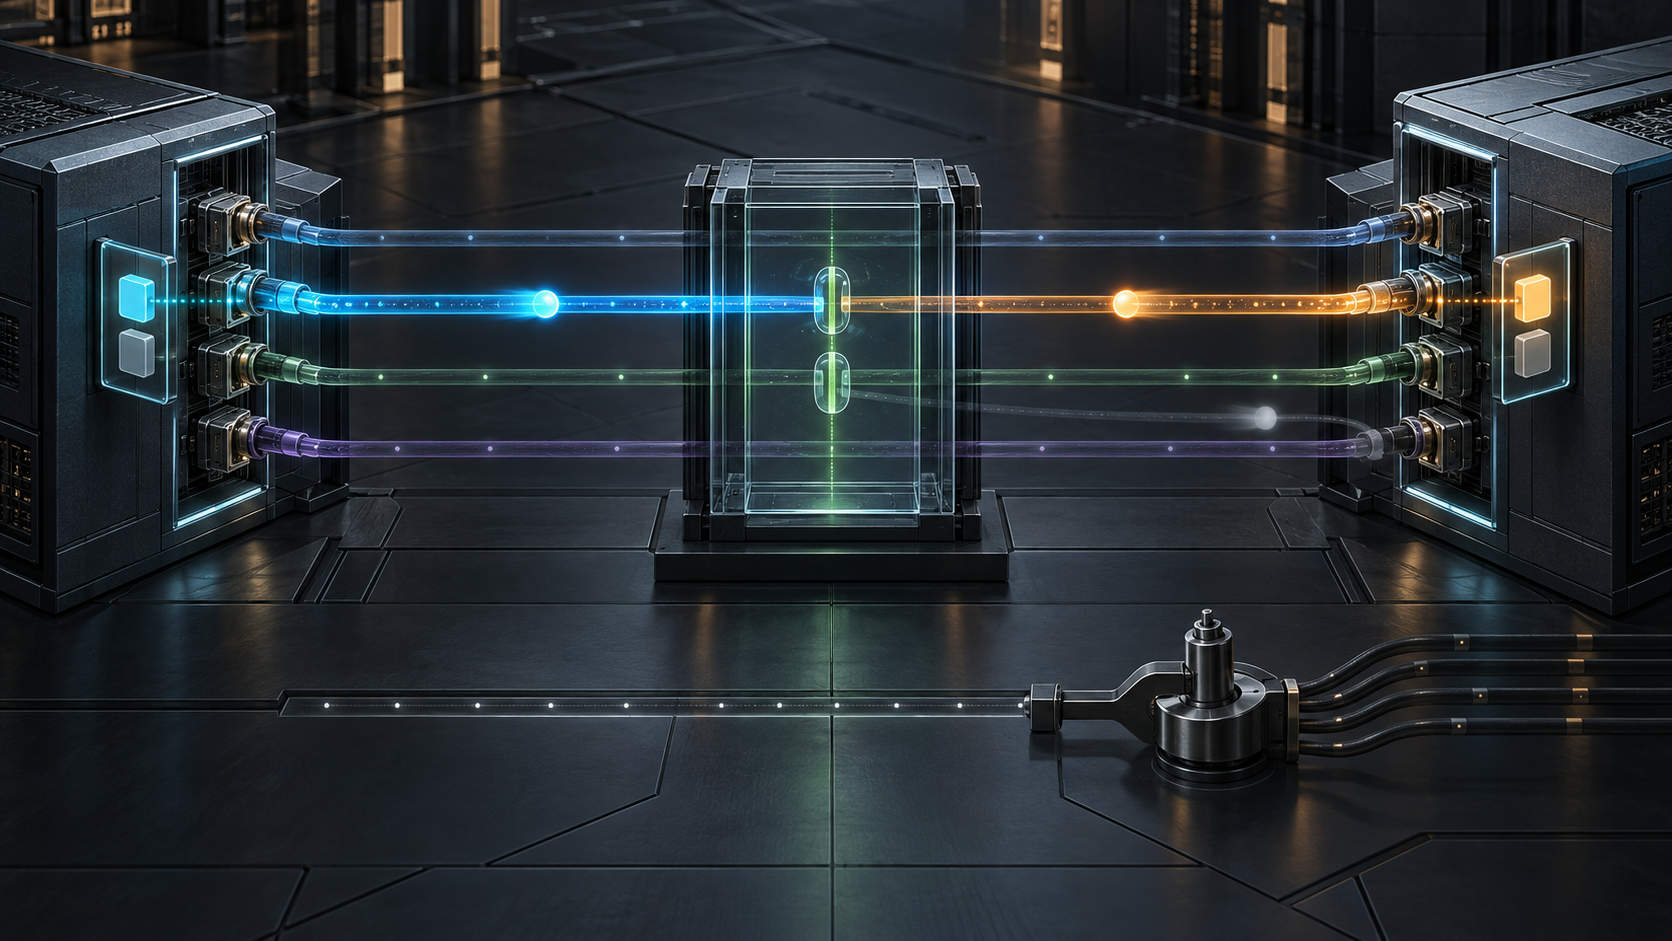
A Link Aggregation Group presents several physical links as one logical interface. That abstraction supplies capacity and resilience, but it also removes detail. Hash-based distribution can send different five-tuples to different members, and members in a wide-area design can traverse paths with different delay, loss and jitter. A single green number for the bundle may therefore describe one fortunate member while another degrades.
Ordinary OWAMP or TWAMP testing does not repair the ambiguity by itself. One fixed five-tuple can select one member. Varying fields can sample some members and yield an average, but the average does not enumerate what was tested. RFC 9533 makes the missing unit explicit: a micro session is an OWAMP or TWAMP session associated with one LAG member, and a complete test creates one for every member.
All those sessions can share the same sender and receiver IP addresses. They may use different UDP port pairs, but the RFC recommends a common pair because it is operationally simpler. The decisive difference is not the outer IP identity. It is the recorded association between a session and a physical member.
The request creates a set, not a convenient sample
The Control-Client sends Request-OW-Micro-Sessions, command 5, or Request-TW-Micro-Sessions, command 11. If the Server accepts, it builds a set of sessions for all members of the LAG on which the request arrived. IANA records those command numbers, but the registry entry is merely vocabulary. It does not show that a named server accepted a request or covered the full current member set.
That distinction matters during failure. Suppose a four-member LAG returns results for three sessions. A dashboard can average the three and look clean. The missing fourth result may be the most important fact: the session was never created, its packets were discarded, or the member mapping changed. Assurance must retain the requested set, accepted set, current inventory and result set separately. Silence is not a zero-loss sample.
Micro OWAMP uses the receiving member itself as the correlation key. The sender must transmit on the member associated with the session. The receiver observes the member on which the packet arrived and finds the matching micro session. If no session exists, the packet is discarded. The port observation is part of the receipt; the five-tuple alone cannot replace it.
Two identifiers because each end owns a different fact
Micro TWAMP adds two 16-bit fields. The Sender Micro-session ID identifies the sender-side member and must be unique within the TWAMP session at the sender. The Reflector Micro-session ID does the corresponding job at the reflector. Neither rule promises global uniqueness or permanence. An ID has meaning only with its endpoint, parent session and effective interval.
The asymmetry is deliberate. The sender may know its own member mapping but not the reflector's. In that case it initially puts zero in the Reflector field. It may later learn the remote value from configuration or from a reflected packet. RFC 9533 does not define that learning mechanism. A record that merely says reflector-id=0 must therefore preserve “not supplied for validation,” rather than inventing a remote link identity.
When a packet arrives, the reflector first uses the actual receiving member to correlate it to a micro session. No session means discard. If the Reflector ID is nonzero, the reflector checks that it names the member on which the packet arrived; a mismatch also means discard. In its response, the reflector copies the Sender ID and supplies the ID associated with its own member.
The sender performs the mirror test. It correlates the reflected packet using the physical member on which it arrived, validates the copied Sender ID, and checks the Reflector ID as evidence of reflector behavior. Failure at any step discards the packet. The accepted timing or loss sample therefore sits behind two independent mappings and two observed member interfaces.
The receipt is narrower than the action
A valid round trip can establish that one probe exchange was associated with the expected members under the session state then in force. It cannot establish that a production flow followed the same member. Production hashing can use a different tuple. Nor does the sample show that a controller consumed the result, chose a policy, installed a new selection, or improved user experience.
RFC 8668 can advertise member-link attributes for steering, but advertisement and measurement remain separate inputs. The responsible evidence chain is longer: inventory named the member; control created the session; packet reception verified the member; measurement produced a sample; policy evaluated freshness and thresholds; a controller requested a change; the device installed it; and subsequent traffic showed the outcome.
This separation also limits the meaning of security. RFC 9533 relies on OWAMP and TWAMP security and adds no new mechanism. An authenticated packet can protect parts of the exchange, but authentication does not make a stale member mapping current or prove that a locally scoped ID survived a hardware replacement. Configuration custody still matters.
A minimum evidence ledger
For each sample, retain the LAG identity and inventory version; both endpoint identities; the accepted control request; expected member count; parent session; sender and reflector IDs; whether the remote ID was configured, learned or zero; actual transmit and receive members; validation results; discarded-packet reason; timestamps and error estimate; metric result; and freshness deadline. For automation, add policy version, decision, requested change, acknowledgement, installation evidence and post-change observation.
This ledger reveals three different failures that a single red tile would merge. A performance failure is an accepted sample beyond a threshold. An evidence failure is a packet discarded because the session or member binding did not validate. A coverage failure is an intended member with no usable micro session. They demand different responses.
Sources
- RFC 9533 information
- RFC 9533 HTML
- RFC 9533 text
- RFC 9533 XML
- IETF Datatracker record
- IETF Datatracker API record
- RFC 4656: OWAMP
- RFC 5357: TWAMP
- RFC 8668: L2 bundle member attributes
- RFC 7799: measurement methods
- IANA OWAMP parameters
- IANA TWAMP parameters
- Heng Lu: Reality Layers
- Heng Lu: Running-Code Primacy
- Heng Lu: Minimum Initial Specification
Sources
- https://www.rfc-editor.org/info/rfc9533
- https://www.rfc-editor.org/rfc/rfc9533.html
- https://www.rfc-editor.org/rfc/rfc9533.txt
- https://www.rfc-editor.org/rfc/rfc9533.xml
- https://datatracker.ietf.org/doc/rfc9533/
- https://datatracker.ietf.org/api/v1/doc/document/rfc9533/
- https://www.rfc-editor.org/rfc/rfc4656.html
- https://www.rfc-editor.org/rfc/rfc5357.html
- https://www.rfc-editor.org/rfc/rfc8668.html
- https://www.rfc-editor.org/rfc/rfc7799.html
- https://www.iana.org/assignments/owamp-parameters/owamp-parameters.xhtml
- https://www.iana.org/assignments/twamp-parameters/twamp-parameters.xhtml
- https://heng.lu/on-reality-layers-symbolic-power-and-why-clarity-feels-so-hostile/
- https://heng.lu/running-code-primary-the-patch-needed-to-preserve-the-internet-original-design/
- https://heng.lu/minimum-initial-specification-localized-future-decision-voluntary-adoption-internet-coordination-system/
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance