
Summary
- RFC 5401 makes reliable multicast scalable by letting receivers request missing material while suppressing redundant requests from peers with overlapping needs.
- A quiet NACK channel is intentionally ambiguous: a receiver may be complete, waiting, suppressed, late, disconnected or unable to return feedback.
- Leaders need separate receipts for intended membership, detected loss, repair transmission, local reconstruction and application acceptance before reporting group completion.
The dashboard ended the story too early
The sender had an attractive fact: it had heard no new negative acknowledgements. It also knew that its current repair queue was empty. Those facts justified reducing transmission work. They did not justify the sentence “all recipients have installed the release.”
RFC 5401, published in November 2008 as a Standards Track specification, describes building blocks for multicast negative-acknowledgement repair and obsoletes the experimental RFC 3941. Its central economy is simple. Receivers normally stay silent when data arrives correctly. A receiver that detects a gap begins a NACK cycle. It waits for a randomized interval, listens for equivalent requests from others and may suppress its own feedback when someone else has already described enough repair to cover its need.
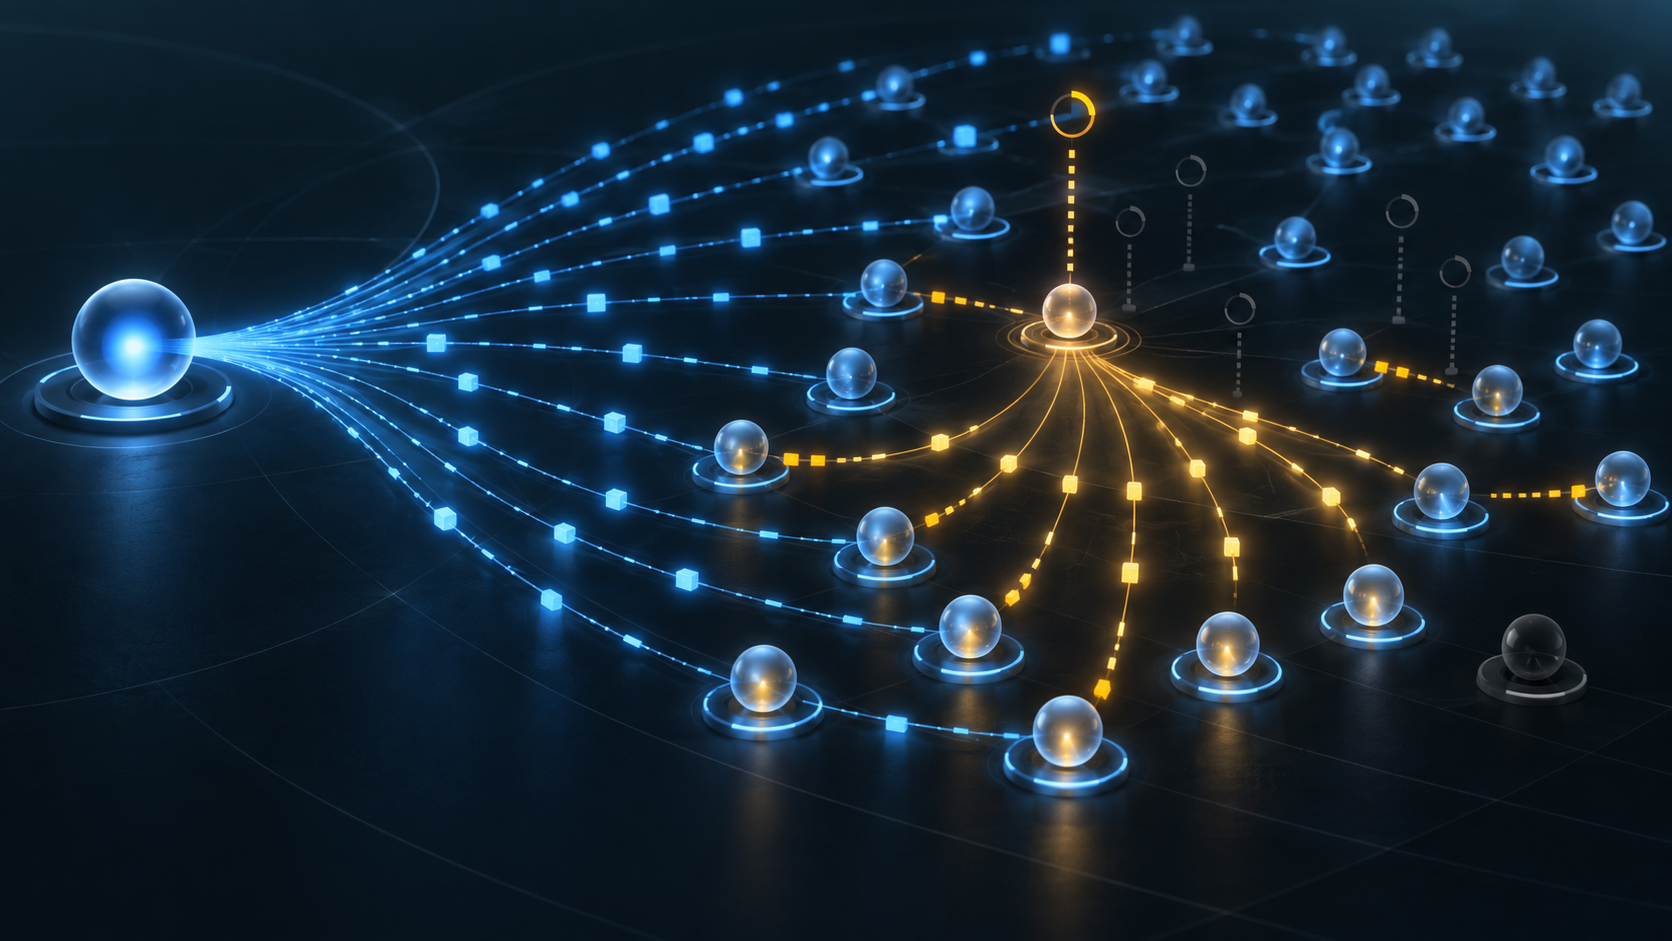
This prevents thousands of receivers from sending the same complaint at once. It also destroys any safe one-to-one mapping between silence and satisfaction. Ten silent receivers may represent ten completed objects. They may instead represent one early NACK and nine suppressed NACKs. Some may still be counting pending repair, some may have joined late, and one may have sent a NACK that never reached the sender.
The ambiguity is not a flaw hidden in the standard. It is the mechanism that makes the system usable at group scale. Trouble begins when an operating report treats a deliberately compressed feedback channel as a complete census.
Suppression is evidence of coordination, not completion
On detecting missing content beyond material already expected, a receiver records the sender's transmission position and starts a backoff timer. Recording that boundary matters because packets arriving during the wait should not erase the context in which the repair decision began. The receiver also retains enough content history to determine what remains missing.
During backoff, another receiver may send a NACK first. If that request supersedes the local repair need, the later receiver can suppress its own message. A sender may reinforce this process by forwarding repair state. Observed sender rewind or repair behaviour can also tell receivers that the missing region is already being addressed.
None of those observations says the later receiver has received the repair. They say that another request would be redundant at that moment. After repair traffic arrives, the receiver may still lack enough symbols. It can begin another cycle. RFC 5401 explicitly allows repair to converge over repeated rounds; NACK transmission itself need not be made perfectly reliable when the overall design can recover in later cycles.
That distinction should appear in telemetry. “NACK suppressed” is a state transition. “Repair heard” is another. “Object reconstructed” is a third. Combining them into one green status discards the very evidence needed to explain long tails and partial failure.
A lost complaint is indistinguishable from no complaint
Negative feedback reduces routine traffic by speaking only about absence. But absence is hard to observe from the sender. If a receiver loses data and its NACK is also lost, the sender sees exactly the same quiet interval it would see if nothing were missing.
Repeated cycles improve the chance of convergence. They do not turn one silent window into a receipt. Timer expiry, retained history and subsequent repair opportunities let a receiver ask again. Whether those opportunities continue long enough depends on the protocol instantiation, object lifetime, session policy and the receiver's ability to remain connected.
Operators therefore need to distinguish a transport design that is expected to converge from an assertion that a particular receiver has converged. The first is a property of mechanisms and parameters. The second requires receiver-side evidence or a deliberately defined group policy that accepts less than universal confirmation.
The same discipline applies when the sender transmits repair proactively. A repair packet leaving the sender proves only that the sender emitted it. Network delivery, local reconstruction and application action remain downstream events. A single “repair complete” timestamp cannot honestly represent all four.
FEC makes repair broader, not self-certifying
Forward error correction can make one repair transmission useful to receivers that lost different source packets. Instead of retransmitting each exact packet for each complaint, a sender can provide encoding symbols that allow different receivers to fill different erasure patterns. RFC 5052 supplies a broader FEC framework for content delivery, and RFC 5401 incorporates this economy into its discussion of repair needs.
The gain is real: fewer individualized retransmissions, better use of multicast and less pressure on the feedback channel. Yet a count of parity symbols sent is not a count of objects reconstructed. Receivers began with different loss histories. One may have enough symbols after the first repair, another after the third, and a late participant may not possess the source symbols assumed by the current coding block.
A receiver should account for repair already planned before requesting more, otherwise it can overstate need and defeat suppression. That optimisation again introduces an intermediate state: repair expected but not yet usable. If a dashboard labels expected symbols as recovered content, it moves the success boundary upstream for visual convenience.
FEC also does not supply congestion control by itself. RFC 5052 says compatible congestion control belongs in a complete delivery system. RFC 5651 makes the same separation in its LCT building block. Repair efficiency, network fairness and application completion are linked concerns, but one control cannot stand as proof for the others.
Timer tuning is a decision about latency
Randomized backoff creates room for early feedback to suppress later duplicates. Longer windows can reduce feedback density in a large group because more receivers have time to hear a representative NACK. The cost is additional repair latency and more buffering at sender and receivers.
RFC 5401 uses estimates such as group size and the group's greatest round-trip time to adapt those timers. These are operating estimates. They cannot certify that the system knows every member, has reached the farthest member, or has included a temporarily silent receiver. A stale group-size estimate can produce excessive feedback or needlessly slow recovery. An underestimated round-trip boundary can cause avoidable duplicates; an overestimate can delay useful requests.
The correct dashboard therefore exposes the parameters and their uncertainty. It should show estimated group size, timing basis, backoff distribution, suppression count, repair rounds and age of the estimates. A single percentage called delivery confidence hides whether the system became quiet because it was efficient or because its feedback window excluded the weak edge.
This trade-off is organisational as well as technical. Product teams may optimise for a fast median. Reliability teams care about the long tail. Network teams must keep repair compatible with congestion control. Customer operations need to know when a receiver is too late or too poor to remain in the primary group. Timer values encode how those interests were balanced.
Membership is a policy surface
Multicast receivers can join late, leave and rejoin. A receiver visible during the final interval may lack data sent before it arrived. A receiver counted at the start may disappear before reconstruction. The sender cannot infer a stable denominator merely from current feedback.
Some applications can proceed when a threshold or selected set has completed. Others must follow the weakest member. RFC 5401 leaves that completion policy to the protocol and application instantiation. It also acknowledges that persistently poor receivers may be excluded or moved to another delivery group.
That means “all” is not a packet counter; it is a governance decision. Which receivers were intended? When was membership sampled? Are late joiners owed the full object? How long may a disconnected member retain its claim? Who authorises exclusion, and where is that decision recorded? Does migration to a slower group count as success, deferral or failure?
Without explicit answers, a completion percentage can improve simply because the denominator shrank. The network may have behaved exactly as designed while the business report misstates who was served. A defensible system preserves the intended audience separately from the currently reachable set and records every policy-driven removal.
Build a receipt chain instead of one status light
A useful control model begins before the first packet. Record the intended receiver set or the rule that defines it, the content identifier and the sender's transmission position. At each receiver, preserve enough packet history to detect loss and distinguish missing content from repair already pending.
When a NACK cycle begins, capture its boundary and timer state. Record whether a local NACK was transmitted, suppressed because equivalent feedback was heard, or abandoned when the session changed. At the sender, keep the aggregation decision and the repair material emitted. At the receiver, distinguish repair arrival, successful reconstruction and application acceptance.
Only after those states exist can a group-level policy determine completion honestly. The policy may not require per-receiver positive acknowledgement; that would surrender much of NACK multicast's scaling advantage. It can use sampling, explicit critical-member receipts, exception queues or defined expiry rules. What matters is that the chosen approximation is visible and does not masquerade as protocol certainty.
NORM, specified in RFC 5740, demonstrates a complete protocol built from related mechanisms. Its transport state should still not be conflated with an application's acknowledgement that a release was installed, parsed or activated. Protocol completion and business completion need a documented bridge.
Uncertainty belongs in the report
These standards establish mechanisms, not current market share or a universal incident rate. They do not prove how a particular vendor exposes suppression, how often NACKs are lost, or which backoff setting is optimal for a given network. A production assessment must add implementation documentation, configuration, telemetry and receiver evidence.
The standards do establish enough to reject one tempting inference. A sender that hears no NACK has not, on that fact alone, learned that every receiver reconstructed the object. Any system making that claim has added an unstated completion policy.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance