
Summary
- A TLS 1.2 Finished message verifies the current handshake transcript under the negotiated secret; application data sent before a renegotiation is not thereby included in that proof.
- RFC 5746 binds a renegotiation to its predecessor with the previous client and server
verify_data. Applications still need separate receipts for principal changes, request boundaries, authorization and irreversible effects.
The handshake succeeded inside an older story
Imagine a server connection that already carries protected application data. A second ClientHello arrives. Certificates may change, fresh keys may be negotiated and a new Finished message may verify. The operator sees no TLS alert and records another successful handshake.
Which conversation did that handshake finish?
RFC 5246 gave Finished a precise job. Its verify_data depends on the master secret and the handshake messages seen by each side. If verification succeeds, the endpoints agree on the current negotiation and key schedule. That is strong cryptographic evidence. Yet application data is not part of that handshake transcript. A perfectly valid second handshake did not originally prove how the bytes sent before it were attached to the identity established after it.
This was not merely a philosophical gap. TLS renegotiation exposed a seam between protocol state and application interpretation. An intermediary could establish a TLS connection to a server, send an application prefix, and then splice a victim's new handshake onto that connection. The server could see authenticated renegotiation and treat the prefix plus the victim's later bytes as one request stream. Each local fact looked respectable; their composition was false.
Pending state is not a bound history
TLS 1.2 maintained current and pending connection states. Handshake messages prepared new algorithms, keys and secrets. ChangeCipherSpec caused a party to copy the pending state into the current state. The Finished message, protected under the new state, tested the handshake result.
That transition answers “which cryptographic state now protects subsequent records?” It does not answer “which earlier application bytes belong to the newly authenticated principal?” Nor does it tell an HTTP server, mail server or custom protocol how to handle a request whose framing crosses the boundary.
The distinction is easy to lose because the connection remains one socket. A socket is a transport container, not a single immutable authority. Within it, TLS state can change, peer credentials can appear or change, and application buffers can outlive the security state that existed when their first bytes arrived.
RFC 5746 supplied the missing backward link
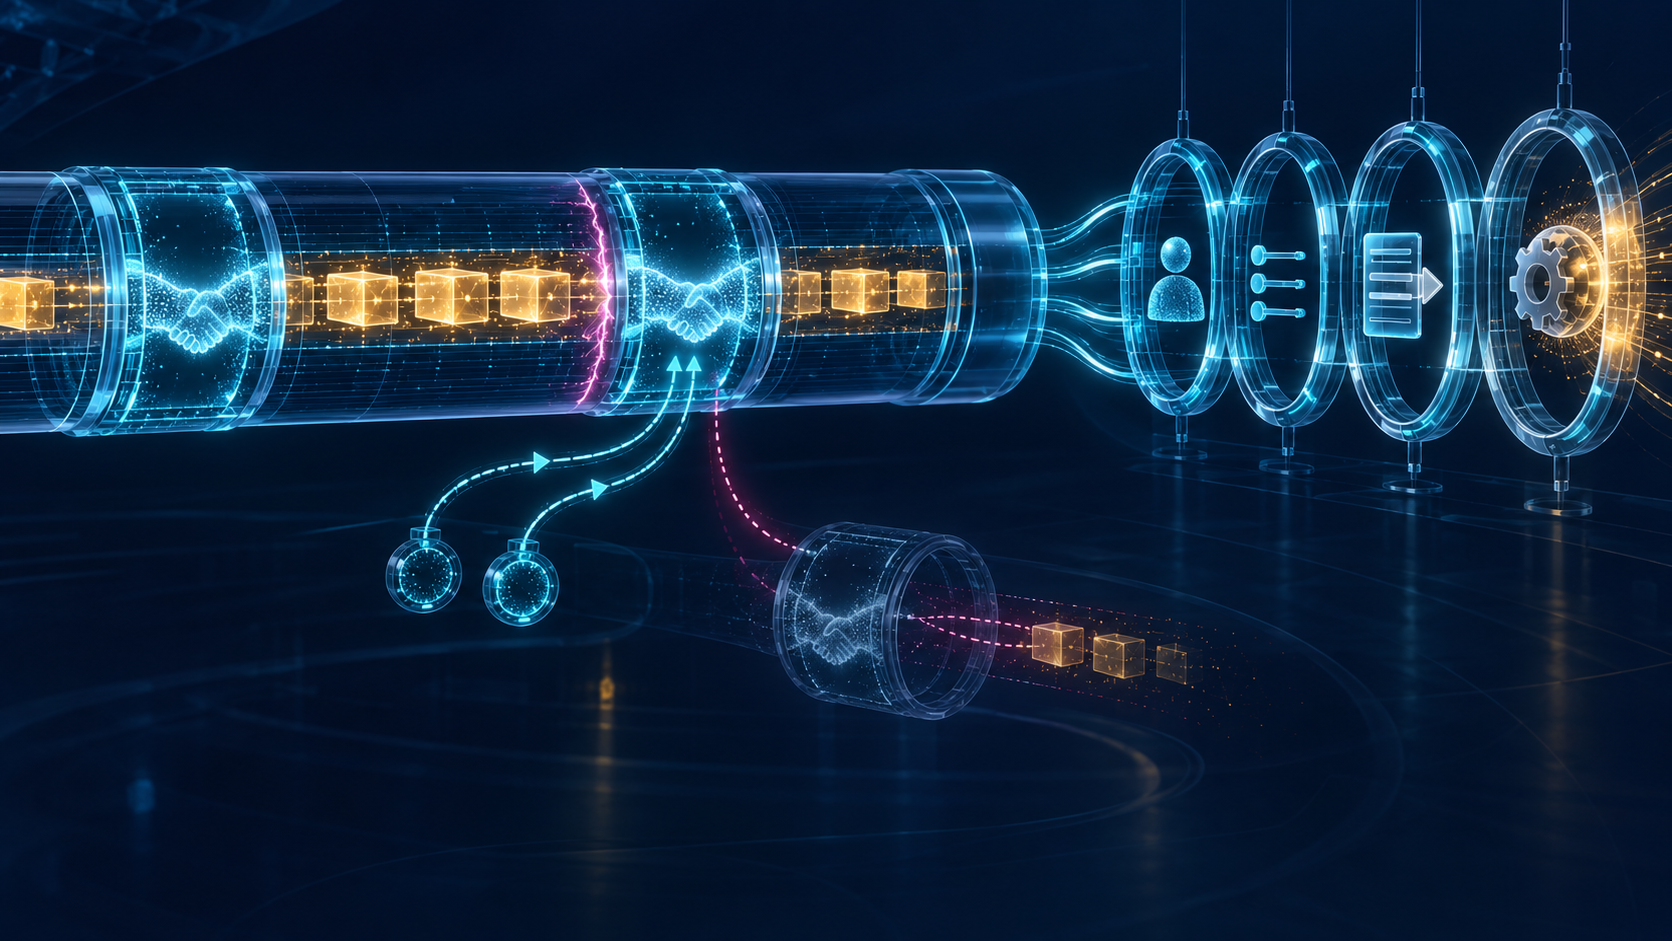
The secure-renegotiation update created an explicit binding. On an initial handshake, a client can signal support with the renegotiation_info extension or TLS_EMPTY_RENEGOTIATION_INFO_SCSV; the server replies with an empty renegotiated-connection value. During renegotiation, the extension carries the previous client and server Finished verify_data values.
The new handshake therefore does not merely finish on its own. It proves knowledge of values from the previous completed handshake. The server and client can reject a renegotiation whose claimed predecessor does not match the connection they actually hold.
That repair illustrates the power of a small protocol field. It converts continuity from an inference based on socket identity into a cryptographically checked relationship between two handshakes. It also demonstrates why the original Finished proof was bounded: if it had already covered the prior connection, no new binding value would have been necessary.
Support signaling, however, is not execution evidence. A library may recognize the extension while policy disables renegotiation. An endpoint may advertise the signaling cipher-suite value yet never perform a second handshake. An inventory record must distinguish implementation support, loaded policy, observed offer, peer response, actual renegotiation and validation of the previous verify_data.
A repaired channel still leaves an application seam
RFC 5746 binds TLS negotiations; it does not define the application's request parser. Suppose an anonymous client sends half a command, then completes certificate-authenticated renegotiation. Should the remaining bytes execute as the newly authenticated user? Should the buffered prefix be discarded? Must the application demand a new message boundary?
Those are authorization and framing decisions. If the TLS termination layer exports only “client authenticated,” an upstream application may inherit buffered work without knowing when the principal changed. The channel is securely continuous while the application authority remains ambiguous.
The safer model attaches a security-generation identifier and principal to every parsed request. A principal change should trigger an explicit policy: reject in-flight messages, complete them under the old identity, or restart framing under the new one. None of those choices can be inferred from Finished alone.
Extended Master Secret fixes a different bond
RFC 7627 later defined Extended Master Secret, deriving the master secret from a hash of the handshake transcript. It addresses session-hash and triple-handshake problems in which separate sessions could share key material under dangerous conditions.
That is not a substitute for RFC 5746. Extended Master Secret binds a master secret to its handshake. Secure renegotiation binds a new handshake to the previous connection through earlier Finished values. Both are cryptographic bindings, but they connect different objects.
Collapsing them into a generic “TLS hardening enabled” flag destroys diagnostic value. An audit should record whether secure renegotiation was negotiated, whether the extension carried the correct prior values, whether EMS was negotiated where applicable, and which application principal each generation produced.
TLS 1.3 removed the moving seam
TLS 1.3 no longer supports renegotiation. That design choice removes the specific in-connection second-handshake mechanism. It does not prove that an estate has migrated. RFC 9851's TLS 1.2 feature freeze likewise governs standards work, not the runtime state of endpoints.
An operator needs listener inventory, loaded version policy, observed handshakes, dependency ownership and service-level canaries. A TLS 1.3-capable endpoint may still negotiate TLS 1.2 with legacy clients. A proxy may terminate one version and open another upstream. Version support is a capability receipt, not a complete retirement receipt.
Build a conversation ledger
For TLS 1.2 endpoints that still allow renegotiation, retain a sequence rather than a final status: initial handshake identifier and Finished values; application-data ranges received under that generation; renegotiation trigger; secure-renegotiation signaling; prior-value comparison; new certificate path and peer result; ChangeCipherSpec activation; new Finished result; application principal mapping; request-parser boundary; authorization decision; operation commit and external outcome.
This ledger is BTW's operational analysis, not a logging format required by RFC 5246. Its purpose is to stop one strong receipt from impersonating every later receipt. If the TLS layer proves a bound renegotiation but the application cannot say which principal owned an in-flight request, the result is unknown—not authorized by default.
That is the reality-first lesson. A standard can repair a cryptographic relationship. A runtime can show that the repair executed. Only the application can explain how identity changed its decisions, and only the system of record can prove what became irreversible.
Sources
- RFC 5246, plain text, information record, Datatracker, history, errata and referenced-by record
- RFC 5746 and its information record; RFC 7627; RFC 5929
- RFC 8446; RFC 9325; RFC 7301; RFC 6066; RFC 5077
- RFC 2119; RFC Editor, What Is an RFC?; IANA TLS Parameters; RFC 9851
- Lu Heng: Reality, Not Advocacy, Running-Code Primacy and The Agency Problem
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance