
Summary
- RFC 3125 required a signer to bind a globally unique policy identifier and a hash of a definitive policy specification into the signature process, allowing a verifier to establish which exact policy bytes governed validation.
- Matching the signature and policy hash was not the end of the decision. Signing period, commitment type, certificate and revocation rules, timestamp and attribute trust, algorithm constraints, institutional recognition and transaction outcome remained distinct tests.
The signature had rules outside the signature value
An electronic signature can answer a narrow and powerful question: under a chosen algorithm and key, do these bytes verify? Business transactions ask more. Was the certificate acceptable for this purpose? Was the signature created in the permitted period? Did the signer claim approval, authorship or receipt? Was a timestamp required? Which revocation evidence counted? Was the algorithm still acceptable? Who was entitled to recognize the result?
RFC 3125, published as Experimental in September 2001, treated those questions as a signature policy. The policy was a set of rules for creation and validation under which signature validity could be determined. A legal or contractual context might recognize a particular policy as satisfying its requirements. The careful verb was “might.” Publication of the RFC did not grant legal force to every policy built with its vocabulary.
The document named several authorities: a Signature Policy Issuer, the signer, one or more verifiers, an arbitrator and supporting trust-service providers. The issuer defined technical and procedural requirements for a business need. The signer committed to a referenced policy. The verifier had to validate under it. An arbitrator could later repeat verification in a dispute. These roles shared an artifact without merging their authority.
An OID pointed to rules; it was not the rules
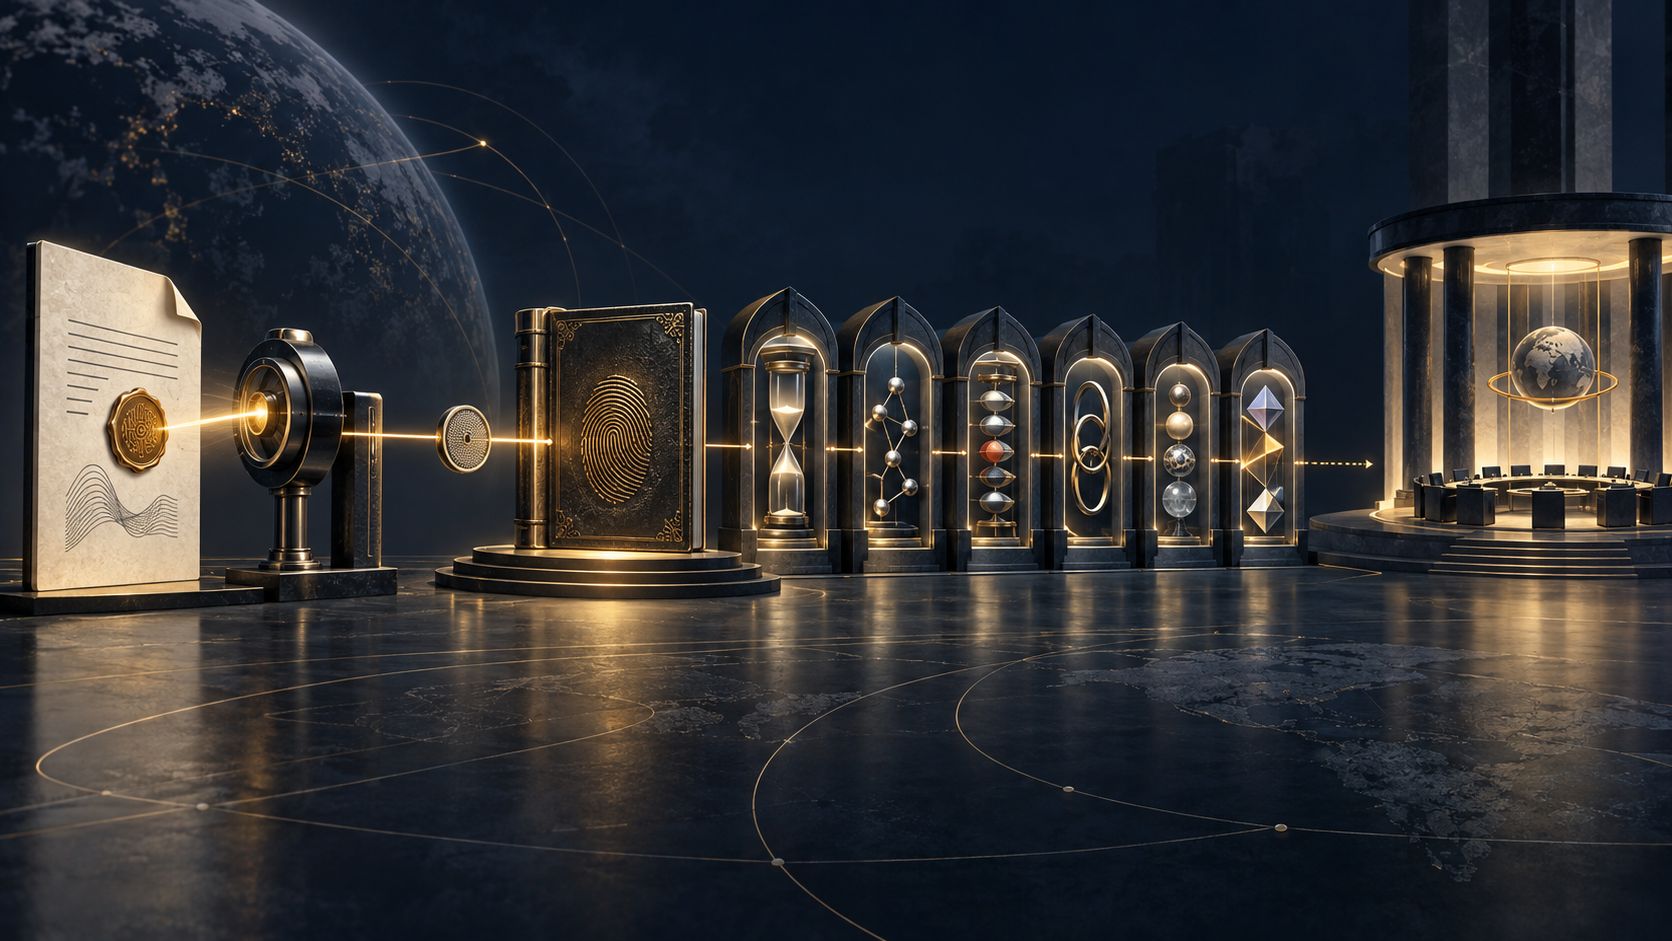
RFC 3125 required the referenced policy to be identifiable by an Object Identifier. It also required a policy specification to exist and one definitive form to possess a unique binary encoding. The signer supplied a hash of that definitive specification with an agreed algorithm; the verifier checked it.
This chain addressed a real ambiguity. A name such as “invoice signature policy” could acquire several editions, summaries or translations. An OID could select an identity, while the hash could bind the transaction to exact definitive bytes. In the optional ASN.1 representation, DER supplied deterministic encoding for the structured form.
But an OID is a reference, not an approval seal. A matching hash establishes that verifier and signer are referring to the same encoded policy specification. It does not show that the issuer was entitled to govern this transaction, that an employee followed an off-system ceremony, or that a court or trading partner recognizes the policy. It solves identity and integrity at one layer.
The document therefore required a human-readable form as well as allowing a machine-processable one. Software could apply rules. People and institutions still had to assess whether those rules met the legal or contractual need.
One policy could contain several kinds of validity
The structured validation policy began with a signing period, common rules and commitment rules. The signing period named a not-before time and an optional not-after time for creating signatures. A cryptographically correct signature outside that period could remain mathematically correct while failing the policy's creation rule.
Common rules could define signer and verifier duties, certificate trust, timestamp trust, attribute trust, algorithm constraints and extensions. Commitment rules could supply these conditions for a selected kind of commitment. A policy might treat approval differently from receipt, or rely on message semantics when no explicit commitment type was present.
This made the meaning of “valid” conditional. First the verifier needed the correct policy edition. Then it needed the applicable commitment rule. A signature could satisfy one commitment type and not another. The same key and content might be acceptable before an algorithm deadline and unacceptable after it. A certificate chain trusted for one field of application might not be trusted for another.
The framework did not make these distinctions subjective noise. It made them explicit inputs to processing. That was a form of automation, but not automation of the entire institution.
Trust providers supplied evidence, not one universal verdict
RFC 3125 listed certification and registration authorities, repositories, timestamp authorities, certificate-status responders and attribute authorities among the supporting providers a policy could use. A certificate trust tree could name trust points and constrain path length, certificate policies, names and policy processing. Revocation requirements could identify the evidence needed. Timestamp and attribute rules could select their own trust conditions.
Each service answered a bounded question. A certificate connected a key with an asserted identity under an issuer. A status response described certificate status within its model and time. A timestamp attested that data existed before a reported trusted time. An attribute authority supplied role or attribute evidence. None alone selected the transaction's commitment type or proved business authority.
The policy assembled these receipts. The verifier still needed to retain which receipt was used, from which provider, under which time and rule. A green result with no policy OID, definitive-policy hash, commitment rule or validation inputs would be difficult to reproduce in a later dispute.
Procedure could extend beyond what software observed
The policy issuer could define technical and procedural requirements. Some were directly testable in a CMS signature: required signed attributes, unsigned attributes, certificate references and certificate material. Others might concern human handling, key custody or organizational approval.
A matching policy hash proves that the rulebook was identified. It does not prove every procedure in the rulebook occurred. That evidence may live in key-management records, approval systems, training controls or witness logs. RFC 3125's signer representation—that the data was signed under the policy—was a commitment, not omniscient telemetry.
This gap is where careless audit language becomes dangerous. “Signature valid under OID X” should mean the verifier ran a stated policy implementation against stated evidence at a stated time. It should not silently become “the signer had authority,” “the counterparty accepted,” or “the contract was performed.” Those are later decisions with different owners.
Algorithms made policy validity historical
The security considerations emphasized private-key protection and declining algorithm strength. Implementations were advised to be modular because mandatory algorithms could change. A policy could also constrain algorithms and key lengths.
Validity was therefore time-sensitive in two ways. The signature had a creation time and evidence history; the policy and relying context also had evolving views of acceptable cryptography. A later verifier might need to know which rule version applied at signing, what timestamp evidence existed, and whether an algorithm transition was prospective or retrospective.
RFC 3126 addressed long-term electronic signature formats and RFC 3161 specified timestamp protocol evidence. RFC 2630 and RFC 2634 supplied CMS and S/MIME security-service context; RFC 2459 and RFC 2560 supplied the contemporary certificate and status setting. These sources explain the components around the policy. They do not prove that a named RFC 3125 policy was deployed.
Experimental publication was not a deployment receipt
RFC 3125 defined an experimental framework and optional ASN.1 format. Its conformance statement required signer and verifier systems to process a signature according to the policy identified by OID. That is a protocol obligation for conforming participants, not a census of participants.
Later PKIX and CMS specifications, including RFC 5280 and RFC 5652, help a modern reader understand the lineage of certificate and signed-data processing. They must not be projected backward as evidence that implementations in 2001 followed RFC 3125 or that one legal regime adopted it.
A responsible history records what the document made possible: explicit policy identity, exact policy-byte binding and machine-readable rule families. Adoption, interoperability, legal recognition and dispute outcomes need separate records.
The complete receipt had several signatures of its own
A reproducible decision would preserve the signed object, signature bytes, signer certificate, policy OID, definitive policy representation, policy hash and algorithm, issue date, signing period, selected commitment rule, certificate path, revocation material, timestamps, attributes, algorithm constraints, verifier software and time. It would then add the external instrument—contract, regulation or agreement—that recognized the policy.
Even that would not prove performance of the underlying transaction. Delivery, acceptance, payment, fulfillment and adjudication remain downstream events.
RFC 3125's historical contribution was to refuse a false binary. A signature was not simply valid or invalid in the abstract. It was verified under a particular policy, with particular evidence, for a particular commitment and context. The cryptography closed one equation; the policy stated which equation mattered.
Sources
- https://www.rfc-editor.org/rfc/rfc3125.txt
- https://www.rfc-editor.org/info/rfc3125
- https://datatracker.ietf.org/doc/rfc3125/
- https://www.rfc-editor.org/rfc/rfc3126.txt
- https://www.rfc-editor.org/rfc/rfc2630.txt
- https://www.rfc-editor.org/rfc/rfc2634.txt
- https://www.rfc-editor.org/rfc/rfc2459.txt
- https://www.rfc-editor.org/rfc/rfc2560.txt
- https://www.rfc-editor.org/rfc/rfc3161.txt
- https://www.rfc-editor.org/rfc/rfc2119.txt
- https://www.rfc-editor.org/rfc/rfc5280.txt
- https://www.rfc-editor.org/rfc/rfc5652.txt
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance