
Summary
- RFC 9730 describes coexistence between distributed GMPLS control and centralized controller systems. It does not replace one with the other, and it does not make route computation, path establishment, local switching and end-to-end service restoration equivalent events.
- The strongest operational posture is evidence-based: preserve the controller request and constraints, the topology view and policy context used for computation, the domain signaling and label state, the local protection action, and the endpoint service result. Each proves a different part of the recovery story.
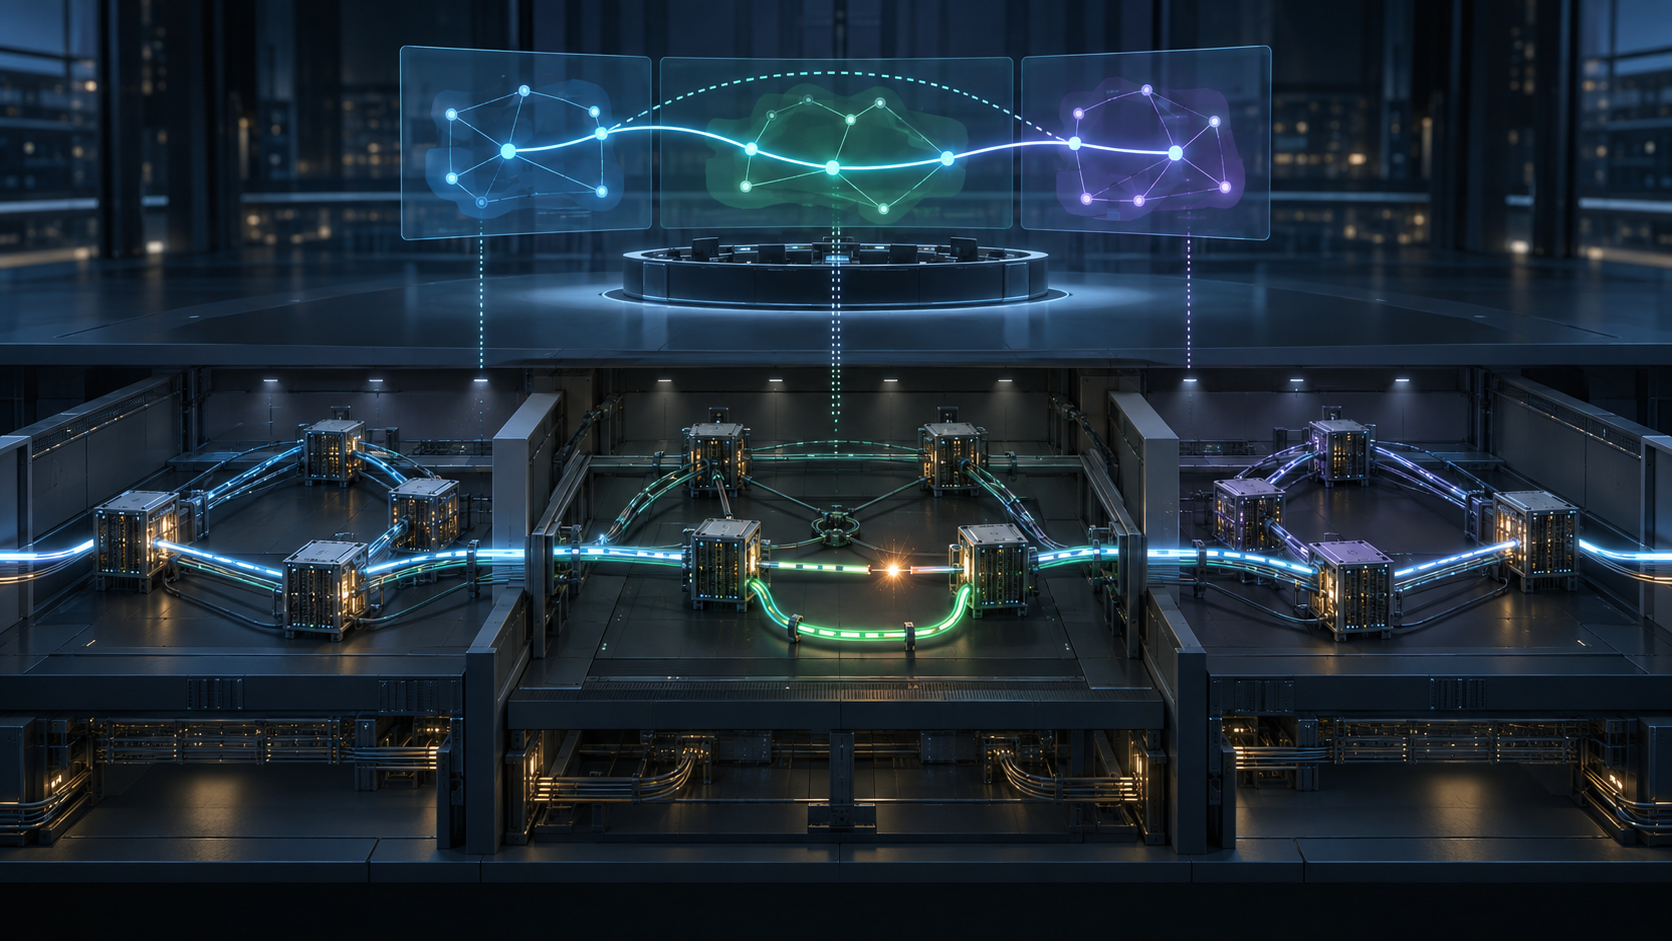
RFC 9730, published by the IETF as an Informational RFC in March 2025, addresses a problem that mature transport operators already face: control is rarely located in only one place. A GMPLS-enabled network element can discover resources, build a view of topology, compute a route under local policy and participate in RSVP-TE signaling that allocates labels hop by hop. At the same time, a controller hierarchy can coordinate multiple domains, translate service intent into resource requests and work from views that are raw, reduced or deliberately abstracted.
That combination changes the operational question. Instead of asking whether a network is “centralized” or “distributed”, operators need to ask which function made which decision, which state it relied on, and where the action was executed.
Coordination does not imply per-hop control
The architecture described by RFC 9730 permits a centralized system to select or precompute a route and then ask an ingress node to provision it. The request can reach the ingress through mechanisms such as PCInitiate or NETCONF. From that point, RSVP-TE can run among the network elements. The controller has influenced the service without directly programming every hop.
A controller acknowledgement can establish that a request was accepted. It does not establish that every hop admitted the path, labels were allocated, cross-connect state was installed, or customer traffic resumed. Those claims require lower-layer and service-boundary evidence.
ACTN sharpens the distinction at larger scale. RFC 8453 places the Multi-Domain Service Coordinator between customer-facing requests and Provisioning Network Controllers. The MDSC maps and translates services, coordinates domains and works over abstraction; the PNC configures and monitors network elements and exposes detailed or reduced topology.
The MDSC-PNC interface carries both connectivity or bandwidth requests and a policy-filtered resource view. A cross-domain graph can be global in reach while intentionally incomplete inside each domain.
The route can be computed in more than one place
RFC 9730 also resists a simple assumption about where path intelligence resides. Computation may be performed by a controller, by an ingress node using its traffic-engineering database, or by a Path Computation Element.
These choices have different responsibility boundaries. In a classic stateful PCE model, a PCE may return a path while the Path Computation Client decides whether and when to deploy it. PCE-initiated operation changes that relationship by allowing the PCE to trigger setup, maintenance and teardown.
This matters during incident review. “The PCE found a valid path” is a computation claim. “The PCC initiated it” is an activation claim. “RSVP-TE established it” is a signaling claim. “The forwarding plane carried traffic over it” is a service claim. A clean record keeps those statements separate.
The same discipline applies in multi-domain provisioning. An end-to-end service may be realized through end-to-end RSVP-TE, stitched domain LSPs or separate segments. Inter-domain labels may be allocated by border nodes or controllers. A single service can therefore have multiple control narratives underneath it, each with different observable evidence.
State is not one thing, and it is not on one clock
Mixed-control systems also expose a difficult but ordinary fact: different entities may hold different versions of reality at the same time.
A network element can maintain detailed local state. A domain controller can have a raw or reduced topology view. An MDSC can receive an abstract representation in which internal nodes or links are intentionally hidden. These views can age at different rates. RFC 9730 imposes no universal freshness bound.
That is particularly important for protection and restoration. A controller may precompute disjoint working and protection paths. It may also refresh a single-domain alternate route. But the usefulness of that computation at the moment of failure depends on the complete reporting chain: detection, reporting, controller processing, state storage and the head-end’s own current view.
The meaningful question is narrower than “the controller had the latest topology”: which topology version and abstraction policy supported the path decision, and what changed before execution?
Failure recovery is a handoff, not a single mechanism
RFC 9730’s recovery discussion is most useful when read as a handoff between time scales and scopes.
At the fastest edge, local mechanisms can act before wider coordination completes. For span protection, RFC 9730 adds no new requirement. Automatic Protection Switching or GMPLS notification-driven behavior can switch locally. In fast reroute, the responsibilities can be separated even more clearly: a controller may compute a detour, RSVP-TE may create it, and a Point of Local Repair may perform the actual switch when failure is detected.
RFC 4873 provides another example. A branch or PLR can establish an independent recovery LSP toward a merge node. Dynamic branch and merge choices may be made locally; inability to establish the required recovery path must be reported. That creates a useful operational separation between preparation, activation and outcome.
The same hierarchy appears in wider failures. A GMPLS domain may attempt segment rerouting first. If resources are insufficient, or if an inter-domain link fails, the condition can move upward through the domain controller toward the MDSC. The MDSC may then compute and trigger a cross-domain alternative, potentially involving a different domain.
Recovery scope expands when the nearer mechanism cannot complete the job.
RFC 4426 is relevant because it distinguishes span, segment and end-to-end recovery and allows recovery levels to coexist. Concurrent recovery also creates secondary operational questions. Preemption can displace other traffic. Reversion can cause another transition after the initial repair. A service may therefore be “restored” at one layer while still experiencing a later event at another.
The evidence chain should follow the control chain
For operators, auditors and institutional decision-makers, the most useful reading of RFC 9730 is procedural: every major claim in the recovery chain should have evidence appropriate to the layer that made or executed it.
At the controller or MDSC level, retain the service request and constraints, the abstract-topology version and abstraction policy, PNC responses, path or segment selections, disjointness assumptions and the acknowledgement of any reroute command. This shows what the coordinating system knew, what it asked for and what it believed should happen.
At the domain level, retain the raw traffic-engineering view where available, the local-policy result, receipt of PCInitiate or NETCONF instructions, RSVP Path and Resv messages and errors, label or cross-connect programming records, and state reports equivalent in purpose to PCRpt. This demonstrates whether the planned action became a domain-level LSP and whether the domain observed it as established.
At the local recovery level, record the detection timestamp, the PLR or branch and merge points, the protected scope, detour or bypass state, the traffic-switch event, insufficient-resource notifications and any preemption or reversion. This separates a prepared alternate from an alternate that actually carried traffic.
Finally, preserve endpoint evidence: reachability, performance and the customer-boundary service-level result. Controller success is not the same as customer recovery. End-to-end verification closes the chain.
This structure is most valuable when evidence disagrees. A controller can accept a request while RSVP-TE fails; RSVP-TE can establish a path while endpoint performance remains outside the service objective; a local switch can succeed before later cross-domain optimization. Those are different layer outcomes, not necessarily contradictions.
Availability of the controller is part of the operating model
RFC 9730 is also explicit that existing services and pre-established protection should continue to operate when the controller is unavailable. Redundancy and network-element backup functions are desirable because controller reachability is not synonymous with forwarding continuity.
Controller reliability should therefore be judged alongside autonomous behavior. A design should state what continues independently, what restores locally, what requires domain coordination and what truly depends on higher-level control.
The security implication follows. Each entity has its own management, trust and security policy. Controllers are high-value points because they can influence many resources and domains, so authentication, authorization, patching, monitoring and protection are core operating requirements. The same principle applies to interfaces carrying requests and abstractions: trust must be established not only for who may issue a command, but also for who may receive topology information and at what level of detail.
There is also a lifecycle issue. The more recovery depends on a particular controller’s state representation, policy behavior or proprietary integration, the more migration and failure isolation depend on preserving equivalent capabilities elsewhere. That argues for documenting which functions are portable, which use standard protocols and which are implementation-specific.
What RFC 9730 does not prove
The document is useful partly because its scope has limits.
It defines no universal telemetry product, no convergence target and no standard proof format for a successful recovery. Some non-GMPLS recovery behavior remains outside its scope. It also should not be blurred with adjacent standards simply because they sit near the same architectural space. RFC 9731 concerns a virtual-network YANG model. RFC 9732 addresses network-resource partitioning. RFC 9889 concerns 5G network-slice realization. They may be relevant to broader service orchestration, but they are not substitutes for RFC 9730’s recovery discussion.
The operational conclusion is straightforward. Mixed-control transport networks should be judged by responsibility boundaries and linked evidence, not architectural labels. Controllers can coordinate, compute and initiate; GMPLS elements can discover, signal, protect and restore; local mechanisms can act before higher-level systems converge. End-to-end service proof remains separate.
That separation makes resilience testable: it shows where partial recovery can occur, where stale state can enter a decision, and why globally coordinated systems may still rely on local mechanisms for their fastest response.
Sources
- RFC 9730 — Interworking of GMPLS Control and Centralized Controller Systems
- RFC 8453 — Framework for Abstraction and Control of TE Networks
- RFC 3945 — Generalized Multi-Protocol Label Switching Architecture
- RFC 4426 — Generalized Multi-Protocol Label Switching Recovery Functional Specification
- RFC 4872 — RSVP-TE Extensions in Support of End-to-End GMPLS Recovery
- RFC 4873 — GMPLS Segment Recovery
- RFC 4090 — Fast Reroute Extensions to RSVP-TE for LSP Tunnels
- RFC 8231 — Path Computation Element Communication Protocol Extensions for Stateful PCE
- RFC 8281 — Path Computation Element Communication Protocol Extensions for PCE-Initiated LSP Setup
- RFC 9731
- RFC 9732
- RFC 9889
- IETF Datatracker history for RFC 9730
- RFC Editor errata search for RFC 9730 — checked on 2026-09-14: no matching errata found.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance