Summary
- RFC 9703 defines Target FEC Stack sub-TLVs for PeerAdj, PeerNode and PeerSet SIDs, allowing an egress router to validate the AS, router and EBGP-session association named by a probe.
- PeerAdj can also validate the incoming interface, but the check is skipped when the supplied interface address is zero; PeerNode next-hop detail relies on DDMAP and separate controller reconciliation.
- Return code 3 proves a bounded FEC/egress result. It does not prove that the controller model, selected peer link, production SR policy or customer delivery was correct.
A correct name can stop short of the wire
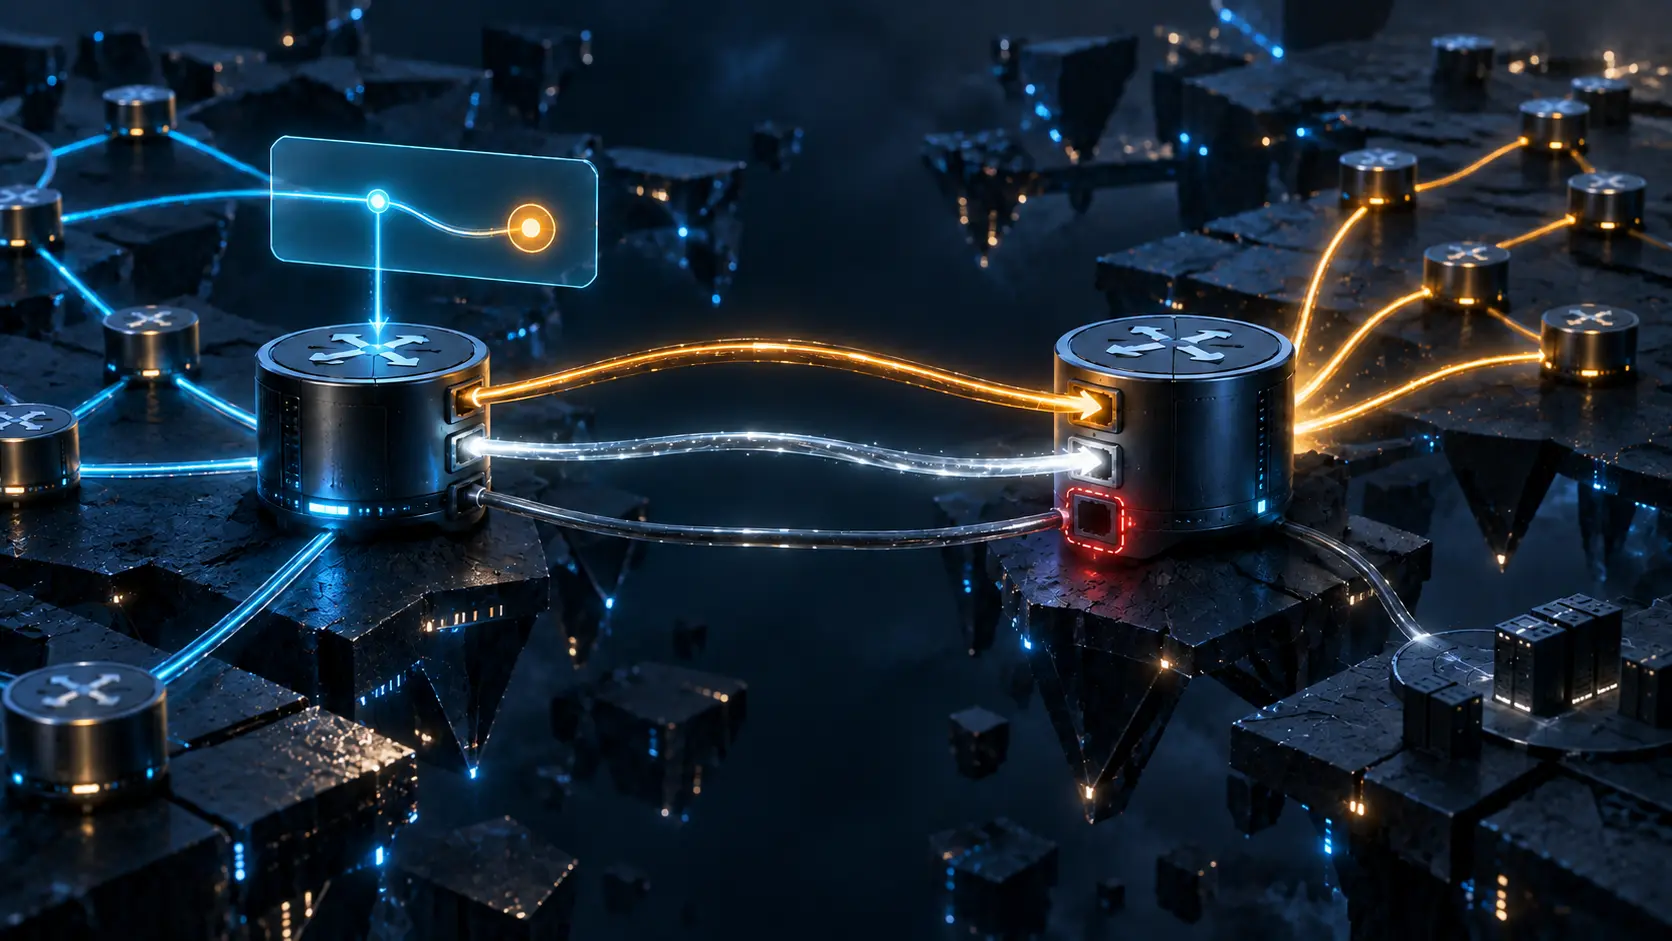
A controller sees a PeerAdj SID advertised for one exit link and installs a policy that should use it. An MPLS traceroute reaches the neighbouring ASBR. The responder's AS number, router ID and EBGP peer relation match the Target FEC Stack, and the echo returns code 3: the replying router is an egress for that FEC.
That is useful evidence, but the decisive question is what was actually checked. If the remote interface address in the PeerAdj FEC was non-zero, the receiver also compared the interface on which the OAM packet arrived. A mismatch produces code 35. If the address was zero, RFC 9703 says the receiver should skip that interface validation. The same green-looking egress result can therefore contain different coverage.
RFC 9703, published in December 2024 on the IETF Standards Track, adds sub-types 38, 39 and 40 for PeerAdj, PeerNode and PeerSet. These objects describe different scopes: one peer link, a session between two nodes that may span several links, or a set over which traffic may be balanced. Their identities are not interchangeable.
The initiator must construct the FEC from information learned through BGP-LS EPE or another controller channel. RFC 9703 explicitly leaves the acquisition and carriage of all construction details outside its scope. The FEC is thus an attributed statement about control-plane association, not a self-authenticating description of the live data plane.
Three checks, three different blind spots
For each EPE type, the remote ASBR checks its local AS, its BGP Router ID and the existence of the named EBGP session. PeerSet accepts one of the listed remote AS/router pairs. PeerAdj adds interface identity when that field exists. A malformed FEC gets code 1; mapping failure begins from code 10; interface mismatch gets 35; complete applicable validation gets 3.
PeerNode has a different visibility problem. A multi-hop session can load-balance across several interfaces. RFC 9703 points to the Downstream Detailed Mapping TLV in RFC 8029 for next-hop details, after which a controller may compare the reported interfaces with its topology. The RFC then draws a hard boundary: discrepancies between controller state and forwarding state are not detected by its procedures. DDMAP receipt, controller comparison and comparison success must be recorded separately.
This is also why RFC 9703 does not duplicate the existing RFC 9716 analysis. RFC 9716 asks how an echo reply obtains a return path across domains. RFC 9703 asks what the forward EPE FEC names, which validation reached the egress, and where the procedure deliberately has no observation.
Preserve absence as evidence
A defensible record should include the BGP-LS advertisement and its age; controller inventory and policy version; imposed label stack; exact FEC bytes; responder identity; AS/router/session results; whether the interface check was performed, skipped or failed; DDMAP content; controller reconciliation result; echo return code; and separately measured production delivery.
Do not encode a skipped interface check as pass. Use an explicit state such as skipped_zero_address. Do not encode DDMAP receipt as controller_consistent. Do not infer that one member of a PeerSet carried customer traffic because a member answered an OAM probe. And do not turn standards status into a deployment claim.
Security and cooperation narrow the test further. Independent neighbouring ASes may drop MPLS OAM before control-plane processing. Stale FEC entries retained after an AS boundary is crossed can expose internal information to a later domain. The diagnostic therefore has both an evidence owner and a disclosure owner.
Sources
Primary and protocol records: RFC 9703, RFC Editor record, IETF Datatracker, RFC 9086, RFC 8029, RFC 8287, RFC 9256, RFC 8403, RFC 8690, and the IANA MPLS LSP Ping registry. Editorial lenses: Running-Code Primacy, Minimum Initial Specification, and reality layers.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance