
Summary
- A TCP, UDP or SCTP port can be a reliable transport field and a useful default rendezvous point without authenticating the application, payload, user or intent behind it.
- RFC 3639 warns that controls built on assumed service meaning can block legitimate traffic and encourage alternate ports, dynamic negotiation, proxying, tunnelling or encryption, reducing later visibility.
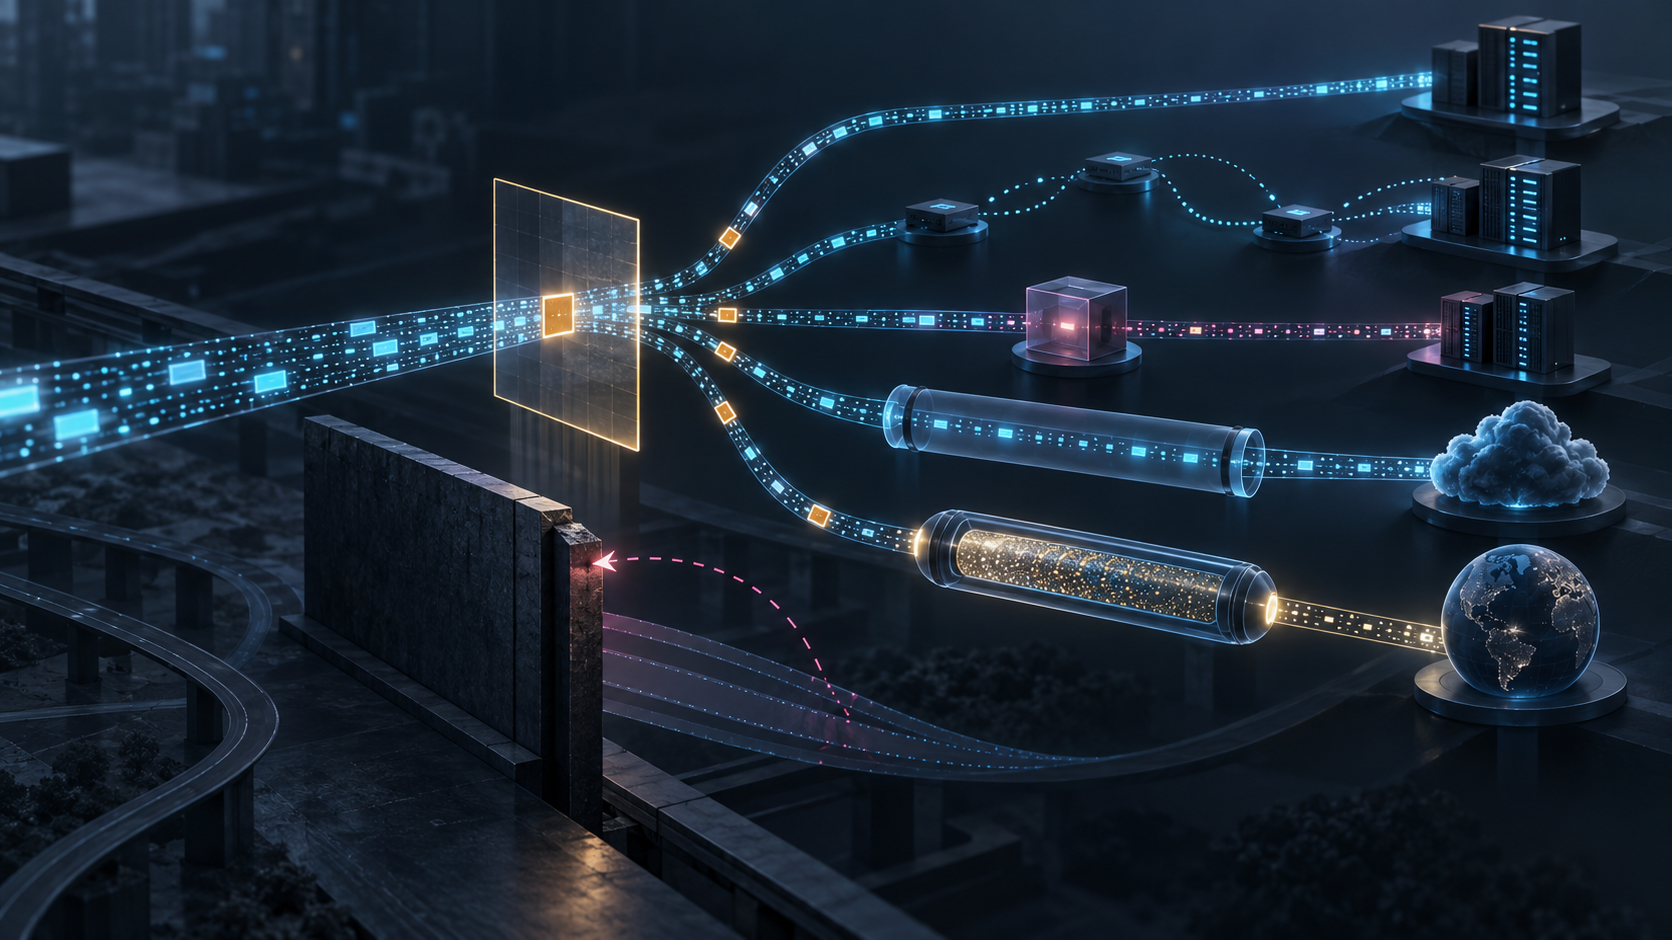
Start with the fact an observer actually has: a protocol number, source and destination addresses, and perhaps two transport ports. Those fields can be parsed exactly. They let an endpoint demultiplex traffic and, when a shared convention exists, let two endpoints find a familiar service. The leap occurs when a path device turns “this value is commonly associated with SMTP” into “this packet is SMTP, is authorized as SMTP, and should receive the fate assigned to SMTP.”
RFC 3639 says well-known ports are guaranteed to be meaningful only to the end systems. An intermediary should generally avoid assigning a specific meaning unless an endpoint has signalled it or the communicating parties and the intermediary share a convention. The distinction is practical, not philosophical. Cooperating endpoints can place any service on any port. Some applications allocate ports during a control exchange. A device that did not see that exchange, and was not told its result, lacks the mapping it wants to enforce.
That does not make port visibility worthless. Stable identifiers can support macro-level traffic analysis, load observation, firewall rules and quality-of-service treatment. The RFC explicitly recognizes those benefits. Its concern is the confidence attached to the signal and the feedback created by enforcement.
The port-25 example makes the first risk concrete. Blocking traffic nominally associated with SMTP may reduce some unwanted mail while also blocking legitimate mail. The standard records a possibility, not a measurement of a current provider. The leadership point is broader: a rule can be operationally effective against one pattern and still be evidentially too weak for every flow it captures.
The second risk is reflexive. If users and designers perceive a fixed label as a control point against their interests, they can use another port, negotiate one dynamically, send traffic through a proxy or place the original packet inside another packet. GRE changes what the outer header exposes. IPsec ESP can obscure and encrypt inner information. End-to-end encryption is not wrongdoing, and RFC 3639 expressly refuses to oppose security or encapsulation desired by users. The consequence is simply that yesterday's visible clue may not survive today's architecture.
Later guidance sharpened the same boundary. RFC 7605 describes a port as both a transport demultiplexer and a service convention, but says the correlation ultimately rests on endpoint agreement. A web server can run on port 53 if the clients know to find it there. RFC 6335 provides IANA's coordination procedure for service names and port numbers; an assignment creates a default convention, not exclusive control of actual traffic. The live service-name and port registry is coordination evidence, not an application-authentication service.
Transport specifications preserve the narrower truth. TCP, UDP and SCTP use ports in endpoint communication and demultiplexing. The IP protocol-number registry coordinates another header field. None of those records proves the program, operator, user, authorization or delivered outcome associated with one observed packet.
RFC 3639 also shows when an intermediary may possess stronger evidence. RSVP can explicitly signal treatment. SIP can negotiate subsequent communication parameters. A device that legitimately participates in such signalling may know more than one that reads only a fixed port. Even then, signalling, peer authentication, policy authorization and successful service remain separate findings.
For audit, the evidence chain should be recorded in order: visible outer header; transport tuple; registry convention; endpoint agreement or negotiated mapping; authenticated peer; application exchange; authorized policy action; observed service result. GRE and ESP demonstrate why the first item may not expose the rest. The RFC Editor record, Datatracker entry, history, errata page and plain-text edition bound what the 2003 Informational memo actually claims.
The analytical discipline is consistent with Heng Lu's writing on reality layers, minimum common specification and running-code primacy. A shared register can coordinate a default. Running endpoints determine actual use. A path institution should not promote the symbol into more authority than the operating evidence can support.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance