
Summary
- JRES lists Jehan Procaccia and Emmanuel Halbwachs as co-authors of the 2013 SIRFEX presentation, which described a service for exchanging traffic among regional research and education networks over a dedicated RENATER Layer 3 virtual private network. [1] [2] [3]
- The proposed service used separate routing environments, dedicated interfaces and IPv4/IPv6 route exchange. Its pilot record named RAP, REVE and RUBIS and described route exchange, throughput checks and fallback testing over the ordinary Internet without publishing a broad quantified performance result. [3]
- A separate MiNET team report identifies Procaccia as a project supervisor and thanks him, as a DSI network administrator, for help with a campus IPv6 deployment. The implementation record belongs to the team; it does not establish that Procaccia personally made every configuration change. [4]
- The MiNET report documents a dual-stack rollout, explicit IPv6 addressing and routing controls, Router Advertisement decisions, and a choice to retain some administrative services on IPv4 where equivalent security was not yet available. [4]
- Taken together, the records show why operational continuity depends on bounded route exchange, clear address-family handling and tested fallback. This is BTW analysis of the documented mechanisms, not a claim that either project guaranteed resilience or produced unreported traffic outcomes.
The useful question is where the route should go
The starting problem in the SIRFEX record was not whether the participating institutions had some form of Internet access. It was whether traffic exchanged among regional research networks should have to follow the same ordinary public-Internet paths used for general connectivity. The co-authored presentation described a need for direct interconnection through a research-network service so that the relevant traffic could remain within a controlled routing arrangement. [1] [2] [3]
A research and education network is a network serving universities, laboratories and related institutions. It often connects organizations whose work depends on large data transfers, shared instruments, distributed computing or collaboration across campuses. Those uses do not automatically require a private path, and the SIRFEX sources do not establish a universal rule. They do show a concrete design question: when several regional networks need to exchange traffic, which routing boundary should define the exchange?
“Commodity Internet” in this context means ordinary public Internet transit rather than a dedicated research-network path. Public transit is not inherently defective. It is a broad service built to reach many destinations through commercial and technical relationships. A dedicated research-network interconnection addresses a different requirement. It can make the intended participants, route scope and operating responsibility more explicit.
That distinction is important because a network name does not determine a packet's path. Routing information does. An institution may be connected to a regional research network and still reach another institution through an indirect public path if the necessary routes are not exchanged inside the research-network environment. The visible institutional relationship and the running forwarding path can therefore diverge.
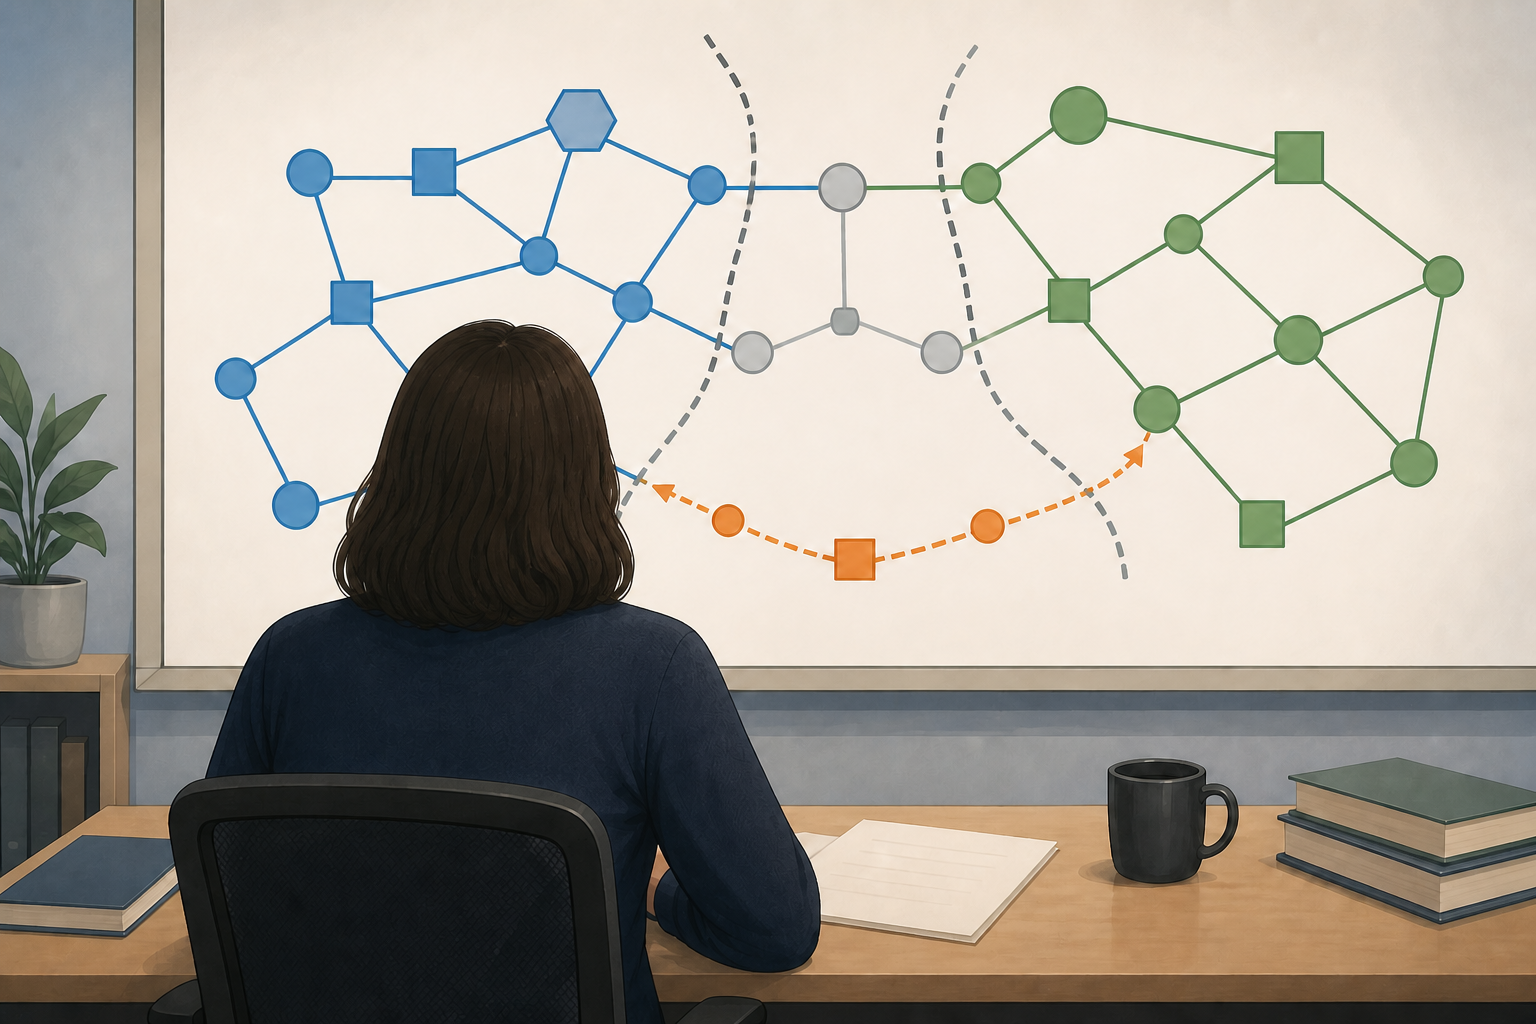
The SIRFEX proposal treated that divergence as an operational problem. The record described a dedicated service over RENATER infrastructure, separate interfaces and controlled route exchange for IPv4 and IPv6. [3] The design was about converting an organizational wish—regional networks should exchange traffic more directly—into a set of routing conditions that equipment and operators could enforce.
Procaccia's contribution is evidenced through co-authorship and supervision
JRES identifies Jehan Procaccia and Emmanuel Halbwachs as the authors of the 2013 SIRFEX presentation. [1] [2] The signed technical presentation supplies the architecture and pilot details used in this article. [3] Co-authorship is person-level evidence: it connects Procaccia by name to a dated technical record and its stated design. It is not evidence that every idea, configuration or test in the presentation was his individual work.
The distinction is more than a legalistic caution. Infrastructure projects depend on multiple kinds of contribution. Someone may frame the requirement, design a routing policy, coordinate participating networks, prepare interfaces, test reachability, document results or operate the service after a pilot. A presentation with two named authors does not allocate every task between them. The accurate description is that Procaccia co-authored the record, not that he alone delivered the service.
A second source class provides a different person-level connection. The MiNET project team's report on an IPv6 deployment identifies Procaccia as a supervisor and thanks him, as a DSI network administrator, for assistance. [4] This is independent of the SIRFEX authorship record. It connects him to practical deployment support and a defined operational role.
Again, the verb sets the boundary. The team implemented the deployment described in its report. Procaccia supervised and assisted according to that report. [4] The evidence does not show that he typed every command, selected every address or personally validated every device. Attributing the implementation to the project team and the bounded contribution to Procaccia preserves both parts of the record.
Official Telecom SudParis teaching pages also connect Procaccia with practical Internet and networking instruction. [5] [6] These pages help confirm continuing technical subject matter, but they are not outcome evidence. Teaching a networking course does not prove that a person built a particular production system. Here it is narrow role context, not a substitute for the dated SIRFEX and MiNET records.
A Layer 3 VPN creates a separate routing environment
The SIRFEX presentation described a RENATER Layer 3 virtual private network, commonly shortened to L3VPN. [3] An L3VPN is a provider-managed private routing environment at the Internet Protocol layer. “Private” in this sense does not mean that all content is automatically encrypted or that every security risk disappears. It means that selected routing domains are kept logically separate from general routing and are connected under a defined service.
The practical benefit is control over who exchanges which routes. A regional network can attach to the service through a dedicated interface, advertise approved destinations and learn approved routes from other participants. The provider carries those routes inside the dedicated environment. General Internet routes can remain outside that exchange unless the design explicitly introduces them.
This separation turns a broad goal into inspectable questions. Which interfaces belong to the service? Which address families are enabled? Which prefixes may each participant announce? Who filters unexpected routes? How is reachability checked? What path is used when the dedicated service fails? Those questions can be answered through configurations, route tables, test records and incident procedures.
The SIRFEX sources support the existence of a proposed architecture and a named pilot. [1] [3] They do not support claims that every French regional network joined, that a permanent production service achieved a particular availability level, or that the arrangement carried a measured amount of traffic. A responsible account can explain the mechanism without inventing the scale.
VRF is the boundary inside the router
The presentation described virtual routing and forwarding, or VRF, as part of the service. [3] A VRF is a separate routing table that keeps one traffic domain from mixing with another. A router can therefore hold a general Internet route for a destination in one table and a research-network route for the same address context in another, depending on how the service is designed.
This separation reduces ambiguity, but it also creates operating duties. An interface must be attached to the correct VRF. Route import and export rules must select the intended destinations. Monitoring must look at the relevant table rather than only the router's global view. A correct route in the wrong routing table does not provide the intended service.
VRF boundaries can fail in more than one way. A missing route may break reachability. An overly broad import rule may expose destinations that were not meant to be shared. A mismatched address-family setting may make IPv4 work while IPv6 fails. An operations team therefore needs both positive tests—approved destinations are reachable—and negative tests—unapproved routes remain excluded.
The SIRFEX material records a design based on bounded route exchange. [3] It does not publish a complete configuration or security audit. This article treats VRF as the mechanism described by the authors and explains the operational questions it creates. It does not claim that the mechanism eliminated every route leak or failure mode.
MPLS carries the separation across the provider network
Multiprotocol Label Switching, or MPLS, is a label-based forwarding mechanism often used to steer traffic through a provider network. The SIRFEX presentation placed the L3VPN on RENATER infrastructure using VRF and MPLS. [3] In simplified terms, the participant-facing routing decision is associated with labels that help the provider carry traffic across its core while preserving the correct virtual network context.
This creates another continuity boundary. A route may appear in a control system while the corresponding forwarding path is incomplete. Conversely, a stale forwarding entry may persist after a routing change. Operational checks need to verify actual reachability, not only that a configuration object exists.
The SIRFEX pilot's throughput checks and reachability work are therefore meaningful as categories of validation. [3] They show that the record considered more than a diagram. But the presentation does not authorize a broad claim about production capacity or long-term availability. A check proves what it measured, at the time and scope in which it ran.
For readers assessing a similar service today, the useful questions remain concrete: Is the participant interface up? Is the intended VRF selected? Are the correct routes present for both address families? Does traffic follow the expected path? Does the fallback behave as documented? A technology label alone cannot answer those questions.
IPv4 and IPv6 require separate evidence
The SIRFEX design included route exchange for IPv4 and IPv6. [3] The two address families can use the same physical infrastructure and still behave differently. A route policy may permit an IPv4 prefix but omit its IPv6 counterpart. A participant may have a functioning IPv6 interface but lack return routes. Monitoring may test one family and leave the other unseen.
This is why “the network is connected” is an incomplete status. Operators need to identify the address family in every reachability claim. If a service is described as dual stack, meaning IPv4 and IPv6 operate at the same time, both paths need their own routing, filtering, name resolution and application checks.
Addressing is also a resource record. An IPv6 prefix must be allocated, recorded and advertised consistently. Uniqueness prevents two participants from presenting the same destination as their own. Accurate route exchange ensures that packets reach the network responsible for that destination. Security metadata and filtering help limit unauthorized or accidental advertisements.
The SIRFEX sources do not provide a full inventory of participant prefixes. [3] They support the narrower claim that IPv4 and IPv6 exchange formed part of the design. The practical consequence is that the service could not be validated with an IPv4-only test if its intended scope included both families.
BTW analysis draws a continuity lesson from this. Migration should not turn IPv6 into a ceremonial checkbox. If an organization advertises that a service supports both families, it should be able to show routes, tests, fault handling and responsible owners for both. The record layer and the running layer should match.
The pilot made route exchange testable
The signed SIRFEX presentation named RAP, REVE and RUBIS in its pilot and described route exchange, throughput checks and fallback testing. [3] Naming the participating networks matters because it bounds the evidence. It tells the reader which relationships the pilot examined rather than implying nationwide or universal adoption.
A route-exchange test can begin with a simple question: does one participant learn the destination that another participant is authorized to announce? The next question is whether packets travel through the dedicated environment rather than taking an unintended public path. Return reachability must also work; one-way success can hide an asymmetric failure.
Throughput checks add an operating observation. Throughput is the amount of data delivered over a period under a stated test. The source indicates that checks took place, but it does not provide a basis here for publishing a headline capacity, average speed or service-level result. This article therefore does not convert the existence of a test into a quantified performance claim.
The same restraint applies to resilience. A pilot that exercises a fallback path demonstrates that the designers considered failure handling. It does not prove that every future incident will recover within a guaranteed time. The result is bounded by the tested topology, conditions and date.
The value of the pilot record lies in its structure. It links the service concept to named participants and operating checks. It gives later readers a way to ask whether the proposed routing boundary was actually instantiated. That is stronger evidence than a strategy statement, even when it remains short of a long-term production measurement.
Fallback is a path that must be deliberately tested
The presentation described fallback over the ordinary Internet. [3] Fallback is a tested alternate path used when the preferred route is unavailable. It is not merely the presence of a second connection. The alternate must be able to learn or reach the required destinations, carry the intended traffic and return service without creating an unacceptable routing or security state.
A fallback design can introduce trade-offs. Traffic may leave the dedicated research-network environment and traverse public transit. Latency or throughput may change. Filters may differ. Source addresses and return paths may behave differently. Applications that rely on restricted reachability may need additional controls.
This means the operating rule should say when fallback is allowed, which traffic can use it, who declares the preferred path unavailable, and how service returns to normal. A manual emergency procedure and an automatic route change create different risks. Both require logs and observable tests.
The SIRFEX source supports the fact that fallback testing formed part of the pilot. [3] It does not say that the public path was identical to the dedicated service or that failover was lossless. The accurate conclusion is that alternate-path behavior was treated as something to test rather than assume.
For continuity reporting, a fallback claim should always carry scope. Which participant pair was tested? Was the test IPv4, IPv6 or both? Which route disappeared? How long did convergence take? Did active sessions survive? The source record used here does not provide all of those measurements, so they remain questions for an operator, not assertions in this article.
The MiNET report supplies a separate implementation record
The MiNET project report is useful because it does not come from the SIRFEX co-authored presentation. It records a campus IPv6 deployment undertaken by a project team and identifies Jehan Procaccia as a supervisor. It also thanks him, as a DSI network administrator, for assistance during the work. [4]
This provides independent support for a practical role at the boundary between instruction and operations. The team had to address real deployment questions rather than only describe IPv6 in the abstract. The report covers dual-stack operation, addressing, routing and Router Advertisement controls. [4]
The attribution must remain precise. The students or project members documented their implementation. Procaccia's contribution is the supervision and help they explicitly recorded. The source does not allocate each configuration step, troubleshooting action or decision to him individually. A person article should not absorb a team's work merely because a senior participant is named.
The report's value is not diminished by this boundary. It shows a second setting in which Procaccia's documented role touched operational networking. The SIRFEX record concerns interconnection among regional research networks. The MiNET record concerns a campus IPv6 deployment. Together they support a thesis about routing boundaries and migration discipline without claiming that the projects were one programme.
They also provide different evidence types. Co-authorship ties a person to a technical design and pilot presentation. An independent team acknowledgment ties the person to supervision and operational assistance. Official teaching records provide limited role context. [1]-[6] The combination is stronger than a generic biography because each source has a defined evidentiary job.
Dual stack preserves service while IPv6 is introduced
The MiNET report documents a dual-stack rollout. [4] Dual stack means running IPv4 and IPv6 at the same time during migration. It allows existing IPv4-dependent services to continue while IPv6 routing and applications are introduced and tested.
Dual stack is not a free continuity guarantee. It creates two network paths and often two sets of operational dependencies. A device may prefer IPv6 when both are available, so a partially broken IPv6 path can make an application appear slow or unavailable even though IPv4 still works. Monitoring must therefore test what users and applications actually select.
Address planning is part of the migration. IPv6 provides a much larger address space, but abundance does not remove the need for structure. Prefixes should map to operational domains, be recorded consistently, and support aggregation where appropriate. Routing policies must identify which prefixes leave a campus and which remain internal.
The MiNET source supports the fact that the team made explicit addressing and routing choices. [4] It does not justify a claim that the design remains current today or that it represents a universal model for every campus. The article uses it as a dated implementation record showing that migration required deliberate controls.
BTW analysis sees continuity in the decision to preserve working IPv4 service while testing IPv6. This is not an argument for indefinite delay. It is a recognition that migration success is measured by functioning applications and controlled routing, not by the mere presence of IPv6 addresses on a diagram.
Router Advertisements define what devices believe about the network
The MiNET report includes Router Advertisement controls. [4] A Router Advertisement is an IPv6 message that tells devices how to configure and reach a network. It can announce a prefix, a default router and other parameters that influence a device's network state.
This mechanism shifts part of configuration from a centrally assigned host record to information devices receive on the local network. That can simplify deployment, but it also makes trust boundaries important. A mistaken or unauthorized advertisement can direct devices toward the wrong router or give them an unintended address configuration.
Operational controls may include deciding which interfaces send advertisements, which network segments accept them, how unexpected messages are detected and how address assignment is coordinated with other services. The precise controls vary by environment. The MiNET report establishes that Router Advertisement decisions formed part of the deployment; it does not establish that every possible threat was eliminated. [4]
The connection to routing continuity is direct. A backbone route can be correct while end devices select an incorrect local gateway. Conversely, local configuration can be correct while the wider network lacks a return path. A complete test follows the path from device configuration through campus routing to the external destination and back.
This is another reason to separate records from slogans. “IPv6 enabled” is too broad to describe an operating state. A useful record shows the advertised prefix, gateway behavior, routing scope, monitoring result and responsible owner. The technical details make the claim more understandable, not less.
Keeping selected services on IPv4 was a bounded security decision
The MiNET report describes a deliberate choice to leave some administrative services on IPv4 where equivalent security was not yet available. [4] The source does not support a blanket claim that IPv6 was insecure. It documents a local migration boundary: the team did not move every service merely to make the deployment appear complete.
This is a useful example of risk-based sequencing. A protocol transition can expand the set of reachable paths, change filtering assumptions and expose services through an address family that existing controls do not yet cover. An operator should verify authentication, access rules, logging, monitoring and incident procedures before treating the new path as equivalent.
Retaining a service on IPv4 can preserve a known control while the IPv6 path is prepared. It can also create technical debt if the temporary exception has no owner or review date. A responsible record therefore needs both the reason for the exception and the condition under which it will be removed.
The report supports the team's documented choice and Procaccia's bounded supervisory or assistance role. [4] It does not show that he alone selected every exception or guaranteed its security. The implementation remains team-attributed.
BTW analysis connects this choice to running-code primacy. A migration milestone should not be declared complete because an address family has been enabled. The relevant question is whether the real application path has equivalent, tested controls. Where it does not, the gap should be explicit rather than hidden behind an adoption percentage.
The common thread is an explicit operating boundary
SIRFEX and MiNET addressed different systems, but their documented mechanisms share a practical pattern. The SIRFEX record bounded route exchange among regional networks through a dedicated L3VPN, separate routing tables and fallback testing. [3] The MiNET report bounded an IPv6 migration through dual-stack operation, addressing and routing choices, Router Advertisement controls and retained IPv4 exceptions. [4]
The common thread is not a claim that Procaccia invented these techniques or personally operated every component. It is that the records connected to him treat connectivity as a set of explicit boundaries. Who exchanges routes? Which address family is active? Which services migrate? What alternate path exists? What security control must remain?
BTW analysis labels this as operational continuity. Continuity does not mean that nothing changes. It means that changes preserve a defined service or fail in a controlled, observable way. A dedicated route can fail. A dual-stack migration can expose an incomplete path. The control comes from knowing the intended boundary, testing it and retaining evidence of the result.
This reality layer is more useful than institutional rhetoric. A network does not become legitimate or resilient because it carries the name of a community, region or research programme. It earns trust through accurate resource records, bounded routing policy, working paths, tested fallback and accountable operations.
The same reasoning avoids false personal credit. A person's contribution should be attached to the co-authored record, supervisory role or documented decision. The operating outcome remains with the teams and institutions that configured, tested and ran the network. Precision strengthens the story because it shows where responsibility actually sat.
Attribution should follow the verb and the responsible system
Person-level infrastructure reporting is most reliable when it follows verbs. Jehan Procaccia co-authored the SIRFEX presentation. [1] [2] A project team identified him as a supervisor and thanked him for network-administrator assistance during an IPv6 deployment. [4] Official pages connect him with practical networking instruction. [5] [6]
The institutions and teams designed, implemented, tested and operated the systems described by their respective records. The sources do not say Procaccia alone performed those actions. Replacing “co-authored” or “supervised” with “built” would turn a supported contribution into unsupported sole causation.
The same rule applies to results. The SIRFEX presentation records a pilot and categories of checks. [3] It does not publish evidence here for a quantified traffic gain, capacity improvement, resilience guarantee or user outcome. The MiNET report documents a team deployment, but its existence does not support a claim that Procaccia personally implemented every control.
Clear attribution is not a way to make a technical profile smaller. It reveals the operating system around the person. Readers can see which record belongs to an author, which deployment belongs to a team, which infrastructure belongs to an operator and which result would require a new measurement.
That separation also makes later accountability possible. If a route exchange changes, the current operator must explain it. If a migration exception persists, the responsible service owner must review it. A historical co-author or supervisor should not be assigned control over a later network state without fresh evidence.
What a responsible reviewer should verify next
The next review of a research-network interconnection should begin with scope. Which institutions are current participants? Which prefixes are authorized? Which address families are supported? Which destinations are meant to remain within the dedicated path? A current inventory prevents a historical design from being mistaken for a live service map.
The reviewer should then inspect route evidence. For each participant, the expected IPv4 and IPv6 prefixes should appear in the correct VRF and nowhere they are not authorized. Import and export rules should have named owners. Unexpected announcements should produce an alert and a documented response.
Path tests should verify both direction and address family. A traceroute or equivalent observation can help show whether traffic uses the intended environment, but it should be interpreted with the operator's topology and privacy constraints. Application tests should confirm that the service users actually need is reachable.
Fallback should be exercised under controlled conditions. The test should identify the withdrawn or failed preferred path, the alternate route, the observed interruption and the restoration procedure. Public transit fallback should be reviewed for security and policy differences, not treated as an identical substitute.
An IPv6 migration review should inspect Router Advertisements, prefix assignment, routing, name resolution and the services still restricted to IPv4. Each exception should state what equivalent control is missing and when it will be reassessed. This turns “temporary” into a governed state.
Finally, the reviewer should preserve attribution. Historical design records can explain why a service exists. Current operations records must show how it behaves now. People should receive credit for supported contributions without being assigned control over systems they do not presently operate.
Sources
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance