
Summary
- HotJava’s applets moved browser extension from a preinstalled handler to Java code delivered with a page and executed on the reader’s computer.
- That flexibility depended on a local policy boundary; Sun’s own Alpha2 documentation said public-key encryption was not yet implemented, and later independent review found flaws in HotJava Alpha3.
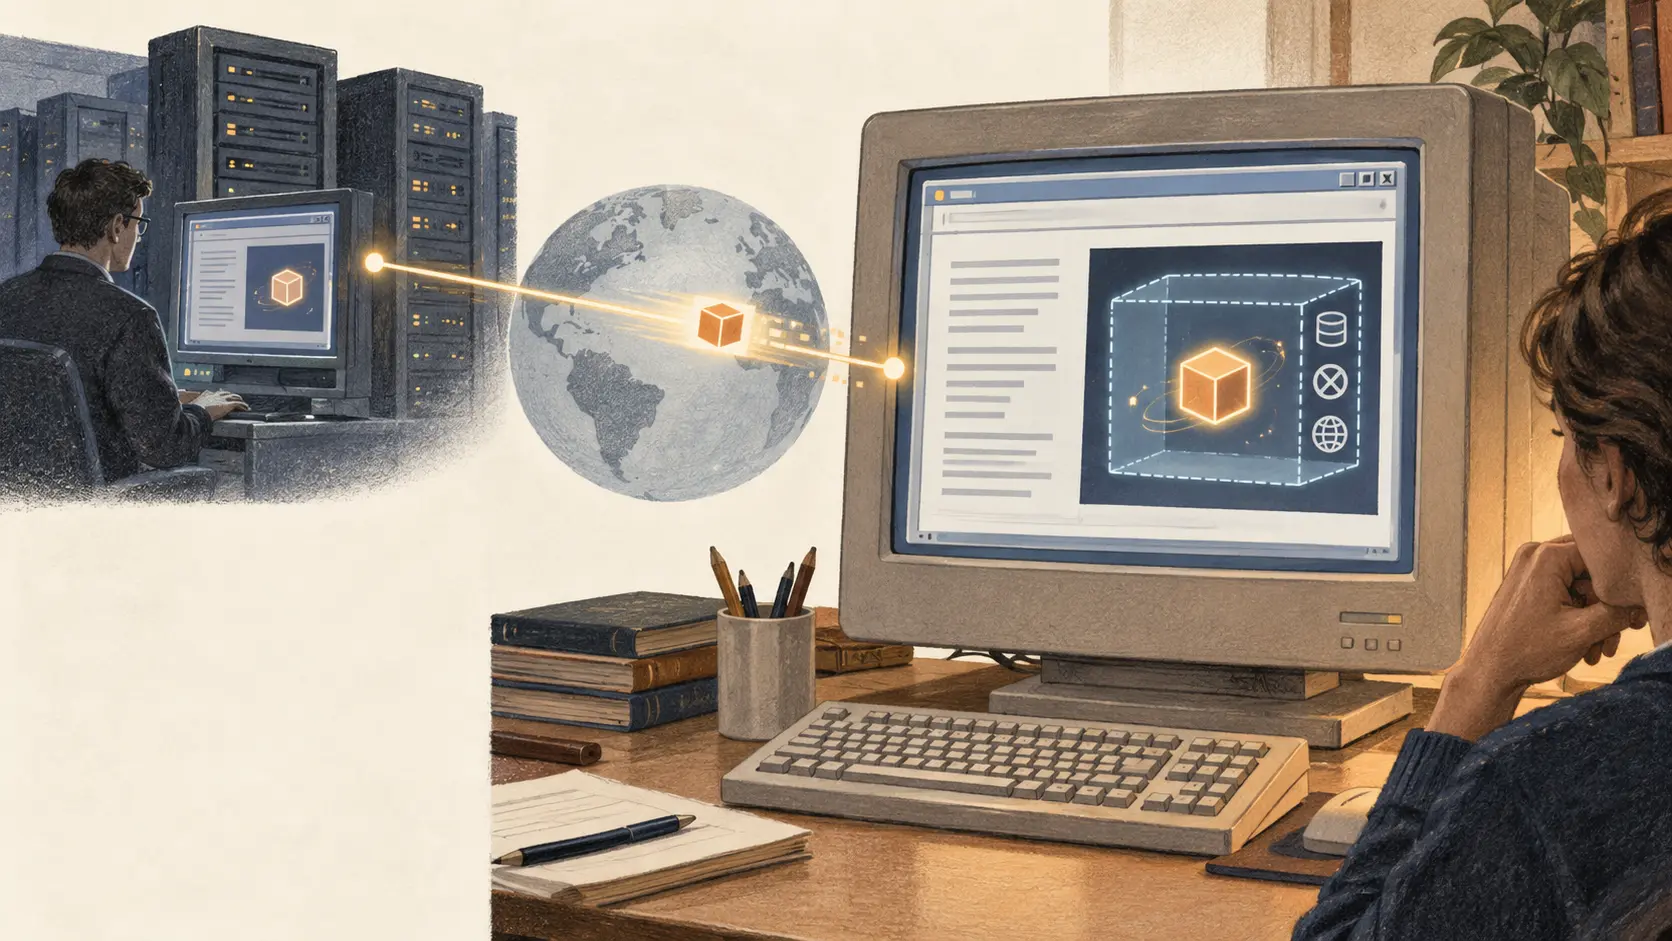
In 1995, a Web page could describe an interactive object, but a conventional browser still needed to know in advance how to interpret it. HotJava’s proposal changed where that missing capability could come from. A page could point to a Java applet; HotJava would fetch the program and run it inside the browser. The network delivered not only a document but part of the machinery for interpreting it.
Sun described this as a way to escape a fixed menu of data types and protocols. A new image format could arrive with a handler; a new protocol could arrive with its own code. Its HotJava white paper called the result “dynamic” browsing and imagined that users would not have to install each new piece of software manually. These were design claims and examples, not evidence that the Web had already adopted this model at scale.
The move also changed the compatibility bargain. The Alpha2 applet guide described applets embedded in HTML. A browser that did not understand the new tag could ignore it and still read the surrounding page. That offered graceful degradation for text, but only HotJava could execute the new behavior. The author gained a way to ship a richer experience without waiting for every browser vendor to add a handler; the reader needed a compatible runtime and accepted code running locally.
The local machine therefore became the decisive boundary. Sun’s October 1995 paper presented Java’s type checks, bytecode verification, and runtime controls as safeguards. But the release notes put limits around that confidence. HotJava Alpha2 was a prototype for Solaris/SPARC, and its README explicitly said public-key encryption was not implemented. Confinement and authenticity were different problems: restricting what code could do did not, by itself, prove who had supplied it.
Alpha3 documentation made policy visible to the user. Its security dialog offered modes ranging from no applet access to source-host, firewall, or unrestricted access. File access was also mediated by read and write paths. The default write path was empty, although an operator could configure one. The boundary was not simply “Java is safe”; it was a set of rules, defaults, and administrator choices around a program arriving from elsewhere.
That distinction appeared in the public discussion almost immediately. In an April 1995 W3C mailing-list exchange, participants debated whether a safe execution environment was enough or whether users also needed assurance that downloaded code was genuine. The exchange records disagreement, not a settled consensus. A later 1996 security study by Drew Dean, Edward Felten, and Dan Wallach examined HotJava Alpha3 and documented flaws, including denial-of-service risks. That later audit cannot tell us what every user knew in 1995, but it does show why a sandbox had to be tested and maintained rather than treated as a permanent guarantee.
HotJava’s historical contribution was a relocation of the extension point. Publishers could send executable behavior with a page; readers and their administrators inherited the decision about what that behavior could touch. The same design that lowered the coordination cost of adding a new browser capability raised the assurance burden at the endpoint. The sources establish a prototype and a debated architecture—not universal deployment, invulnerability, or a measured change in Web usage.
Sources and evidence limits
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance