
Policy continuity, legitimacy, and accountability signals across internet governance institutions.
Governance
Governance
Internet governance intelligence tracks institutions, policy processes, standards activity, registry operations, accountability disputes, and implementation signals that affect internet infrastructure. BTW.
RIR WatchdogCase FileNumber Resource SocietyICANNIETFHistory of InternetNOGs

RIR Watchdog, Case File, NRS, ICANN, IETF, History of Internet, and NOG sessions.
Coverage prioritizes implementation evidence and institutional behavior over declarative positions.
Latest Coverage
Latest from Governance
7,593 articles
IETF
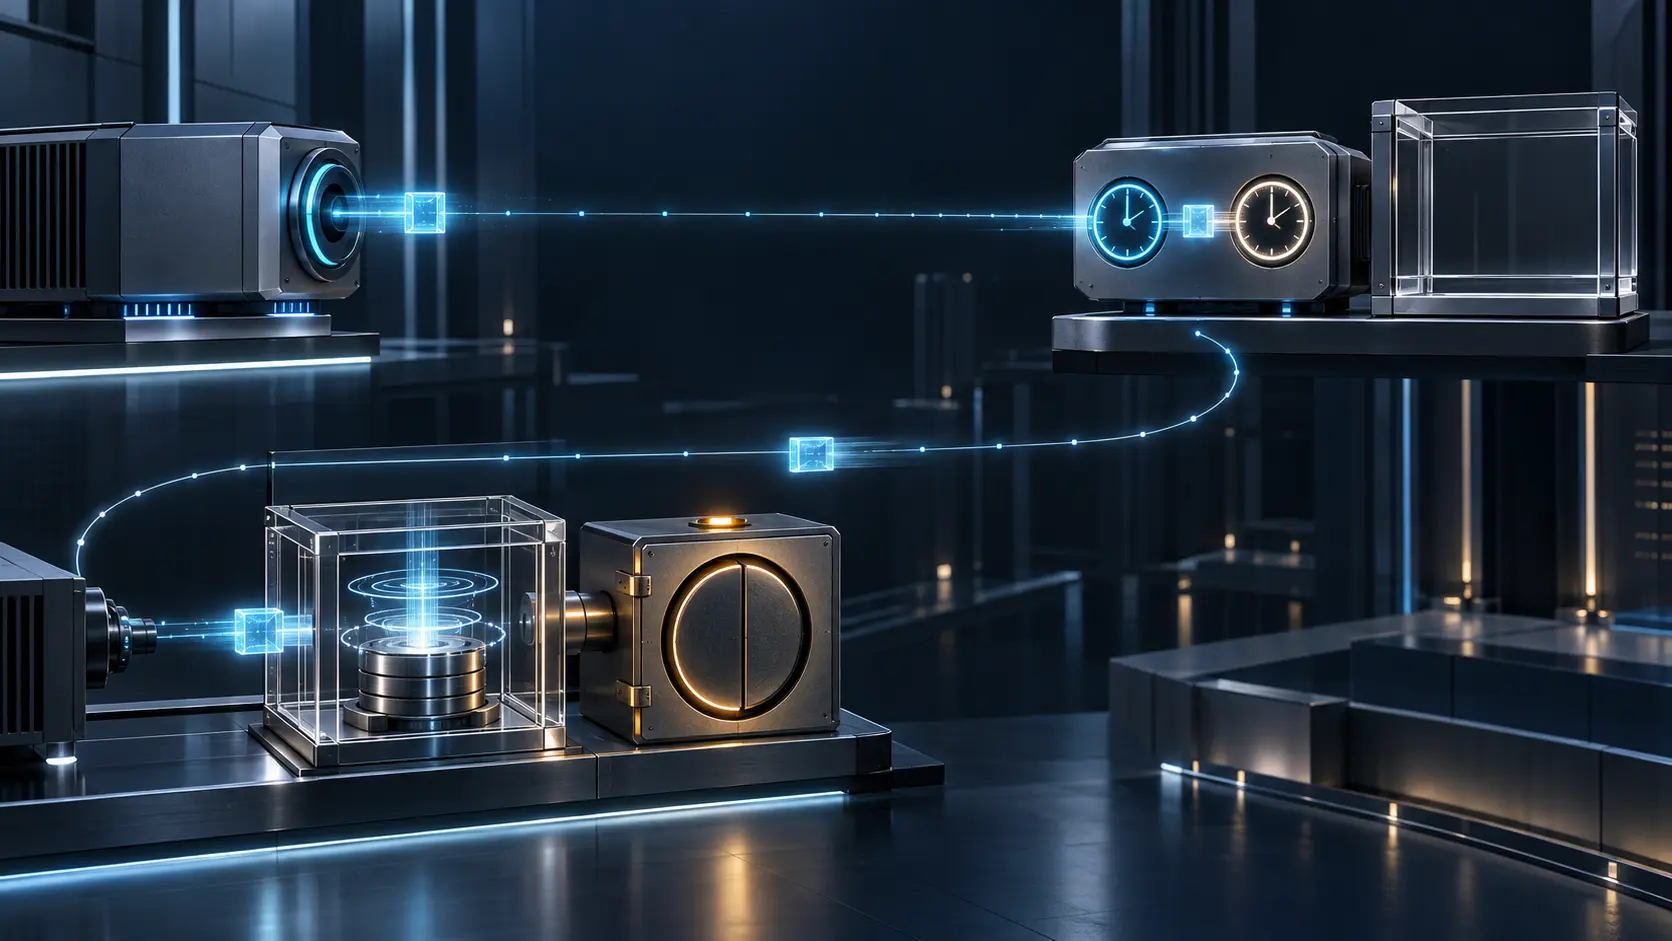
The Reflector Returned the Evidence. It Kept No Measurement Report.
TWAMP's Session-Reflector receives a test packet, timestamps it, creates a response and sends the relevant packet evidence back. It does not retain packet-level results for a Fetch-Client, because TWAMP has no such role. RFC 5357 therefore places measurement custody at the…

History
The Alias Said “Local Disk.” The Login Needed a Different Name: RFC 3721
An operator could recognize a storage target by a friendly label, but the protocol could not safely treat that label as identity. RFC 3721 separated the name that persists, the address that locates, the credential that authenticates, and the rule that authorizes—then drew a…

History
The Name Promised Persistence. Its Resolver Did Not Yet Exist: RFC 3937
RFC 3937 registered a global namespace for IPTC resources and committed the organization to persistent access. But the registration arrived before the resolver and validation machinery. The name, the authority that assigned it, the map to a URL and the accessible resource were…
IETF
The KDC Sent a Preferred Curve List. The Message Was Not Authenticated.
The client proposed elliptic-curve parameters. The Key Distribution Center rejected them and returned an ordered list of alternatives. That list could guide the next authentication attempt, but RFC 5349 states that the Kerberos error carrying it was not integrity protected. The…
IETF
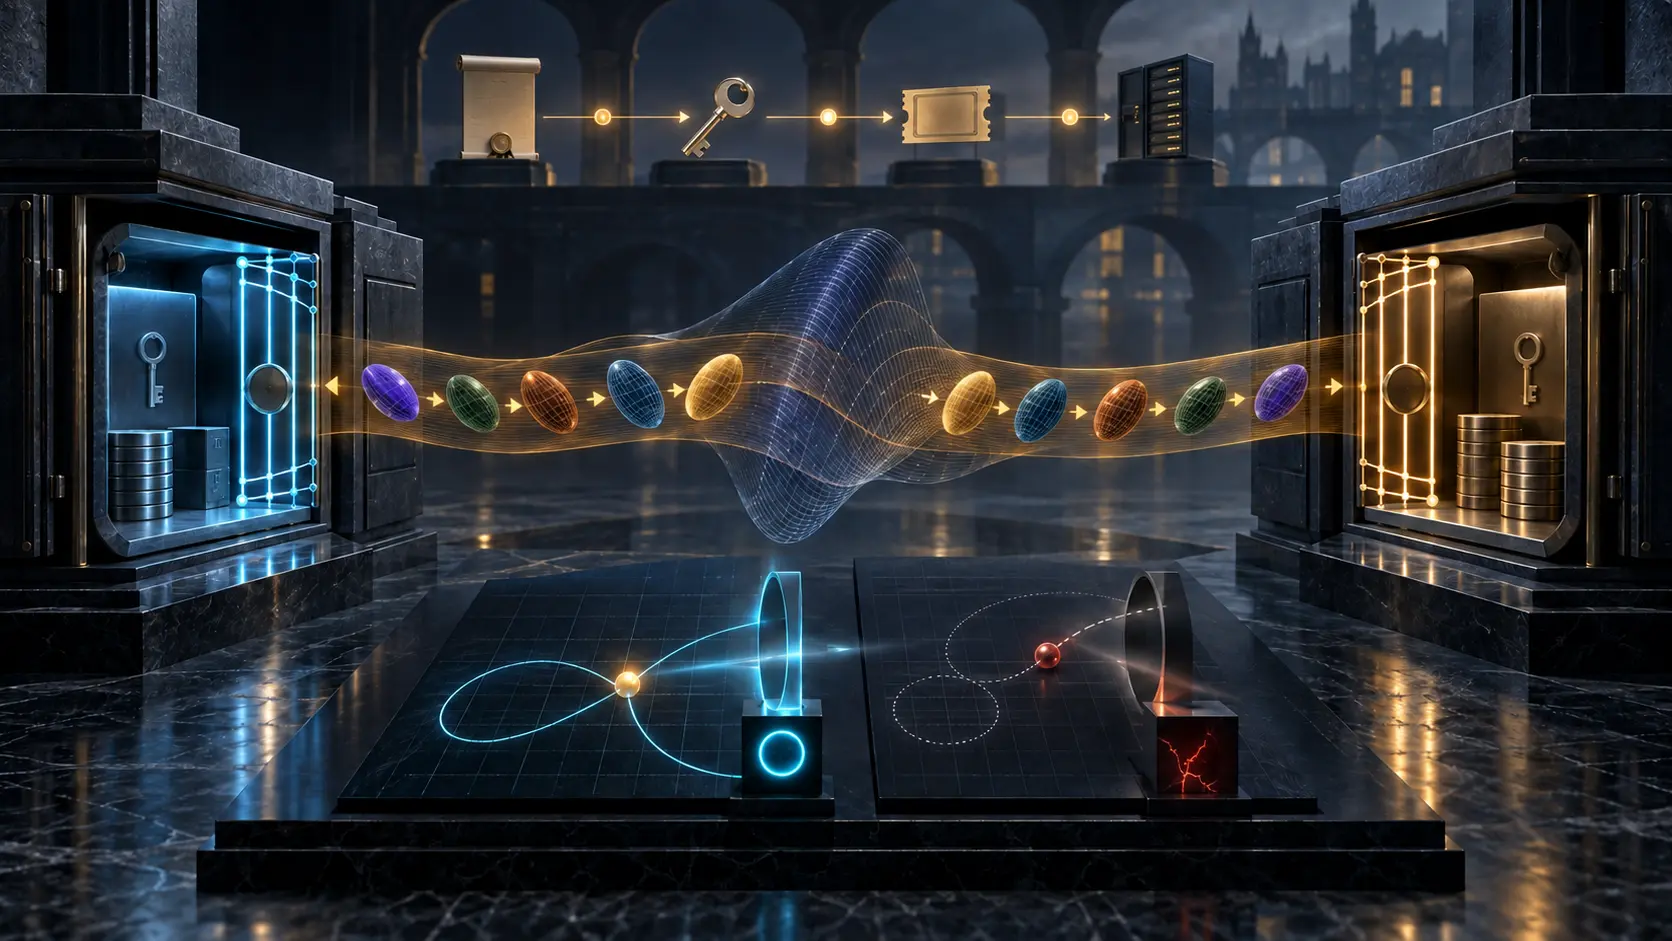
The KDC Suggested a Curve. The Error Message Had Not Been Authenticated.
The client offered one elliptic curve and the Key Distribution Center declined it. The reply looked authoritative: error 65, followed by a preference-ordered list of acceptable parameters. The client could select a curve and try again. RFC 5349 places one hard limit on that…
History
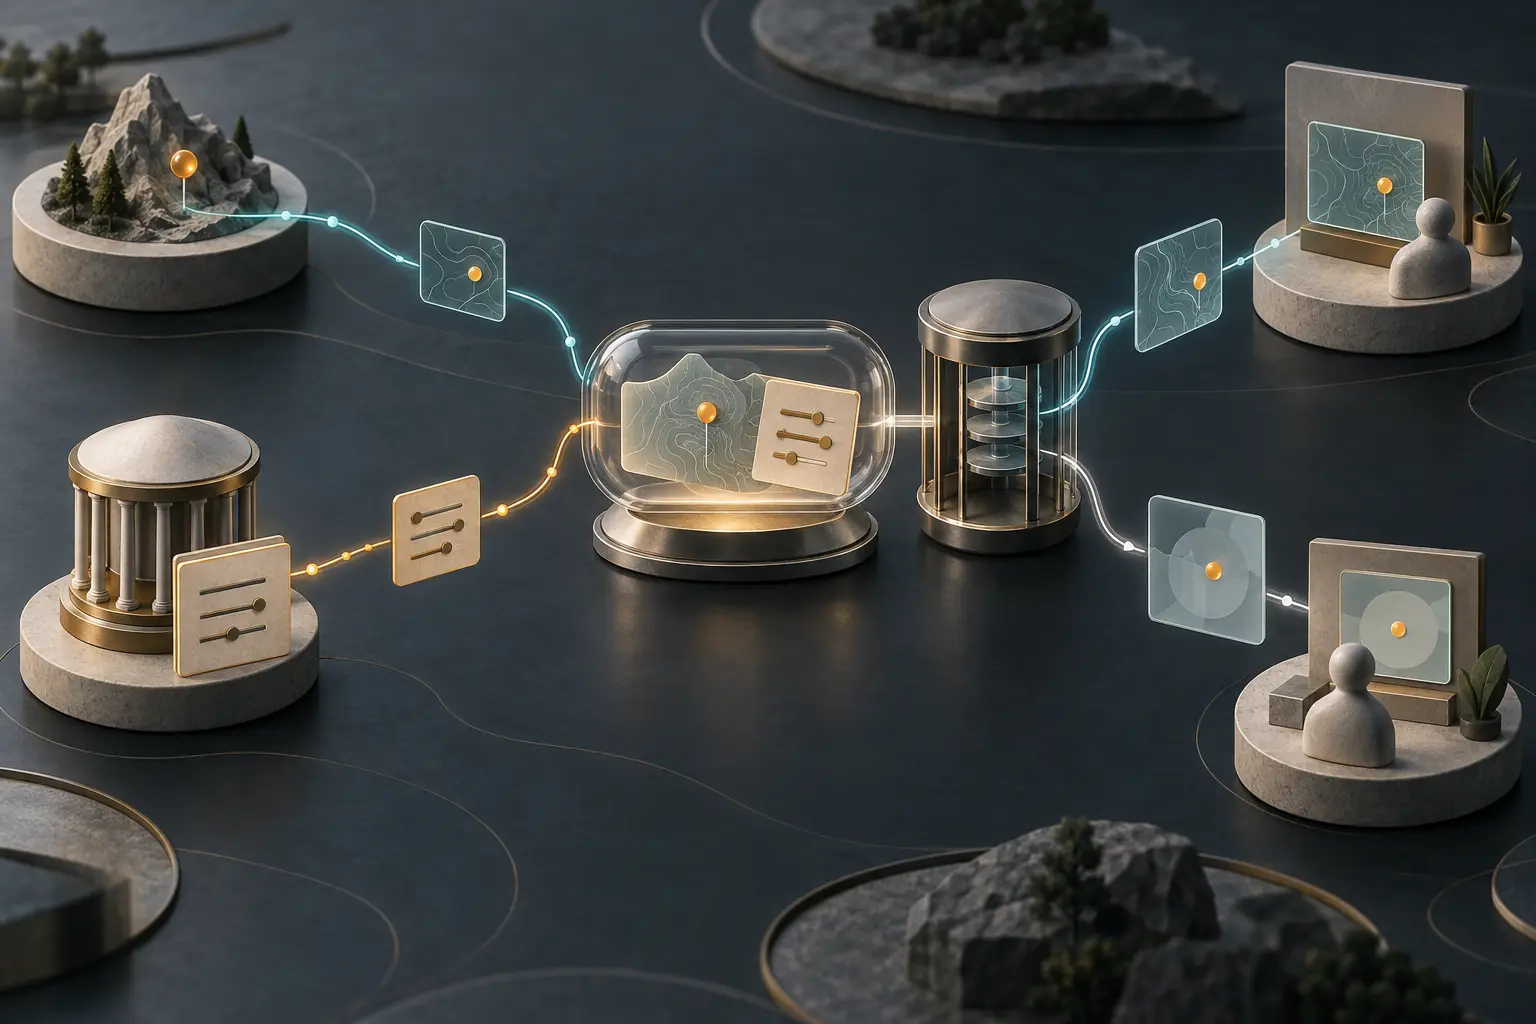
The Location Object Could Carry Rules, Not Just Coordinates: RFC 3693
In February 2004, GEOPRIV treated location privacy as a chain of actors and decisions, not a switch on a map pin. RFC 3693 asked what a location record should say about who may receive it, how precisely it may be shown and what may happen to it—while leaving important enforcement…

History
The Code Point Was Private. Its Top Bits Still Controlled Every Unknown Router: RFC 3936
RFC 3936 opened RSVP number space to standards, experiments and private extensions without pretending that a number was merely a label. The first bits of an entity class already told an old node whether to reject the message, discard the entity or carry it onward untouched.

IETF
The Command Succeeded. The Fax Method Had Disappeared.
The same MGCP `ModifyConnection` can produce two opposite operationally useful results. Leave the fax option unstated and the gateway may accept the command even though the previously required T.38 procedure will no longer run. Repeat `t38` explicitly and the gateway must reject…

Story
RIPE NCC designates two Foundation board members after Falk’s notice
The RIPE NCC Executive Board has named two people for the Rob Blokzijl Foundation board after Falk von Bornstaedt said he would step down. The Foundation’s own rules keep a separate appointment decision with its board.

IETF
The Federation Received the Full Presence Document. Nobody Proved It Filtered the Next Copy.
The optimization was elegant: instead of sending a different presence document for every remote watcher, the home network sent one rich document across the federation and entrusted the receiving network to remove what each watcher was not allowed to see. Bandwidth fell. The…

History
The RFC Was Missing. The DHCP Option Was Not.
RFC 3679 returned DHCP option numbers that had no durable use, but it refused to treat an empty RFC shelf as proof that every code was free. PXE and Apple implementations were already using some undocumented numbers. Sixteen years later, a captive-portal experiment would show why…

History
The Rule Had a Sunset Date. Its Evidence Report Was Optional: RFC 3933
RFC 3933 gave the IETF a clock for temporary process changes. The rule had to expire or be reconsidered, yet the problem statement, success criteria and written account of what happened could remain optional. A sunset constrained authority; it did not manufacture evidence.

IETF
The Call Completed. ENUM Had Not Supplied the Route.
The operations dashboard marked the call as successful. A SIP `200 OK` had arrived, the caller heard ringing, and the session moved into the billing system. Yet the route ledger told a different story: the ENUM query had failed, the softswitch had returned to its vendor-specific…

History
The Message Looked Like a Document. The Protocol Had Already Split It Apart: RFC 3930
RFC 3930 warned that a network message can look like one digital document to a person while the protocol treats it as many fields with different histories, destinations and security rules. The mistake was not aesthetic. It could make extensions fail, signatures brittle and…

History
The Filter Could Change One Entry—or All at Once.
RFC 3678 did not ask every multicast application to learn a new membership vocabulary. It left the old calls in place, then offered two different ways to change a source filter: adjust one source, or replace the complete filter in a single operation.

IETF
The Manager Learned the Engine ID. It Still Had No Permission to Change Anything.
The discovery reply looked like the missing credential. A management application had reached an SNMP endpoint, asked under a well-known local context, and received the identifier of the engine behind it. The value was stable enough to address later scoped requests. It might even…
IETF
The CSV Said the Poll Succeeded. The Trap Could No Longer Be Reconstructed.
One row looked complete: timestamp, source, destination, SNMP version, operation, request ID, zero error status and a list of variable bindings. It was compact enough to scan, join and graph. But when the question changed from “how many responses succeeded?” to “what did this…

History
The Output Stayed 128 Bits. The Key Rules Changed.
In 2004, RFC 3664 adapted AES-XCBC for IKE by keeping the full result that IPsec’s MAC had shortened to 96 bits. Two years later, its successor changed a different boundary: which key lengths the same PRF would accept, and for what IKEv2 purpose.
History
The Name Crossed Protocols. Its Parameters Did Not Move by Themselves: RFC 3555
RFC 3555 did not merely give RTP codecs names that could be printed in another protocol. It specified a custody chain: each piece of a media-type expression had a different destination in SDP, and the payload specification—not the registry—kept authority over what the pieces…

IETF
The Parameter Had an IANA Row. The Call Still Had No Route.
RFC 5341 gives `tel` URI extensions a controlled namespace and a durable reference. That is vital coordination. It is not a runtime receipt for the URI, the number, the network or the call.
Session Map
Governance Branch
RIR Watchdog
Five regional sessions tracking allocation policy, board legitimacy, and institutional continuity.
Open RIR WatchdogCase File
Long-cycle governance dossiers with legal, election, and institutional stress analysis.
Open Case FileNumber Resource Society
Membership, charter, and resource-governance intelligence from the NRS ecosystem.
Open NRS SessionICANN
DNS coordination, accountability frameworks, and global multi-stakeholder process dynamics.
Open ICANN SessionIETF
Protocol standardization trajectory and interoperability risk under fragmented policy conditions.
Open IETF SessionHistory of Internet
Long-cycle infrastructure history used for governance interpretation and structural forecasting.
Open History SessionNOGs
Operator-level implementation intelligence from APRICOT plus regional and national NOG ecosystems.
Open NOGs Session