Summary
- BigTime’s 2025 measurements, presented at RIPE 93, found that about half of more than 9,000 Microsoft-facing RIPE Atlas vantage points received one NTP source in DNS, although the provider inventory listed 12 IPv4 server addresses.
- NTP’s best-current-practice document calls for multiple time sources. DNS addresses, Anycast sites and independent clocks are different counts; one does not prove the next.
Time is the quiet setting that can bring a very loud machine to a halt. Certificates expire against clocks. Logs sort events by them. Caches and key lifetimes use them. Most people never open the time panel until something has gone badly wrong, which gives the service behind that setting a peculiar kind of power: it works out of sight.
At RIPE 93, researcher Pascal Huppert presented BigTime, a study of seven large time services. It examines how they copy server capacity and direct clients to it. The original report published the measurements in 2025. Huppert brought those results to RIPE in October 2026; the talk did not repeat the tests. One finding asks a simple question: when a provider says it has many servers, how many time sources reach the device?
The team used 500 RIPE Atlas probes to map DNS answers. Every ten minutes for eight hours, each probe asked the service’s authoritative DNS server—the source responsible for that domain’s answer. This avoided relying on a recursive resolver, an intermediary that looks up and caches answers for users. A second analysis counted what individual clients received. It covered more than 9,000 Atlas measurement points. Each sent 72 direct queries over 12 hours, one every ten minutes. The Microsoft sample contained 9,010 points.
About half of those 9,010 Microsoft measurement points received one NTP server address. The report listed 12 IPv4 addresses in the service’s inventory. One number counts what the provider had; the other counts what many measured clients saw in DNS. This is a result for the study’s sample, not for half of all Windows computers. RIPE Atlas observes selected networks; it did not count every device on earth.
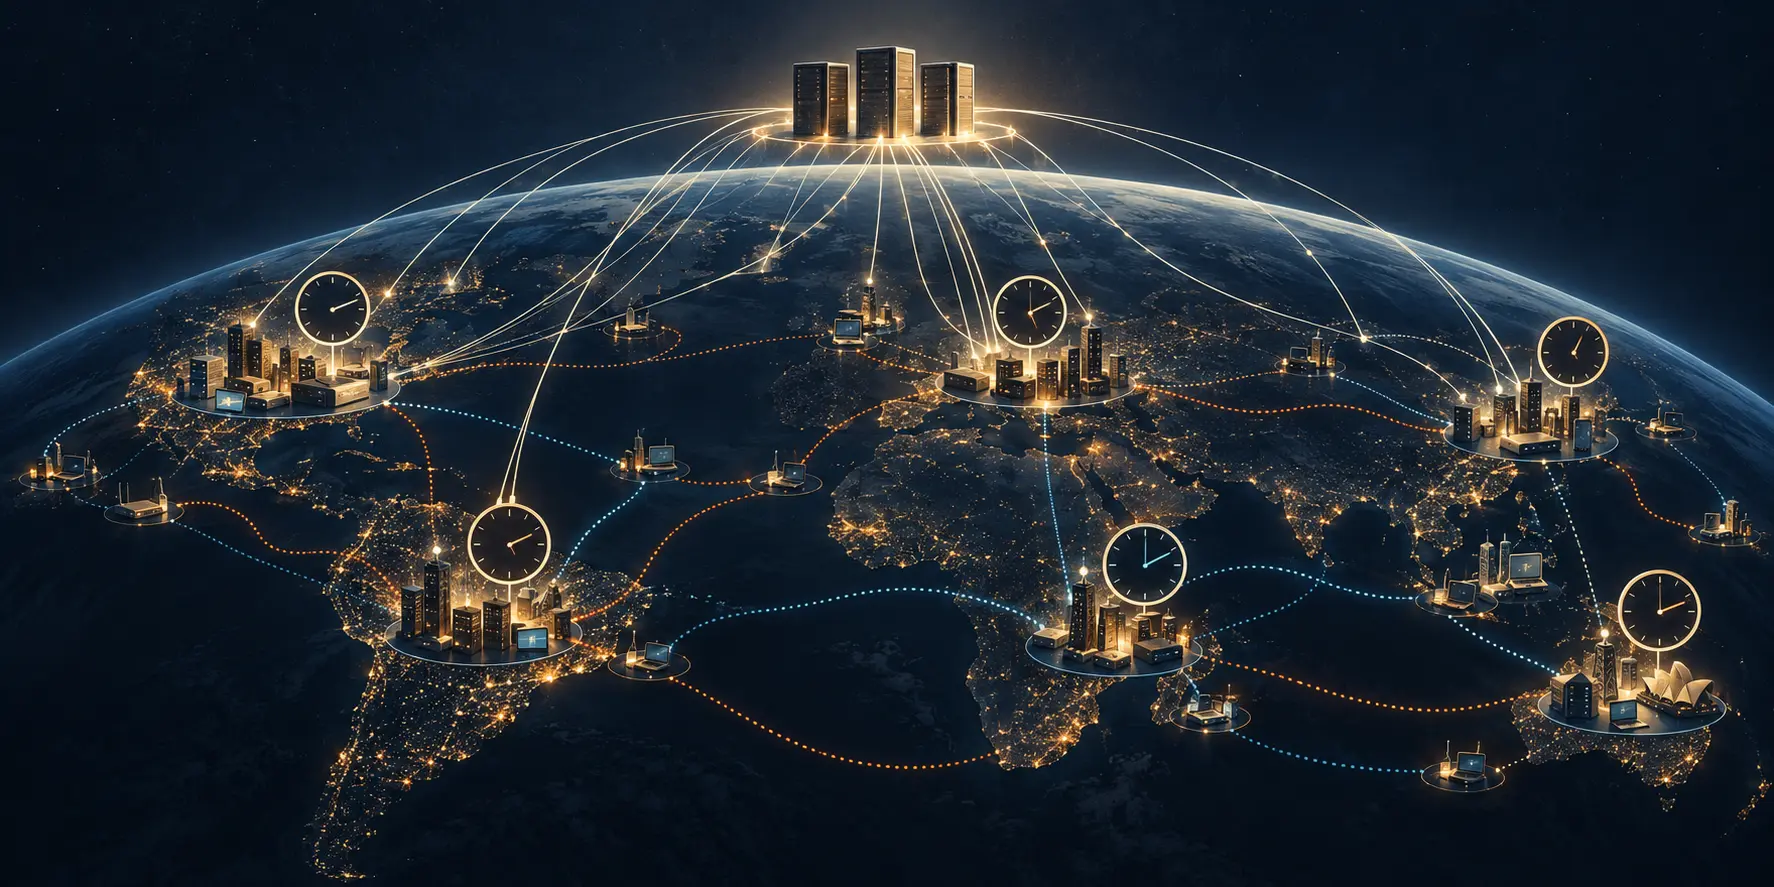
There is more than one layer in this design. DNS can return several addresses for one name. With Anycast, several sites announce the same address and the network routes a client to one of them. A local load balancer can then share requests among servers at that site. These layers can move traffic and handle some failures. They do not automatically give a client several time sources to compare.
The seven services did not share one design: three used Anycast and four used unicast addresses. Huppert said the team could not rule out local load balancers. So the address count is not a machine count or a map of separate failure zones. It tells us what DNS returned to the measured clients.
RFC 8633 connects this design choice to the client. It recommends that an NTP client use several time sources, compare their readings, keep reliable ones and reject poor ones. The RFC’s Anycast section explains the catch: one Anycast address can lead to a large distributed pool but still look like one source to the client. Operators can use separate Anycast pools to give clients more than one source without making setup complicated.
The provider’s global inventory and the client’s list measure different things. A cluster behind one address can add capacity or switch servers at a site. It still gives the client no second reading to check. If that source is wrong, the client has no independent source in its list. The study records no widespread clock failure. It identifies a setup where the client cannot carry out RFC 8633’s recommended comparison because DNS supplied only one source.
The accuracy test used two vantage points synchronised to reference clocks. It was separate from the much larger DNS sample. The address count covers many Atlas points; the accuracy test covers two. A new, independent check of today’s operating-system defaults is the missing evidence needed to know whether the 2025 results still describe devices now.
Any public scorecard for a time service should publish three separate counts: addresses returned to clients, sites reachable behind those addresses, and independent sources each client can compare. Server dots show the provider’s scale. They do not show how many clocks a device can check before trusting one.
Sources
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance