
Open standards body with worldwide implementation impact.
Governance / IETF
IETF
IETF governance intelligence tracks institutions, policy processes, standards activity, registry operations, accountability disputes, and implementation signals that affect internet infrastructure. BTW.
GlobalProtocol GovernanceInteroperability Risk

Protocol process and standards legitimacy.
Spec-to-implementation gap across vendors and operators.
Major standards shifts usually affect systems over 120d+ cycles.
Latest Coverage
Latest from IETF
1,252 articles
IETF
Removing an OAuth Attester Is Not a Kill Switch for Issued Access
A new individual OAuth draft lets a client publisher withdraw an attester it once endorsed. The harder governance question starts after that edit: which authorization server has seen it, and what happens to access already granted?

IETF
DTPC Lets an Application Delete Yesterday Before the Network Sends Today
On a scarce delayed link, not every queued measurement deserves a journey. A new DTPC draft gives the application power to replace stale state before it becomes a bundle. The bandwidth saving is intelligible; the deletion authority needs a receipt of its own.

IETF
A Proof of “We Cannot Tell” Still Has an Evidence Boundary
A new individual Internet-Draft proposes a verifiable receipt for a claim that remains unresolved under a defined body of evidence. Its most important control is not the cryptography at the end. It is the choice, made beforehand, of what evidence and possible worlds the proof is…

IETF
BGP Found a Reachable Address. It Had Not Yet Measured the Path That Would Carry the Packet
A new IDR draft confronts a quiet error in modern routing: the address BGP can reach may not be the tunnel, policy or SID that will carry the traffic. Its answer is not another universal metric, but a stricter evidence boundary around each path-resolution decision.

IETF
The Action ID Stayed the Same. The Validator Did Not.
The latest CAID draft holds the digest steady for entities both revisions accept, yet explicitly refuses some action entities that could carry valid identifiers under the previous draft. For an audit trail, the missing fact is not another hash. It is which rules were used when an…

IETF
The Resolver Disclosed the Exception. It Did Not Authenticate the Answer
An emerging DNS signal can tell a client that a resolver suspended validation for a name. That is valuable candour. It is not a seal of truth, a defence of the operator's decision, or evidence that the application reached a safe service.

IETF
An Accepted AAuth Event Is Not an Agent's Decision
A new AAuth Events draft gives a resource an always-on place to send a signed event. Its `202 Accepted` response closes only the first hand-off: an agent may still be offline when the event's useful lifetime runs out.

IETF
The Parent Admitted the Boundary. It Did Not Promise a Road
A proposed DNS convention lets a public parent say that a child zone exists in another namespace while offering no public nameserver to reach it. The empty target is useful precisely because it is modest: it records a boundary without turning parent intent into proof of private…

IETF
Two Small Agent Budgets Can Authorize One Large Bill
An exploratory AAuth draft puts a hard ceiling on each agent token. The harder governance question sits one step upstream: who reserves against the person's total when several tokens are alive at once?
IETF
The Ladder Stayed in Cache. The Proof Still Had to Cross
SigTag proposes a smaller post-quantum DNSSEC response when a resolver says it already knows the signed Merkle Tree Ladder. That saves retransmission; it does not make cache state authoritative. The server’s omission, the resolver’s retained bytes, signer binding, validation…

IETF
A Valid Signature Is Not a Shared Trust Decision
An individual Internet-Draft on agent-action evidence has changed a deceptively small word in its evaluation model. The revised proposal asks a verifier to say separately whether an artifact checks out and whether this particular relying party is willing to rely on it.

IETF
The Certificate Shrunk. The Trust Decision Did Not
The Certificate Shrunk. The Trust Decision Did Not intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The IETF…
IETF
The Hop That Changed Nothing Can Still Disappear
A revised WIMSE proposal draws a sharp line between evidence that a message changed and evidence that an intermediary was present at all. The second question matters most when the intermediary forwarded the request untouched.

IETF
A SUIT Update Can Be Signed Before Its Target Can Understand It
The latest SUIT update-management draft leaves a crucial pre-delivery fact with the deployment: which devices actually support the optional command on which a firmware update depends. A sound manifest signature cannot answer that compatibility question.
IETF
The Certificate Was Good for the Number. The Call Still Needed a Decision
STIR’s new OCSP profile can make a narrow and valuable statement in real time: this certificate is still valid for this telephone number. The discipline begins where that statement ends. It does not certify the human speaker, the purpose of the call, the safety of the request or…

IETF
An SR Policy-Scale Pass Is Not an ECMP Speed Result
A router can forward traffic while many Segment Routing policies are installed without proving how fast its multipath forwarding is. The IETF BMWG's 22 September revision puts both observations in the same test programme but, crucially, does not give them the same evidentiary…

IETF
LAKE's KEM Draft Drops a Four-Message Shortcut That Exposed Identity
A shorter handshake looked possible in July if the initiating device revealed its credential identifier at the start. The September working-group revision no longer offers that trade: its proposed KEM authentication flow has five mandatory messages, and the responder reaches its…
IETF
The Server Marked the File Uncacheable. The Client Still Had to Obey.
NFSv4.2 is gaining a standard way for a server to tell clients that a file should not live in their data caches. The flag is useful precisely because it is narrow: it records an instruction, while compliance, durability and cross-client visibility still need their own evidence.

IETF
BGP Best-Path Review Asks What a Failed Forwarding Check Actually Does
A route may have a reachable next hop in a routing table and still lack the forwarding path that would carry its packets. An IETF early review says a draft meant to close that gap has not yet specified which state to test—or the consequence when the test fails.
IETF
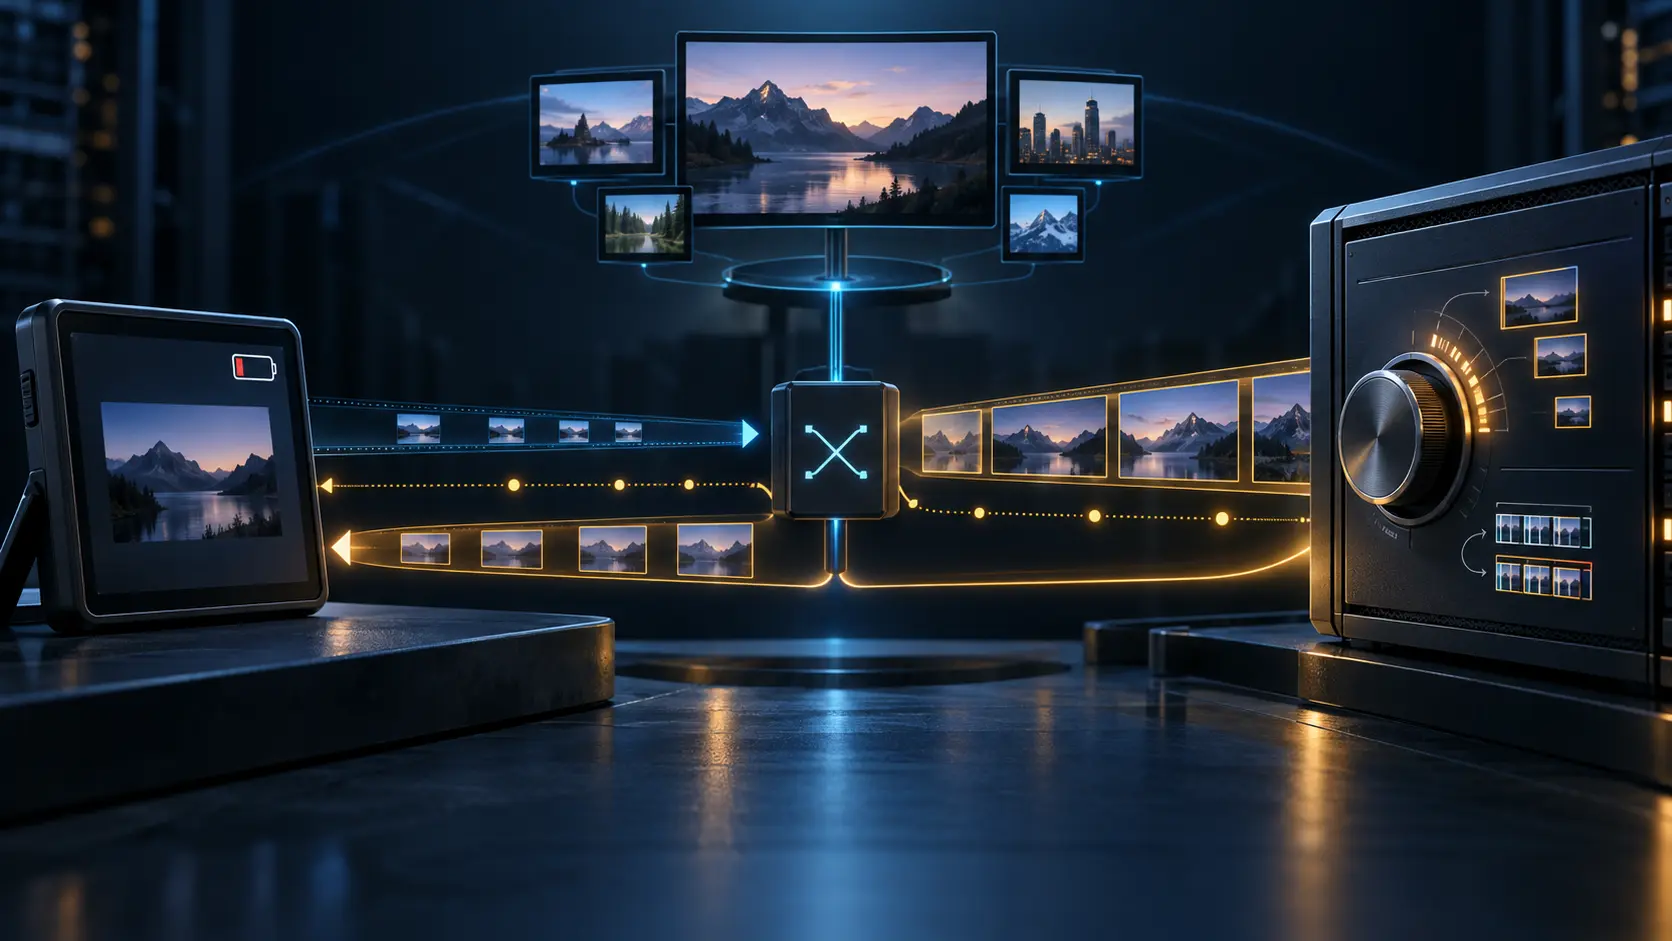
The Receiver Pays the Battery Cost. The Sender Still Chooses the Picture.
An IETF mechanism nearing publication lets a video receiver ask for fewer pixels or frames when its battery or decoder is under pressure. The request is useful precisely because it is not sovereign: the encoder, mixer, negotiated session and congestion controller still determine…
Member Unlock
Restricted Profile Intelligence
Login is required to unlock full profile briefings and deep-dive sections.
Strategic Circle Briefing
Join to unlock strategic briefings after signing in.
Join Strategic CircleLeadership Alliance Briefing
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance