
Topic
WHOIS/RDAP Accountability
Within the Topic facet, WHOIS/RDAP Accountability topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.

Story
LACNIC’s WHOIS Shows the Origin ASNs but Not Their Authorization Boundary
LACNIC’s WHOIS Shows the Origin ASNs but Not Their Authorization Boundary intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may…

Story
APNIC Wants Login to Read the Current IRT Email State
An account should not inherit yesterday’s lock answer when today’s IRT contact state says something else. APNIC’s 2026 roadmap proposes replacing reliance on a static account lock flag with a login-time check of continuously tracked IRT email validity. That is a small sentence…

Story
RIPE’s RDAP Marks a Mixed AS Block Reserved at Either Boundary
RIPE’s RDAP Marks a Mixed AS Block Reserved at Either Boundary intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The…

Story
APNIC's RDAP Use Is 20%. That Is Not an Adoption Rate.
APNIC's new survey puts RDAP at 20% among respondents asked about core registry services. The number is useful evidence about reported use; it is not a census of deployed systems, a traffic share or a verdict on whether RDAP can replace WHOIS.

Story
RIPE’s Plain-Text History Needs Its Request Context
Whois 1.124 made historical entities easier to read as plain text. The returned body is still filtered history, while the structured response carries a separate revision label. Saving the text is not the same as saving what identifies it.

Story
ARIN's WhoWas Accepts an IPv6 Address. The History Still Needs a Capability Receipt
A request can be well formed, a report can have the right columns, and the archive behind both can still remain unproved. ARIN’s public record now makes all three propositions about IPv6 WhoWas look adjacent. What it does not provide is the small, dated receipt that would make…

Story
APNIC Has an ASN Endpoint and an Empty Changelog. They Do Not Prove the Same Release
APNIC Has an ASN Endpoint and an Empty Changelog. They Do Not Prove the Same Release intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences…

Story
AFRINIC's 2026 Closure Data Spells Voluntary Two Ways
AFRINIC has done the useful thing by publishing reproducible statistics on closed memberships and returned number resources. But its current 2026 data place `VOLUNTARY` beside `VOLUNTART`, and the dashboard treats the two strings as different categories. That one-character split…

IETF
A Verified RDAP Contact Needs an Audience Boundary, Not a Universal Badge
A registrar can verify an email address once and face two different disclosure questions the next morning: what may an anonymous reader learn, and what may an authenticated investigator learn for a justified purpose? The verification event is the same. The authority to disclose…
Story
A Correct RIR Record Did Not Fix One Geo-IP Error After Two Months
An APNIC 62 case study exposed a small but consequential accountability gap: the registry data could be right, several geolocation databases could agree, and one downstream service could still send a customer to the wrong country.

Story
ARIN Waited for a Geofeed Standard. Its RDAP Help Still Does Not Claim It.
Two years ago ARIN tied a community request to a visible trigger: once the common RDAP geofeed standard was accepted, three named product surfaces would change. The standard is now RFC 9877. The useful question is no longer whether the IETF will finish the vocabulary, but how an…
Story
APNIC Prop-173 Would Make Every Directory Query an Agreement. The Response Would Carry No Version.
An acceptable-use policy can change while the response governed by it remains in a cache for years. APNIC's prop-173 would make ordinary WHOIS, RDAP and web queries subject to a clear, versioned policy and would tell users that querying or using the service means agreeing to…

Story
APNIC Will Automate Route-Record Alignment. The Roadmap Does Not Name the Conflict Winner
“Alignment” sounds like database housekeeping. In APNIC’s Q3 2026 roadmap, it means something harder: deciding how resource holdings, a route-management template, Whois route objects and RPKI authorizations should change when they disagree—and preserving enough evidence to show…
Global Institutional
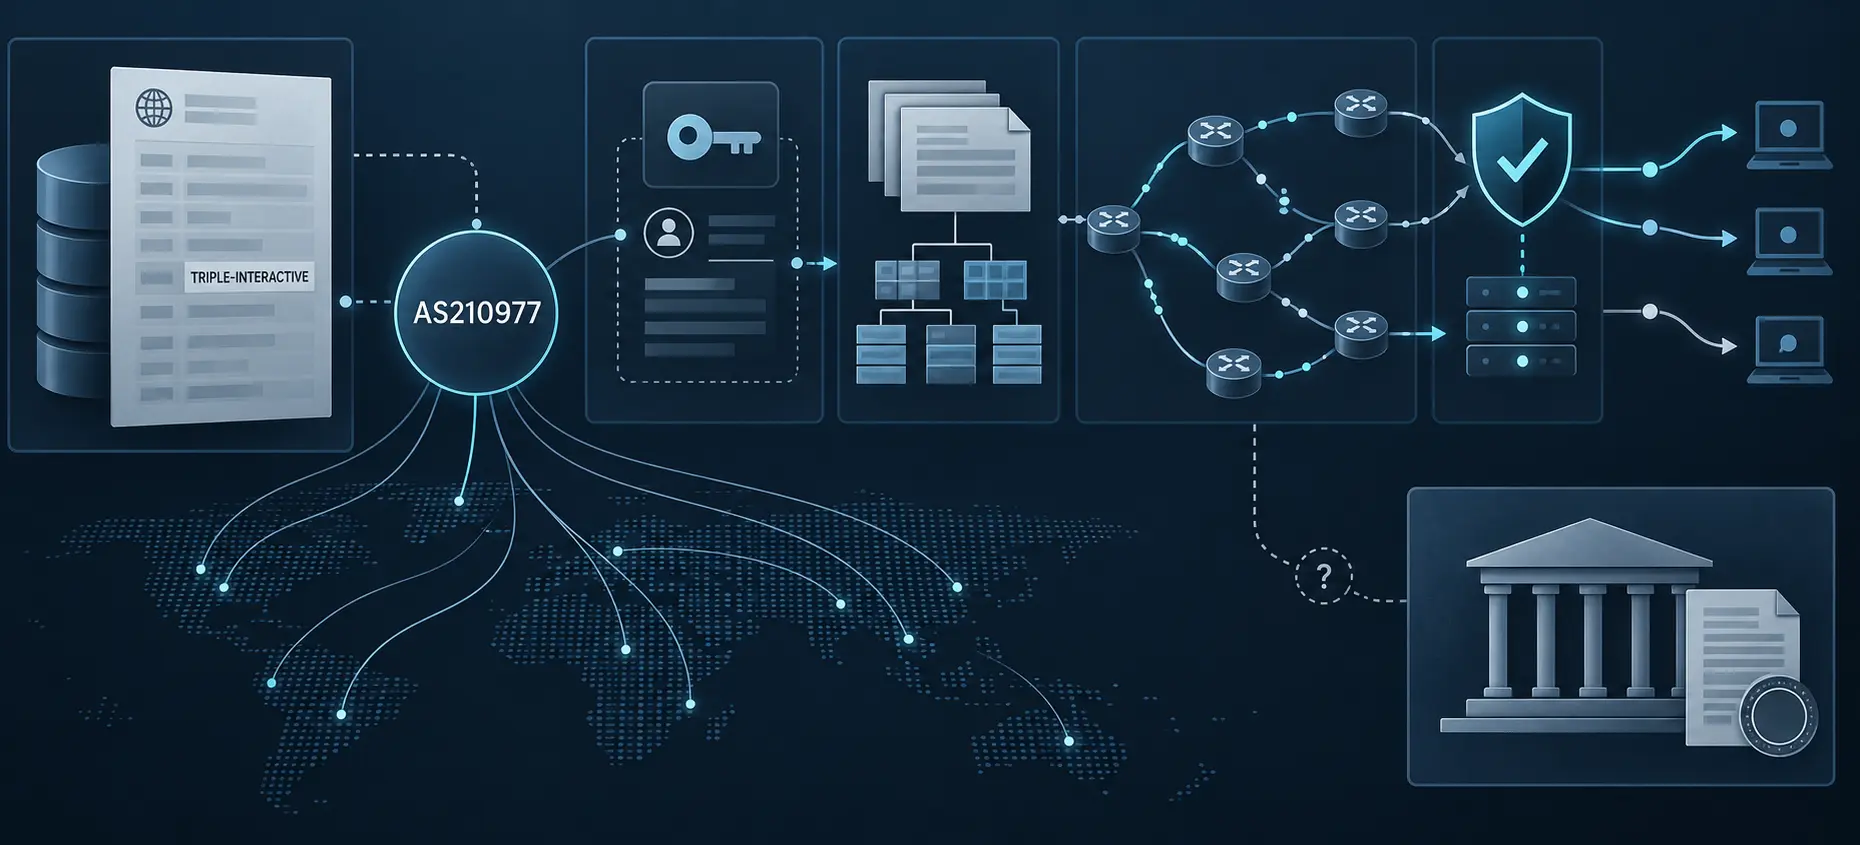
What AS210977’s Registry Record Can—and Cannot—Prove
What AS210977’s Registry Record Can—and Cannot—Prove intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The Global…

Global Regional ISP
INFINITYWIFI: Three Different Meanings of Network Control
INFINITYWIFI: Three Different Meanings of Network Control intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The Global…

Leaders
What AFRINIC’s Registry Records Can—and Cannot—Attribute to Maina Mukhangu Noah
A public registry listing connects Maina Mukhangu Noah to ORG-BITL1-AFRINIC, but the available record does not establish that he held institutional authority inside AFRINIC. The distinction matters because a contact field can guide operational communication without identifying…
Story
RIPE ABUSE: Who Controls the Next Step After a Report?
RIPE ABUSE is often described as a contact point. That is accurate, but incomplete. The published abuse-c field creates a route into a responsibility chain: a report can be addressed to a resource holder or designated organisation, the mailbox can be tested by RIPE NCC, and a…

Global Institutional Trends
RIPE ABUSE: A Reporting Route Is Not Proof of Repair
RIPE ABUSE: A Reporting Route Is Not Proof of Repair intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The Global…

Story
AFRINIC's 8 September Snapshot Returned Four Old Resources to “Allocated.” It Cannot Say Why
Three ASNs and one /19 crossed AFRINIC’s public boundary together between two signed daily files. Their 2006 dates came back with them. That is evidence of a current state change, not evidence of a new allocation—and the distinction deserves a small public receipt.

Story
RIPE Database 1.124.1 Fixed Certificate Selection. Its “No Evidence” Finding Needs a Search Boundary
RIPE NCC was right to ship a reported authentication vulnerability without waiting for a routine test interval. The next duty is different: show members what time, traffic and registry history were actually examined before “no evidence of exploitation” became the public…