
Topic
Network-resource Evidence
Within the Topic facet, Network-resource Evidence topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.
CASE FILE
The Signature Passed. The From Address Still Wasn't the Signer: DKIM and the Authority of a Domain Signature
The message displayed `bank.example` as its From identity, carried an urgent payment instruction and passed DKIM. The result was genuine—but for `receipt-alert.example`, a domain controlled by the attacker. A valid signature had been promoted into authority over a different name.
CASE FILE
The Digest Matched. The Sender Was Still Unknown: HTTP `Content-Digest` and the Authority of a Checksum
The policy upload carried a valid `Content-Digest`. The service recomputed the hash, displayed a green “verified” badge and applied the file. The file was malicious. Nothing had been corrupted in transit; the attacker had chosen both the bytes and the checksum.

History
The Mask That Silence Guessed Wrong: How ICMP Bootstrapped a Subnet
A host wakes with an IPv4 address but no rule for deciding which destinations are on its own wire. It broadcasts a question: what mask divides this address into network, subnet and host? Nothing answers. The old specification permits a conservative guess—the unsubnetted mask…
CASE FILE
The Header Named the Client. The Peer Address Did Not Agree: HTTP `Forwarded` and Proxy-Chain Authority
The origin normally sat behind two reverse proxies. One night a requester reached it directly, supplied an administrator's allowlisted address as the first `X-Forwarded-For` value, and crossed an IP rule. The header parser returned exactly what it had been asked to return. The…
CASE FILE
The Name Selected a TLS Context. It Did Not Authorize the Request: SNI and the Authority of a Routing Hint
The gateway received `tenant-a.example` in a ClientHello, selected Tenant A's certificate, and attached Tenant A's policy context. It then let the connection reach a privileged route without a tenant credential. Every TLS selection step had worked. The error was believing that a…
CASE FILE
The Certificate Signature Passed. The Handshake Was Not Finished: TLS 1.3 `Finished` and Transcript Authority
The dashboard declared a secure session when the server's CertificateVerify signature passed. One record later, the client rejected a corrupt `Finished` message and closed the connection. The certificate key had proved one thing accurately. Operations had promoted it into proof…
Global National Telecom Trends
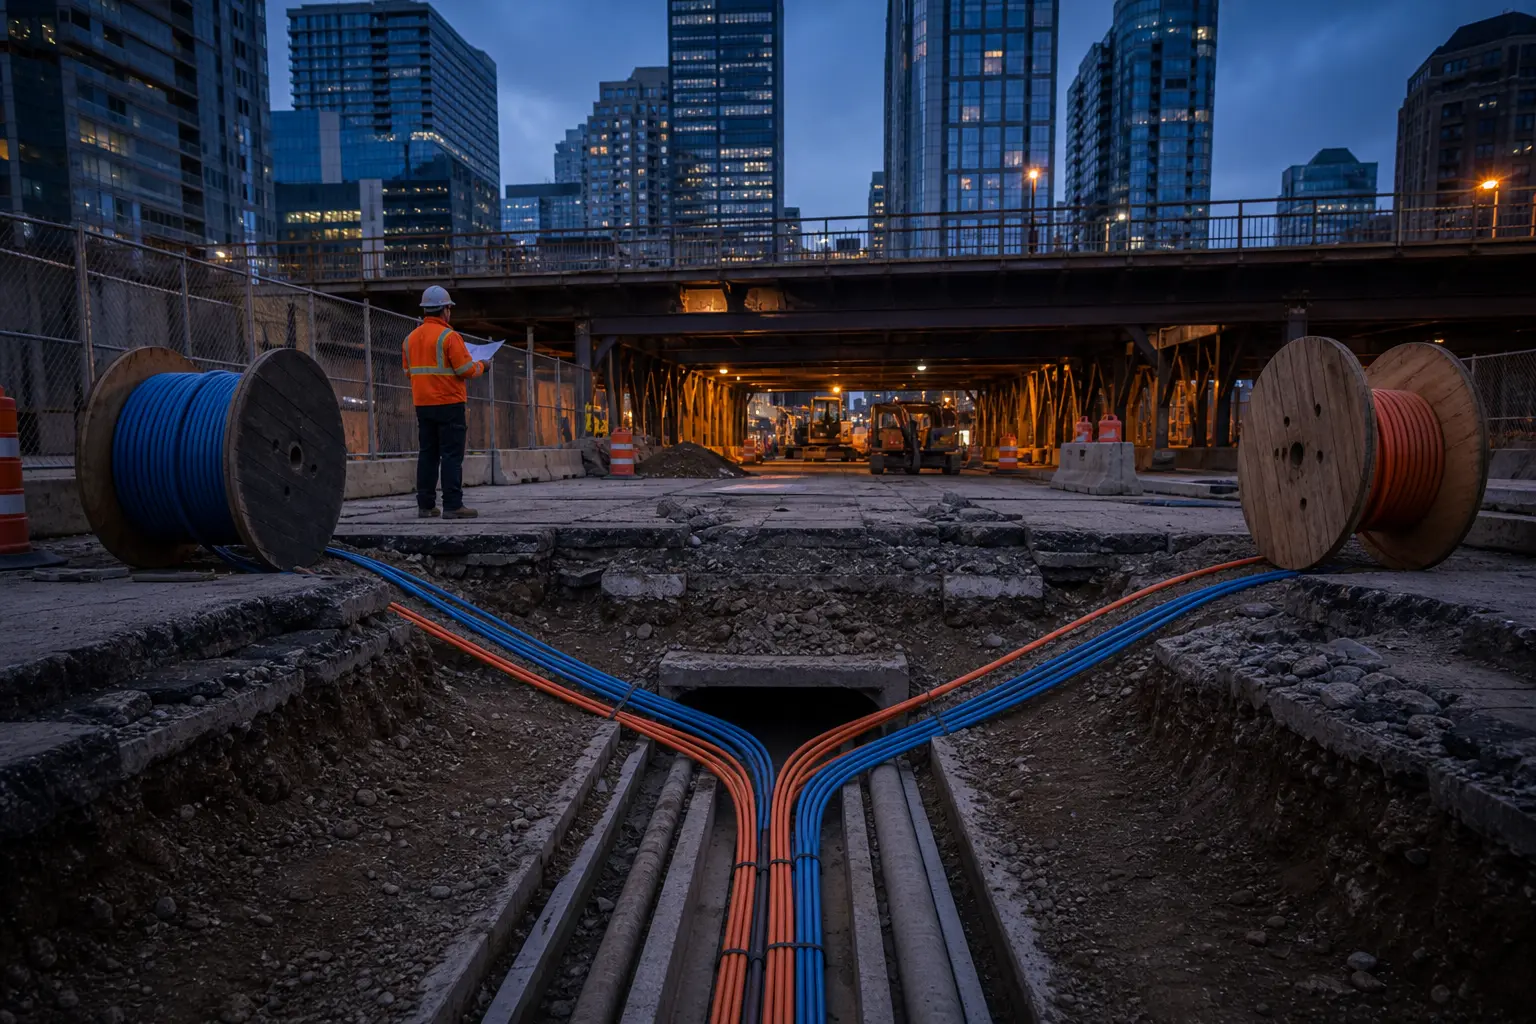
Two carrier paths are one risk if they share the same civil work
The second circuit on a procurement sheet may have a different carrier, circuit ID and invoice while still running through the same conduit, bridge or building entrance. Resilience begins where supplier plurality ends and physical evidence starts.
History
The Token That Proved a Reply Had a Path Back: DNS Cookies Without Identity
A small EDNS option changed what a DNS server could reasonably infer from a UDP source address. It did not identify the sender. It showed, more narrowly and more usefully, that someone at that apparent address had received an earlier reply and returned a server-made token.

History
The Test That Succeeded by Saying Nothing: What Discard Could Actually Prove
An engineer sends a known stream to port 9 and waits for confirmation. None arrives. That is not an omitted feature: RFC 863 requires the Discard service to throw the data away and send no response. The test can still be useful, but only if its operator names which layer produced…
CASE FILE
The Edge Negotiated HTTP/2. The Origin Still Spoke HTTP/1.1: TLS ALPN and the Authority of One Connection
The browser offered `h2` and `http/1.1`. The edge selected `h2`, completed TLS and exchanged valid HTTP/2 frames. A fleet dashboard then labelled the origin “HTTP/2 native.” It was not. The edge terminated that connection and opened a different one upstream, where it sent…

History
The Clock Answer with No Grammar: Why Daytime Was for People, Not Programs
A client connects to port 13 and receives a perfectly valid answer. Another host returns the same moment in a different order, with a different year width and another kind of timezone label. Both exchanges succeeded. RFC 867 promised a readable clock line, not a grammar that…
CASE FILE
The CA Was on the List. The Identity Was Not Approved: TLS `certificate_authorities` and the Authority of a Selection Hint
The client chose a certificate whose issuer appeared in the server's CA list. The server built and validated the chain. Then the application rejected the subject because that identity had never been admitted to the tenant. Every cryptographic step could be correct while access…
CASE FILE
The Staple Was Signed. The Status Could Still Be Stale: TLS OCSP and the Authority of a Cached Answer
The certificate was revoked at 10:07. At 10:11, the server still stapled a correctly signed `good` OCSP response whose `nextUpdate` was hours away. Nothing had been forged. The answer was authentic, within its declared interval and already behind reality. The incident began when…

History
The One-for-One Replies That Never Stopped: How Echo and Chargen Formed a Network Loop
The sender can vanish after the first datagram. One machine receives a packet and generates characters for the address named as its source. A second receives those characters and echoes them back. From then on, each reply is the other service's request. Nothing in either…
CASE FILE
The Socket Closed. The Transaction Did Not: TLS close_notify and the Authority of an Ending
The payment service wrote a success response, initiated an orderly TLS shutdown and recorded the request as complete. Its database commit failed milliseconds later. The client had received an authentic ending, but not the fact it needed. `close_notify` said the server would send…

History
The Null Byte That Made Return Unambiguous: How Telnet Distinguished a New Line from a Carriage Return
A print head has reached column forty when the network sends carriage return. Should it move to the left edge of the same line, or is a line feed about to move it down as well? Telnet refused to make the receiver guess. The next byte carried the distinction: `LF` meant new line…
CASE FILE
The Ticket Survived. The Session Did Not: TLS 1.3 Resumption and the Authority of Carried State
The failover node accepted a TLS 1.3 session ticket issued before the user’s access was revoked. Cryptographically, the shortcut worked: the client knew the resumption PSK and its binder covered the new handshake. Operationally, the old decision had crossed into a new connection…
CASE FILE
The Record Was Longer. The Message Was Not: TLS 1.3 Padding and the Authority of Observable Length
The incident report treated a larger encrypted record as a larger application message. Its arithmetic was precise and its conclusion was false. The sender had rounded TLS 1.3 records to a block boundary and sometimes emitted padding-only Application Data. The capture established…

History
The Server That Changed Jobs Mid-Connection: How NNTP Made Roles Explicit
One NNTP connection can begin by offering peer-to-peer article transfer and, after two words from the client, present itself as a reading service. The socket has not moved. The server’s authority has. `MODE READER` made that change visible—and made stale assumptions dangerous.
CASE FILE
The First Hello Was Rejected. It Was Not Erased: TLS HelloRetryRequest and the Authority of the Transcript
The capture began with a second ClientHello. It offered one key share, the server accepted it, and the handshake completed. Read in isolation, the trace appeared to prove that the client had chosen that group from the start. It proved nothing of the kind. The missing first flight…