
Topic
Network-resource Evidence
Within the Topic facet, Network-resource Evidence topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.

History
Traffic Could Flow Upstream Before the Return Mapping Existed: RFC 3472
In CR-LDP's bidirectional setup, the first packets could travel back toward the initiator while the labels for the other direction were still returning hop by hop.
IETF
The Line Was Operational. No Call Had Completed
RFC 5098 gave PacketCable operators a detailed view of an MTA's signaling configuration and line-service state. Its most reassuring status stopped at an acknowledged control link; it did not say that a phone rang, media arrived or two people spoke.

IETF
The OAM Packet Shared the Service Label. It Did Not Share the Packet History: RFC 9546
The assurance console showed an unbroken test sequence while the control application reported a missing command. Nothing in that disagreement required either instrument to be wrong. RFC 9546 gives DetNet OAM its own sequence history, deliberately separate from the App-flow it is…

History
The Label Left the Packet and Entered the Physical World: RFC 3471
In 2003, an MPLS label stopped being only a value a router could read from a packet. It could name a time slot, a wavelength, or the physical port through which light must pass.
IETF
The Envelope Named AES-GCM. Its Nonce History Was Still Off-Object
RFC 5084 gave CMS precise identifiers and parameters for authenticated encryption. It also made the decisive control easy to miss: a valid envelope can show its nonce, but it cannot by itself prove that the same nonce was never used elsewhere under the same key.

History
The Backup Path Existed. Recovery Was Still a Cycle: RFC 3469
In 2003, MPLS engineers gave failure a clock with several hands: detecting damage, carrying the alarm, moving labels, seeing packets return, and deciding whether the temporary route was good enough to keep.
IETF
IPV6CP Was Open. The Global Address Was Still Unproven
RFC 5072 gives IPv6 over PPP a clear control-state milestone. It also leaves leaders with a harder obligation: prove the address, exception conditions, route and outcome instead of treating `Opened` as an end-to-end receipt.

IETF
The Name Persisted. The Resource Still Needed an Authority: RFC 9517
RFC 9517 gives research-data resources a globally scoped DDI name and a DNS-based route to possible services. The durable-looking identifier is useful precisely because its promise is narrow: it identifies under delegated authority, but it does not guarantee that a resolver…

IETF
The Preference Was Accepted. The Source Address Was Not Yet Proven
RFC 5014 gives an IPv6 application a disciplined way to ask for a kind of source address. Its most important lesson is what happens next: an accepted preference is not a receipt for the address selected, the packet sent or the outcome achieved.
History
CDNs Could Share Reach. They Still Had to Negotiate the Deal: RFC 3466
In 2003, a content network could be described as infrastructure for moving requests and responses, not just packets. RFC 3466 gave separate networks a vocabulary for working together—but left the terms of that cooperation where they already belonged: in a negotiated relationship.
History
The ACK Count Changed. The Byte Count Held the Window Honest: RFC 3465
TCP once let the number of acknowledgment messages help decide how quickly a sender could expand its congestion window. RFC 3465 asked a stricter question: how many previously unacknowledged bytes did those messages actually prove had moved?
IETF
The Trace Reached the Name. It Did Not Prove One Content Path: RFC 9507
RFC 9507 gives name-based networks a traceroute of their own. Its replies can expose one branch through forwarders, caches and applications, but a clean trace to a name is evidence of one answering route—not a certificate of one origin, one permanent path or completed content…

IETF
The Leasequery Reply Was Green. The Endpoint Was Not Proven Present
RFC 5007 lets a requestor retrieve a DHCPv6 server’s binding view. It does not turn that view into proof that an endpoint is online, a subscriber is identified, traffic is legitimate or an authorization decision has succeeded.

History
The Human Explanation and Machine Report Shared an Envelope: RFC 3462
A delivery failure could be read by a person or processed by software, but those were not the same act. RFC 3462 gave both audiences one recognizable container without pretending that either the prose or the syntax proved what had happened.
History
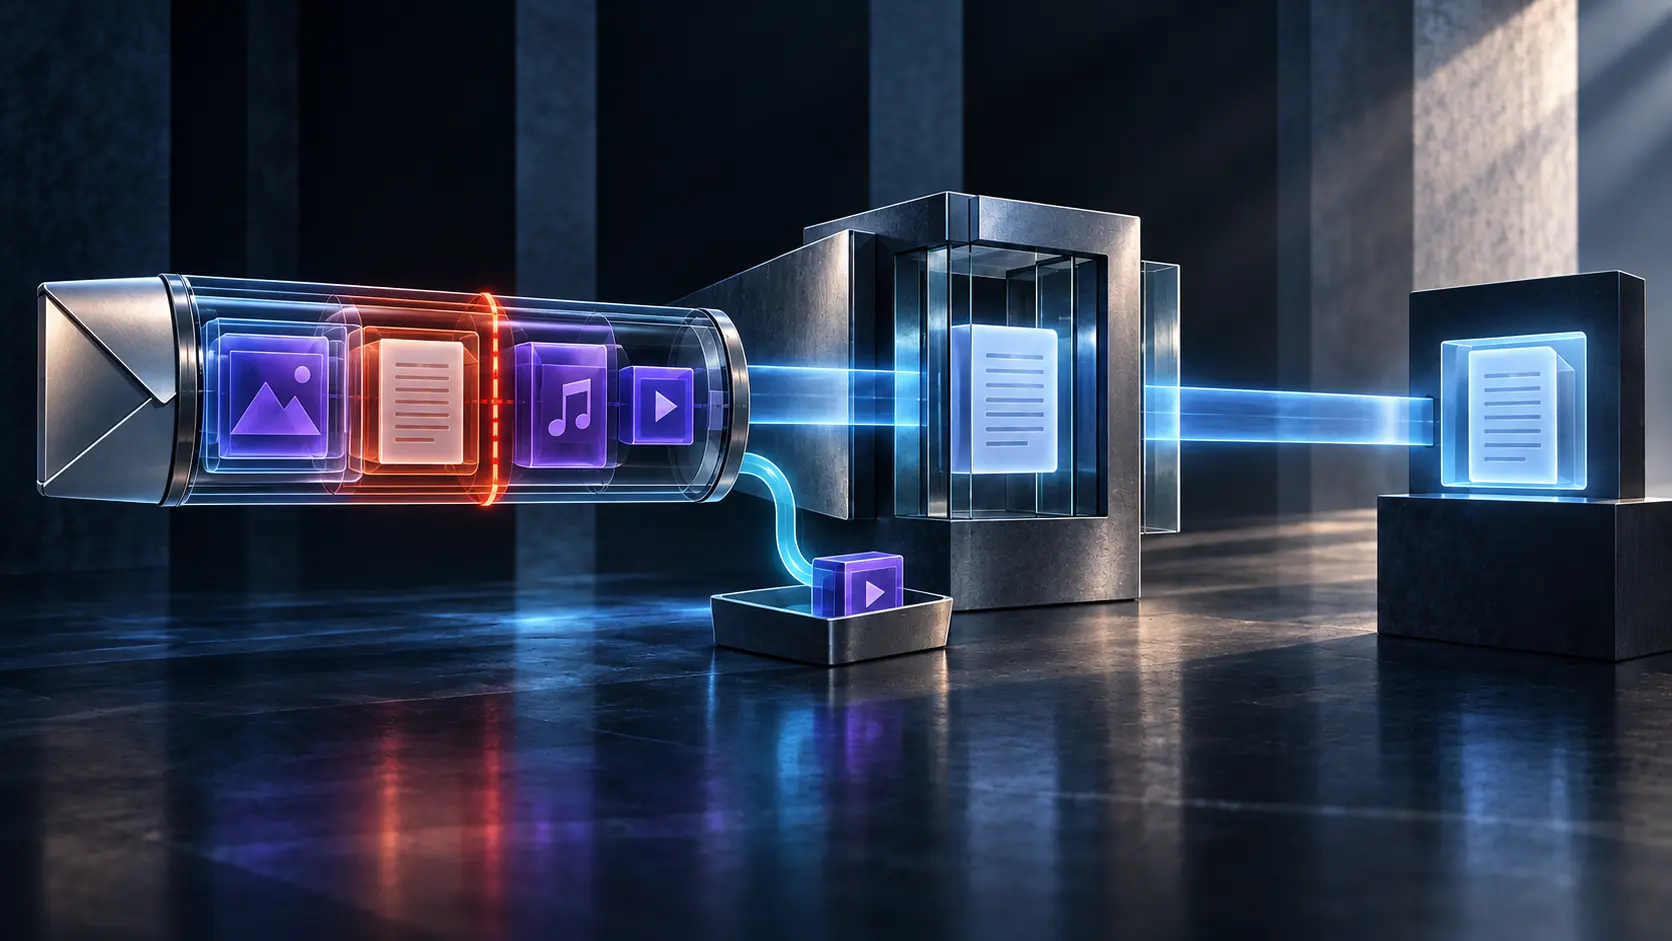
The Optional Part Vanished. Delivery Could Still Succeed: RFC 3459
RFC 3459 confronted a problem that ordinary email tried not to have: a gateway might deliver only part of a multipart message because the receiving system could neither store nor render everything. The standard made the sender state which loss changed the meaning of delivery.

IETF
The Bits Made Loss Visible. They Did Not Make the Verdict: RFC 9506
RFC 9506 lets encrypted transports expose a few carefully bounded signals for on-path loss and delay measurement. A visible bit can improve diagnosis, but only if endpoint state, observer geometry, timing, path, queue treatment and application outcome remain separate evidence.
IETF
The Archive Link Was Reachable. That Did Not Prove the History Was Reconstructed
RFC 5005 gives publishers precise ways to describe complete, paged and archived feeds. Its most useful leadership lesson is what those structures do not collapse: a route to old documents, a completed traversal, a retained logical history and a reader-visible account are four…

Global Cloud Services
The per-prefix answer: what each of Datamatix's remaining /24s actually serves
The per-prefix answer: what each of Datamatix's remaining /24s actually serves intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may…
History
The Header Said Voice. The Message Still Had to Be Read: RFC 3458
RFC 3458 gave a mixed-media inbox one compact clue about how a message expected to be used. Its achievement was not making that clue authoritative, but specifying how the system must remain useful when the clue and the surviving body disagreed.

History
The Tunnel Was Secure. The Assigned Address Was Not an Access Credential: RFC 3456
RFC 3456 reused DHCPv4 to give a remote machine a virtual place inside a corporate network. Its sharpest rule was also its easiest to lose: a protected DHCP exchange could assign an address, but that address could not be trusted as the reason to admit traffic.