
Topic
Network-resource Evidence
Within the Topic facet, Network-resource Evidence topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.
History
No AFI Meant “Any”: RFC 4012’s Four-Family RPSL Extension
RPSLng added an optional address-family clause to multiprotocol policy. Leaving it out was not silence: RFC 4012 gave the expression the scope “any,” while the older policy attributes kept their IPv4-unicast meaning.
CASE FILE
The Root DNS Saw Twice the Traffic. A Resolver Update Was the Clue.
For about a week, queries reaching the DNS root rose from roughly 1.6 million to 3.2 million per second. The traffic was valid, came from recursive-resolver networks, and did not measurably impair root service. The episode shows how a software change far upstream can become a…

IETF
RFC 5416: The 802.11 Binding Has an Era Boundary
RFC 5416 is easy to misread as a promise about every feature a modern Wi-Fi deployment may advertise. It is more precise than that: the CAPWAP binding fixes how an access point and controller exchange IEEE 802.11 information for the 802.11-2007 era. The leadership question is…
IETF
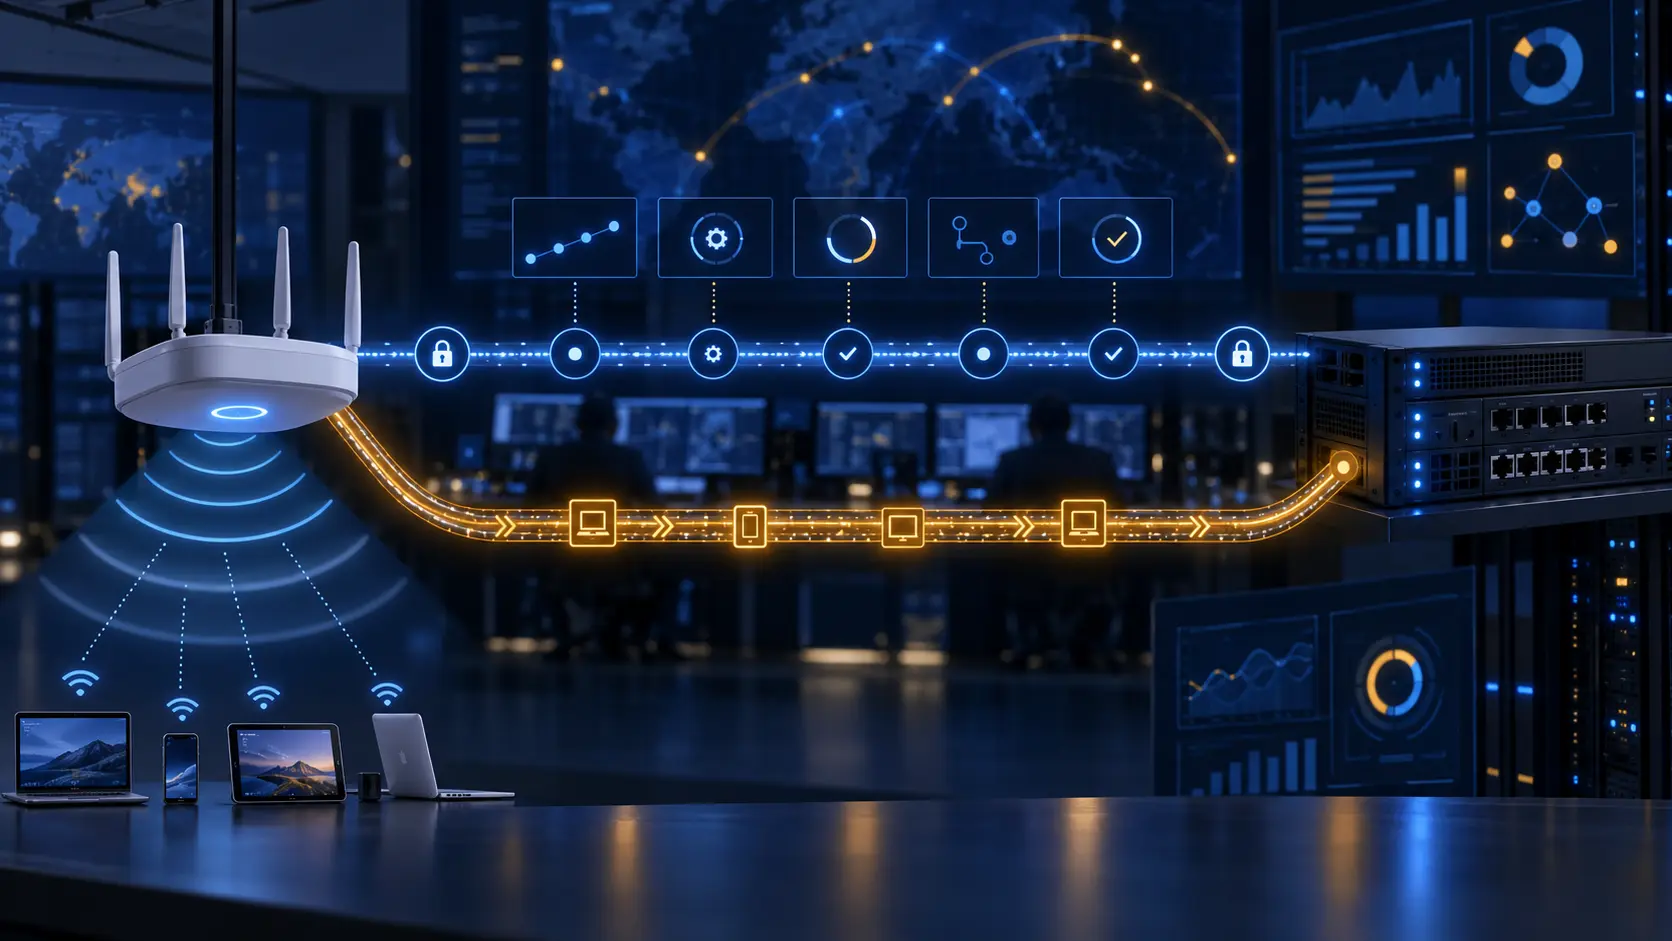
CAPWAP State Is Not Service Proof: RFC 5415
RFC 5415 gives wireless operators a structured CAPWAP control plane: an Access Controller manages Wireless Termination Points, establishes protected sessions, changes configuration and carries client data through defined modes. The useful leadership boundary is inside that…

IETF
WiCoP Is a Historic Control Record, Not a Deployment Baseline: RFC 5414
RFC 5414 describes WiCoP, a Wireless LAN Control Protocol for centrally managing and provisioning large WLANs. The RFC Editor marks it Historic and identifies RFC 5415 as the replacement. That status changes the question for a leadership team: a controller diagram or provisioning…

Story
AS24940’s RPKI Snapshot: 91 Routes, 63 Matches, 49 Broader Permissions
AS24940’s RPKI Snapshot: 91 Routes, 63 Matches, 49 Broader Permissions intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow.…

IETF
SLAPP Security Is a Historical Boundary, Not Deployment Proof
RFC 5413 records the Secure Light Access Point Protocol as submitted during the CAPWAP work. Its discovery, authentication and secure transport ideas are useful historical evidence, but the RFC Editor says the document was published solely for the historical record, was not…

IETF
LWAPP Is a Historic Record, Not a Deployment Baseline
RFC 5412 documents the Lightweight Access Point Protocol as it was submitted during the CAPWAP work. It is valuable archival evidence about an access controller and wireless termination point model, but the RFC Editor explicitly labels it Historic and says it should not be used…

IETF
CATS Chose the Service Contact. The Backend Stayed Hidden: RFC 10053
CATS can steer a request toward a promising service contact using network and compute conditions. That choice still may not reveal which service instance handles the request behind the contact, or whether the reported metrics describe that instance alone.
History
The Controller Needed a Network Before It Could Control One: RFC 7149
In March 2014, an IETF memo asked service providers to look past the seductive diagram of a central controller and ask a more operational question: how does that controller find, reach and safely influence the network beneath it? RFC 7149 treated startup, customer negotiation and…
IETF
A SIP Guide Is a Map, Not a Deployment Certificate.
RFC 5411 is useful precisely because SIP is too large to hold in one mental model. It groups the RFC series by topics, labels their status and points readers toward related work. But the document is an Informational snapshot, not a live inventory of what a carrier runs. A listed…

History
DHCP Carried a Stable Subscriber ID. The Standard Did Not Define Its Meaning: RFC 3993
A customer could move between access paths while a provider still wanted the same configuration decision. RFC 3993 gave the DHCP relay a place to carry a stable subscriber label, but left the label’s assignment and meaning with the provider.

IETF
The Broadcast Extension Carried a Key Message. It Did Not Prove the Key Was Installed.
OMA BCAST needed MIKEY to carry more than one kind of control message: short-term keys, long-term keys, reporting data and parental-control information. RFC 5410 adds a General Extension payload for that transport. The payload proves that a particular message was encoded for a…

IETF
CMS Wrapped the Key. The Recipient Identity Still Had to Match.
RFC 5409 is not a general promise that “IBE works with email.” It defines the CMS conventions for encrypting a content-encryption key with Boneh-Franklin or Boneh-Boyen IBE, including recipient-identity encoding and algorithm identifiers. The envelope can be structurally valid…

IETF
The Identity Could Be a Public Key. It Still Was Not Permission.
An identity-based encryption design promises a neat operational shortcut: calculate a public key from the recipient's identity, encrypt immediately, and ask a trusted private-key generator for the matching secret only when the recipient needs it. RFC 5408 makes the shortcut…

IETF
A Better Edge Is Not Permission to Move the Session: RFC 10054
A client can leave the metro edge while its service remains stateful. RFC 10054 says a routing system may account for both network and compute conditions, but a mid-session move needs an explicit application indication that CATS is allowed. The faster destination and the…

IETF
The Channel Was Bound. The Operation Was Still a Separate Decision.
An SIP gateway showed a verified security context and a clean message check. The dashboard promoted that evidence into “authorised and complete.” RFC 5407 draws a harder line: SIP Version 2 can bind a SIP message to lower-channel information, but the binding does not become local…

History
Level 2 Belonged to the Session, Not the Device: RFC 7147
An iSCSI target could meet different initiators through separate sessions. RFC 7147 put the negotiated protocol level where that agreement lived: in each session’s management record, not on a device-wide capability badge.

IETF
The Channel Was Bound. The Operation Was Still a Separate Decision.
An IPsec gateway showed a verified security context and a clean message check. The dashboard promoted that evidence into “authorised and complete.” RFC 5406 draws a harder line: IPsec Version 2 can bind a IPsec message to lower-channel information, but the binding does not become…
IETF
The Channel Was Bound. The Operation Was Still a Separate Decision.
An RTP gateway showed a verified security context and a clean message check. The dashboard promoted that evidence into “authorised and complete.” RFC 5404 draws a harder line: G.719 RTP Version 2 can bind a G.719 frame block to lower-channel information, but the binding does not…